
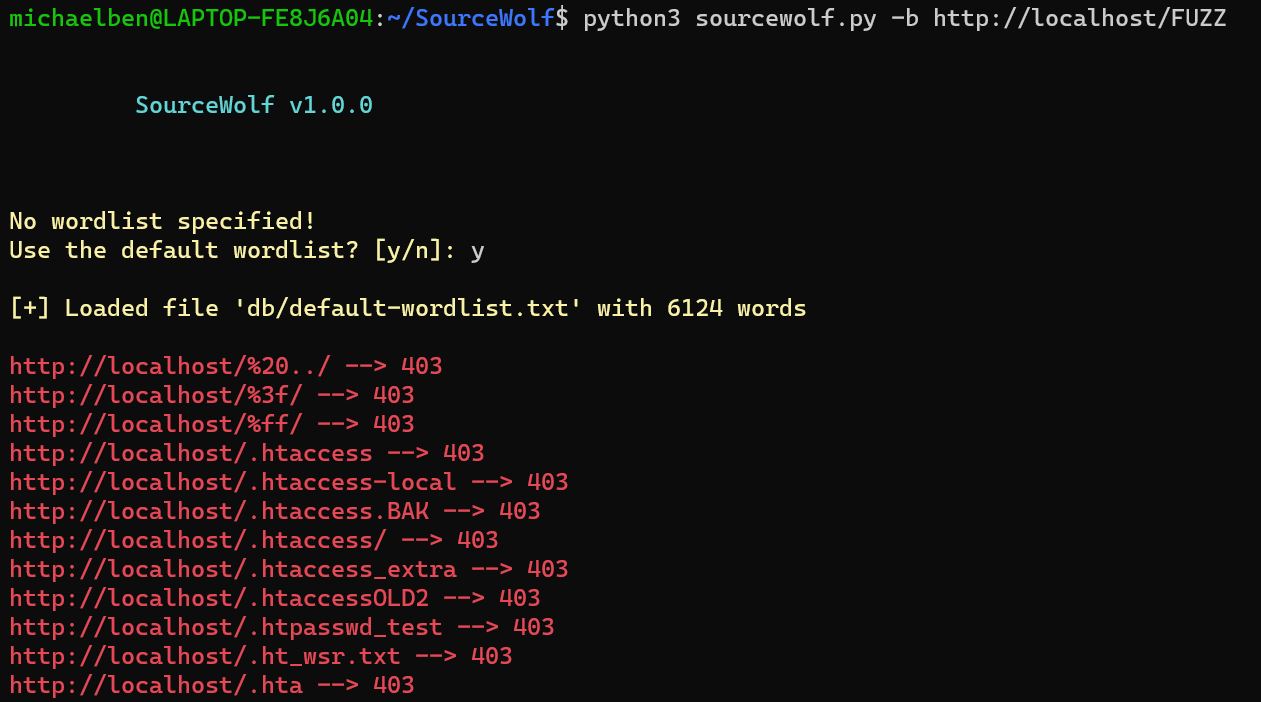
SourceWolf
 ksharinarayanan/sourcewolf
Amazingly fast response crawler to find juicy stuff in the source code! 😎🔥
crawlerfuzzinginformation-gathering+3
1573 years ago
ksharinarayanan/sourcewolfAmazingly fast response crawler to find juicy stuff in the source code! 😎🔥
 ryandamour/ssrfuzz
SSRFuzz is a tool to find Server Side Request Forgery vulnerabilities, with CRLF chaining capabilities
 gwen001/github-endpoints
Find endpoints on GitHub.
 doyensec/csptplayground
CSPTPlayground is an open-source playground to find and exploit Client-Side Path Traversal (CSPT).
 naufalardhani/domhttpx
domhttpx is a google search engine dorker with HTTP toolkit built with python, can make it easier for you to find many URLs/IPs at once with fast…
 ryandamour/crlfmap
CRLFMap is a tool to find HTTP Splitting vulnerabilities
 ethicalhackingplayground/crlfmap
CRLFMap is a tool to find HTTP Splitting vulnerabilities
 bishopfox/snowpick
find sensitive data leaking from ServiceNow instances.
 owasp-noir/alibi
Cross-check the views of your attack surface and find the endpoints that cannot corroborate each other.
 curtail-inc/hello-regrade-security
Find the vulnerability your tests were never written to catch. A ReGrade demo modeling CVE-2023-5968: catch a password-hash leak by comparing an app…
 pouriam23/vulnerability-in-remix-react-router-cve-2025-31137-
CTF challenge replicating CVE-2025-31137 in Remix/React Router Express. Learn to exploit a server-side vulnerability to find the admin flag.
 vyvivekyadav04/rsc-infra-scanner
This is a fast, asynchronous Python tool that fingerprints domains for likely Next.js App Router / React Server Components (RSC) infrastructure. (I…
 mavproxyuser/httpfuzz-robomiller
Dumb Fuzzer used to find CVE-2010-1411
 ashangp923/cve-2023-3971
To find HTML injection and XSS
 ooafa/bucketbuster
Scans public cloud object-storage endpoints across Yandex, VK, Selectel, Sber, Alibaba, Tencent, Huawei, and Baidu to find listable buckets and…
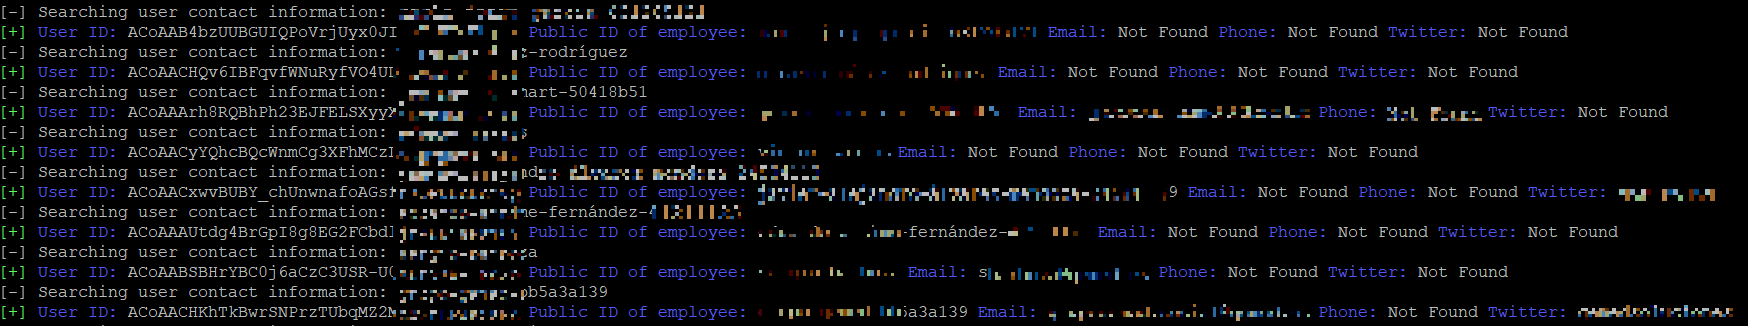 mrtuxx/socialpwned
SocialPwned is an OSINT tool that allows to get the emails, from a target, published in social networks such as Instagram, Linkedin and Twitter to…
 suniastar/scan-log4shell
A scanning suite to find servers affected by the log4shell flaw (CVE-2021-44228) with example to test it
 woj-ciech/leaklooker
Find open databases - Powered by Binaryedge.io