
CVE-2026-82222
 ghostlyrootb2h/cve-2026-82222
Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…
command-and-controlexploitationinformation-gathering+5
ghostlyrootb2h/cve-2026-82222Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…
 shoucheng3/perwendel__spark_cve-2016-9177_2-5-1
Exploit for CVE-2016-9177 targeting Spark Java web framework, demonstrating directory traversal vulnerability in version 2.5.1 for security testing…
 shoucheng3/vert-x3__vertx-web_cve-2018-12542_3-5-3-cr1
Exploit for CVE-2018-12542 in Vert.x-Web, a Java web framework. Demonstrates a path traversal vulnerability allowing unauthorized access to static…
 osungjinwoo/cve-2022-22965
Proof-of-concept exploit and testing scripts for Spring4Shell (CVE-2022-22965), a Spring Framework remote code execution vulnerability, with bash and…
 epicosy/jooby
Exploit toolkit targeting CVE-2019-15477 in the Jooby micro web framework, enabling vulnerability analysis and exploitation of Java/Kotlin web…
 pouriam23/pre-render-data-spoofing-on-react-router-framework-mode-cve-2025-43865
Proof-of-concept exploit for CVE-2025-43865 demonstrating pre-render data spoofing in React Router framework mode, enabling data injection during…
 unicordev/exploit-cve-2025-29927
Exploit for CVE-2025-29927 (Next.js) - Authorization Bypass
 shoucheng3/apache__myfaces_cve-2011-4367_2-0-11
Exploit for CVE-2011-4367 targeting Apache MyFaces JSF implementation, demonstrating a remote code execution vulnerability in the Jakarta Faces…
 pl4tyz/cve-2026-33701-unsafe-deserialization-in-opentelemetry-java-agent-rmi-instrumentation
Technical analysis of CVE-2026-33701, an unsafe deserialization vulnerability in OpenTelemetry Java Agent RMI instrumentation, including exploit…
 w2hcorp/cve-2025-29927-poc
Here is a simple but effective exploit for CVE-2025-29927.
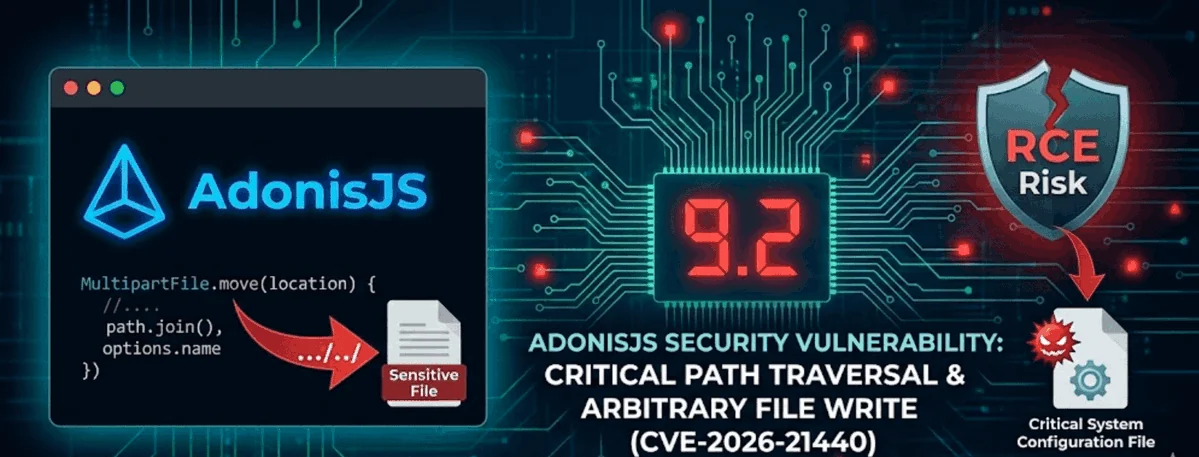 redpack-kr/ashwesker-cve-2026-21440
Proof-of-concept exploit for CVE-2026-21440, a critical path traversal in AdonisJS multipart uploads enabling arbitrary file write and remote code…
 koutto/jok3r
Jok3r v3 BETA 2 - Network and Web Pentest Automation Framework
 byt3bl33d3r/mitmf
Framework for Man-In-The-Middle attacks
 beefproject/beef
The Browser Exploitation Framework Project
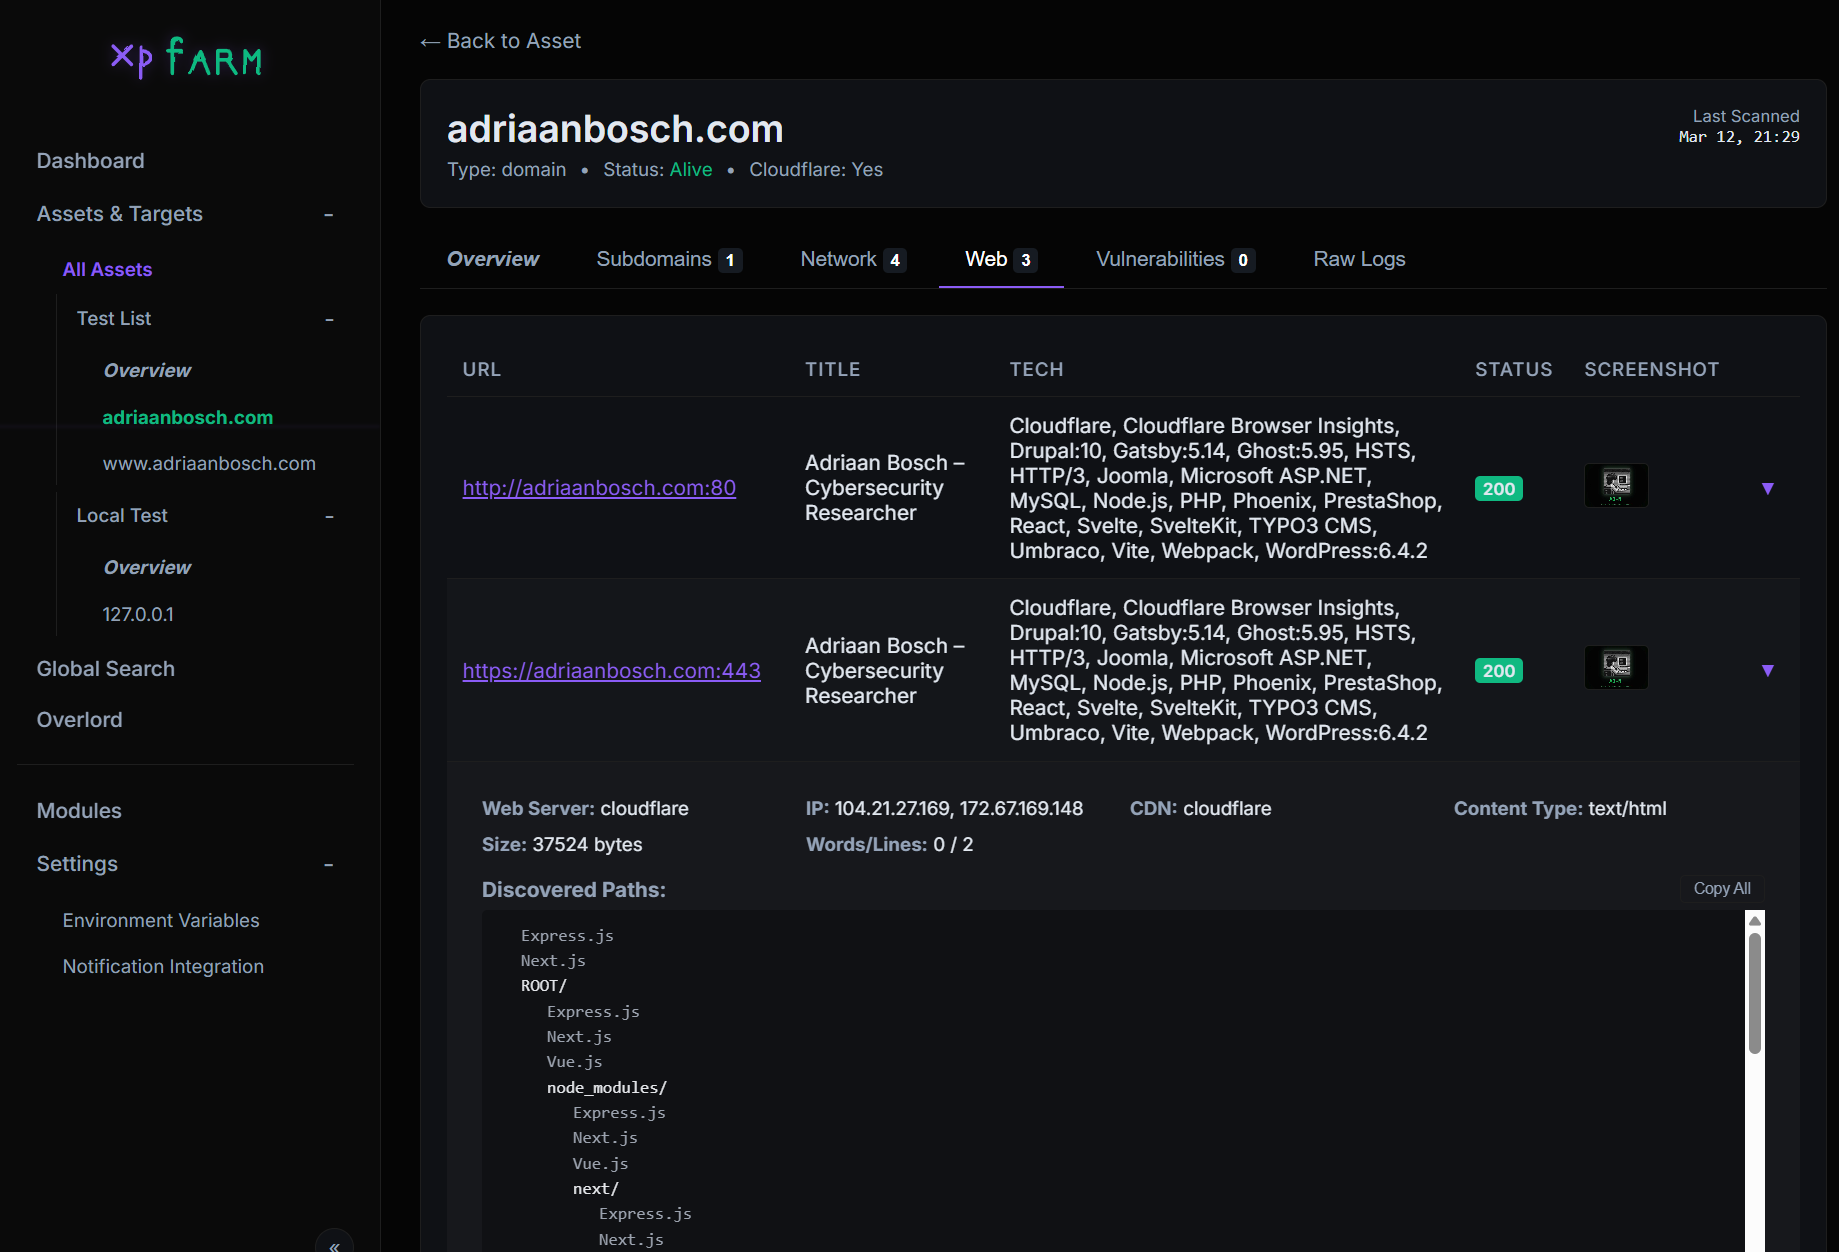 canuk40/xpfarm
Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI
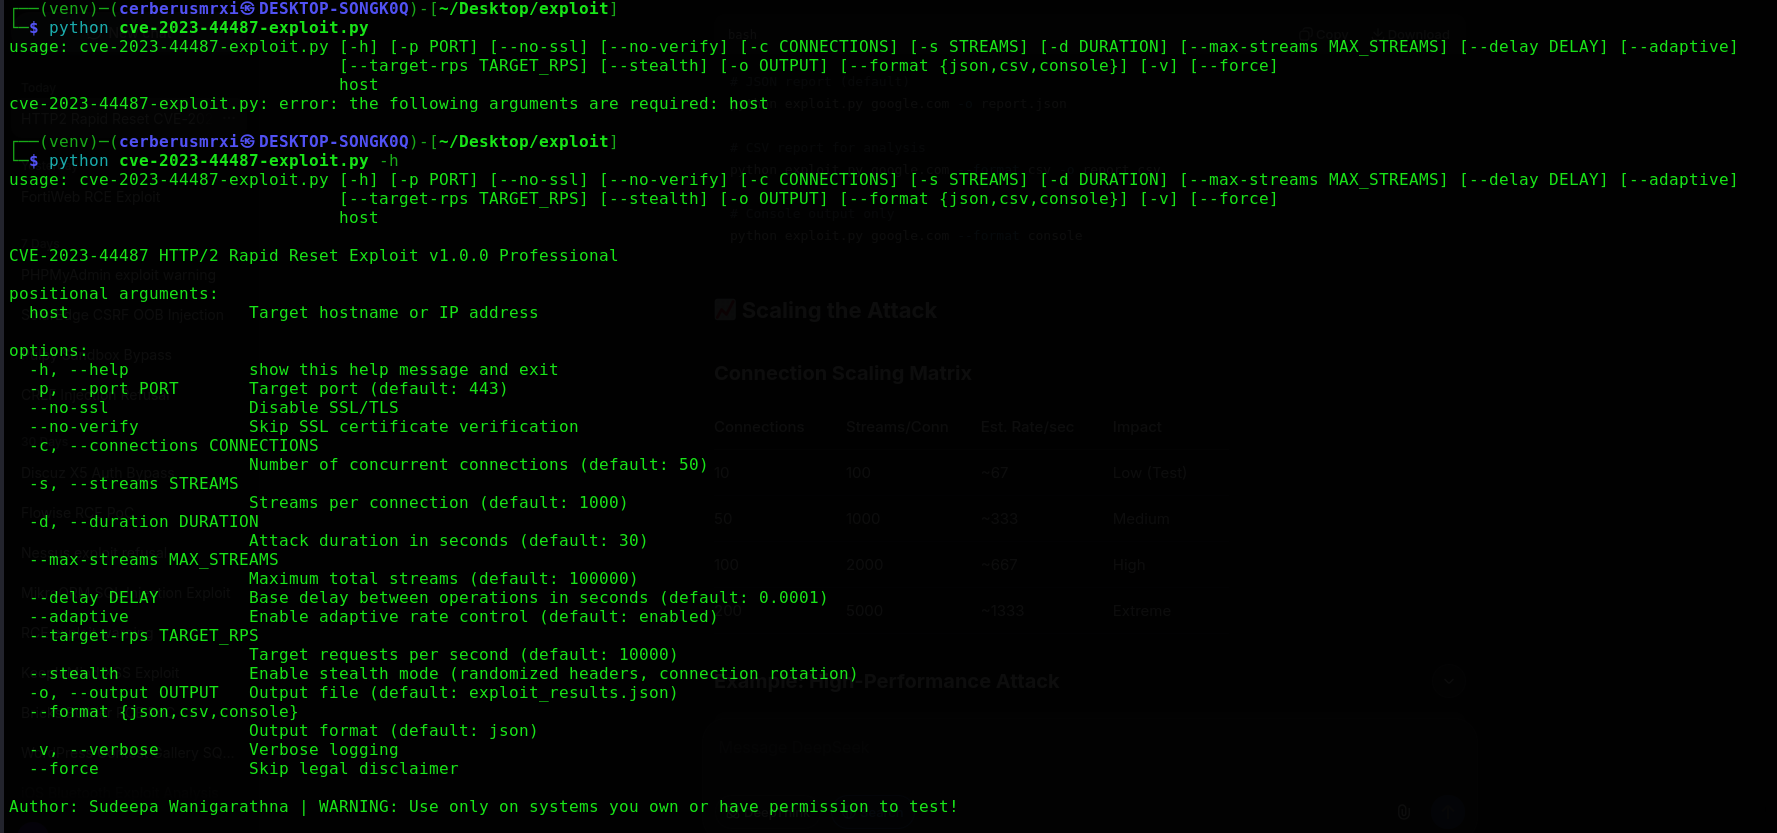 cerberusmrxi/cve-2023-44487-http2-dos-rapid-reset-exploit
Advanced CVE-2023-44487 HTTP/2 Rapid Reset vulnerability exploitation framework. Features multi-connection concurrent attacks, adaptive rate control,…
 simoesctt/ctt-exchange-rce-v1.0---microsoft-exchange-exploit-cvss-10.0-critical-cve-2021-26855-cve-2021-27065
CTT-enhanced version of the Microsoft Exchange Server SSRF to RCE exploit (ProxyShell/ProxyLogon), another CVSS 10.0 critical vulnerability that…