
heartbleed
 cheese-hub/heartbleed
Educational Docker-based lab demonstrating the Heartbleed bug (CVE-2014-0160) with hacker, victim, and server containers for hands-on exploitation…
container-securityctfeducation+4
2
cheese-hub/heartbleedEducational Docker-based lab demonstrating the Heartbleed bug (CVE-2014-0160) with hacker, victim, and server containers for hands-on exploitation…
 0xzerosec/cve-2025-55888
Proof-of-concept exploit demonstrating an XSS vulnerability in ARD's Ajax transaction manager endpoint through unsanitized accountName input,…
 mbanyamer/cve-2026-25916-roundcube-webmail-dom-based-xss-exploit-via-svg-href-attribute
Python exploit for Roundcube Webmail DOM-based XSS (CVE-2026-25916) via SVG href attributes, enabling session hijacking and data exfiltration through…
 eliangonzi00/pockeycloakcve-2023-0264
Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…
 bugresearch/cve-2026-50980
oPanel DNS-Based Cross-Site Scripting (XSS) & Session Hijacking
 teteco/cve-2026-52217-vtex-checkout-crosstenant-idor
The VTEX Checkout Service exposes OrderForm data through the endpoints `/api/checkout/pub/orderForm/{orderFormId}` and `/attachments/*`. These…
 theopaid/cve-2026-66421-openclaw-dashboard-stored-xss-via-lastmessage-session-field
Security Advisory: Stored Cross-Site Scripting Via Agent Messages Leading To Session Token Theft (openclaw-dashboard)
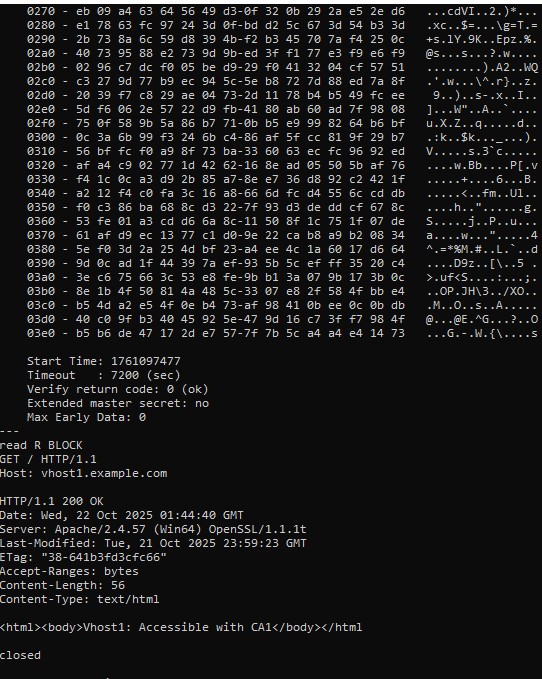 absholi7ly/cve-2025-23048-poc
Apache HTTP Server versions 2.4.35 – 2.4.63 are vulnerable to a client certificate authentication bypass when TLS 1.3 session resumption is used…
 ockeghem/cve-2015-6835-checker
PHP script to detect CVE-2015-6835 (session deserialization vulnerability) by analyzing source code for unsafe unserialize() calls in session…
 kalhoralireza/cve-2026-17532-lab
Docker lab demonstrating CVE-2026-17532, an unauthenticated reflected XSS in Seraphinite Accelerator that chains to RCE via admin session, with…
 ifqygazhar/cve-2024-44000-litespeed-cache
Exploit script for CVE-2024-44000 targeting LiteSpeed Cache WordPress plugin session management vulnerability, enabling unauthorized data access…
 wubinworks/magento2-session-reaper-patch
Patch for CVE-2025-54236(a.k.a Session Reaper) which allows customer account takeover and RCE under certain conditions. This patch is actually a…
 joshuavanderpoll/cve-2026-2991
PoC exploit for CVE-2026-2991 — authentication bypass in KiviCare WordPress plugin (≤4.1.2) allowing unauthenticated patient account takeover and…
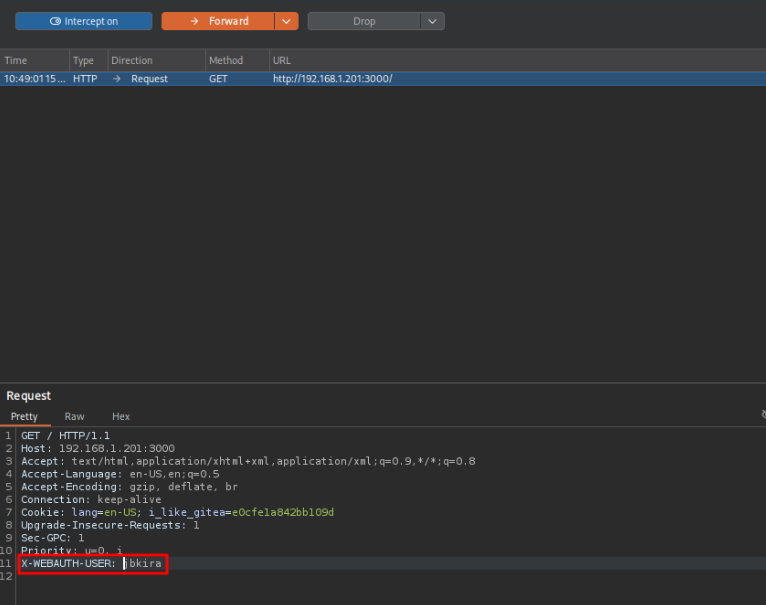 judgedbykira/cve-2026-20896-gitea-authentication-bypass
An explanation and PoC to exploit CVE-2026-20896 Authentication Bypass Vulnerability on Gitea. Being able to steal session tokens for valid users in…
 cerberusmrxi/cve-2025-48932-invision-community-sqli-exploit
CVE-2025-48932 - Unauthenticated SQL injection exploit for Invision Community ≤ 4.7.20. Fully automated exploitation with database enumeration,…
 jet-pentest/cve-2023-31779
Proof-of-concept exploit for stored XSS (CVE-2023-31779) in Wekan kanban board. Demonstrates JavaScript injection via reaction to comment, enabling…
 fevar54/cve-2026-3055---citrix-netscaler-memory-overread-poc
PoC de CVE-2026-3055: memory overread en Citrix NetScaler ADC/Gateway para filtrar session IDs.
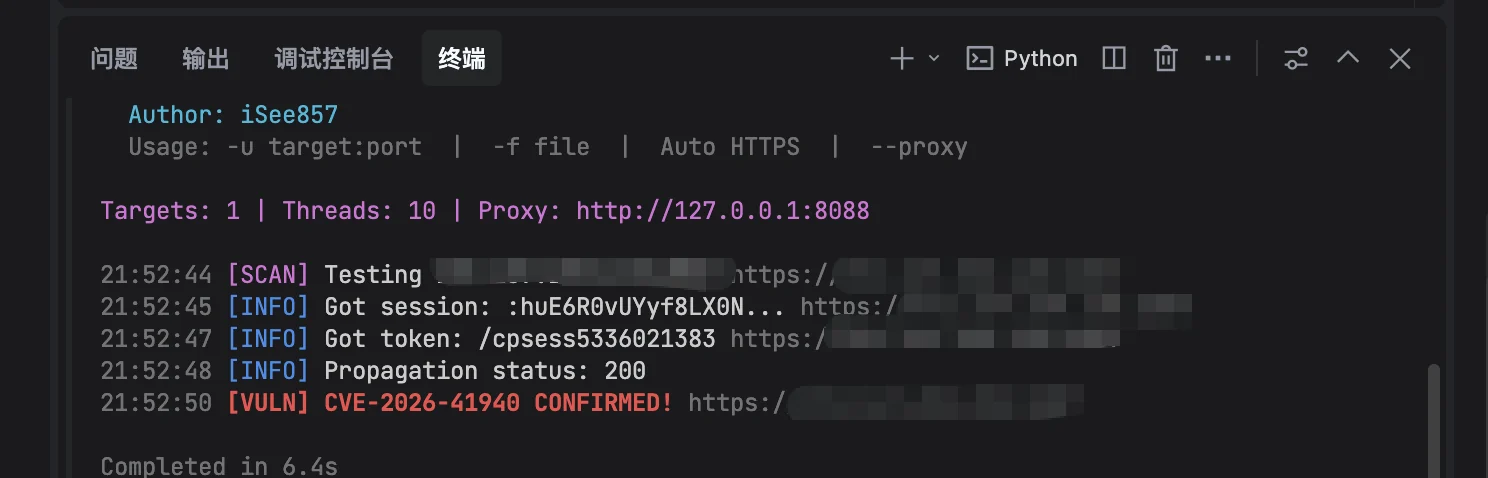 isee857/cpanel-whm-cve-2026-41940-authbypass
Scanner for cPanel & WHM authentication bypass (CVE-2026-41940) that detects vulnerable versions via CRLF injection and session manipulation, with…