
CVE-2023-2822-demo
 cberman/cve-2023-2822-demo
Simple flask application to implement an intentionally vulnerable web app to demo CVE-2023-2822.
ctfeducationlabs-practice+3
3
cberman/cve-2023-2822-demoSimple flask application to implement an intentionally vulnerable web app to demo CVE-2023-2822.
 sensepost/cve-2025-64446
A scanner for the FortiNet vulnerability CVE-2025-64446
 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 mister-joe/cve-2021-44593
Public disclosure and writeup of CVE-2021-44593, an unauthenticated SQL injection in Simple College Website leading to arbitrary file upload and…
 maikroservice/cve-2022-3949
XSS in Simple Cashiering System
 anomalousvectors/cve-2022-24785-poc-lab
Moment.js vuln lab
 geraldoalcantara/cve-2023-51802
Simple Student Attendance System v.1.0 - Cross-site scripting (XSS) vulnerabilities in attendance_report
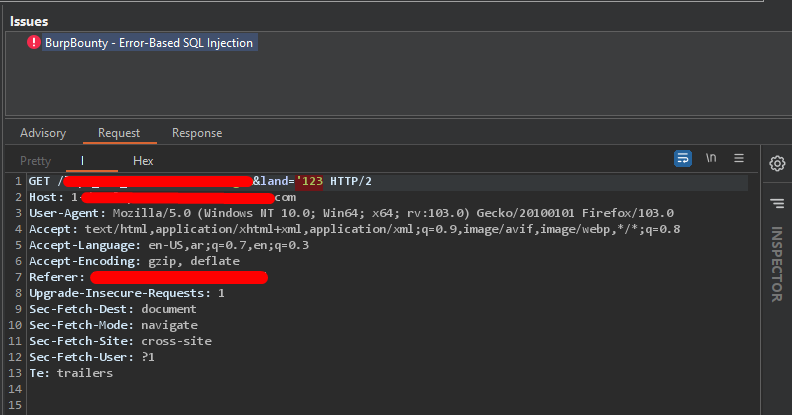 eslam3kl/sqlidetector
Simple python script supported with BurpBouty profile that helps you to detect SQL injection "Error based" by sending multiple requests with 14…
 4nner/cve-2019-9053
Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
 hattan515/poc-cve-2021-41773
Simple Python exploit script for Apache HTTPd 2.4.49 path traversal vulnerability (CVE-2021-41773). Supports single IP and file-based scanning.
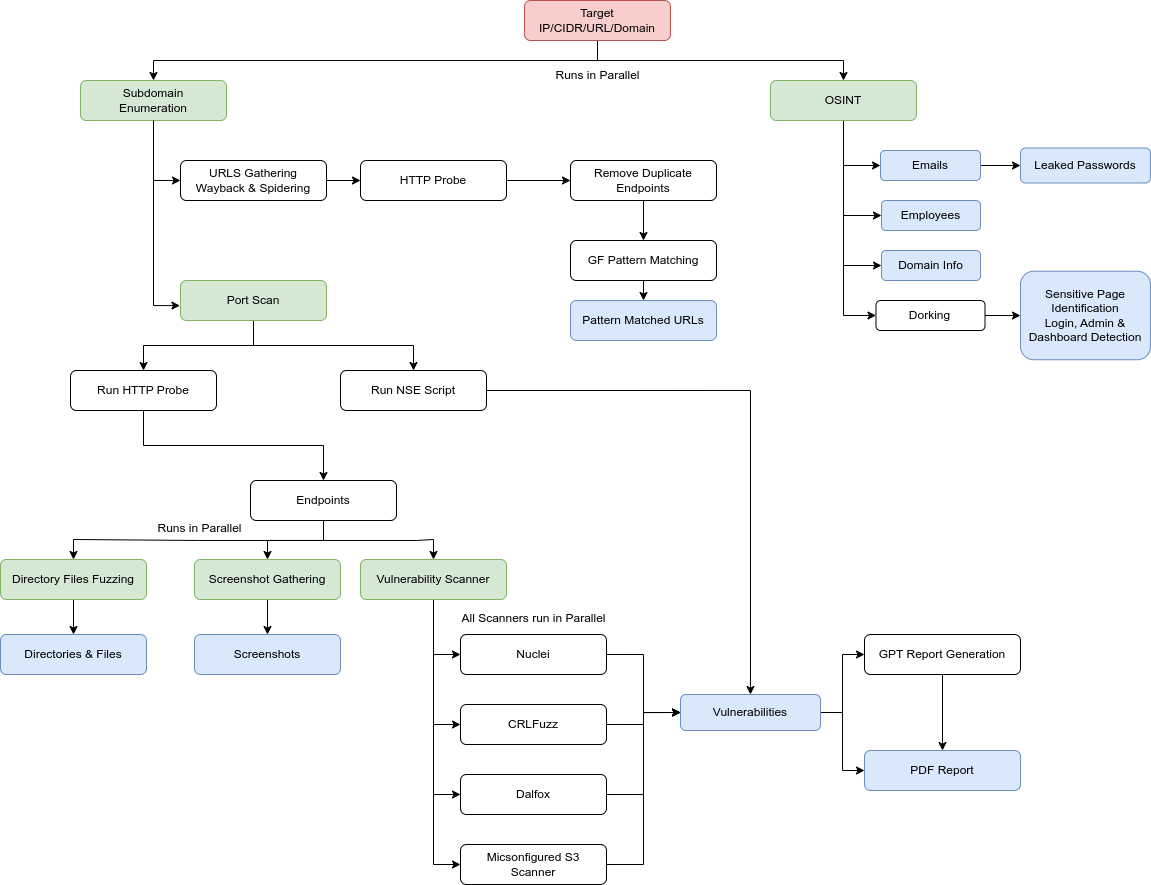 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 rxerium/cve-2023-6000
The Popup Builder WordPress plugin before 4.2.3 does not prevent simple visitors from updating existing popups, and injecting raw JavaScript in them,…
 xmendez/wfuzz
Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…
 amirzargham/cve-2023-0099-exploit
simple urls < 115 - Reflected XSS
 polosss/by-poloss..-..cve-2026-11912
Missing Authorization to Unauthenticated File Modification
 namelesssaint8/cve-2025-24813-poc
A simple, easy-to-use POC for CVE-2025-42813 (Apache Tomcat versions below 9.0.99).
 chandraprarikraj/cve-2023-50596
Proof-of-concept for CVE-2023-50596: a stored XSS vulnerability in Simple Image Stack Website (PHP/API v1.0) triggered via a crafted URL payload.
 m3ssap0/wordpress-really-simple-security-authn-bypass-exploit
Python exploit for CVE-2024-10924 authentication bypass in Really Simple Security < 9.1.2. Enables unauthenticated login as any existing WordPress…