

Archived
CVE-2025-54589
 bytereaper77/cve-2025-54589
PoC for CVE-2025-54589 – a reflected XSS vulnerability in Copyparty ≤ 1.18.6.
exploitationpenetration-testingvulnerability-analysis+2
bytereaper77/cve-2025-54589PoC for CVE-2025-54589 – a reflected XSS vulnerability in Copyparty ≤ 1.18.6.
 synacktiv/sharker
A simple, reliable and reasonably fast network capture analyzer.
 satriarizka/cve-2024-24919
A simple bash and python script to check for the vulnerability CVE-2024-24919
 thecyberfairy/cve-lfi-lab
A hands on lab investigating CVE-2025-39507 from a Tier 1 SOC analyst perspective. Includes log review in Microsoft Sentinel, IP analysis, real world…
 g4lb1t/pstf2
Passive Security Tools Fingerprinting Framework
 d3duct1v/cve-2022-41040
Python-based scanner for CVE-2022-41040 that tests single or multiple URLs for the vulnerability, with simple CLI interface and dependency on…
 eurogig/jankybank
Simple Java Front and Back end with bad log4j version featuring CVE-2021-44228
 ashiqrehan-21/mcp-inspector-cve-2025-49596
MCP-Inspector-vulncheck is a Python script that checks if an MCP Inspector server is vulnerable to CVE-2025-49596. It tests whether the /sse endpoint…
 ikoz/cert-pinning-flaw-poc
Simple script for testing CVE-2016-2402 and similar flaws
 z3n70/cve-2023-23752
simple program for joomla CVE-2023-23752 scanner for pentesting and educational purpose
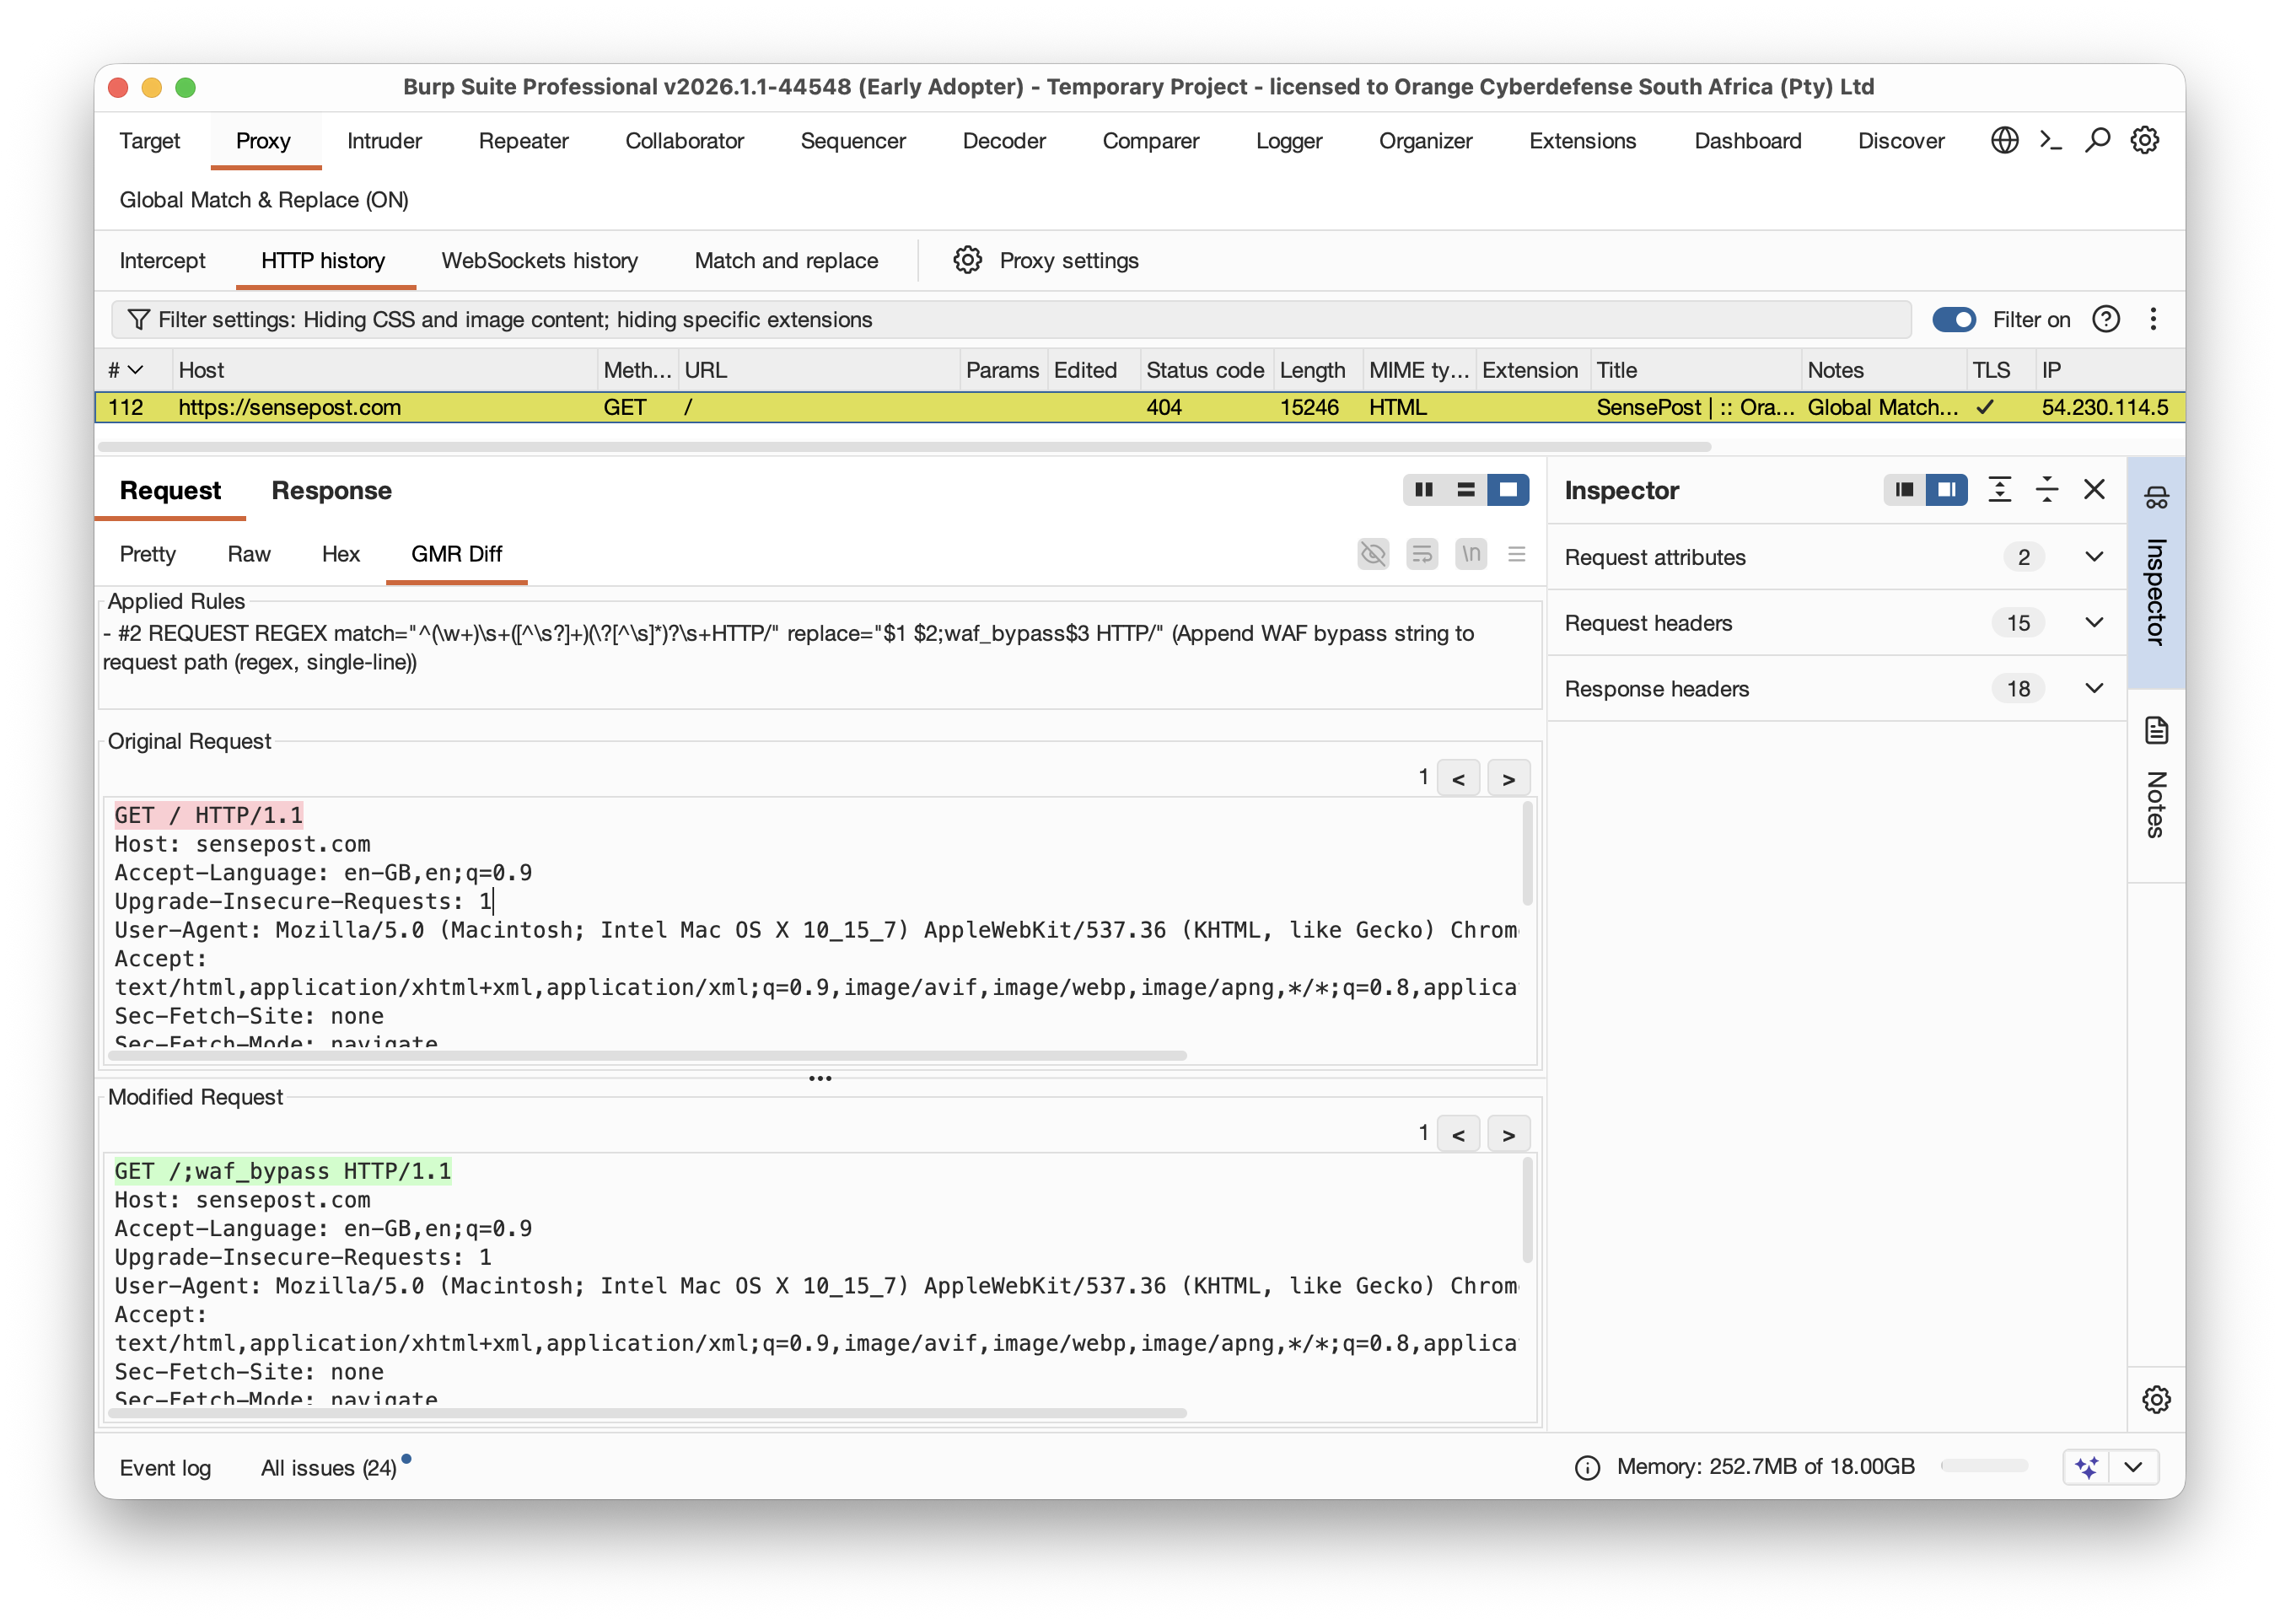 singe/burp_global_match_replace
Match & Replace rules for Portswigger's Burp that operate globally across all utilities.
 halencarjunior/dlkploit600
Simple Python script for D-Link vulnerability scan and test [CVE-2019-13101]
 trackflaw/cve-2024-10924-wordpress-docker
Vulnerable docker container for Really Simple Security (Free, Pro, and Pro Multisite) 9.0.0 – 9.1.1.1 – Authentication Bypass CVE-2023-50164
 dubs3c/injectus
CRLF and open redirect fuzzer
 0verl0ad/dumb0
A simple tool to dump users in popular forums and CMS :)
 cyberblackhole/domain-to-webapp
Bash script that enumerates subdomains via Subfinder, resolves IPs, and identifies live web applications hosted on a domain for reconnaissance and…
 ingokl/httpuploadexfil
A simple HTTP server for delivering and exfiltrating files/data during, for example, CTFs.