CVE-2024-28397-js2py-Sandbox-Escape

Detailed analysis of CVE-2024-28397, a sandbox escape vulnerability in js2py enabling RCE via Python object traversal. Includes code analysis, PoC,…

Detailed analysis of CVE-2024-28397, a sandbox escape vulnerability in js2py enabling RCE via Python object traversal. Includes code analysis, PoC,…

Firefox/Burp extension for security audits with single-click proxy, container profiles, postMessage logging, JS injection toolbox, and security…

HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…

You can read the writeup on this script here

Mitigate CVE-2018-6389 WordPress load-scripts / load-styles attacks

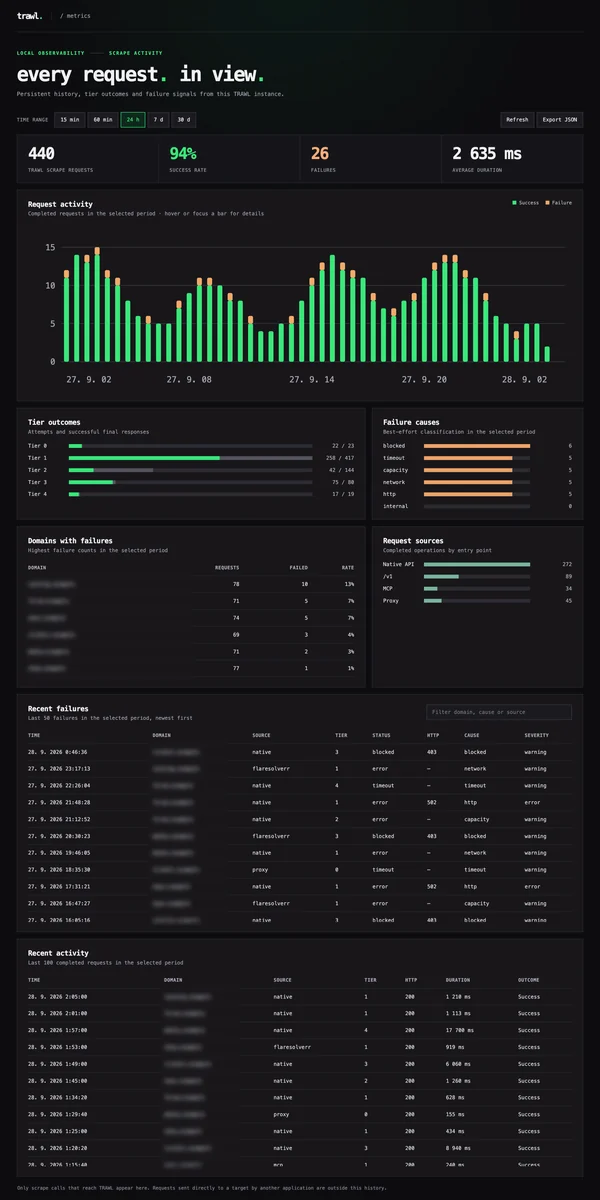
Self-hosted scraping engine — bypasses any JS challenge & captcha: Cloudflare, Turnstile, reCAPTCHA, hCaptcha, GeeTest. FlareSolverr & Byparr…

Technical documentation and proof-of-concept for CVE-2025-63700, an OAuth authentication bypass vulnerability in Clerk-js 5.88.0 allowing…

Safari XSS (CVE-2017-7038) https://support.apple.com/en-us/HT207923

React2Shell CVE-2025-55182: unauthenticated unsafe deserialization in React Server Components leading to reliable remote code execution via the…

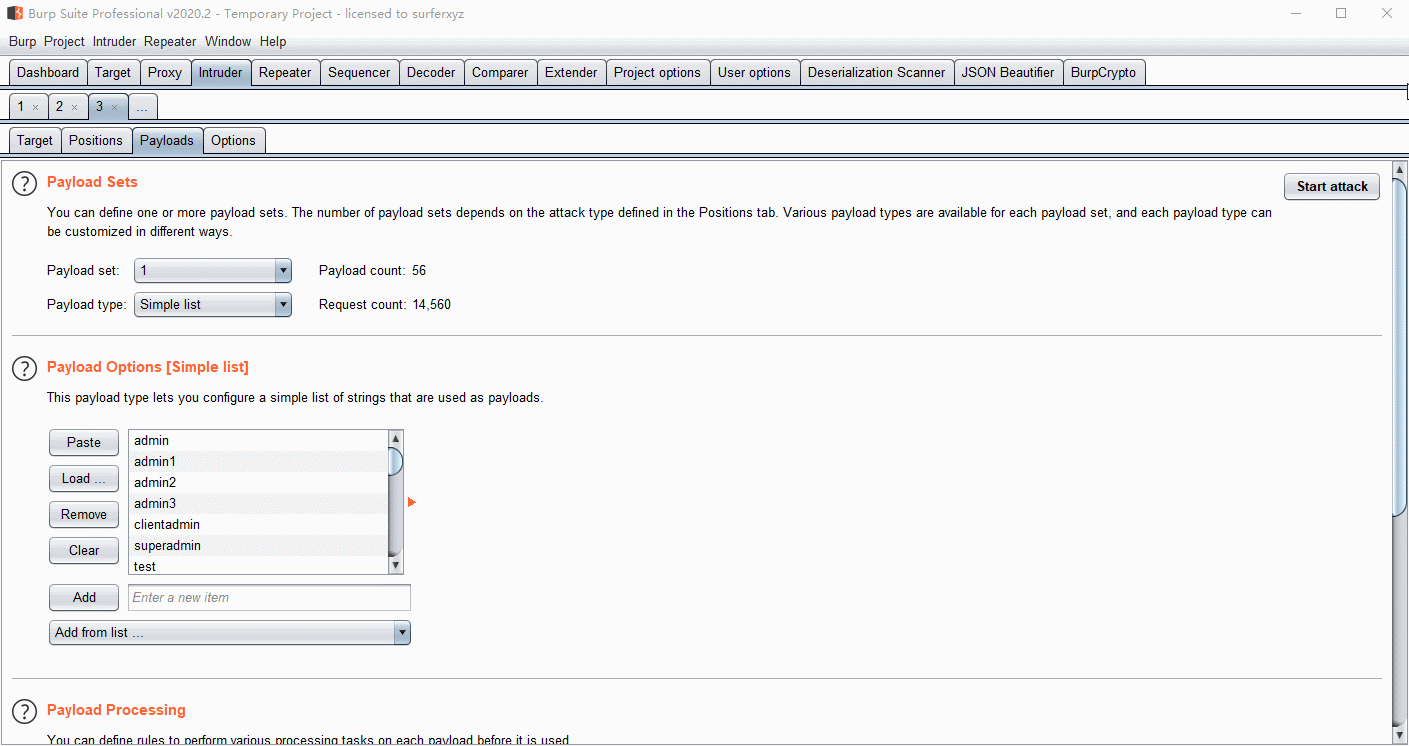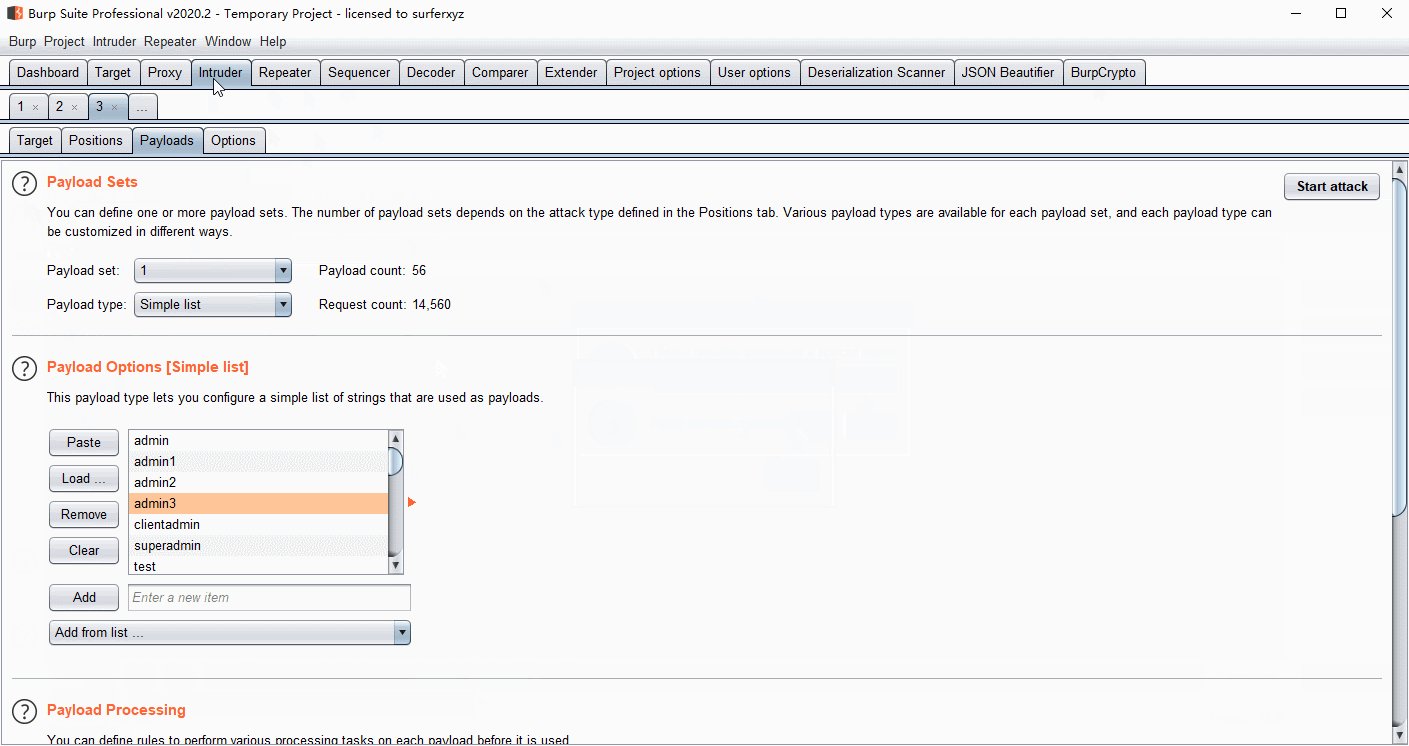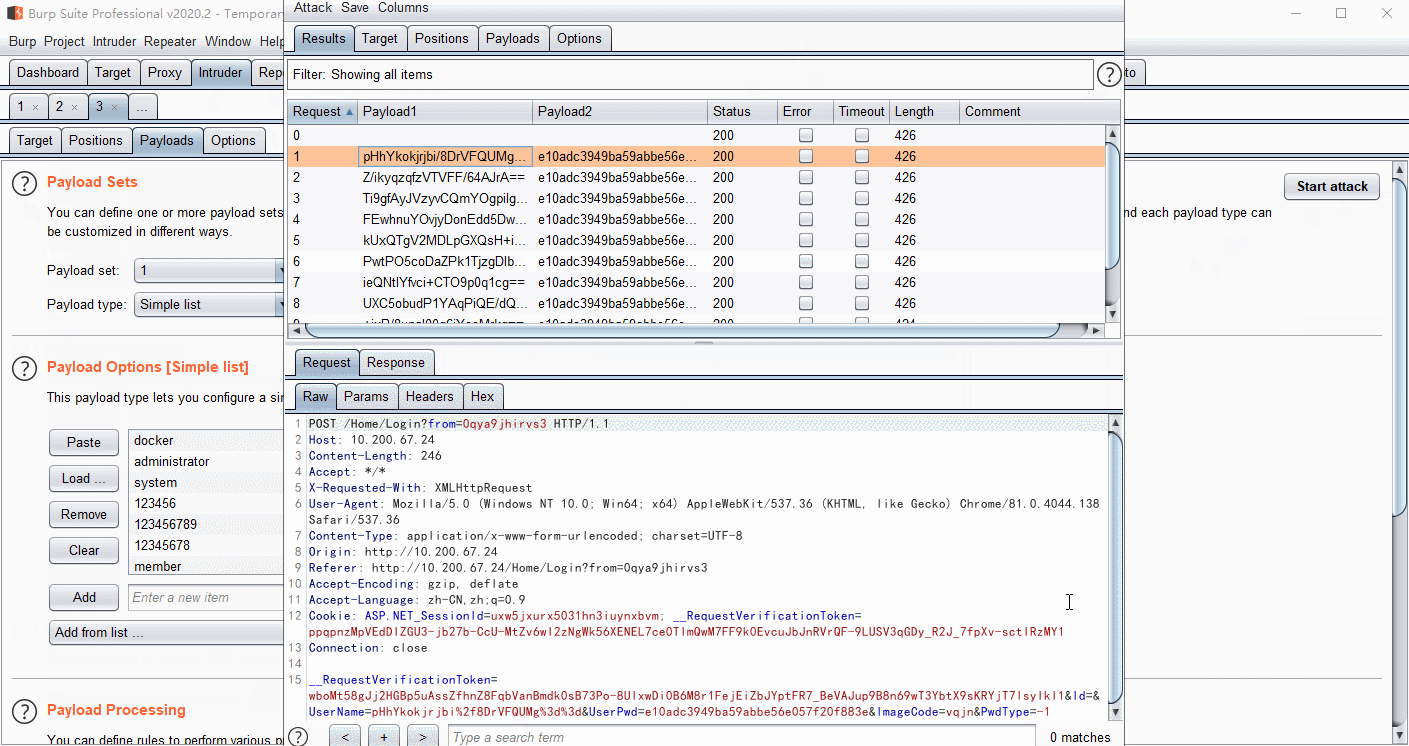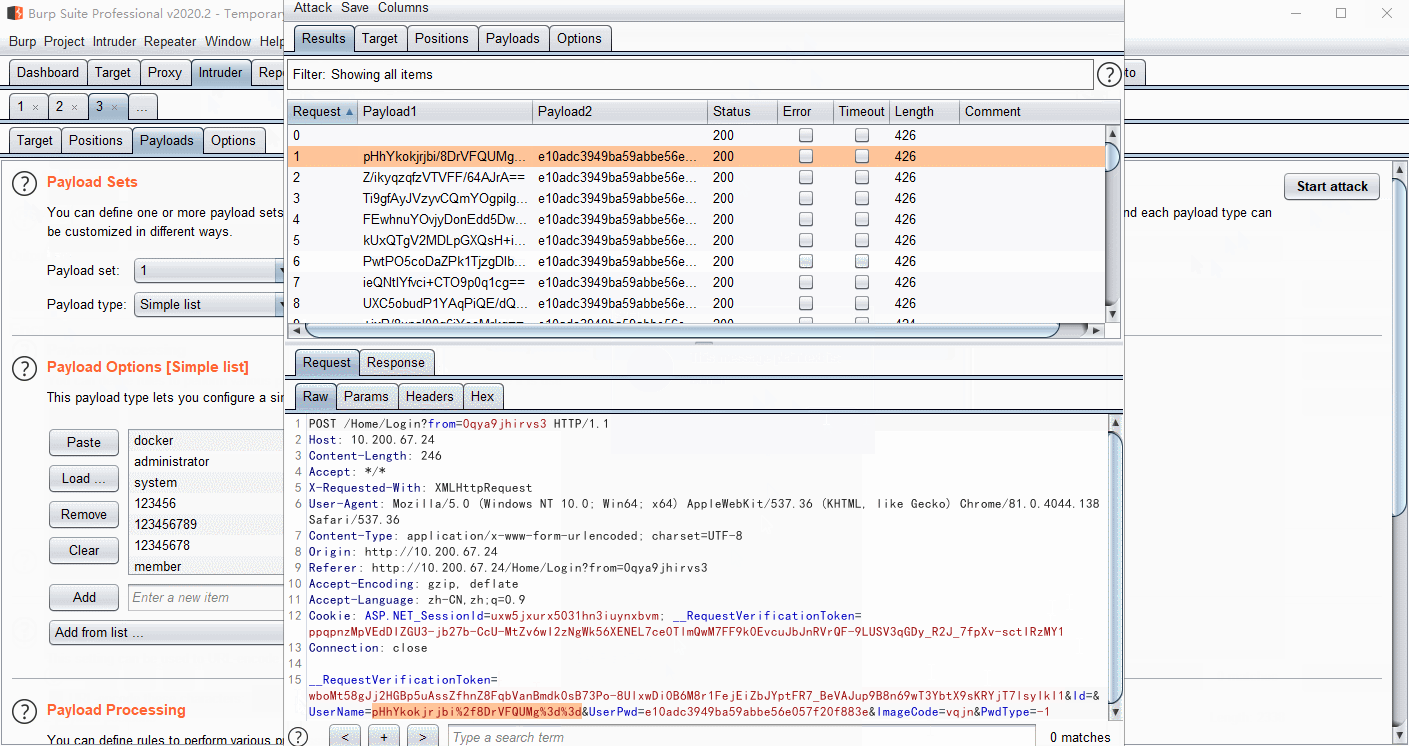
BurpSuite plugin for encrypting payloads with AES, RSA, DES, or custom JS code, enabling automated decryption of front-end encrypted traffic during…

Electron JS Browser To Find XSS Vulnerabilities Automatically

Burp Suite JS Beautifier

JS Archive List <= 6.1.5 - Unauthenticated SQL Injection

JS Job Manager < 1.1.9 - Unauthenticated Arbitrary Plugin Installation/Activation

Burp Suite Certified Practitioner - Portswigger - My notes - Guide

CVE-2022-23861: Multiple Stored Cross-Site Scripting in YSoft SafeQ

Tool Information Gathering & social engineering Write By [Python,JS,PHP]

Example on how to injection(currently under work) of keylogger js through Safari Extension(that part done)