
403bypasser
 yunemse48/403bypasser
Automates HTTP 403 access control bypass techniques using header manipulation, path obfuscation, and HTTP method conversion for web application…
ids-ips-evasioninformation-gatheringpenetration-testing+2
956
yunemse48/403bypasserAutomates HTTP 403 access control bypass techniques using header manipulation, path obfuscation, and HTTP method conversion for web application…
 0xdekster/reconnote
Web Application Security Automation Framework which recons the target for various assets to maximize the attack surface for security professionals &…
 tegal1337/0l4bs
Cross-site scripting labs for web application security enthusiasts
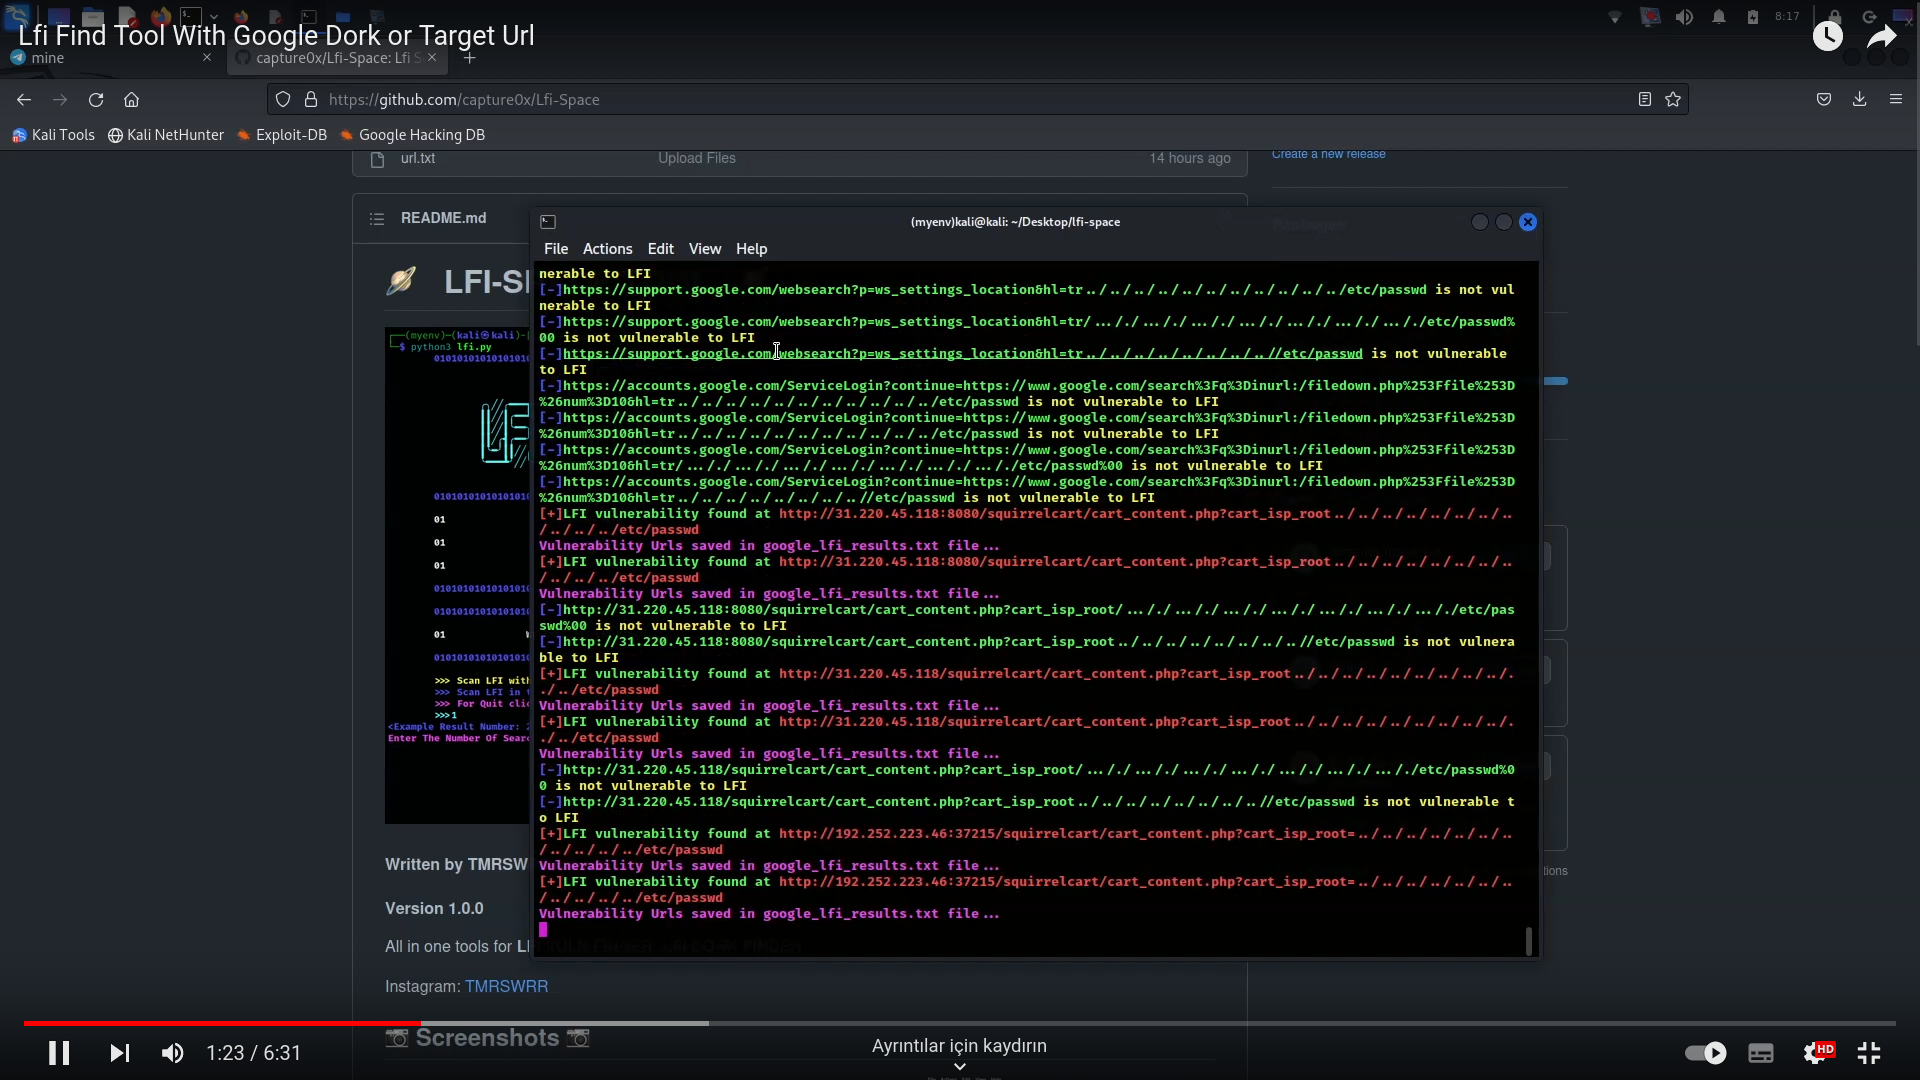 capture0x/lfi-space
Automated Local File Inclusion (LFI) vulnerability scanner with Google Dork search and targeted URL scan modes for web application security testing.
 owasp/owaspwebgoatphp
A deliberately vulnerable web application for learning web application security.
 bwasp/bwasp
BoB Web Application Security Project
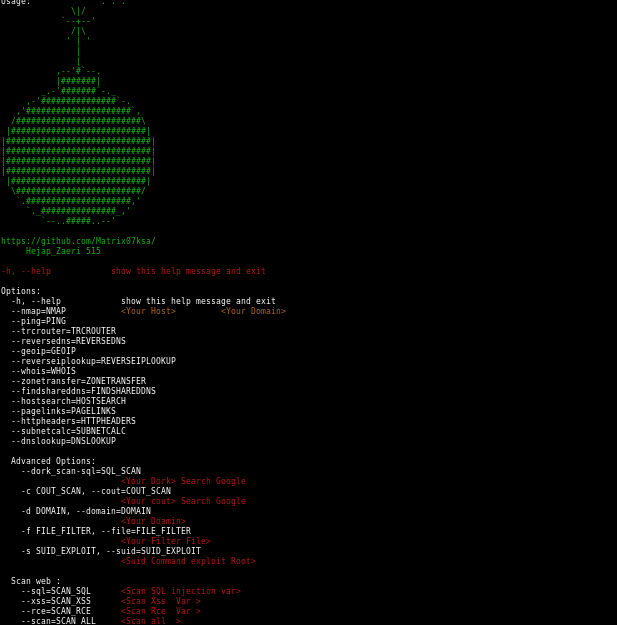 matrix07ksa/hackerinfo
Hackerinfo infromations Web Application Security
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
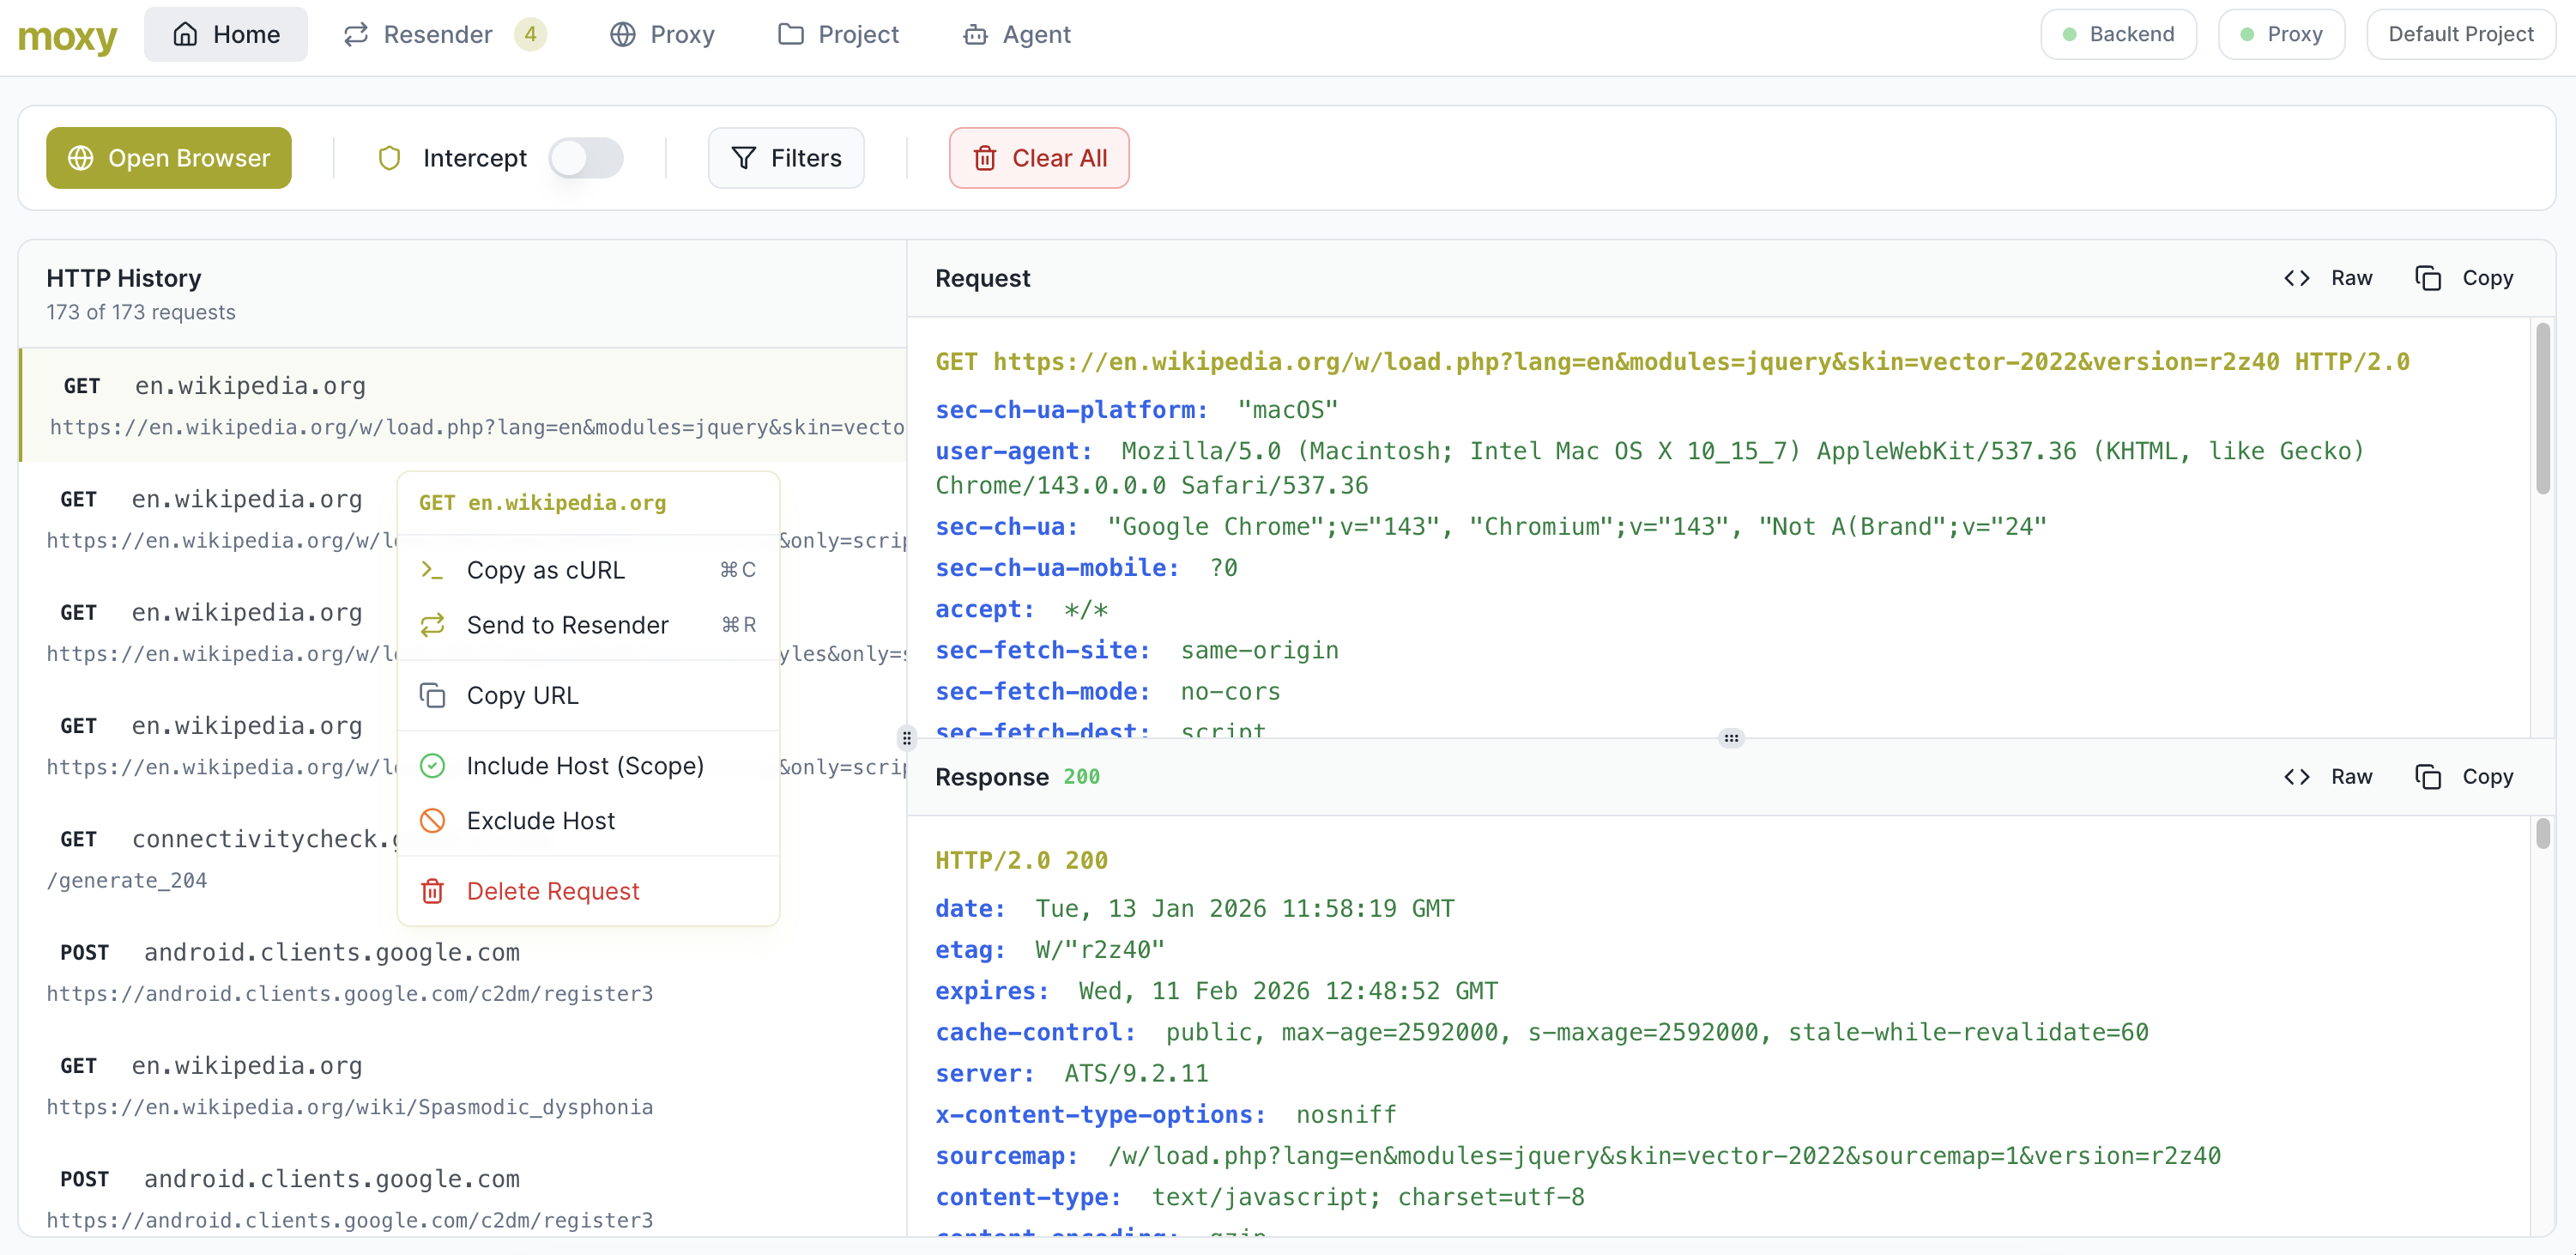 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 jas502n/burpsuite_pro_v1.7.37
Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…
 p0pr0ck5/lua-ffi-libinjection
LuaJIT FFI bindings for libinjection, providing SQL injection and XSS detection with context-specific APIs for web application security.
 cappricio-securities/burpflow
BurpFlow is one of the best Burp Suite automation tools for bug bounty hunters and penetration testers, widely used to load recon data via proxy and…
 zaproxy/zap-api-rust
Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…
 mehedi-hasan-sami98/dvwa-zap-pentest
Web application security assessment of DVWA using OWASP ZAP — vulnerability scanning, RCE (CVE-2012-1823) analysis, and remediation report.
 owasp/mimosa
Open-source web application security challenge platform with auto-approved registration, SQL dump generation, and Docker deployment for hands-on…
 shoucheng3/vert-x3__vertx-web_cve-2019-17640_3-9-3
Analysis and exploitation code for CVE-2019-17640, a vulnerability in Vert.x-Web. Provides a targeted test case for security researchers validating…
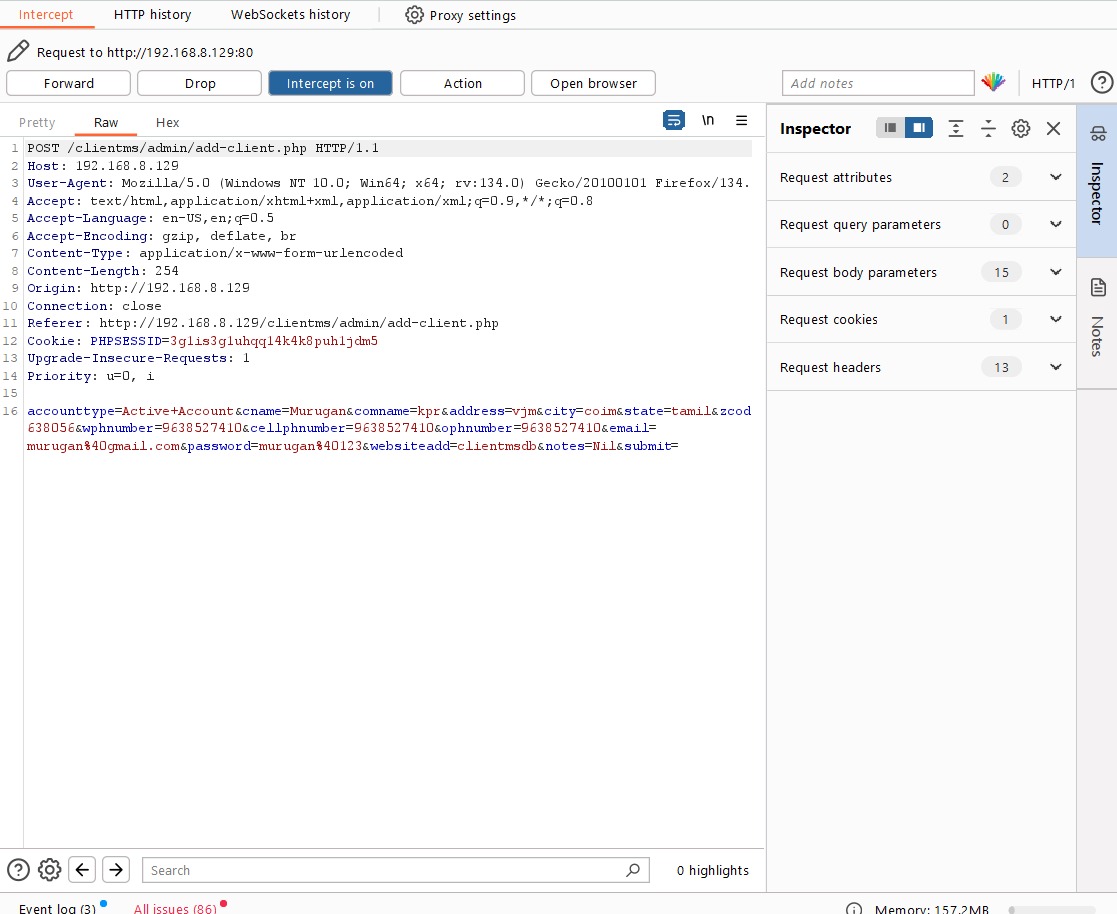 moulish2004/cve-2025-44603-csrf-leads_to_create_fakeusers
Proof-of-concept demonstrating a CSRF vulnerability in a PHP-based Client Management System, with HTML exploit code and mitigation strategies for web…
 imjdl/cve-2012-4431
Apache Tomcat source code repository for CVE-2012-4431, a Java servlet container vulnerability. Provides the vulnerable codebase for analysis and…