
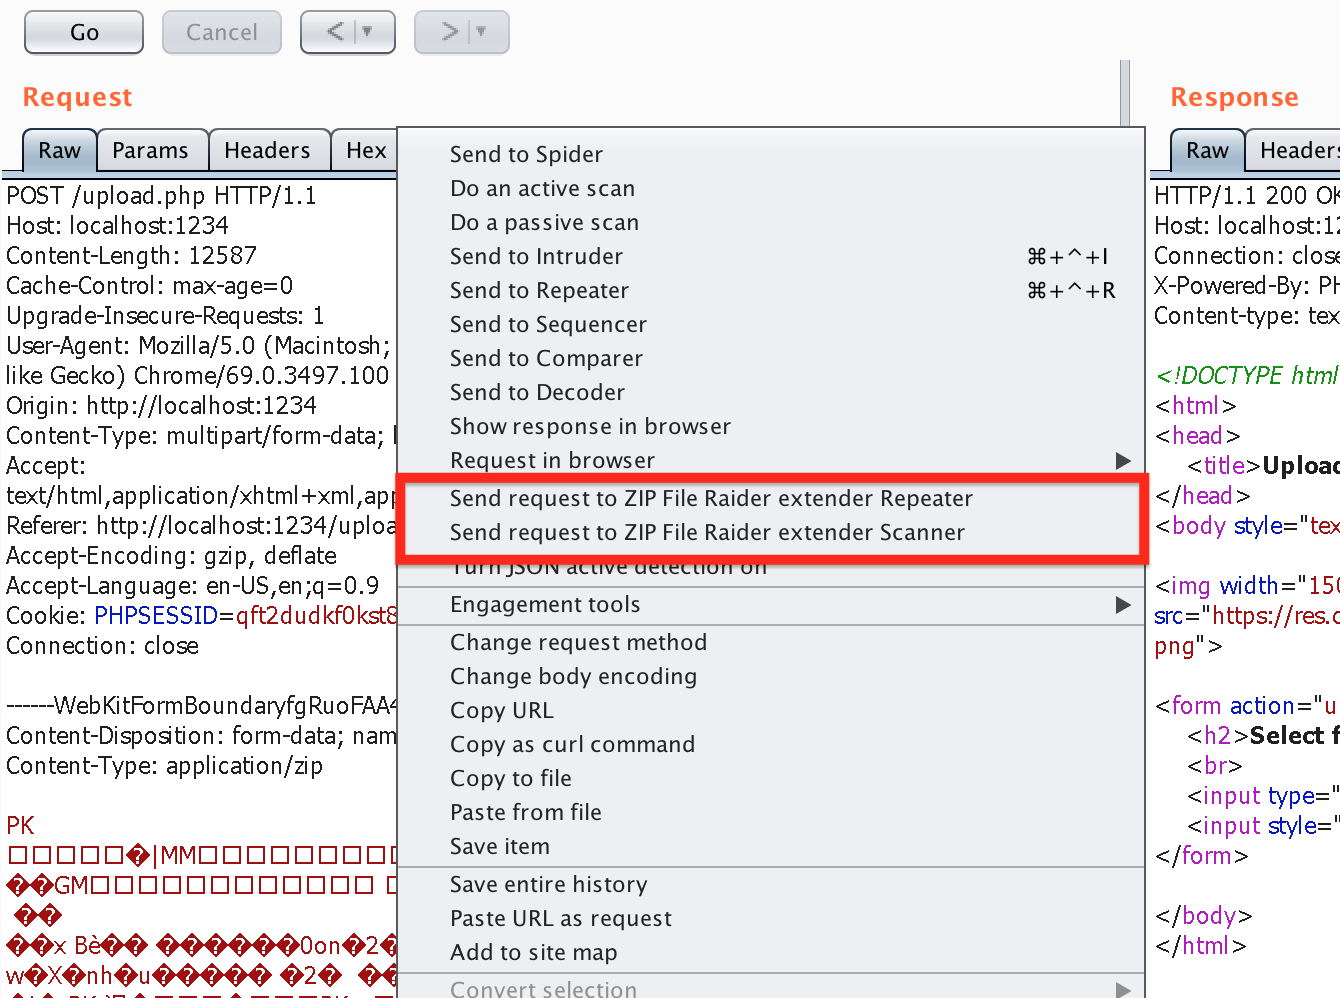
ZIPFileRaider
 destine21/zipfileraider
ZIP File Raider - Burp Extension for ZIP File Payload Testing
fuzzingpayload-generationpenetration-testing+2
716 years ago
destine21/zipfileraiderZIP File Raider - Burp Extension for ZIP File Payload Testing
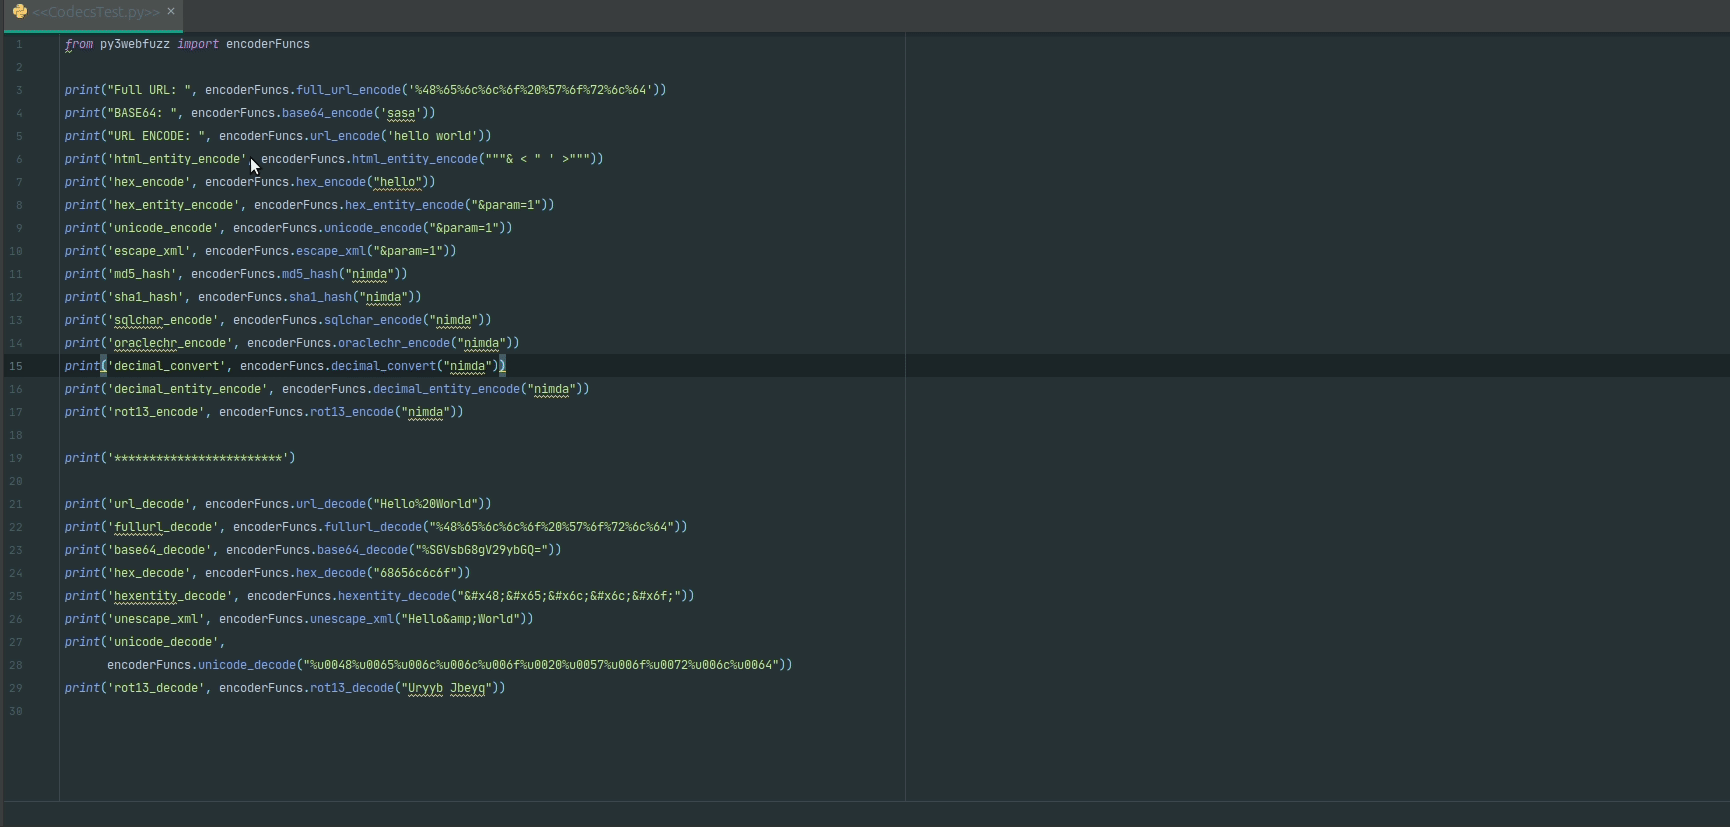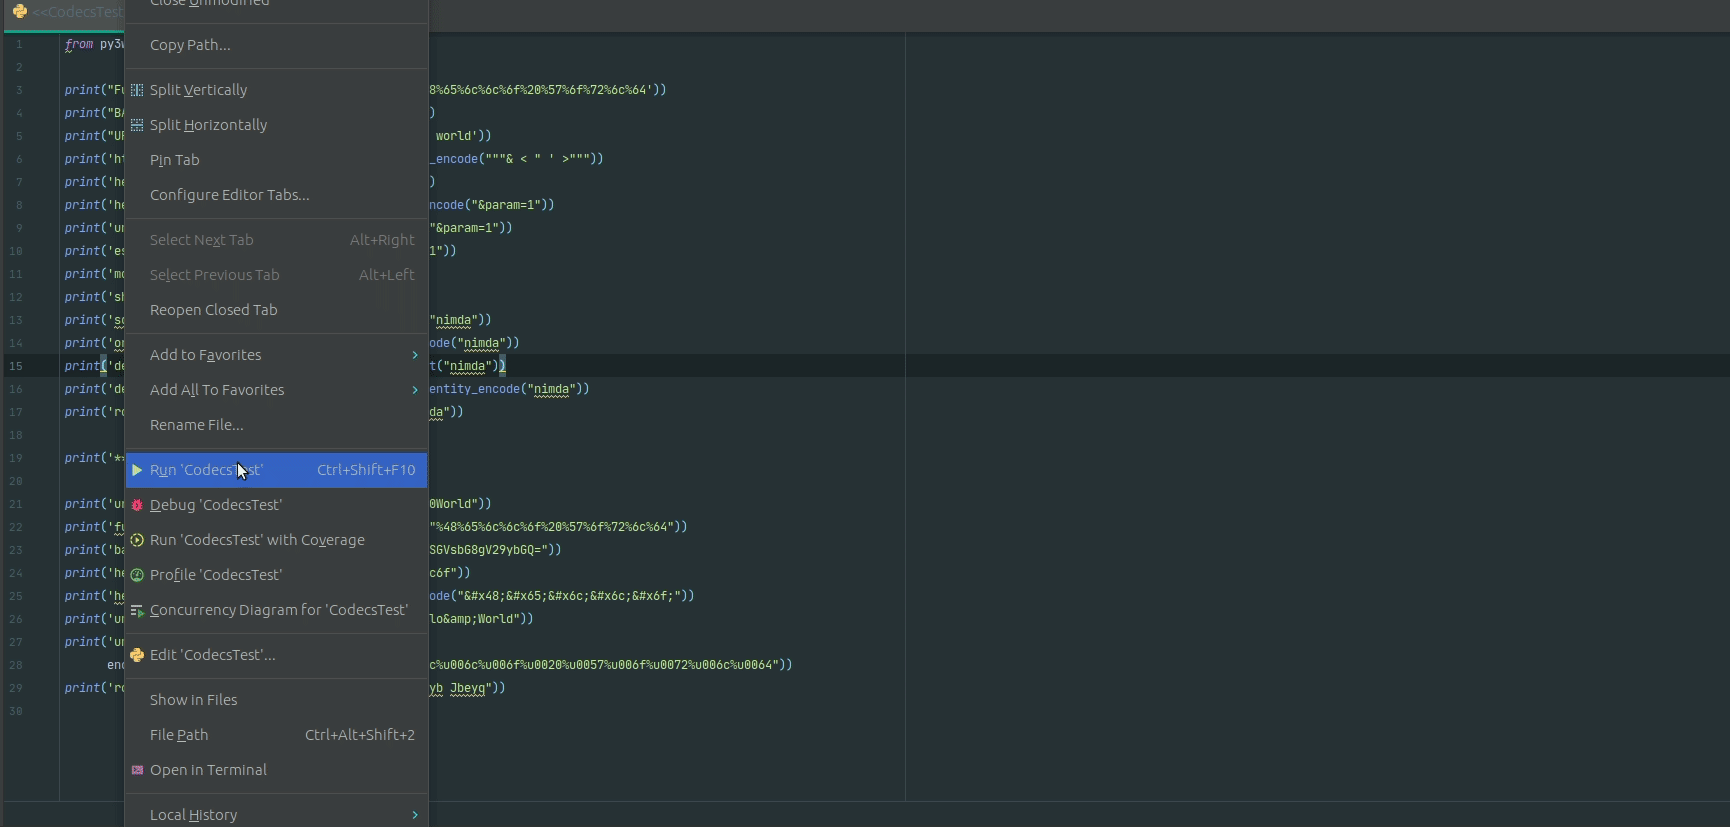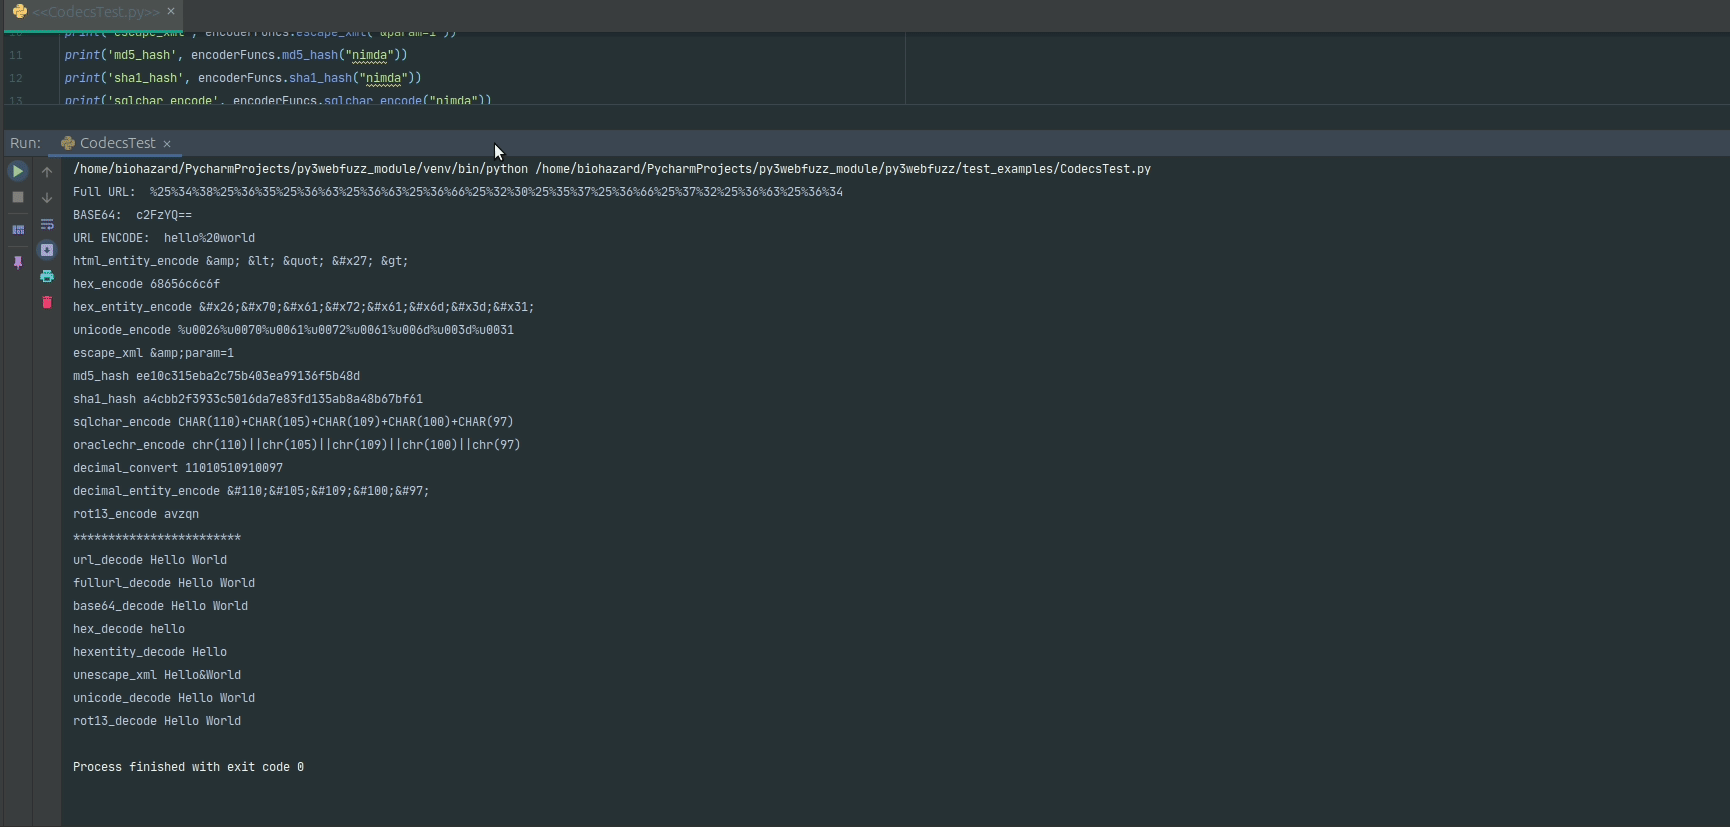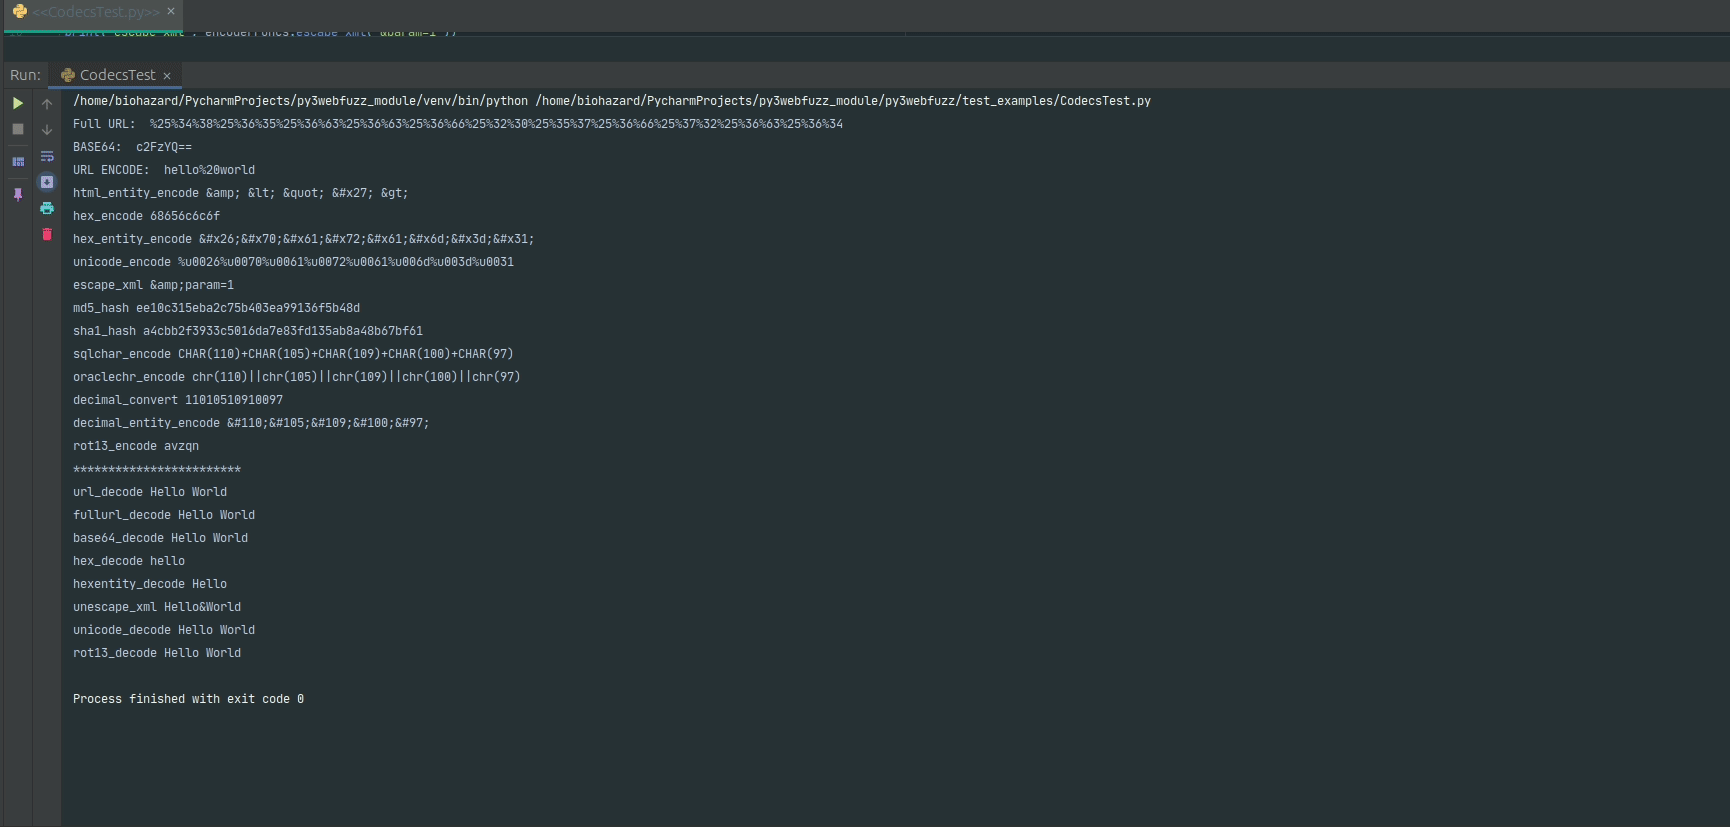 jangelesg/py3webfuzz
A Python3 module to assist in fuzzing web applications
 momika233/loxs-optimized
Web vulnerability scanner focused on automated XSS/CSP bypass payload testing and batch SQL injection detection, using SQLMap and reporting only…
 nxploited/cve-2025-7340
HT Contact Form Widget For Elementor Page Builder & Gutenberg Blocks & Form Builder. <= 2.2.1 - Unauthenticated Arbitrary File Upload
 xshadow-here/cve-2026-0740
Automated mass exploiter for CVE-2026-0740, an unauthenticated arbitrary file upload in Ninja Forms File Uploads plugin, enabling remote code…
 jenderal92/cve-2026-49049
Mass vulnerability scanner for CVE-2026-49049 – Unauthenticated Remote Code Execution in Joomla Helix3 plugin. Multi‑threaded, detects both executed…
 george0papasotiriou/cve-2026-11112-xxe-via-svg-image-upload
Demonstrates XXE via SVG upload with a vulnerable Flask/lxml parser and an exploit script for arbitrary file read, SSRF, and denial-of-service…
 nxploited/cve-2024-52380-exploit
Picsmize plugin for WordPress is vulnerable to arbitrary file uploads.
 anomalousvectors/cve-2024-4367-poc
POC for PDF JS' CVE-2024-4367 vuln
 siunam321/cve-2024-8743-poc
Proof-of-Concept script for WordPress plugin Bit File Manager version <= 6.5.7 Authenticated (Subscriber+) Limited JavaScript File Upload…
 andsnw/sockjs-dos-py
CVE-2020-7693: SockJS 0.3.19 Denial of Service POC
 moften/cve-2019-20372
Nginx CVE-2019-20372 PoC, Unauthenticated File Upload Exploit
 professor6t9/cve-2025-3515
CVE‑2025‑3515 — Drag and Drop Multiple File Upload for Contact Form 7
 nxploited/cve-2025-2807
Wordpress - Motors Plugin <= 1.4.64 - Arbitrary Plugin Installation Vulnerability
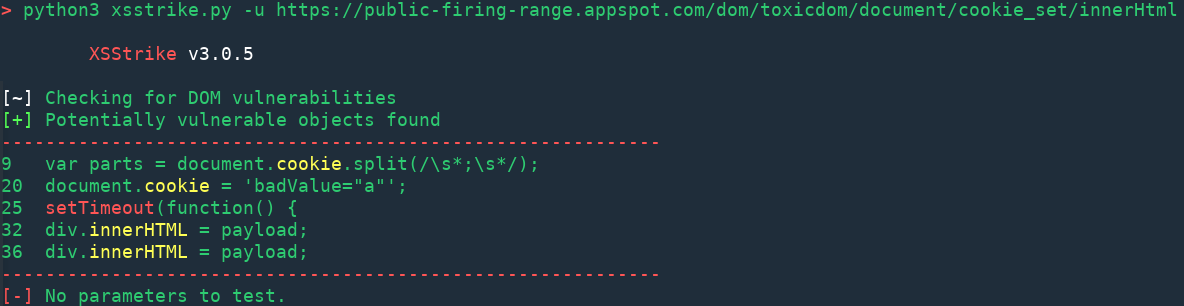
 t3l3machus/toxssin
An XSS exploitation command-line interface and payload generator.
 digitalocean/nginxconfig.io
⚙️ NGINX config generator on steroids 💉
 rsrdesarrollo/generator-burp-extension
Everything you need about Burp Extension Generation