CVE-2021-41773_Honeypot
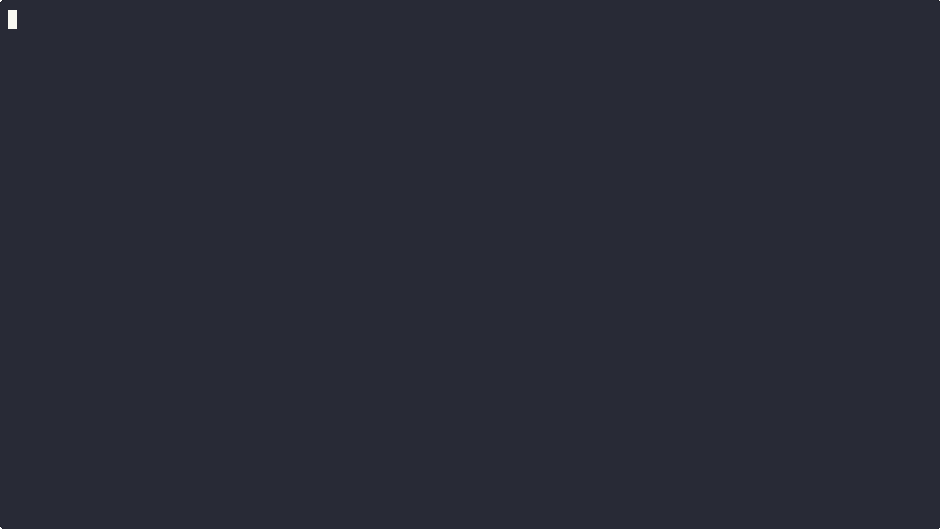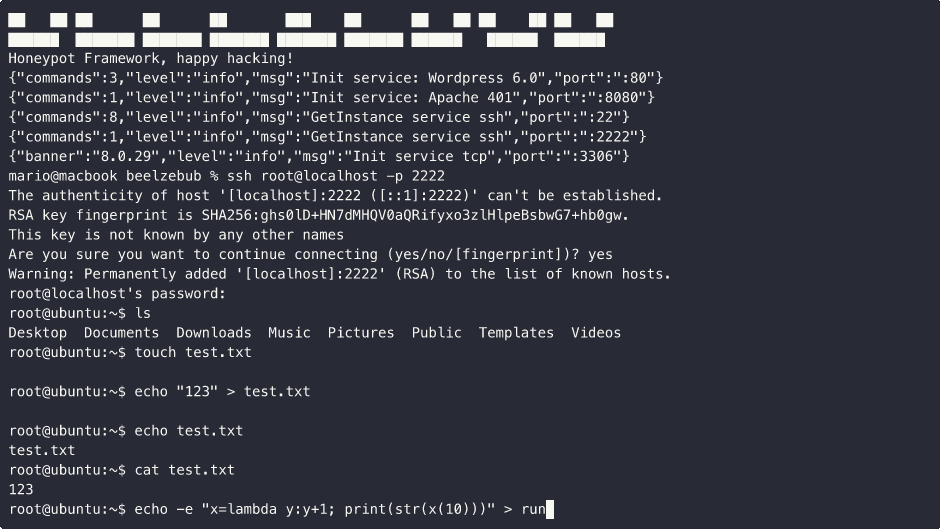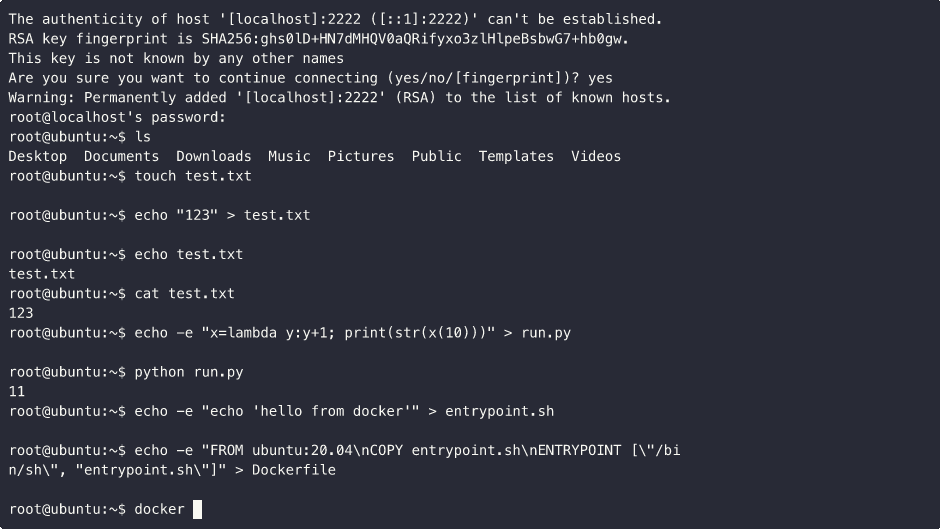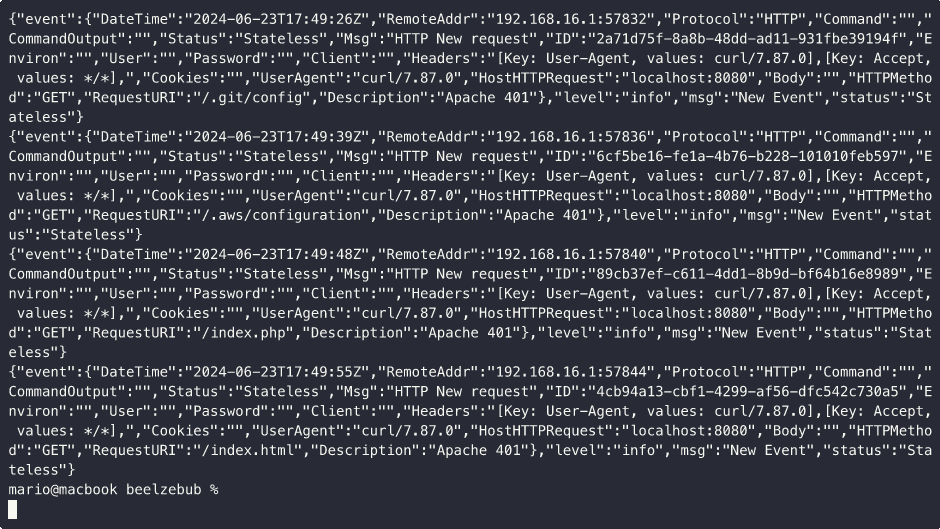
Lightweight honeypot for Apache HTTP Server path traversal vulnerability CVE-2021-41773, designed to capture and log exploitation attempts.

Lightweight honeypot for Apache HTTP Server path traversal vulnerability CVE-2021-41773, designed to capture and log exploitation attempts.

Http request smuggling vulnerability scanner

PoC of HTTP Request Smuggling in nodejs (CVE-2020-8287)

Proof-of-concept exploit for CVE-2023-41080, demonstrating URL validation bypass in Apache Tomcat to redirect users to arbitrary external sites via…

Vulnerable configuration Apache HTTP Server version 2.4.49/2.4.50

Vulnerable configuration Apache HTTP Server version 2.4.49

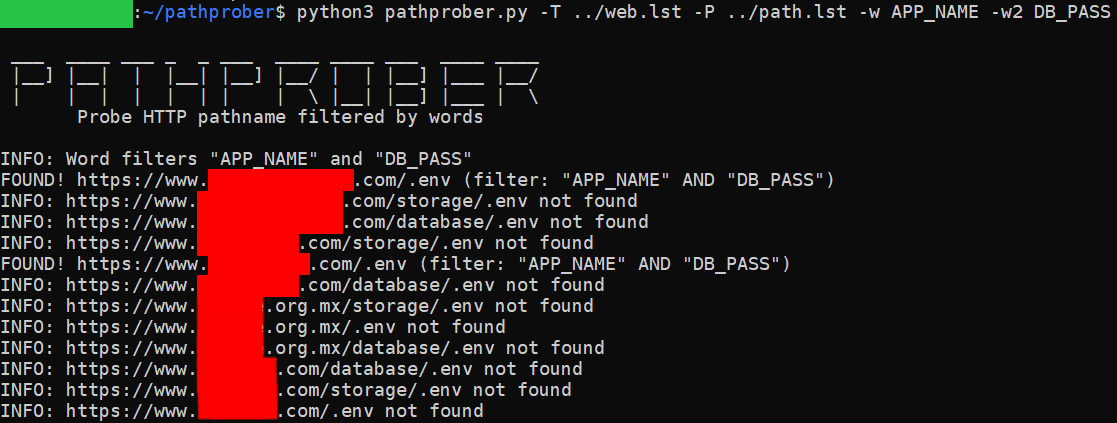
Probe and discover HTTP pathname using brute-force methodology and filtered by specific word or 2 words at once

Privaxy is the next generation tracker and advertisement blocker. It blocks ads and trackers by MITMing HTTP(s) traffic. Also check out my new…

Adaptive web scraping framework with anti-bot bypass, automatic element relocation, concurrent crawling, proxy rotation, and browser automation for…

The successor to reDuh, pwn a bastion webserver and create SOCKS proxies through the DMZ. Pivot and pwn.

Low bandwidth DoS tool. Slowloris rewrite in Python.

A secure low code deception runtime framework, leveraging AI for System Virtualization.

Burp extension to evade TLS fingerprinting. Bypass WAF, spoof any browser.

A curated collection of top-tier penetration testing tools and productivity utilities across multiple domains. Join us to explore, contribute, and…

TCP tunneling over HTTP/HTTPS for web application servers

Command-line tool to scan Google search results for vulnerabilities

A better whois and domain intelligence toolkit

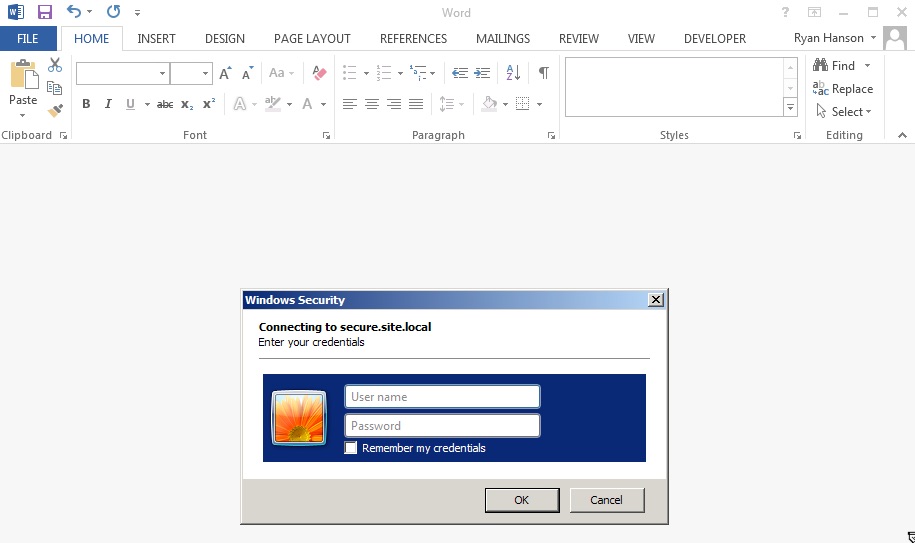
An SSL Enabled Basic Auth Credential Harvester with a Word Document Template URL Injector