
Burp_CVE-2025-31324
 blueowl-overlord/burp_cve-2025-31324
Python-based Burp Suite extension is designed to detect the presence of CVE-2025-31324
api-security-testingexploitationpenetration-testing+3
blueowl-overlord/burp_cve-2025-31324Python-based Burp Suite extension is designed to detect the presence of CVE-2025-31324
 randomrobbiebf/cve-2023-6289
Swift Performance Lite <= 2.3.6.14 - Missing Authorization to Unauthenticated Settings Export
 shoucheng3/perwendel__spark_cve-2018-9159_2-7-1
Lightweight Java 8 web framework with routing, filters, and static file serving. Includes security advisory for older versions and CRUD API examples.
 shoucheng3/perwendel__spark_cve-2018-9159_2_7_2_fixed
Lightweight Java 8 web framework for building REST APIs and web applications, with built-in routing, static file serving, and template engine support.
 havoc10-sw/detect_polyfill_cve-2024-38537-
Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.
 corgizz/springcloud
Spring Cloud Config CVE-2019-3799|CVE_2020_5410 漏洞检测
 t0xodile-swig/http3-adapter
Burp Suite extension that intercepts requests and sends them over HTTP/3, converting responses back for Burp, with support for kettled requests and…
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…
 wkeeling/selenium-wire
Extends Selenium's Python bindings to give you the ability to inspect requests made by the browser.
 google/martian
Martian is a library for building custom HTTP/S proxies
 gsmith257-cyber/graphcrawler
GraphQL automated security testing toolkit
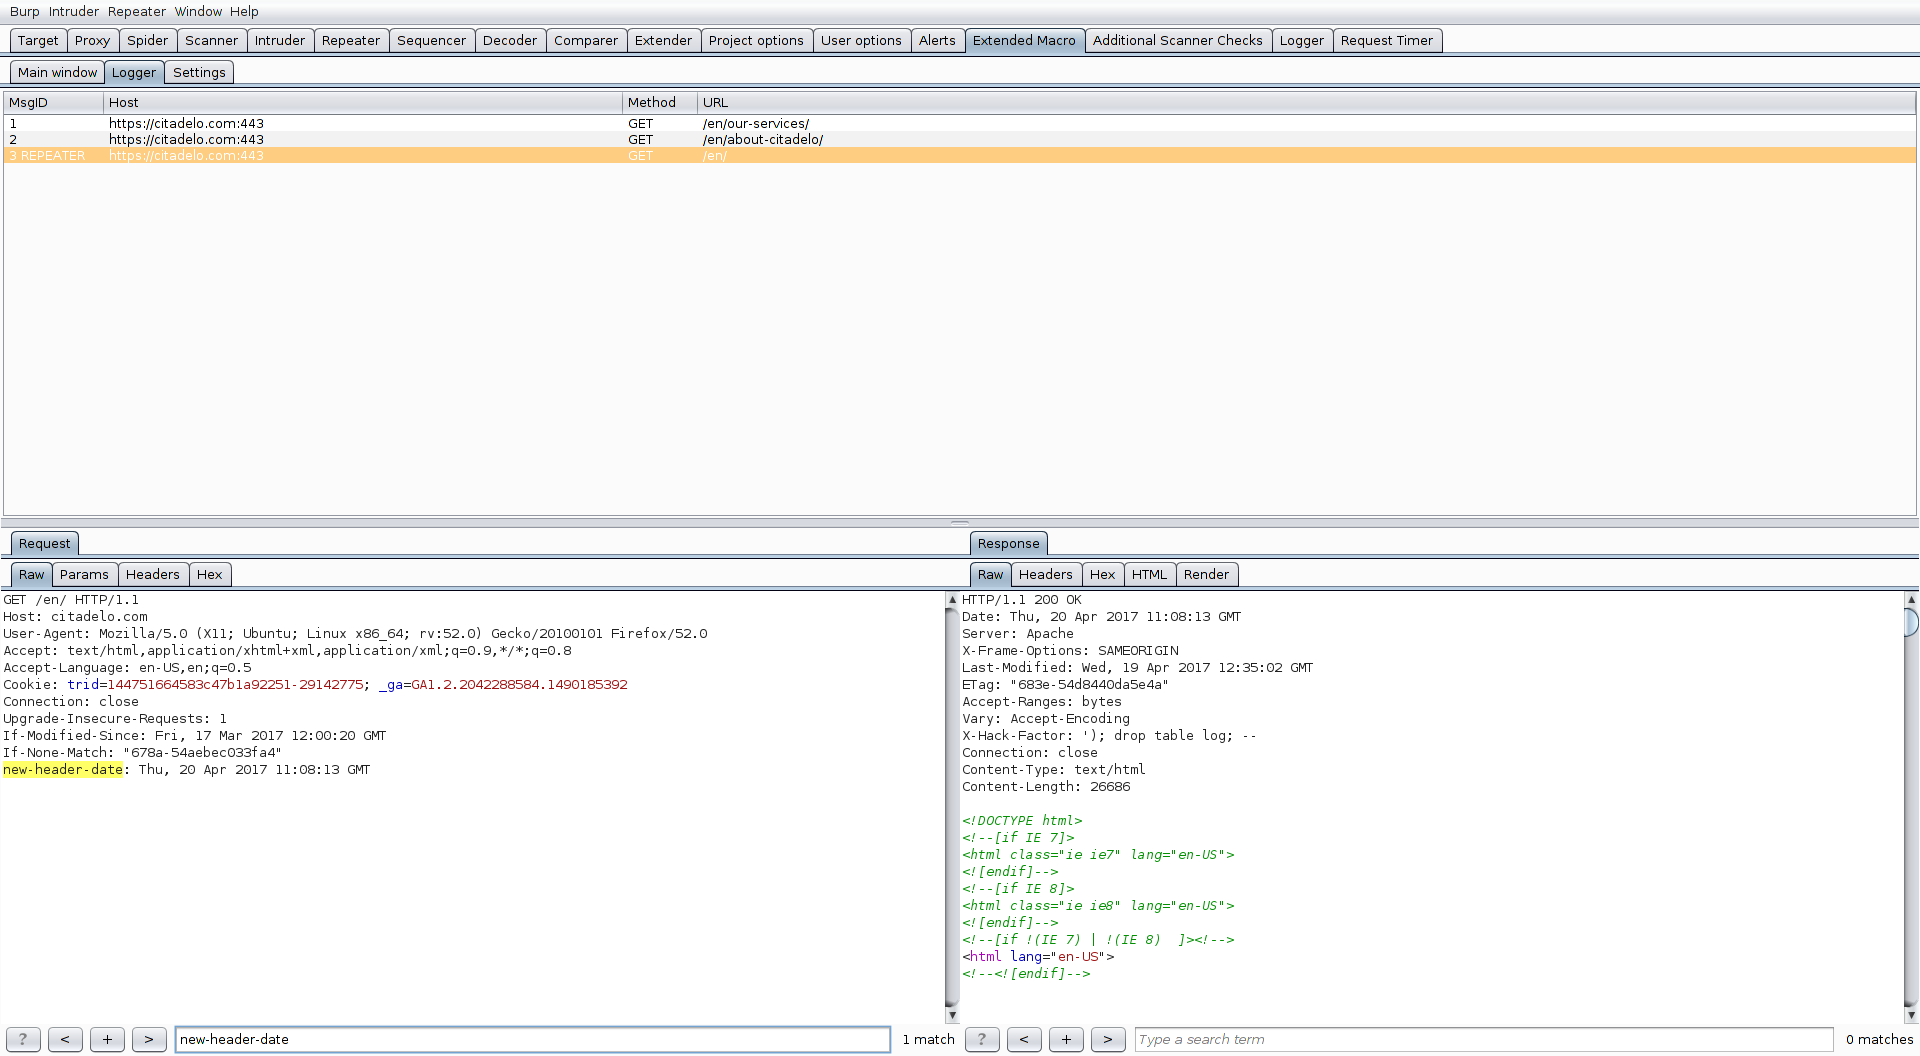 fruh/extendedmacro
ExtendedMacro - BurpSuite plugin providing extended macro functionality
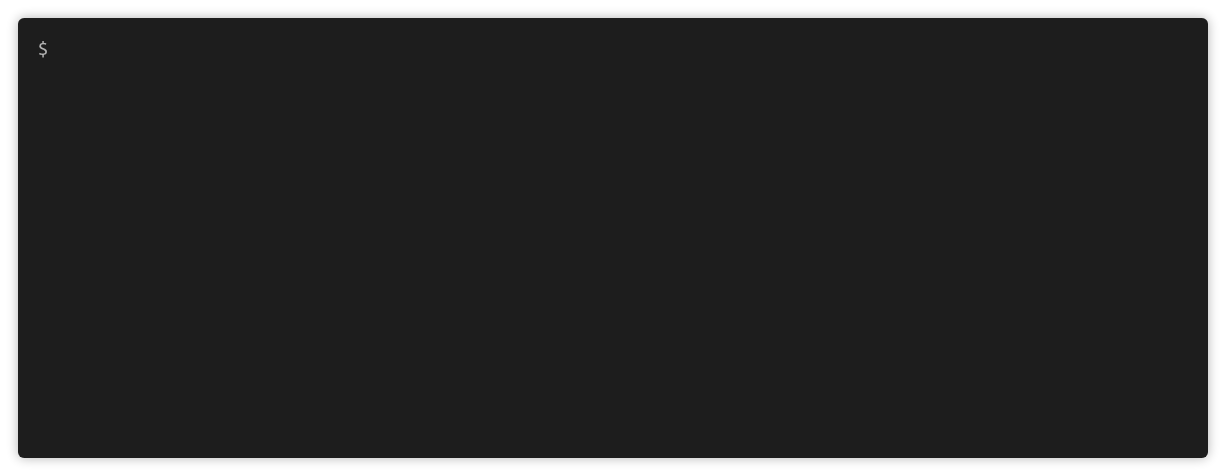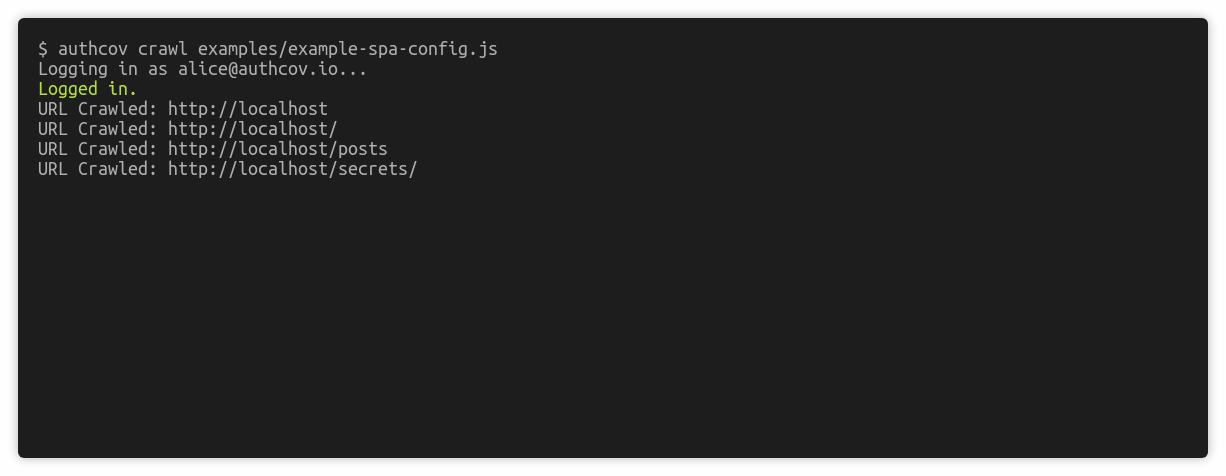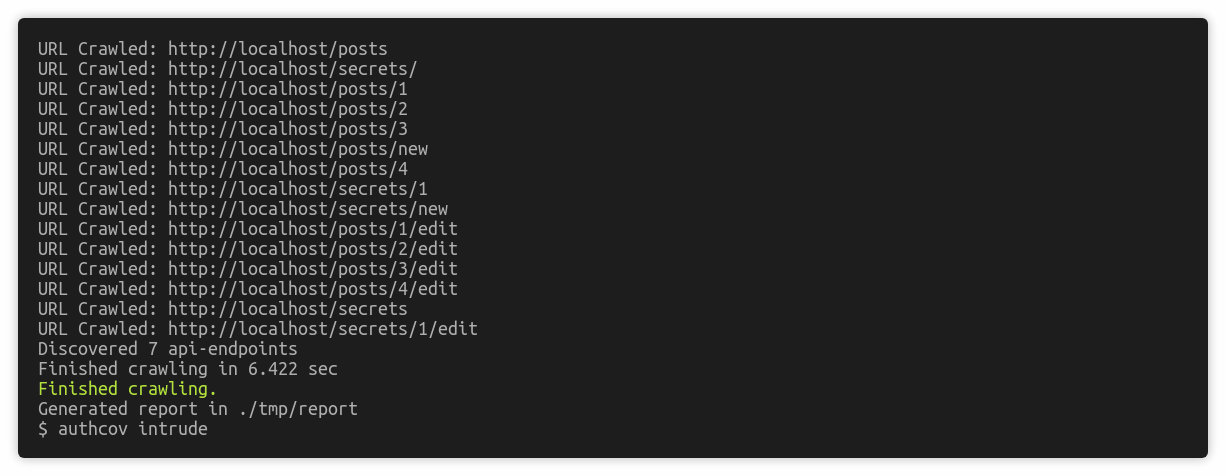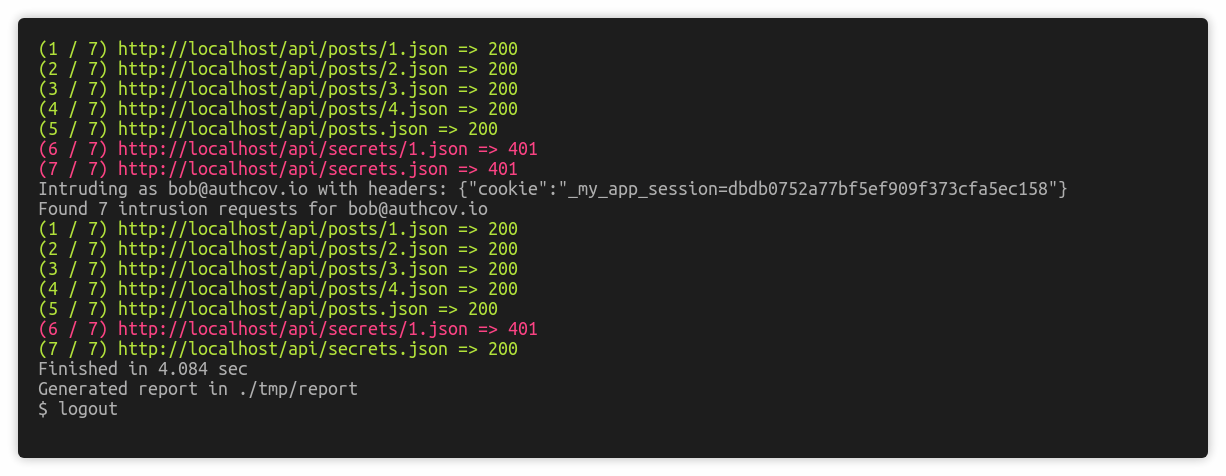 authcov/authcov
Web app authorisation coverage scanning
 sh1yo/request_smuggler
Http request smuggling vulnerability scanner
 rapid7/hackazon
A modern vulnerable web app
 openstack-archive/syntribos
Python API security testing tool from OpenStack Security Group
 vmware-archive/burp-rest-api
REST/JSON API to the Burp Suite security tool.
 google/nogotofail
An on-path blackbox network traffic security testing tool