Serdyuk-DO-homework-CVE-2021-41773

Proof-of-concept exploit script for CVE-2021-41773, a path traversal vulnerability in Apache HTTP Server 2.4.49, enabling directory traversal and…

Proof-of-concept exploit script for CVE-2021-41773, a path traversal vulnerability in Apache HTTP Server 2.4.49, enabling directory traversal and…

Apache HTTP Server 2.4.23 vulnerability study (CVE-2016-8740)

Detects Apache HTTP Server path traversal vulnerabilities (CVE-2021-41773, CVE-2021-42013) by checking for exposure of /etc/passwd through…

Proof of concept demonstrating Server-Side Request Forgery in ChatGPT, allowing attackers to force the AI to make arbitrary HTTP requests, exposing…

HTTP Request Smuggling

This Python script checks for the presence of CVE-2024-40898, a critical vulnerability in Apache HTTP Server that may allow SSL/TLS certificate…

Technical research paper analyzing CVE-2024-38476, a critical Apache HTTP Server vulnerability enabling SSRF, information disclosure, and potential…

Python test client that sends HTTP GET requests with oversized Authorization headers to trigger header-parsing bugs like CVE-2025-4476. For…

Python script to check for CVE-2023-2745 vulnerability by sending crafted HTTP requests to a target URL and analyzing responses.

An issue was discoverd in Overhang.IO (tutor-open-edx) (overhangio/tutor) 20.0.2 allowing local unauthorized attackers to gain access to sensitive…

🦀 Stealth HTTP client for Rust . mimics real browser TLS fingerprints for undetectable requests. Fast, type-safe, and built for precision networking.

Proof-of-concept for CVE-2023-36643: an incorrect access control vulnerability in ITB-GmbH TradePro v9.5 that allows remote attackers to enumerate…

Proof-of-concept exploit for Apache Tomcat CVE-2018-1304, demonstrating remote code execution via crafted HTTP requests for security testing and…

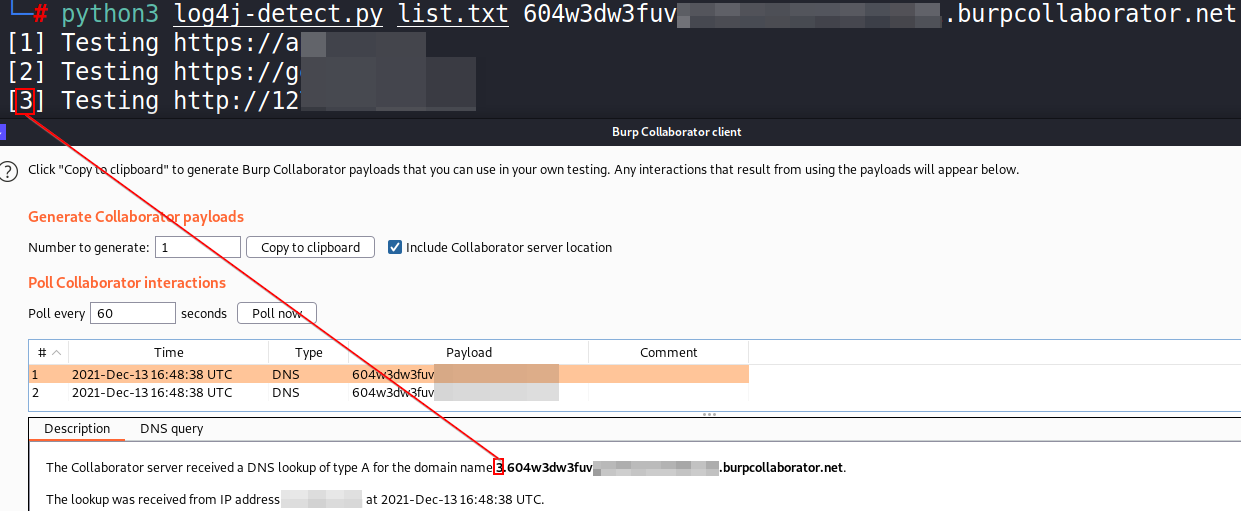
Multithreaded Python scanner that detects Log4Shell (CVE-2021-44228) by sending crafted HTTP requests with JNDI payloads and monitoring DNS callbacks…

Proof-of-concept exploit for CVE-2017-15715, an Apache HTTP Server vulnerability allowing file upload bypass via crafted Content-Disposition headers.

Proof-of-concept exploit for CVE-2014-7816 targeting Undertow Java web server, demonstrating a directory traversal vulnerability in the HTTP server's…

Python toolkit to audit Apache HTTP Server against CVE-2026-23918 (HTTP/2 double-free RCE) and 4 related CVEs. Passive scanner with ALPN verification…

Python script to scan networks for Cisco IOS XE devices vulnerable to CVE-2023-20198, detecting implants via HTTP status and response analysis.