Nuclei-TemplatesNuclei-Templates-CVE-2017-17736

Nuclei template for detecting CVE-2017-17736, a command injection vulnerability in ntopng, by sending crafted HTTP requests and matching response…

Nuclei template for detecting CVE-2017-17736, a command injection vulnerability in ntopng, by sending crafted HTTP requests and matching response…

Exploit for CVE-2019-17638 targeting Jetty Java HTTP server, enabling remote code execution via crafted HTTP requests for security testing and…

Repository containing nse script for vulnerability CVE-2022-21907. It is a component (IIS) vulnerability on Windows. It allows remote code execution.…

CVE 2023 25690 Proof of concept - mod_proxy vulnerable configuration on Apache HTTP Server versions 2.4.0 - 2.4.55 leads to HTTP Request Smuggling…

CVE-2025-1868: Advanced IP Scanner & Advanced Port Scanner NTLM Leakage HTTP Tester

Proof-of-concept exploit for CVE-2021-42013, a path traversal and remote code execution vulnerability in Apache HTTP Server 2.4.50.

CVE-2021-26690 patch diffing - Apache HTTP mod_session NULL pointer dereference

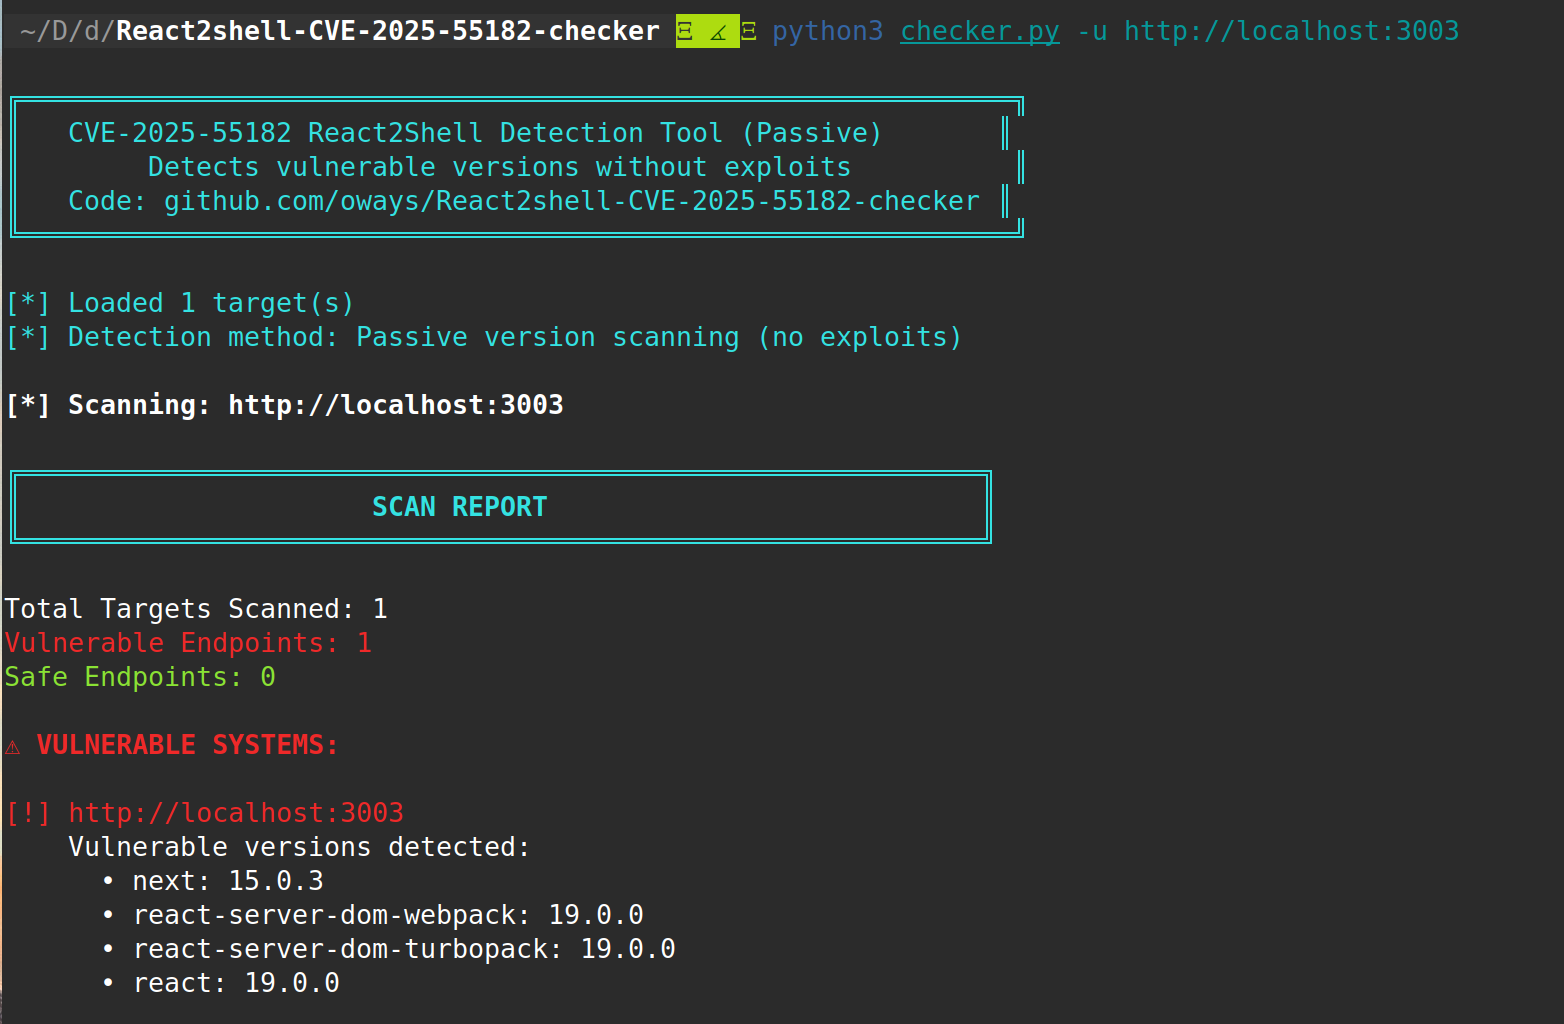
Passive CVE-2025-55182 detection tool for vulnerable React Server Components. Scans package.json, JavaScript bundles, HTTP headers, and API endpoints…

Technical analysis of CVE-2026-24072, a local privilege escalation in Apache HTTP Server mod_rewrite, including root cause, patches, and Dockerized…

Local privilege escalation exploit for CVE-2019-0211 targeting Apache HTTP Server 2.4.17-2.4.38 with mod_php. Uses UAF in PHP to corrupt Apache…

Proof-of-concept for CVE-2026-36957, a denial-of-service vulnerability in Dbit Router firmware via HTTP flood on the Boa web server, causing resource…

YAMCS yamcs-core < 5.12.7 lacks rate limiting on POST /auth/token. An unauthenticated attacker can perform unlimited brute-force attempts against any…

Proof-of-concept exploit for an unauthenticated IDOR vulnerability in FreeScout that allows thread enumeration and manipulation of read status via…

Proof-of-concept demonstrating CRLF injection and HTTP request smuggling in Axios, chaining prototype pollution to achieve SSRF and access internal…

Stack-based buffer overflow in MiniShare 1.4.1 reachable through a single HTTP PUT request.

Proof-of-concept exploit for CVE-2026-23918, a double-free vulnerability in Apache HTTP Server, demonstrating remote crash via crafted requests.

Python exploit for CVE-2026-32201, a reflected XSS in Microsoft SharePoint Server, enabling unauthenticated spoofing and data modification via…

Classic stack-based buffer overflow in Savant Web Server 3.1 demonstrating early-2000s remote memory corruption through a crafted HTTP request.