

CVE-2021-41773
 emaar1x/cve-2021-41773
Educational Docker lab for Apache HTTP Server 2.4.49 path traversal and RCE (CVE-2021-41773) with CVE research, PoC exploit, testing evidence, and…
educationexploitationlabs-practice+4
emaar1x/cve-2021-41773Educational Docker lab for Apache HTTP Server 2.4.49 path traversal and RCE (CVE-2021-41773) with CVE research, PoC exploit, testing evidence, and…
 theopaid/cve-2026-66752-http-request-smuggling-via-unparsed-transfer-encoding-values-tiny_http-
Security Advisory: HTTP Request Smuggling via Unparsed Transfer-Encoding Values (tiny_http)
 becodoexploit-mrcat/sapgatebreaker-exploit
SAPGateBreaker is a PoC exploit for CVE-2022-22536, a critical HTTP Request Smuggling vulnerability in SAP NetWeaver. It demonstrates how to bypass…
 sxmpl3/cve-2024-21762-safe-check
Safe, non-intrusive scanner that detects FortiOS SSL VPN out-of-bounds write vulnerability (CVE-2024-21762) by comparing normal and chunked HTTP POST…
 thanhlam-attt/cve-2023-25690
Proof-of-concept exploit for CVE-2023-25690 HTTP Request Smuggling in Apache mod_proxy. Includes lab environment with Docker, BurpSuite walkthrough,…
 lukaszstu/pritunl-cve-2020-25200
Exploit for CVE-2020-25200: enumerates valid Pritunl VPN usernames by analyzing HTTP response code changes after repeated login attempts.
 cappricio-securities/crlfi-scanner
CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…
 ch4n3-yoon/cve-2026-33033-poc
Proof-of-concept exploit for CVE-2026-33033, a denial-of-service vulnerability in Django's MultiPartParser via base64 whitespace CPU amplification,…
 abdurahmon3236/cve-2024-38473
Proof-of-concept demonstrating an encoding flaw in Apache HTTP Server mod_proxy that can bypass authentication via crafted encoded URLs.
 jenderal92/cms_detector
Detects and identifies content management systems (CMS) used by web applications through HTTP response analysis and known signatures, aiding in…
 alexcote1/cve-2024-23722-poc
Proof-of-concept exploit for CVE-2024-23722, a denial-of-service vulnerability in Fluent Bit versions 2.1.8 through 2.2.1, causing server crashes via…
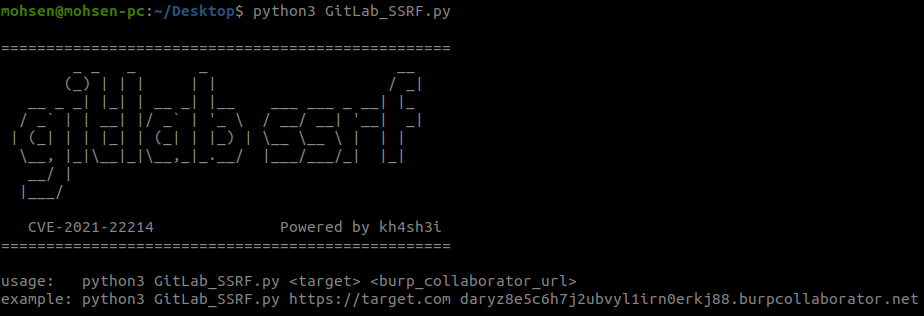 kh4sh3i/gitlab-ssrf-cve-2021-22214
Proof-of-concept exploit for CVE-2021-22214, a server-side request forgery in GitLab webhooks, allowing unauthenticated attackers to make internal…
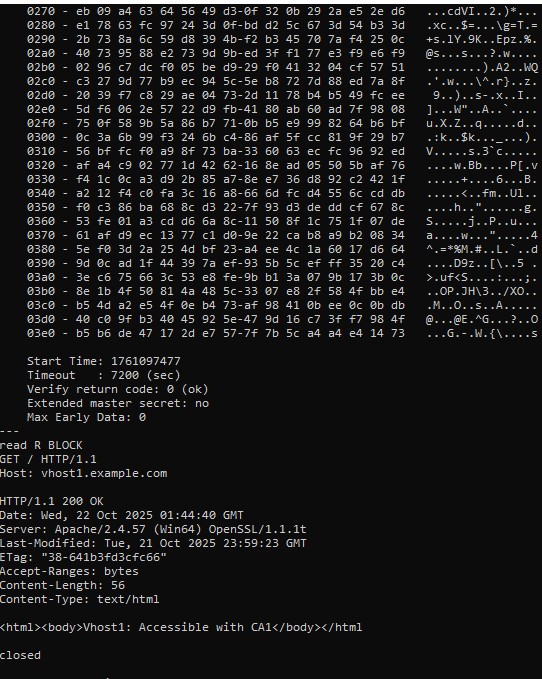 absholi7ly/cve-2025-23048-poc
Apache HTTP Server versions 2.4.35 – 2.4.63 are vulnerable to a client certificate authentication bypass when TLS 1.3 session resumption is used…
 penteraio/cve-2026-41473-cyberpanel-ai-scanner-unauth
Nuclei detection template for CVE-2026-41473, an unauthenticated read/write API access flaw in CyberPanel AI Scanner before 2.4.4. Uses two HTTP…
 sobri3195/pegasus---forbidden-buster
A penetration testing tool for bypassing HTTP 401/403 responses using various header manipulation techniques and path fuzzing.
 jmg0929/cve-2021-40346
PoC exploit for CVE-2021-40346: HAProxy integer overflow enabling HTTP request smuggling and ACL bypass. Includes analysis, reproduction steps, and…
 fxdyx-a/cve-2021-41773-poc
Apache HTTP Server 2.4.49 Path Traversal Vulnerability Reproduction
 abrahamsurf/cve-2023-20198-scanner
Scans Cisco IOS XE devices for CVE-2023-20198 Web UI authentication vulnerability using curl payloads, detects HTTP 200 responses, and saves detailed…