
Spring-Web-5xx-Mitigated-version
 tina94happy/spring-web-5xx-mitigated-version
Mitigated version for CVE-2016-1000027 spring web.
code-analysisexploitationsupply-chain-security+2
2
tina94happy/spring-web-5xx-mitigated-versionMitigated version for CVE-2016-1000027 spring web.
 nickpaulsec/2026-41940-poc
CVE-2026-41940: detect and exploit cpanel vuln
 dewankpant/cve-2017-16567
Proof-of-concept exploit for a persistent cross-site scripting (XSS) vulnerability in Logitech Media Server 7.9.0, demonstrating script injection via…
 rxerium/cve-2025-24016
Detection for CVE-2025-24016 - Deserialization of Untrusted Data Vulnerability in the Wazuh software
 poblaguev-tot/cve-2025-63499
POC for CVE-2025-63499
 gquere/cve-2018-16987
Technical disclosure of CVE-2018-16987: cleartext storage of external service passwords in Squash TM administration panel, with CVSS 4.1 scoring and…
 atreb92/cve-2024-37763
Proof-of-concept exploit for CVE-2024-37763, an unauthenticated stored XSS in MachForm up to v19, demonstrating payload injection via vulnerable…
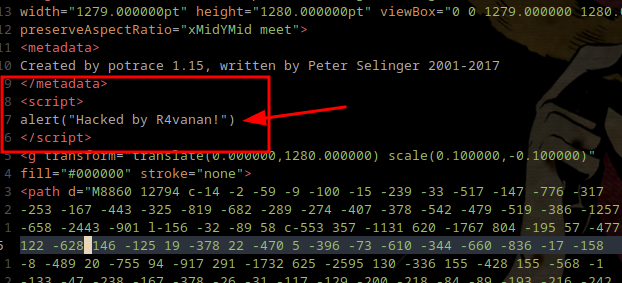 r4vanan/cve-2023-34845
Vulnerability POC for CVE-2023-34845
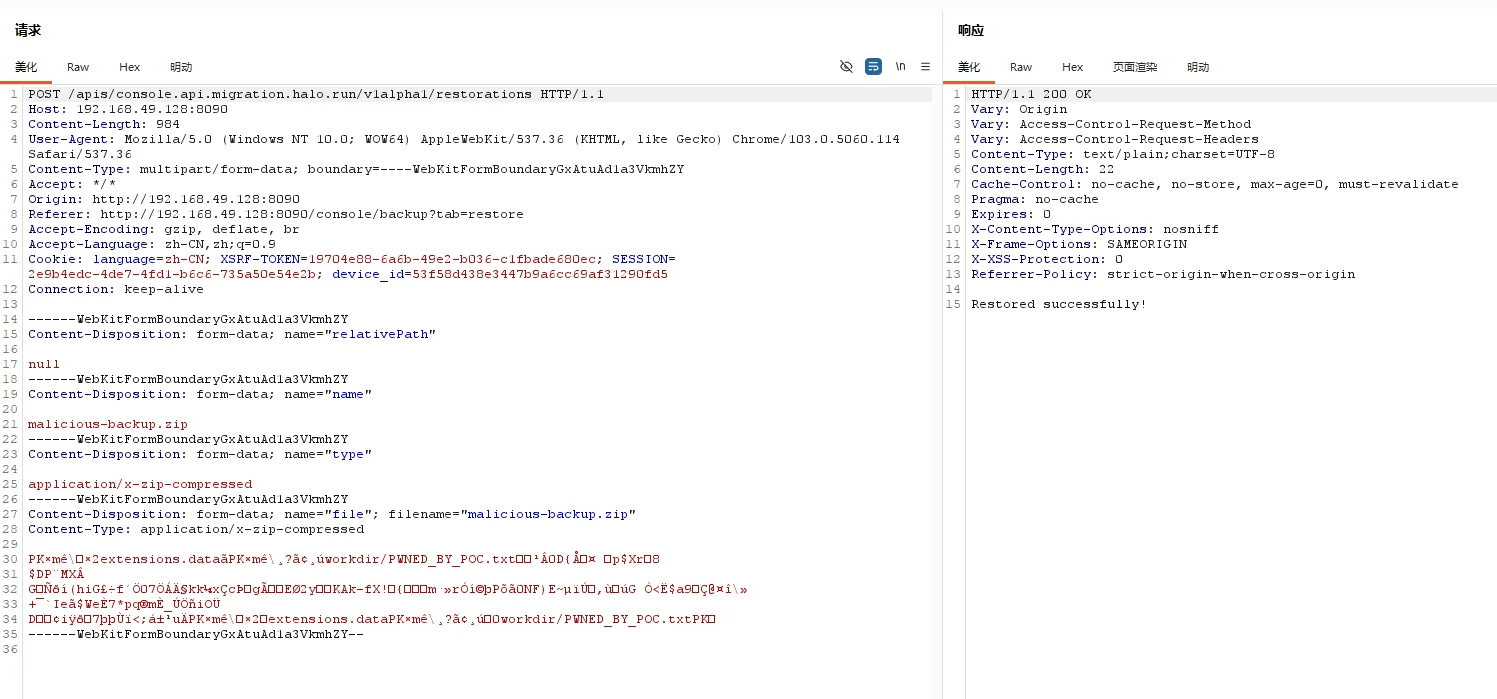 unpredictable21/halo-2.25.4-backup-write-cve-2026-67920
Proof-of-concept exploit for an arbitrary file write vulnerability in Halo CMS backup restoration, enabling RCE via plugin JAR replacement or…
 kirubel-cve/cve-2026-36959
Proof-of-concept exploit for CVE-2026-36959, a missing rate limiting vulnerability in U-SPEED Router firmware allowing brute-force attacks on the…
 izxci/cve-2026-5411
Proof-of-concept exploit for CVE-2026-5411 targeting WP Captcha PRO, demonstrating a vulnerability that bypasses CAPTCHA protections in WordPress…
 jjcjgo/cve-2026-38812-ruoyi-sql-injection
Proof-of-concept exploit for CVE-2026-38812, a SQL injection vulnerability in RuoYi v4.8.2 via the /tool/gen/createTable endpoint, enabling…
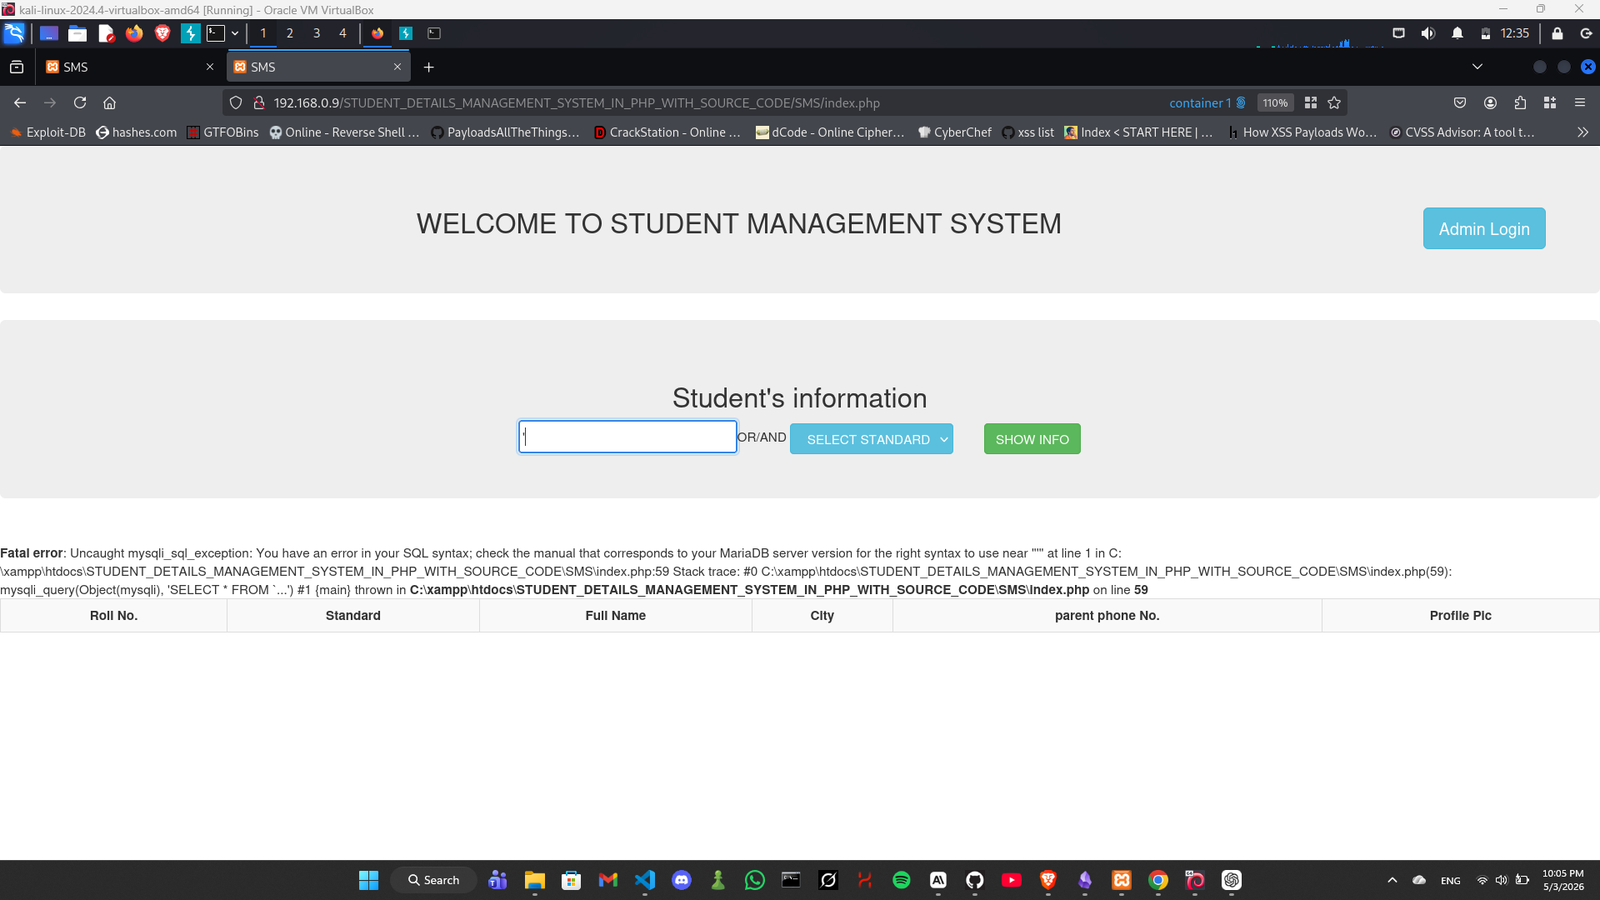 xmyronn/cve-2026-10110-sqli
Proof-of-concept for unauthenticated SQL injection in Student Details Management System 1.0, demonstrating UNION-based data extraction and credential…
 tibrn/cve-2026-5724
Proof-of-concept exploit for CVE-2026-5724, an authentication bypass in Temporal's frontend gRPC service allowing unauthenticated access to workflow…
 tocong282/cve-2026-44578-poc
Proof-of-concept exploit for CVE-2026-44578, a Server-Side Request Forgery in Next.js WebSocket upgrade handler. Includes detection mode and…
 menevarad007/cve-2026-37748
Proof-of-concept exploit for CVE-2026-37748, an unrestricted file upload vulnerability in Visitor Management System 1.0 leading to remote code…
 cyfare/cve-2026-23918-apache-http-server-doublefree-poc
Proof-of-concept exploit for CVE-2026-23918, a double-free vulnerability in Apache HTTP Server, demonstrating remote crash via crafted requests.
 sangsenimanwartefak/cve-2026-23550
Bash exploit for CVE-2026-23550 that triggers unauthenticated WordPress admin login via crafted REST API request to Modular Connector's…