CVE-2026-91097-CVE-2026-91106

HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)

HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)

Best and simplest tool for website change detection, web page monitoring, and website change alerts. Perfect for tracking content changes, price…

Multi-threaded mass exploiter chaining unauthenticated WordPress file-upload flaws in Super Forms and Elementor Pro to deploy and verify a PHP web…

Automated reconnaissance framework with 17+ modules for subdomain enumeration, directory brute-forcing, JS/link mining, WAF fingerprinting, and…

GravityForms < 2.9.23.1 - Unauthenticated Arbitrary File Upload

Automated web reconnaissance tool providing header analysis, DNS enumeration, subdomain discovery, directory scanning, SSL inspection, and port…

AI Engine <= 3.1.3 - Unauthenticated Sensitive Information Exposure to Privilege Escalation

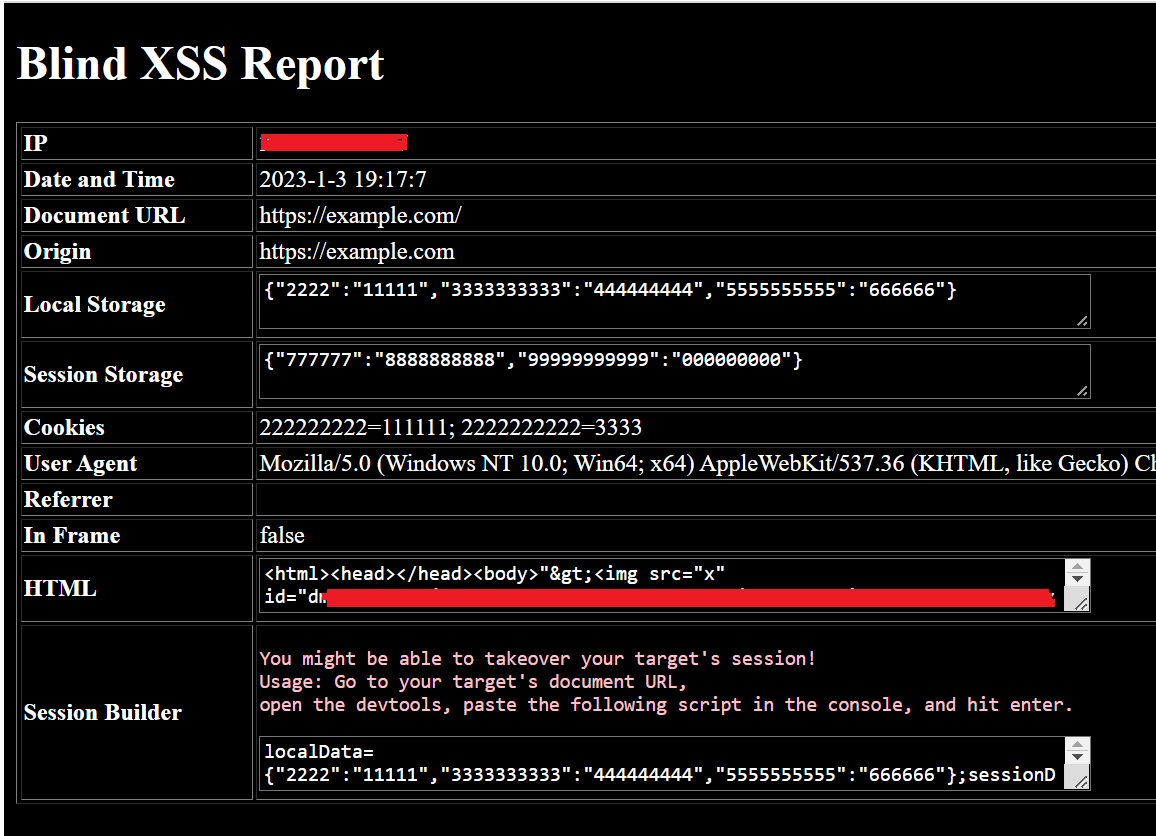
A standalone Blind XSS Script.

LiveHelperChat <=4.61 - Stored Cross Site Scripting (XSS) via Telegram Bot Username

Automated WordPress vulnerability scanner that processes multiple sites concurrently using wpscan, analyzes results, and sends summaries via Telegram.

Apache Real Time Logs Analyzer System

Lightweight web page change monitor written in Go. Detects updates on target URLs and sends notifications via Telegram or other services, ideal for…