

proxify
 projectdiscovery/proxify
A versatile and portable proxy for capturing, manipulating, and replaying HTTP/HTTPS traffic on the go.
packet-sniffing-analysispenetration-testingweb-proxies-interception+1
projectdiscovery/proxifyA versatile and portable proxy for capturing, manipulating, and replaying HTTP/HTTPS traffic on the go.
 al4n4n/cve-2026-25253-research
Proof-of-concept exploit for CVE-2026-25253, demonstrating one-click RCE on OpenClaw via Cross-Site WebSocket Hijacking. Includes attacker server and…
 cbuijs/sdproxy
DNS Proxy that is simple and fast with not so simple features. Focused on routed DNS forwarding, filtering and parental control.
 sebastianmautner/nuclei-cve-2025-24813
University Project of developing a template for safely testing for the CVE 2025-24813 on a server. It is intentionally made to not leave any lasting…
 murrez/cve-2026-89055
Python check/exploit PoC for CVE-2026-89055, an unauthenticated authorization bypass in Customer Reviews for WooCommerce that lets attackers link…
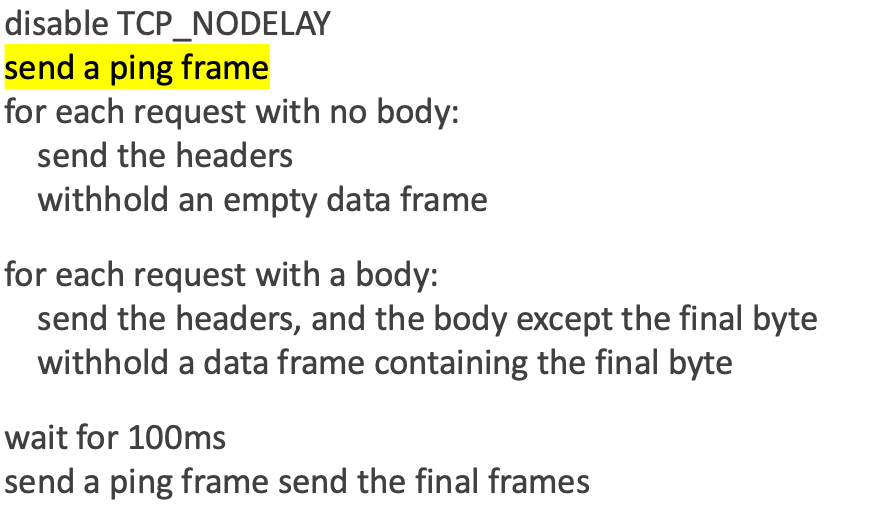 nxenon/h2spacex
HTTP/2 Last Frame Synchronization (also known as Single Packet Attack) low Level Library / Tool based on Scapy + Exploit Timing Attacks
 0dev1337/cpanelscanner
Scans internet-exposed cPanel/WHM instances for CVE-2026-41940 authentication bypass, probing HTTPS on port 2087 and matching response markers to…
 unteikyou/cve-2026-41940-authbypass-detector
Detection tool for cPanel/WHM CVE-2026-41940 (CRLF injection auth bypass). Verify vulnerability on servers you own or have permission to test. For…
 tjoulel/wordpress-6.9.1-blind-ssrf
Based on CVE-2022-3590, WordPress <= 6.9.1 - Unauthenticated Blind SSRF via XML-RPC Pingback Discovery proof of concept (PoC)
 r3verii/cve-2026-33555
One zero-byte QUIC packet is enough to desynchronize HAProxy's backend connection pool and smuggle HTTP requests across unrelated users — even users…
 diegovargasj/cve-2025-32407
Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…
 holypryx/cve-2024-9466
Proof-of-concept script to detect CVE-2024-9466 by checking HTTP responses for a specific debug file path on target URLs.
 mrharshvardhan/py-log4j-rce-scanner
Using this tool, you can scan for remote command execution vulnerability CVE-2021-44228 on Apache Log4j at multiple addresses.
 d3duct1v/cve-2022-41040
Python-based scanner for CVE-2022-41040 that tests single or multiple URLs for the vulnerability, with simple CLI interface and dependency on…
 iveresk/cve-2022-29885
Go-based exploit for Apache Tomcat Denial of Service (CVE-2022-29885) targeting the EncryptInterceptor in Tomcat Cluster NioReceiver. Sends a crafted…
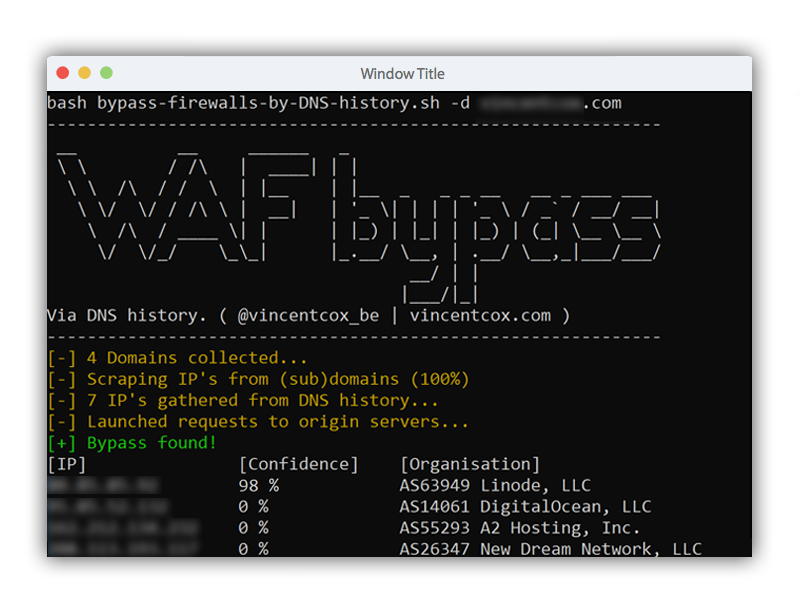 vincentcox/bypass-firewalls-by-dns-history
Firewall bypass script based on DNS history records. This script will search for DNS A history records and check if the server replies for that…
 cybersecurityworks553/scanner-cve-2020-5902
Lightweight Python script to scan hosts for CVE-2020-5902 (F5 BIG-IP TMUI RCE). Accepts IP list input and reports vulnerable or patched targets on…