
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
41 results
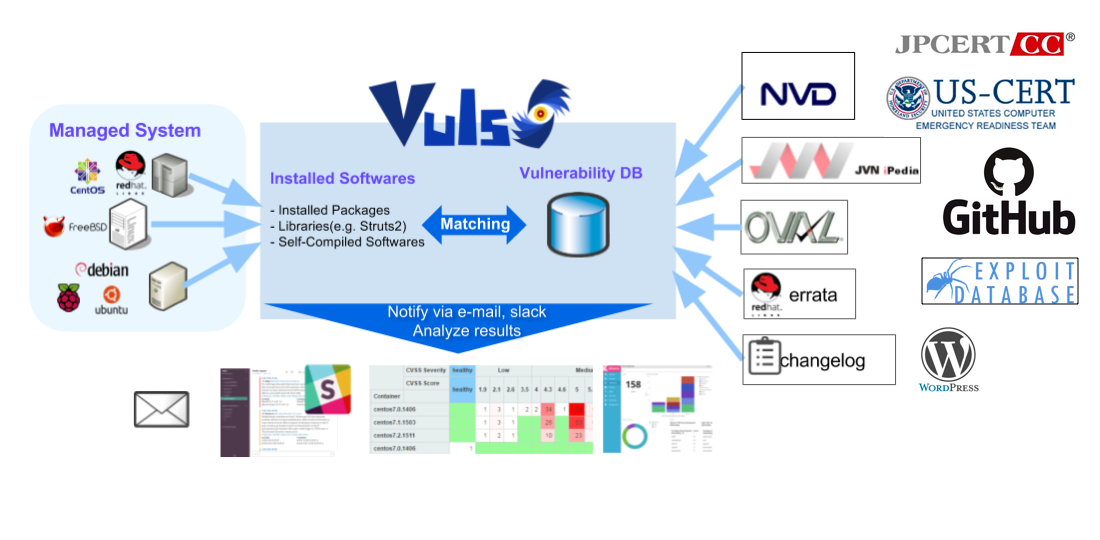
vuls preview

vuls

GitHubfuture-architect/vuls

Agent-less vulnerability scanner for Linux, FreeBSD, Container, WordPress, Programming language libraries, Network devices
cloud-securityconfiguration-auditingcontainer-security+5
12.3k
6 days ago
gitread preview

gitread

GitHubplur1bu5/gitread

CVE-2026-85706 · GitLab CE/EE unauthenticated file read · research PoC with oracle mode, fd enumeration, and tiered loot targeting

data-exfiltrationexploitationinformation-gathering+7
127 days ago
CVE-2026-89012 preview

CVE-2026-89012

GitHubfaceless0x7/cve-2026-89012

Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…

api-securitydata-exfiltrationexploitation+6
629 days ago
CVE-2026-85706 preview

CVE-2026-85706

GitHubmhtsec/cve-2026-85706

Python PoC for CVE-2026-85706, an unauthenticated path traversal in GitLab CE/EE Repository Commits API that leaks arbitrary local files via a…

data-exfiltrationexploitationinformation-gathering+5
1229 days ago
the-callback-that-outlived-the-page-cve-2026-78997-uc-browser-android-universal-xss preview

the-callback-that-outlived-the-page-cve-2026-78997-uc-browser-android-universal-xss

GitHubhunt-benito/the-callback-that-outlived-the-page-cve-2026-78997-uc-browser-android-universal-xss

PoC for CVE-2026-78997, a Universal XSS in UC Browser for Android. Includes a crafted URL builder, a callback-dispatch oracle, and Frida hooks to…
android-securitydynamic-analysis-sandboxingexploitation+6
29 days ago
CVE-2026-21962 preview

CVE-2026-21962

GitHubzeetee1235/cve-2026-21962

Verified PoC and analysis for CVE-2026-21962, an access-control bypass in Oracle HTTP Server/WebLogic Proxy Plug-in via URI normalization…
exploitationpenetration-testingred-teaming+3
31 month ago
patch-CVE-2026-22024 preview

patch-CVE-2026-22024

GitHubgduma-phdata/patch-cve-2026-22024

Patch: Deserialization vulnerability (Oracle WebLogic Server)
vulnerability-analysisweb-security
1 month ago
CVE-2026-10053-lab preview

CVE-2026-10053-lab

GitHubdinosn/cve-2026-10053-lab

Reproducible lab for CVE-2026-10053 (GitLab npm package-registry path traversal -> arbitrary file write as git). Vulnerable 19.2.1 vs patched 19.2.2,…
educationexploitationlabs-practice+3
41 month ago
CVE-2026-26980 preview

CVE-2026-26980

GitHubyym8538/cve-2026-26980

Python PoC and Docker lab demonstrating unauthenticated SQL injection in TryGhost Ghost CMS Content API slug filter, extracting database values via a…

database-securityeducationexploitation+5
11 month ago
CVE-2023-22047---Oracle-PeopleSoft-LFI preview

CVE-2023-22047---Oracle-PeopleSoft-LFI

GitHub0xterror/cve-2023-22047---oracle-peoplesoft-lfi

CVE-2023-22047 is a critical unauthenticated Local File Inclusion (LFI) vulnerability in Oracle PeopleSoft Enterprise PeopleTools. This exploit…
exploitationinformation-gatheringpenetration-testing+3
1 month ago
CVE-2026-67620-poc preview

CVE-2026-67620-poc

GitHubabdugafforov-bobur/cve-2026-67620-poc

CVE-2026-67620 - Flowise SSRF via incomplete cloud-metadata deny-list (Oracle OCI 192.0.0.192 + Alibaba 100.100.100.200 bypass the DEFAULT_DENY_LIST)

cloud-securityexploitationinformation-gathering+4
12 months ago
POC-CVE-2026-60206 preview

POC-CVE-2026-60206

GitHubimbas007/poc-cve-2026-60206

cve cve-2026-60206 weblogic saml exploit poc vulnerability oracle scanner security
authentication-authorizationexploitationpenetration-testing+4
352 months ago
CVE-2026-21978 preview

CVE-2026-21978

GitHubeangly/cve-2026-21978

My CVE in Oracle FLEXCUBE Universal Banking

exploitationinformation-gatheringpenetration-testing+2
12 months ago
Cybersecurity-Capstone-Project preview

Cybersecurity-Capstone-Project

GitHubshahdawadfallah-sys/cybersecurity-capstone-project

Cybersecurity Capstone Project completed during the NCSC Nashama CyberCamp 11, delivered in collaboration with IT Security C&T. The project…

educationexploitationlabs-practice+5
3 months ago
CVE-2026-XXXX-atlassian-email-enumeration preview

CVE-2026-XXXX-atlassian-email-enumeration

GitHubwh4l3x/cve-2026-xxxx-atlassian-email-enumeration

CVE-2026-XXXX: Atlassian GraphQL Email Enumeration Oracle (CWE-204, CVSS 5.3 MEDIUM)
email-harvestinginformation-gatheringosint+5
3 months ago
keycloak preview

keycloak

GitHubmuhammedhussein17/keycloak

Security research disclosing CVE-2026-9794, an unauthenticated client ID enumeration flaw in Keycloak SAML ECP via faultstring oracle, fixed in…
authenticationidentity-managementinformation-gathering+3
4 months ago
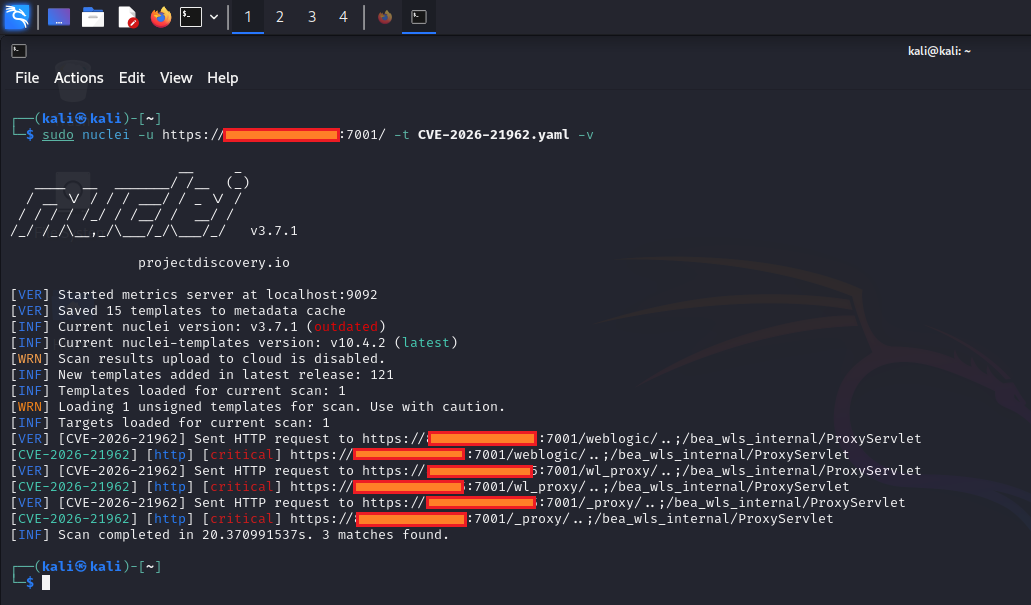
CVE-2026-21962 preview

CVE-2026-21962

GitHub0xblackash/cve-2026-21962

CVE-2026-21962
authentication-authorizationexploitationpenetration-testing+3
25 months ago
CVE-2026-21962-Oracle-HTTP-Server-WebLogic-Proxy-Plug-in-Critical- preview

CVE-2026-21962-Oracle-HTTP-Server-WebLogic-Proxy-Plug-in-Critical-

GitHubgeorge0papasotiriou/cve-2026-21962-oracle-http-server-weblogic-proxy-plug-in-critical-

Oracle Fusion Middleware Oracle HTTP Server / WebLogic Server Proxy Plug-in has an easily exploitable, unauthenticated, network-reachable flaw…

educationexploitationpenetration-testing+3
38 months ago
Previous123Next