

CVE-2021-41773-Apache-Path-Traversal-Lab
 1833ravikumar-max/cve-2021-41773-apache-path-traversal-lab
Docker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
ctfeducationexploitation+6
1833ravikumar-max/cve-2021-41773-apache-path-traversal-labDocker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
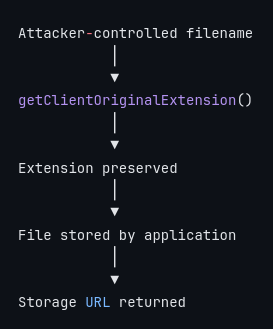 ish3ng0m4/cve-2026-38526-krayincrm
Authenticated Arbitrary File Upload leading to Remote Code Execution Technical analysis and controlled reproduction of CVE-2026-38526 in Webkul…
 zoly-zoly/cve-2025-3248
Educational analysis and proof-of-concept exploit for CVE-2025-3248, a critical unauthenticated code injection vulnerability in Langflow, including…
 yora1928/papercut-cve-2026-81578-82078
Security research tool for PaperCut CVE-2026-81578 & CVE-2026-82078
 horkimhab/cve-2026-19912-cve-2026-19913-cve-2026-19914
Proof-of-concept exploits for CVE-2026-19912, CVE-2026-19913, and CVE-2026-19914, demonstrating file read and remote code execution in Kaltura,…
 kalhoralireza/cve-2026-17532-lab
Docker lab demonstrating CVE-2026-17532, an unauthenticated reflected XSS in Seraphinite Accelerator that chains to RCE via admin session, with…
 alicealys/mgo3-rce
Proof-of-concept remote code execution exploit for CVE-2026-19874 in Metal Gear Online 3, with documentation and video demo for academic research.
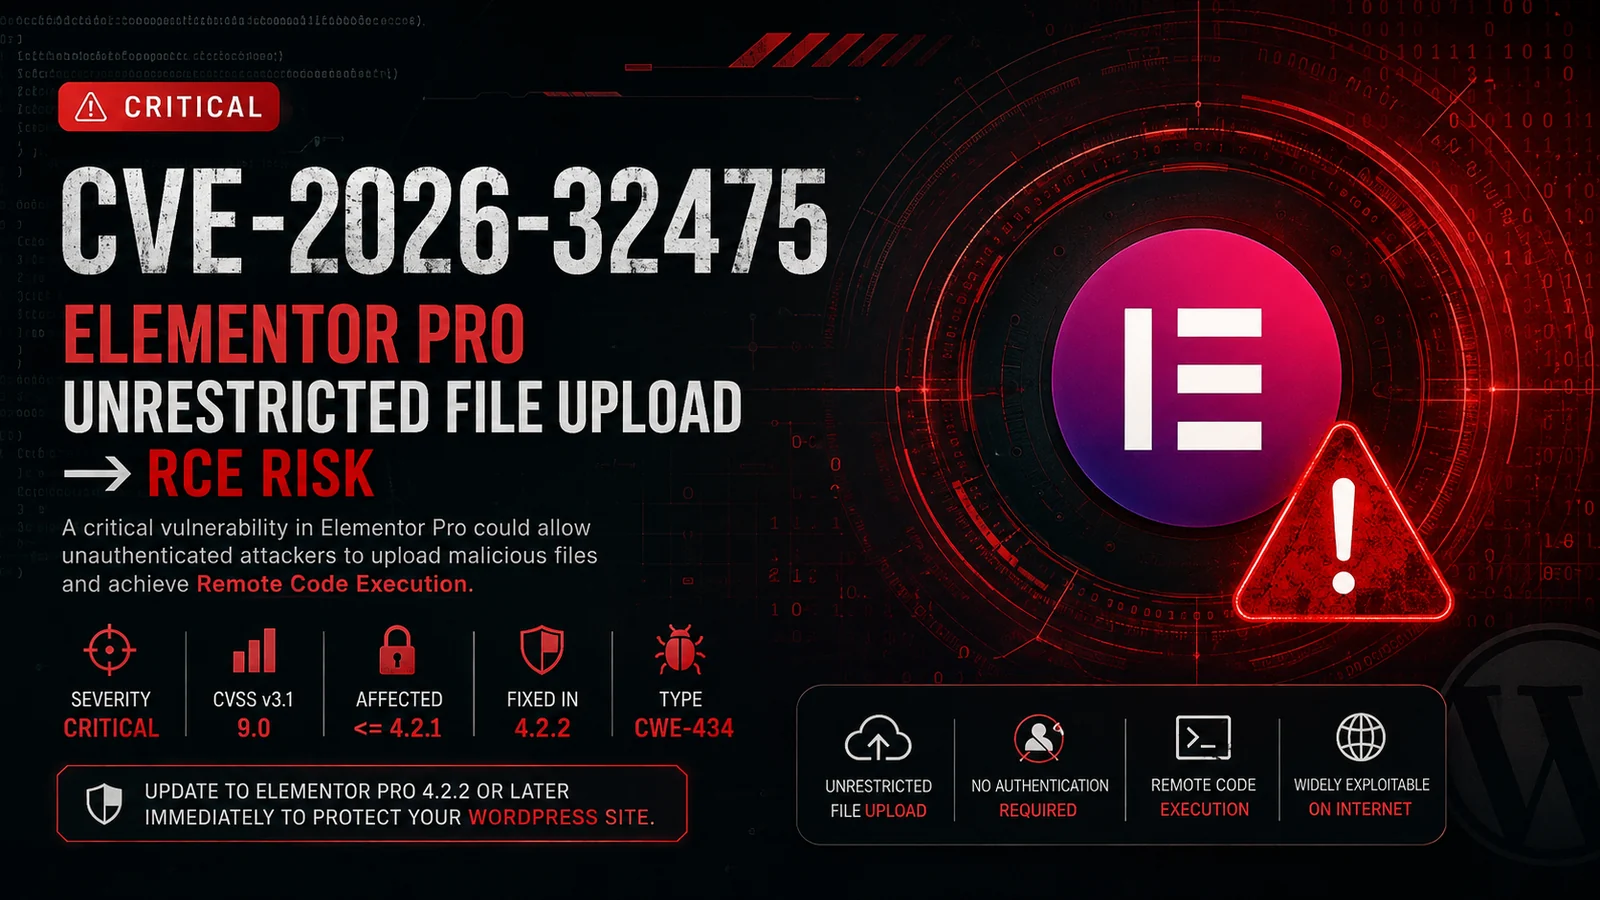 0xblackash/cve-2026-32475
Technical analysis and detection guidance for critical unrestricted file upload in Elementor Pro (CVE-2026-32475) leading to remote code execution.
 mhassani97/cve-2026-63030-lab
wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain
 mattiacervelli/cve-2025-24893_analysis
Self-contained Docker lab that reproduces CVE-2025-24893, an unauthenticated SSTI-to-RCE in XWiki SolrSearch, and compares vulnerable vs patched…
 aisha-jimoh/cve-2025-55182-react2shell-analysis
Technical analysis of CVE-2025-55182 (React2Shell), covering vulnerability mechanics, root cause, controlled PoC testing, impact, and mitigation…
 ilhomjonr/cve-2026-70376
Advisory and Python PoC for Pluck CMS CSRF: fail-open Referer check plus double-extension upload enables webshell deployment and remote code…
 shams-ul-mehmood/cve-2018-7600-drupalgeddon2-rce
Educational CVE-2018-7600 exploit project combining a Python RCE PoC, isolated Docker Drupal lab, payload research, and mitigation documentation for…
 george0papasotiriou/cve-2026-11104-python-ssti-via-jinja2-attr-filter-bypass
PoC exploit for CVE-2026-11104 demonstrating Jinja2 attr filter bypass in Flask, enabling server-side template injection and remote code execution.
 imbas007/cve-2026-63223-poc
CVE-2026-63223 PoC — CodeIgniter 4 is_image/mime_in File Upload RCE (CVSS 9.8). Unauthenticated remote code execution via unrestricted file upload…
 theopaid/cve-2026-66754-remote-denial-of-service-via-reachable-assertion-in-url-prefix-handling-rouille-
Security Advisory: Remote Denial of Service via Reachable Assertion in URL Prefix Handling (rouille)
 lazarus0x1337/cve-2026-25632
CVE-2026-25632 — Fix Unsafe JSON Deserialization Leading to Remote Code Execution