

unKover
 brutelogic/unkover
Bash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…
api-security-testinginformation-gatheringpenetration-testing+7
126
brutelogic/unkoverBash 403/401 access bypass tester that probes a URL with header spoofing, method tampering, path normalization, and encoding techniques, returning a…
 joaovicdev/exploit-cve-2026-87902
Lab vulnerável (Docker) + PoC Python para a CVE-2026-87902 — path traversal não autenticado no WordPress Core (page-template -> LFI -> RCE…
 hackingteamoficial/getrobarb
Automated reconnaissance and XSS detection framework integrating subfinder, httpx, katana, gospider, waybackurls, and dalfox into a 9-stage pipeline…
 oseasfr/scanner_cve_2026-42945
Script Python para detecção de instâncias Nginx vulneráveis ao CVE-2026-42945 em IPs, CIDRs e ASNs.
 infobyte/emploleaks
An OSINT tool that helps detect members of a company with leaked credentials
 trivulzianus/tarantubench
The full repo of all the labs available as part of the benchmark
 karmanyat28/multi-stage-exploitation-and-detection-engineering-analysis-of-cve-2023-34362-in-moveit-transfer
This repository contains an academic and technical analysis of CVE-2023-34362, a critical SQL injection vulnerability affecting the MOVEit Transfer…
 harley-ghostie/safe-check-cve-2025-23419
Script em python scanner safe-check da CVE-2025-23419
 4l13n-dn/poc-cve-2018-7600
Drupal vulnerable a CVE-2018-7600
 waleedadam360-web/syncshield
SyncShield - Browser Extension to Detect Unsafe Rsync Commands (CVE-2018-5764)
 moften/cve-2025-29927_next.js_auth_bypass
Next.js Auth Bypass PoC Edge Runtime Env Leak via Middleware Bug
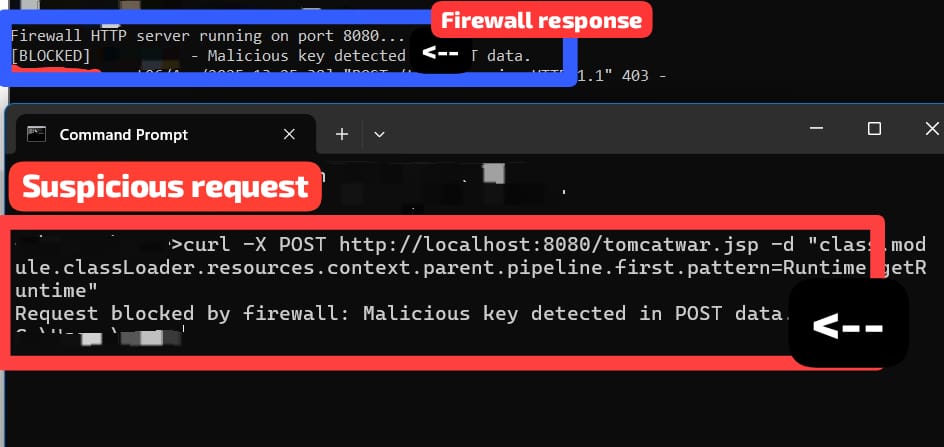 salo-404/firewall
🔒 Spring4Shell Firewall Defense — Cybersecurity Incident Simulation This project is part of a Cybersecurity Job Simulation I completed in August…
 moften/symfony-cve-scanner-poc-
CVE-2021-21424 - CRLF Injection - CVE-2021-41268 - Host Header Injection - CVE-2022-24894 - WebProfiler abierto - CVE-2019-10909 - Directory Traversal
 aulauniversal/cve-2023-44487
RapidResetClient
 jfoz1010/cve-2024-24549
Proof of concept of the CVE-2024-24549, Exploit in Python.
 jheeree/cve-2022-1388-checker
Simple script realizado en bash, para revisión de múltiples hosts para CVE-2022-1388 (F5)
 miguelm001/vulescanjndilookup
HERRAMIENTA AUTOMATIZADA PARA LA DETECCION DE LA VULNERABILIDAD CVE-2021-44228
 jheeree/simple-cve-2021-41773-checker
Simple script realizado en bash, para revisión de múltiples hosts para CVE-2021-41773 (Apache)