

SecLists
 danielmiessler/seclists
Curated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
ctfcurated-resourcesdns-fuzzing+11
73.9k
danielmiessler/seclistsCurated collection of wordlists for security assessments, including usernames, passwords, URLs, fuzzing payloads, and sensitive data patterns for…
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 cliffe/breakescape
Mountable Rails engine providing 24+ cybersecurity escape room scenarios with randomized passwords, JIT-compiled NPC dialogue, and RESTful API for…
 nilsteampassnet/teampass
Collaborative Passwords Manager
 zhairiazzeddine/exploit-cve-2023-6063-poc-vuln
Python PoC for CVE-2023-6063, an unauthenticated time-based blind SQL injection in WP Fastest Cache <=1.2.2, extracting WordPress password hashes and…
 unpredictable21/halo-cors-csrf-cve-2026-67921
Proof-of-concept demonstrating a combined CORS misconfiguration and CSRF protection bypass in Halo CMS, enabling cross-site request forgery attacks…
 hashview/hashview
A web front-end for password cracking and analytics
 0xdsm/pinkerton
🕵️ Python project to crawl for JavaScript files and search for secrets like API keys, authorization tokens, hardcoded credentials, etc.
 tw1sm/spraycharles
Low and slow password spraying tool, designed to spray on an interval over a long period of time
 fevra-dev/claimjumper
Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…
 p0dalirius/rdwatool
A python script to extract information from a Microsoft Remote Desktop Web Access (RDWA) application
 ya551n3/bug-bounty-wordlists
Curated collection of wordlists for bug bounty hunting, covering directories, subdomains, parameters, usernames, passwords, and web fuzzing payloads.
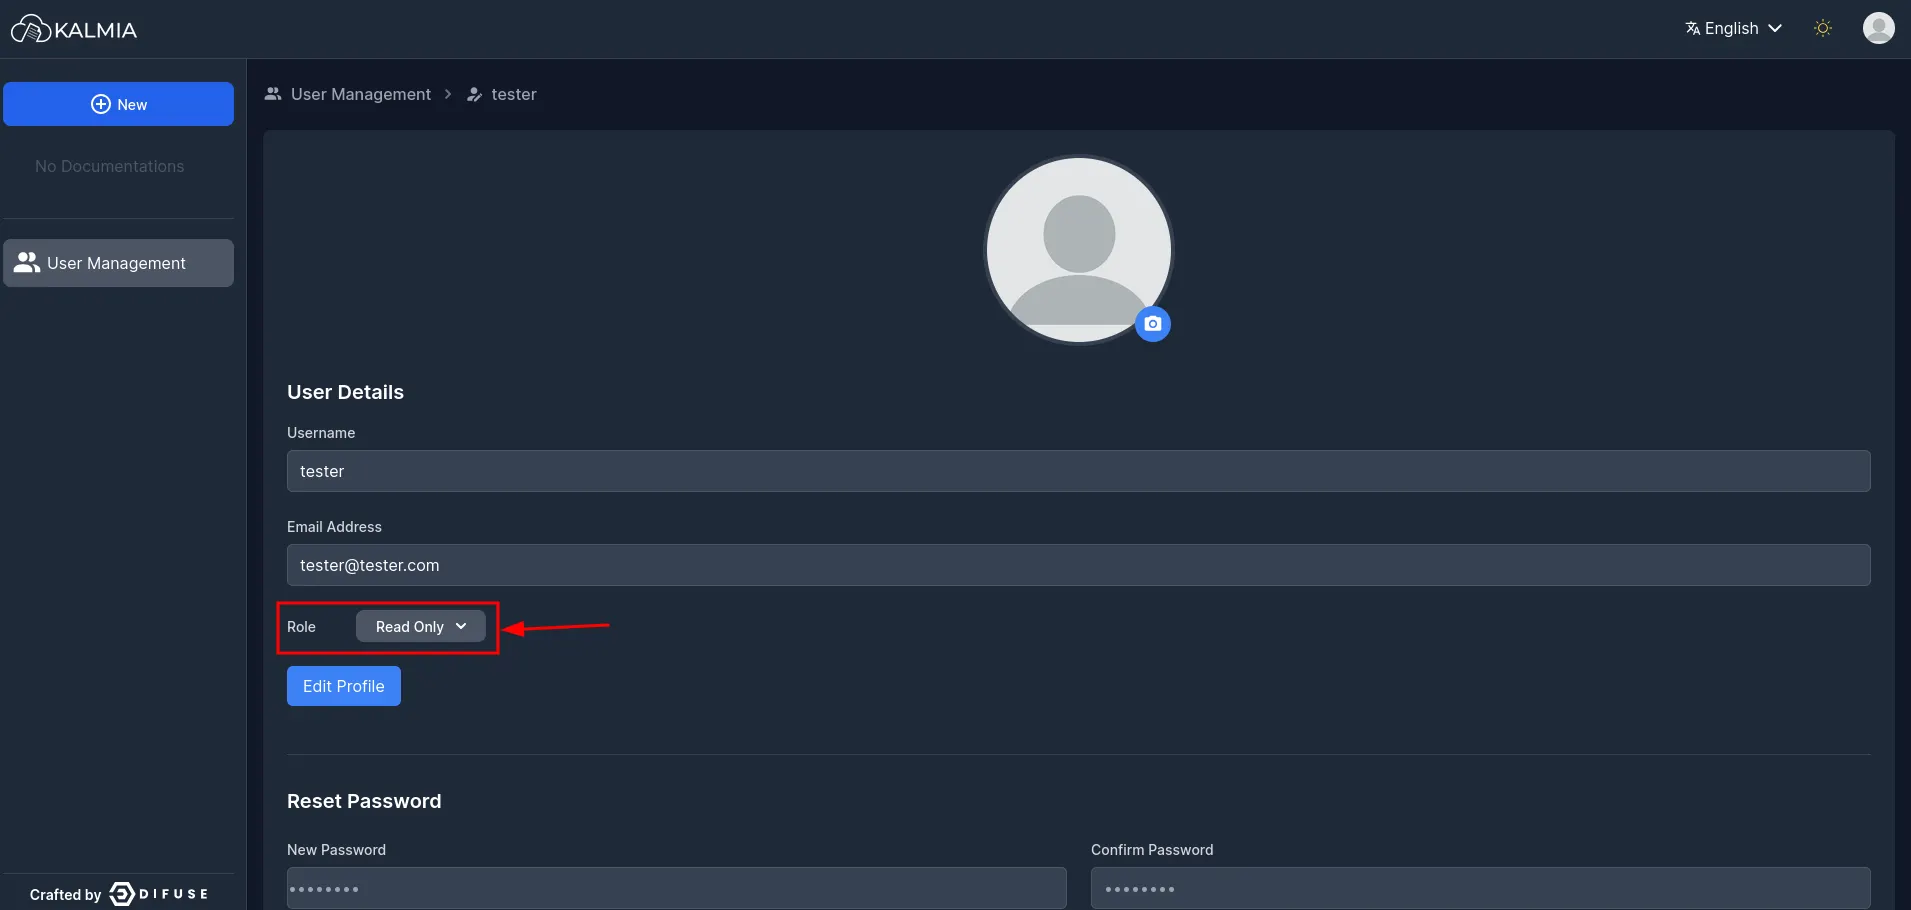 noxurge/cve-2025-65900
DifuseHQ Kalmia CMS version 0.2.0 contains an Incorrect Access Control vulnerability in the /kal-api/auth/users API endpoint. Due to insufficient…
 barisbaydur/cve-2025-63579
Unauthorized access to all user names and passwords entered in the Address Book feature found in Kyocera printers.
 wkovacs64/pwl
Password Lense: reveal character types in a password
 tyki6/myjwt
A cli for cracking, testing vulnerabilities on Json Web Token(JWT)
 z-bool/venom-jwt
针对JWT渗透开发的漏洞验证/密钥爆破工具,针对CVE-2015-9235/空白密钥/未验证签名攻击/CVE-2016-10555/CVE-2018-0114/CVE-2020-28042的结果生成用于FUZZ,也可使用字典/字符枚举(包括JJWT)的方式进行爆破(JWT Crack)