

qyvora-toha3ee
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
exploitationnetwork-securityosint+9
4
qyvora/qyvora-toha3eeGo-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 dimastopel/certdepot
Create your self-signed SSL certificate instantly and for free
 xcapri/subdosec
Fast, accurate subdomain takeover scanner with zero false positives. Detects vulnerable subdomains, collects metadata (IP, CNAME, title, status…
 alicealys/mgo3-rce
Proof-of-concept remote code execution exploit for CVE-2026-19874 in Metal Gear Online 3, with documentation and video demo for academic research.
 error-inside/cve-2025-10897
WooCommerce Designer Pro <= 1.9.28 - Unauthenticated Arbitrary File Read
 xaanziu/cve-2026-5513
CVE-2026-5513: Bookly <= 27.2 Stored XSS via Cookie (Unauthenticated)
 crussella0129/tricorne
a Fedora remix focused on pentesting and purple hat tooling
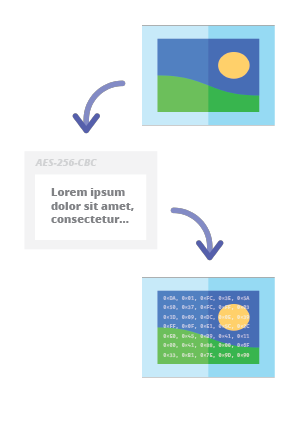 pelock/steganography-online-codec-javascript
Steganographic online codec allows you to hide a password encrypted message within the images & photos using AES encryption algorithm with a 256-bit…
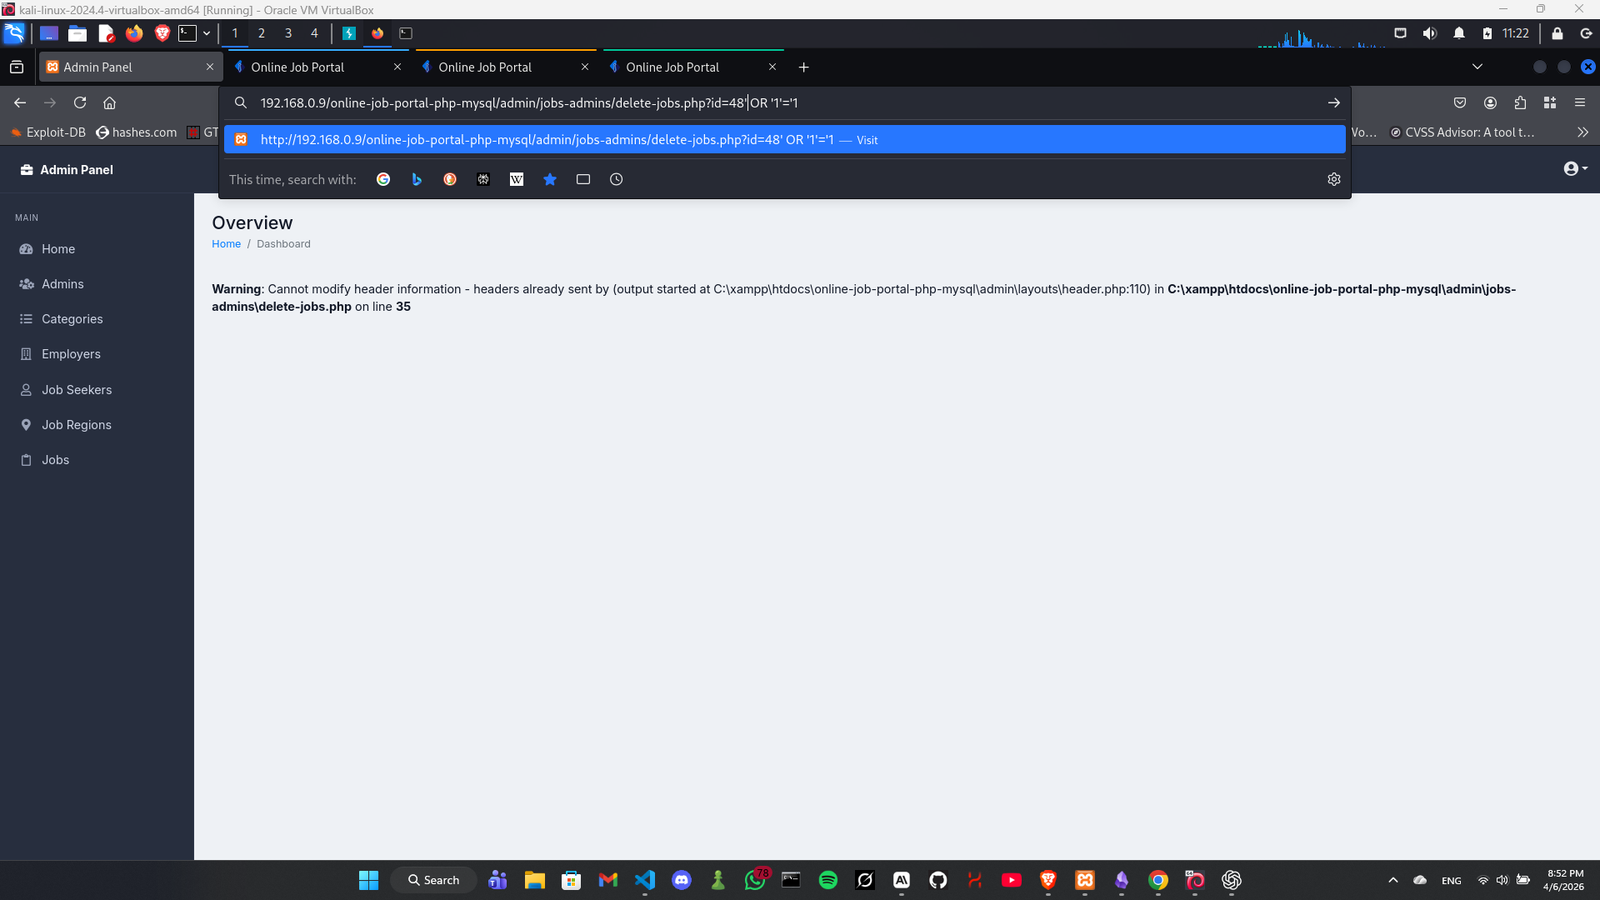 xmyronn/cve-2026-7028-sqli
Proof-of-concept exploit for SQL injection in CodeAstro Online Job Portal allowing authenticated deletion of all job records via crafted GET request.
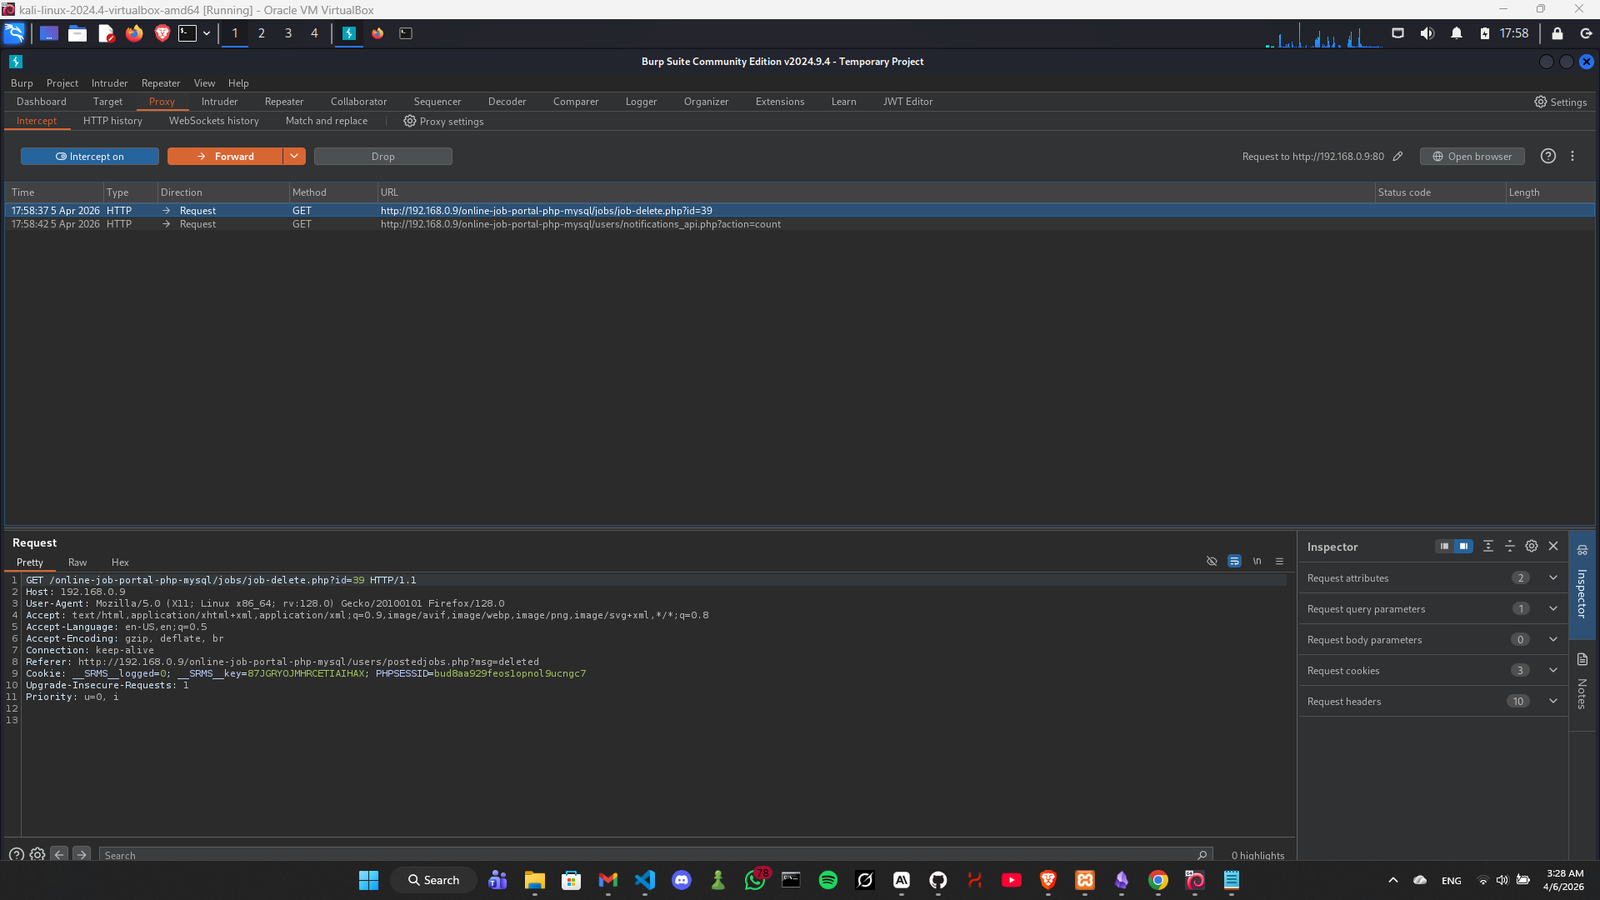 xmyronn/cve-2026-6201-idor
Proof-of-concept demonstrating an IDOR vulnerability in CodeAstro Online Job Portal allowing authenticated employers to delete arbitrary job postings…
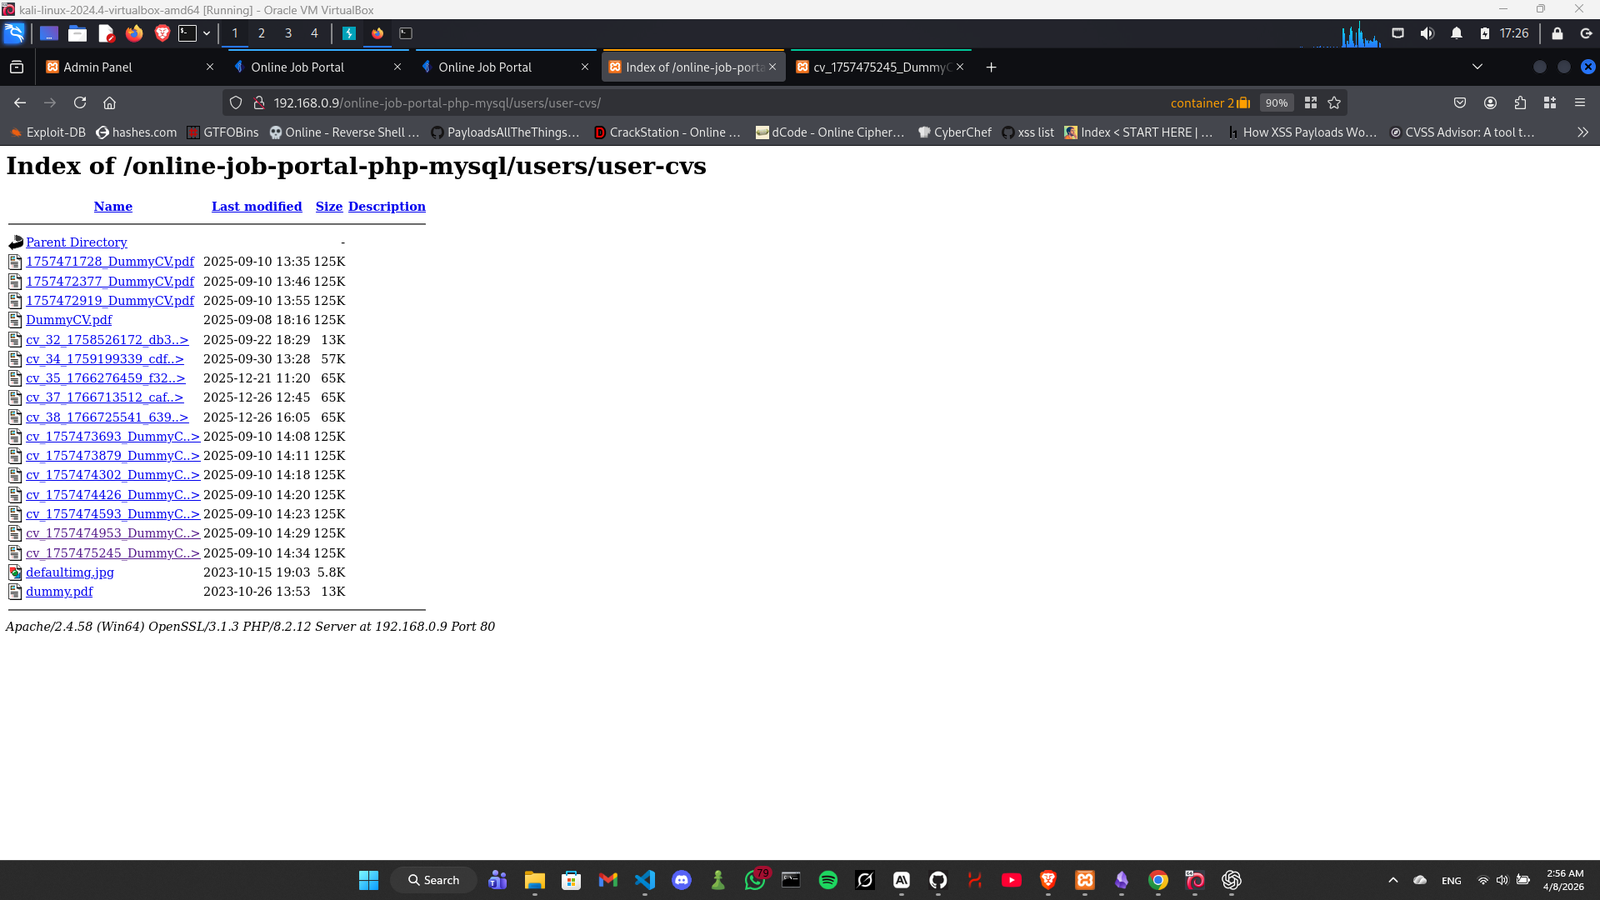 xmyronn/cve-2026-7071-access-control
Proof of concept demonstrating unauthenticated access to user resumes via directory listing in CodeAstro Online Job Portal, with reproduction steps…
 sobri3195/pegasus-neo
PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…
 mathavamoorthi/cve-2025-70899
Proof-of-concept exploit demonstrating a missing CSRF protection vulnerability in PHPgurukul Online Course Registration System, for security testing…
 cameloo1/sharepoint-toolshell-micro-postmortem
Reproducible incident micro-postmortem for on-prem Microsoft SharePoint “ToolShell” (CVE-2025-53770): ATT&CK snapshot, “logs that matter” table,…
 mfmokbel/crawlector
Crawlector is a threat hunting framework designed for scanning websites for malicious objects.
 fatmatrabelsi17/cve-2025-14221
Proof-of-concept for CVE-2025-14221: Stored XSS in SourceCodester Online Banking System 1.0 via unsanitized First Name field, enabling session…
 nxploited/cve-2025-9209
RestroPress – Online Food Ordering System 3.0.0 - 3.1.9.2 - Unauthenticated Information Exposure to Authentication Bypass via Forged JWT
 hafizgemilang/cve-2025-52021
Advisory and proof-of-concept for a time-based blind SQL injection vulnerability in an online shopping system, including technical details, impact…