
CVE-2026-24733
 darabium/cve-2026-24733
Dependency-free Python verifier that detects CVE-2026-24733, an Apache Tomcat HTTP/0.9 HEAD security-constraint bypass, with JSON output and CI/CD…
configuration-auditingdefensive-toolsdevsecops+4
darabium/cve-2026-24733Dependency-free Python verifier that detects CVE-2026-24733, an Apache Tomcat HTTP/0.9 HEAD security-constraint bypass, with JSON output and CI/CD…
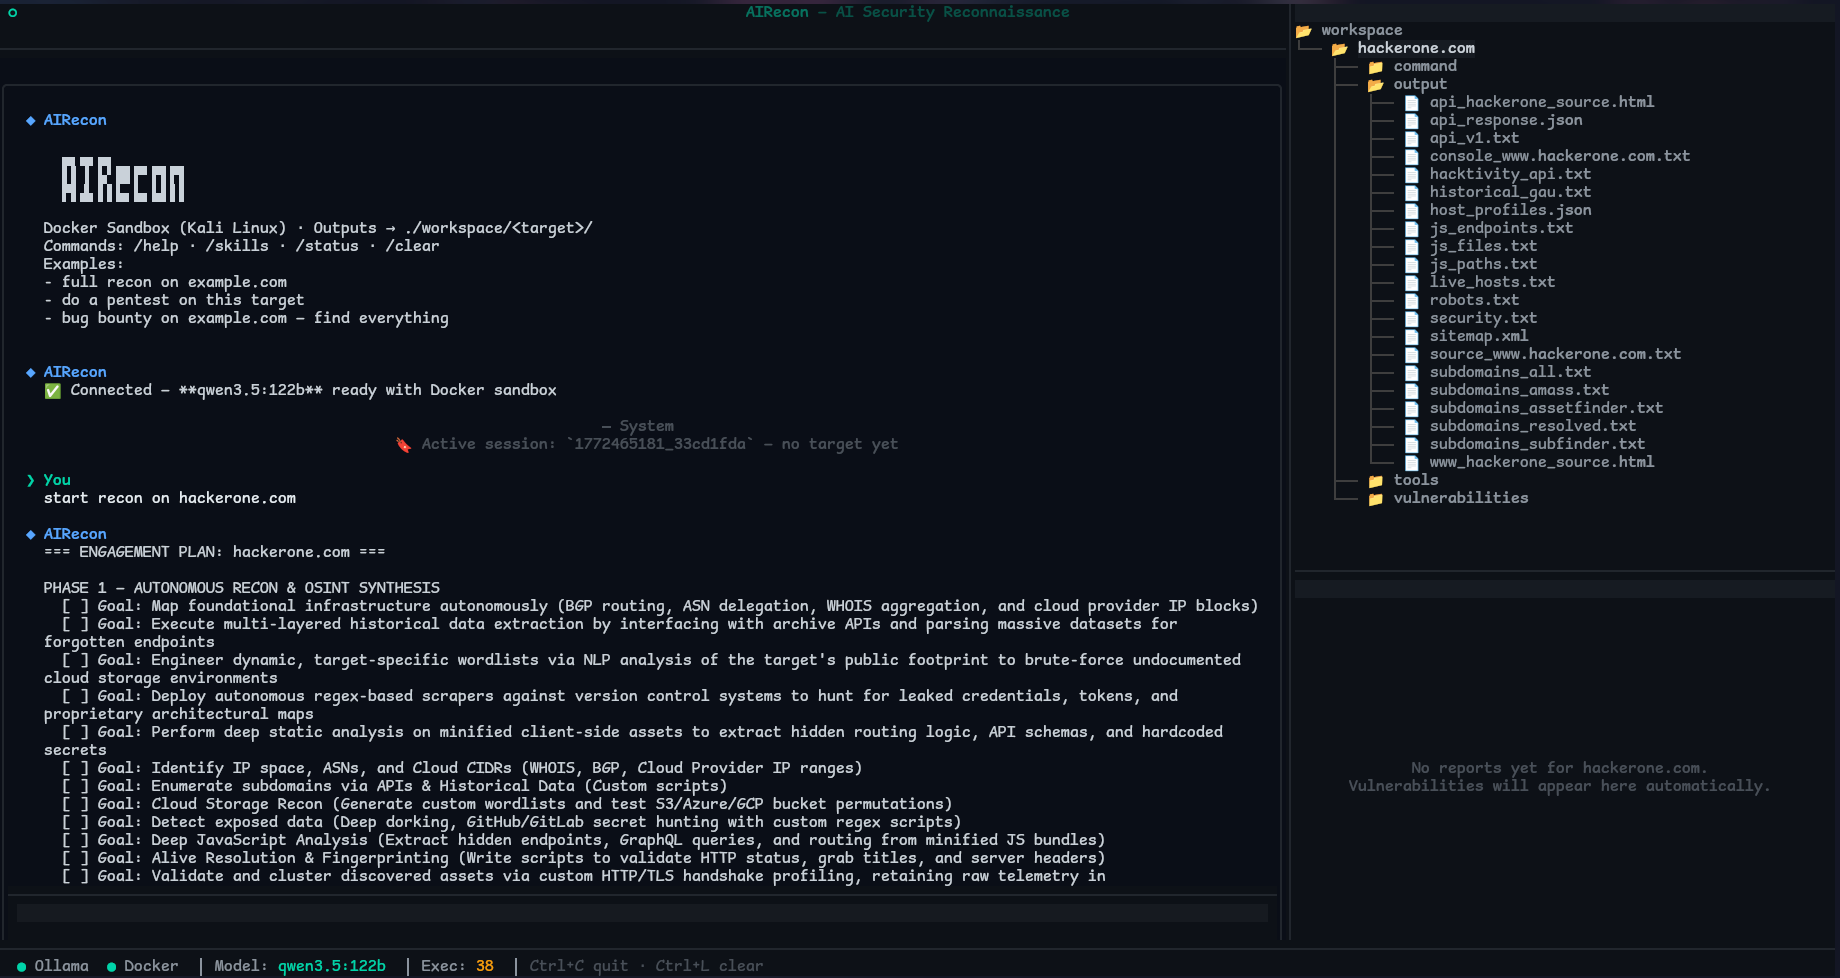 pikpikcu/airecon
AIRecon is an autonomous cybersecurity agent that combines a self-hosted Large Language Model (Ollama) with a Kali Linux Docker sandbox and a Textual…
 virologi-info/mssharepoint-scanner
A scanner for CVE-2026-55040 and CVE-2026-63520, designed to determine whether the server is affected by these two CVEs.
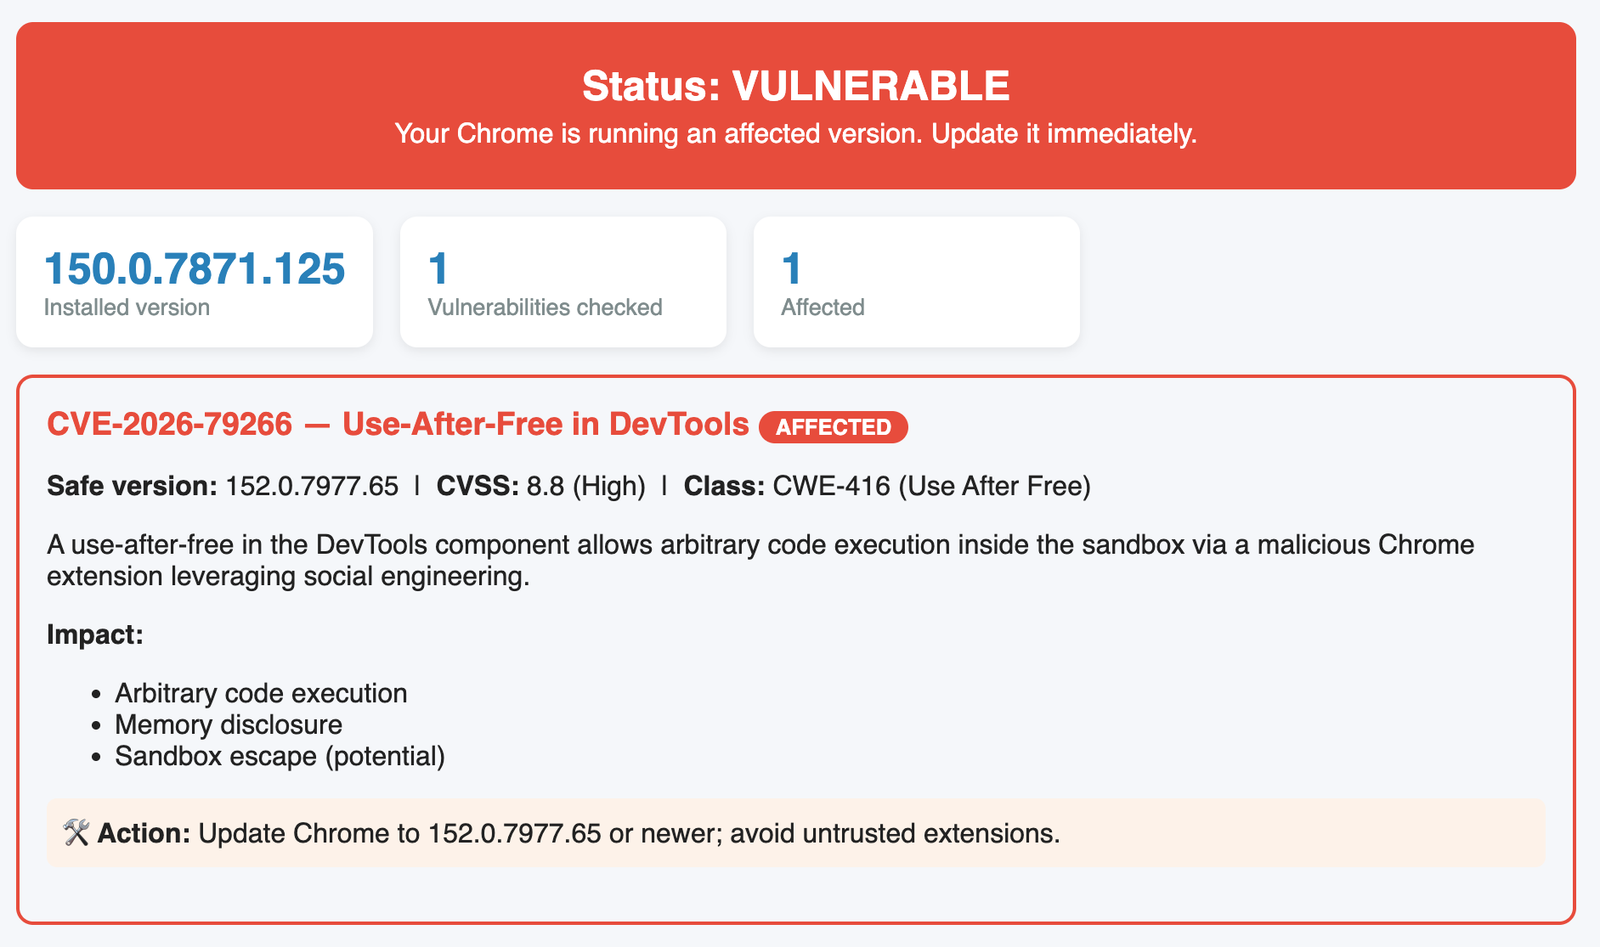 virologi-info/chrome-vuln-scanner
Check for CVE-2026-79266. A use-after-free in the DevTools component allows arbitrary code execution inside the sandbox via a malicious Chrome…
 xal6/cve-2026-64638-banner-poc
Generates a self-submitting HTML trigger page that exploits a reflected HTML injection in WordPress login (CVE-2026-64638) to display a custom…
 jvr2022/cve-2026-40345
Reproduces a stack-exhaustion denial-of-service in deepmerge-ts before 8.0.0, documents exploitation, and includes a scanner for vulnerable…
 sanaullahamanullah/xss2shell-check
Non-destructive detector for CVE-2026-64638 (XSS2Shell) — WordPress pre-auth XSS reflection primitive
 eonraider/violent-python3
Source code for the book "Violent Python" by TJ O'Connor. The code has been fully converted to Python 3, reformatted to comply with PEP8 standards…
 nichetoolkit/spring-retry-toolkit
spring retry 1.3.x fix with niche toolkit for CVE-2026-41710
 0xsha/kindarails2shell
Single-file PoC for Rails CVE-2026-66066: arbitrary file read, secret recovery, threaded scanning, and conditional RCE via signed image variations.
 k3ystr0k3r/php-8.1.0-dev-backdoor
PHP 8.1.0-dev User-Agentt Backdoor Remote Code Execution (RCE)
 simota/nginx-rift-scanner
Detect-only scanner for CVE-2026-42945 (NGINX Rift), a heap overflow in ngx_http_rewrite_module. Version detection + nginx.conf pattern analysis.…
 ammaraskar/github-dev-token-steal-poc
Proof-of-concept exploit demonstrating a GitHub OAuth token-stealing vulnerability via crafted developer workflow triggers, enabling unauthorized…
 emresandikci/nextjs-cve-2026-23870-checker
Checker and fixer for all 13 vulnerabilities in the Next.js May 2026 security release (CVE-2026-23870)
 jvr2022/cve-2026-31802
Proof of concept and technical write-up for CVE-2026-31802, a symlink path traversal in npm tar allowing arbitrary file overwrite outside extraction…
 rohitberiwala/nodejs-tar-symlink-exploit-cve-2026-29786
Technical analysis and Proof-of-Concept (PoC) for a critical Path Traversal vulnerability via Symlink manipulation in the Node.js 'tar' package…
 jvr2022/cve-2026-29786
Proof-of-concept demonstrating a hardlink path traversal in the tar npm package, allowing overwrite of files outside the extraction directory via…
 garethmsheldon/react2shell-cve-2025-55182-detector
Multi-language detection scripts for CVE-2025-55182 (React2Shell) that scan package.json files to identify vulnerable React dependency versions and…