
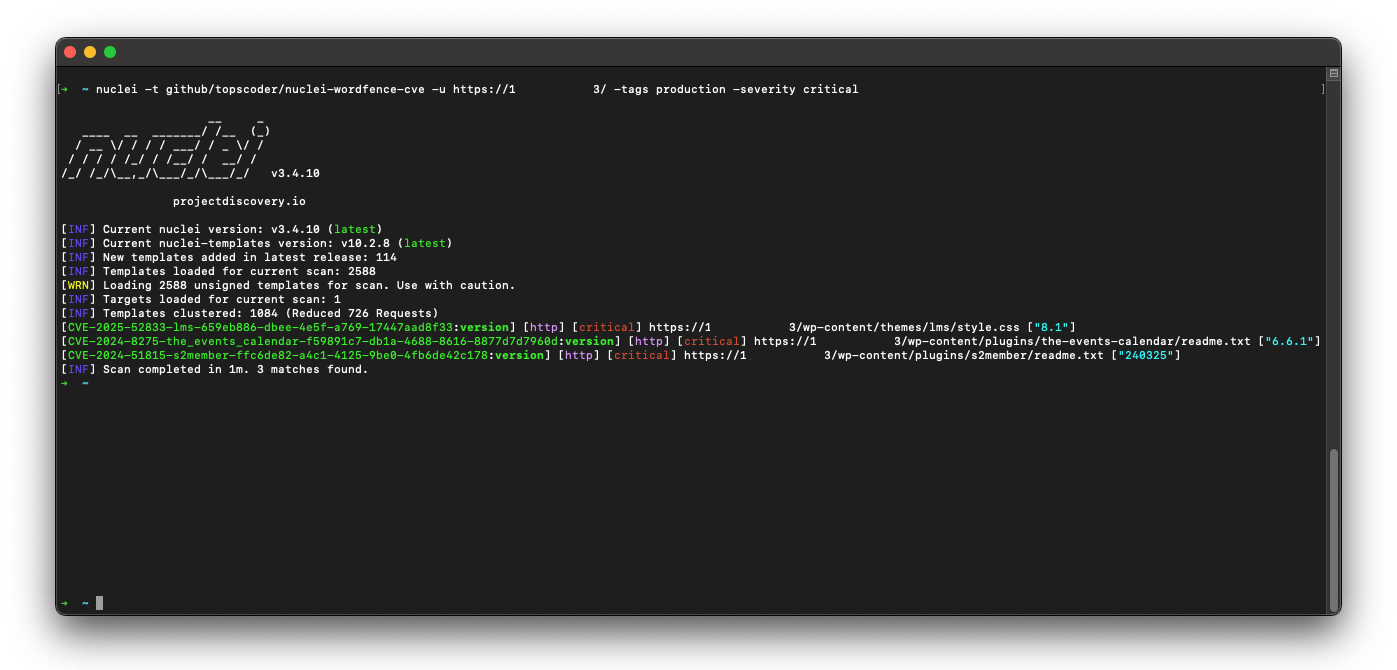
nuclei-wordfence-cve
 topscoder/nuclei-wordfence-cve
80k+ WordPress Nuclei templates, updated daily from Wordfence intel—filter by severity/tags/CVE and scan in one line. 🚀🔒
crawlerexploitationinformation-gathering+3
1.3k
topscoder/nuclei-wordfence-cve80k+ WordPress Nuclei templates, updated daily from Wordfence intel—filter by severity/tags/CVE and scan in one line. 🚀🔒
 yairhinkis/cve-2026-56096
Proof of concept and technical write-up for CVE-2026-56096, a blind Solr query injection in TYPO3 EXT:solr enabling unauthenticated field enumeration…
 nu11secur1ty/cve-nu11secur1ty
Curated repository of CVE records with CVSS scoring, providing a structured reference for vulnerability analysis, exploitation research, and security…
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 nxploited/cve-2026-91097-cve-2026-91106
HPLIP < 3.26.6 — Full admin takeover via PAPPL web interface (no auth). Related to CVE-2026-91097 through CVE-2026-91106 (CVSS 9.3)
 muradislamzada/cve-2026-93528
Technical analysis, proof of concept, and responsible disclosure timeline for CVE-2026-93528, an unauthenticated order data disclosure in NP Quote…
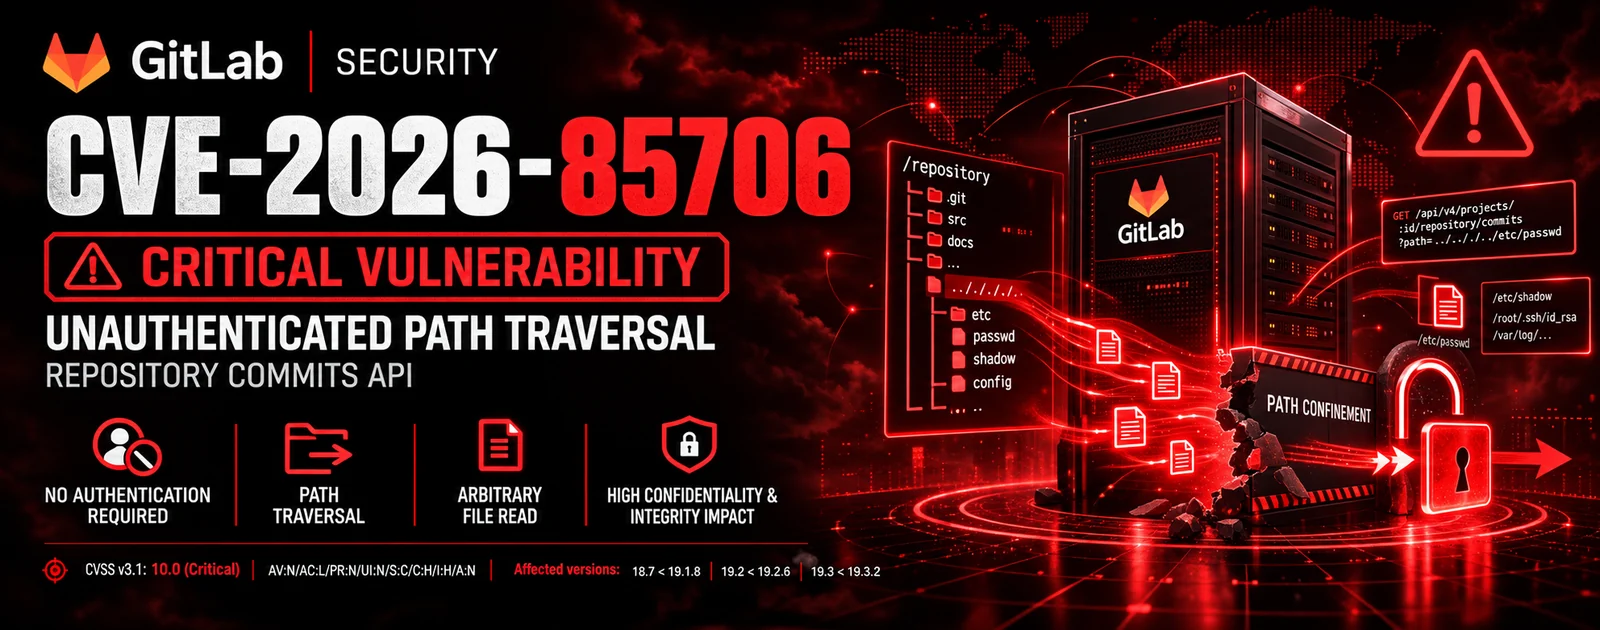 tc4dy/cve-2026-85706-poc-toolkit
Python toolkit for CVE-2026-85706 GitLab unauth file read: weaponized exploit with loot, shell, mass scan, plus non-intrusive SafeChecker audit and…
 kashyapghodasara/public_exploit-1--wordpress-cve-2021-29447
CVE-2021-29447 is an authenticated XML External Entity (XXE) vulnerability in WordPress
 gabrielunknown/cve-2026-85706
Perl PoC exploiting CVE-2026-85706, an unauthenticated GitLab path traversal enabling arbitrary file read, with bulk scanning and credential…
 jithinkrishnanrs/gitlab-cve-2026-85706-ioc
CVE-2026-85706 — GitLab Path Traversal IOC Scanner & Detection Toolkit. Detect and hunt for exploitation of the critical unauthenticated GitLab CE/EE…
 bombobombone/cve-2026-73320
Proof-of-concept and technical write-up for an unauthenticated information disclosure vulnerability in XenForo's unfurl endpoint, including a Python…
 fientix/cve-2026-8732-poc
CVE-2026-8732 | WP Maps Pro <= 6.1.0 Unauth Admin Creation
 yora1928/cve-2026-15748
Scans WordPress Forminator for CVE-2026-15748 unauthenticated RCE. Detects vulnerable sites, crawls forms, extracts nonces, runs safe upload tests.
 e4zyy/project-cve-2025-54068
Fast Python scanner detects vulnerable Laravel Livewire v3 sites (CVE-2025-54068, CVSS 9.2). Separates risky sites into vuln.txt, safe sites into…
 ehaoxiongdiycw/cve-2014-085
Nuclei template and PoC for exploiting ZooKeeper unauthorized access vulnerability (CVE-2014-085), enabling automated security testing against target…
 minhhk68/cve-2026-13736
Proof-of-concept exploit and technical advisory for an unauthenticated member PII disclosure in a WordPress REST API directory plugin, including…
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.
 0xterror/cve-2023-22047---oracle-peoplesoft-lfi
CVE-2023-22047 is a critical unauthenticated Local File Inclusion (LFI) vulnerability in Oracle PeopleSoft Enterprise PeopleTools. This exploit…