

CVE-2023-31594
 yozarseef95/cve-2023-31594
IC Realtime ICIP-P2012T 2.420 is vulnerable to Incorrect Access Control
exploitationhardware-securityiot-security+3
yozarseef95/cve-2023-31594IC Realtime ICIP-P2012T 2.420 is vulnerable to Incorrect Access Control
 dpfkdlemtp/epson-eh-tw5350-advisories
Security advisories for CVE-2021-43716/43717/43718 (Epson EH-TW5350)
 judgedbykira/cve-2026-25938-fuxa-unauthenticated-rce
An explanation and PoC to exploit CVE-2026-25938 Unauthenticated RCE Vulnerability on FUXA
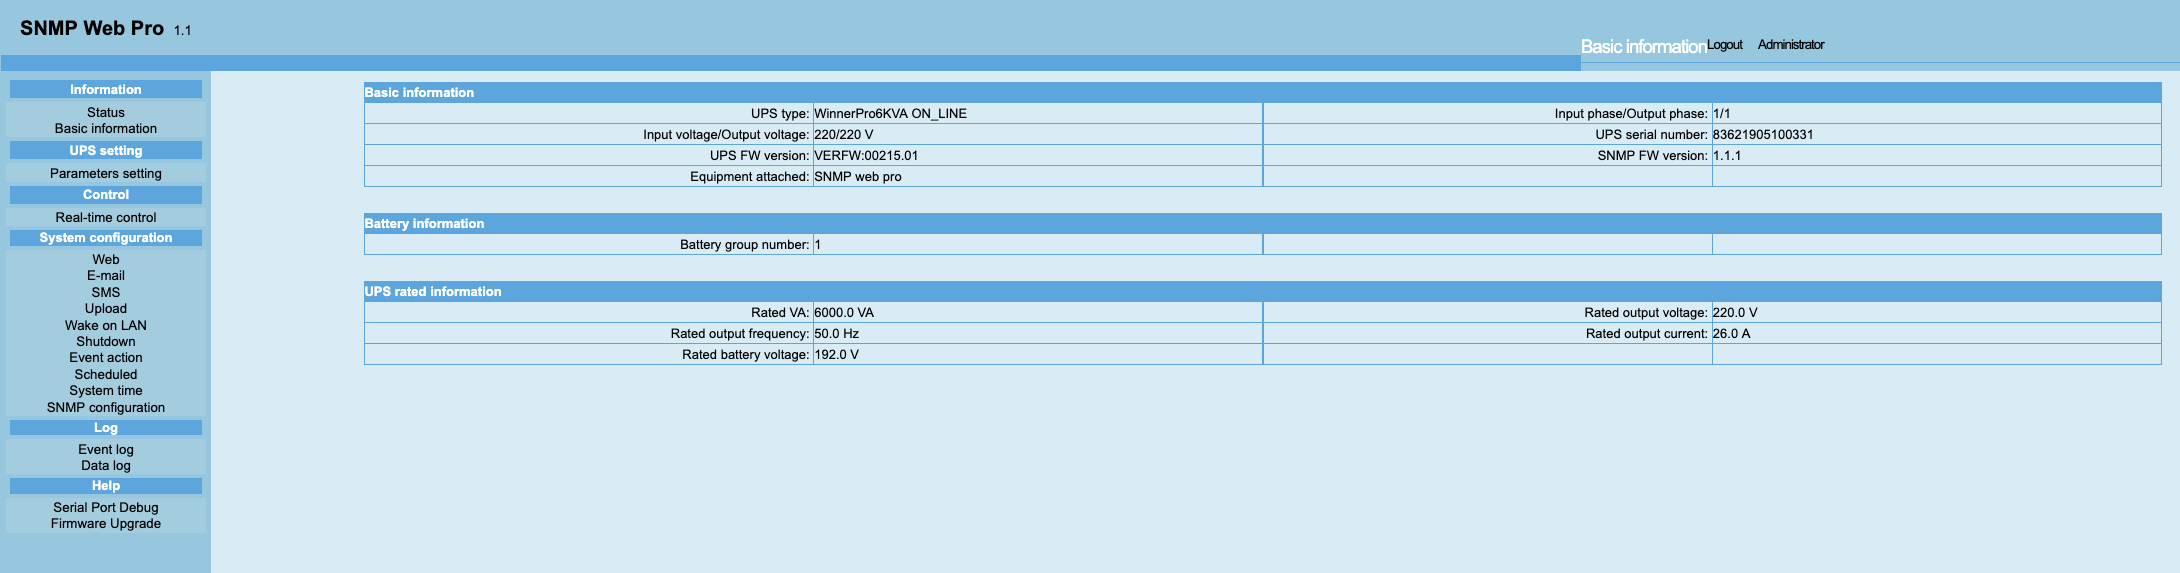 virgula0/cve-2026-44402
Pre-Authenticated Full Root Remote Command Execution in Voltronic Power SNMP Web Pro 1.1
 michaeladamgroberman/cve-2026-54477
CVE-2026-54477: Admin Panel Missing Security Headers (clickjacking/XSS) - Gardyn (ICSA-26-183-03)
 ret2c/cve-2026-8023
PoC for CVE-2026-8023: Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal')
 michaeladamgroberman/cve-2026-28767
CVE-2026-28767: Missing Authentication on Admin Notifications Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 kensh1k/cve-2026-36438
Documentation of CVE-2026-36438: a vulnerability in Intelbras VIP 1230 B/D G4 devices allowing remote attackers to obtain administrator account…
 novaek/cve-2026-0073-research
CVE-2026-0073 is an RCE with a CVSS severity score of 8.3, and here we will explain how it works.
 minanagehsalalma/zyxel-wax650s-research-notebook-public
Wiki-style research notebook for Zyxel WAX650S firmware emulation and vulnerability analysis
 remenis/cve-2025-67159
Vatilon-based IP camera firmware allows authentication bypass and plaintext credential exposure via web.cgi API requests.
 xernary/cve-2025-63820
Proof-of-concept of vulnerability found in Totolink A720R router
 szym0n13k/cve-2025-55971-blind-unauthenticated-ssrf-in-tcl-smart-tv-upnp-dlna-avtransport
TCL 65C655 Smart TV, running firmware version V8-R75PT01-LF1V269.001116 (Android TV, Kernel 5.4.242+), is vulnerable to a blind, unauthenticated…
 joelczk/cve-2025-48461
Technical disclosure of a predictable session cookie vulnerability (CVE-2025-48461) in Advantech WISE-4060 IoT portal, enabling bruteforce…
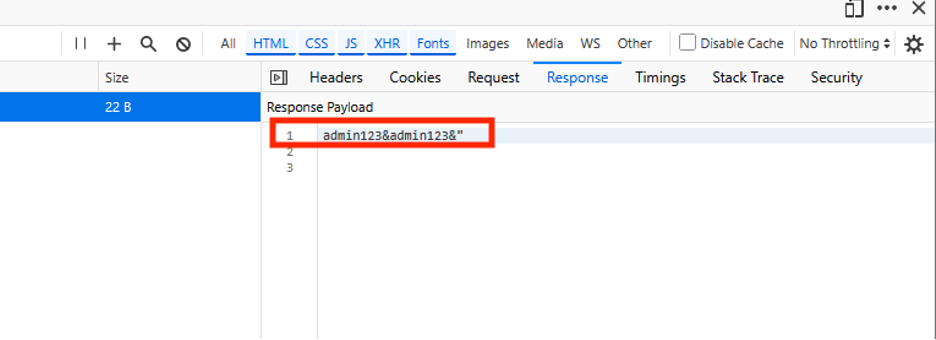 weedl/cve-2025-45620
Disclosure of client-side authentication bypass in AVer camera web interface exposing unencrypted credentials via network traffic monitoring.
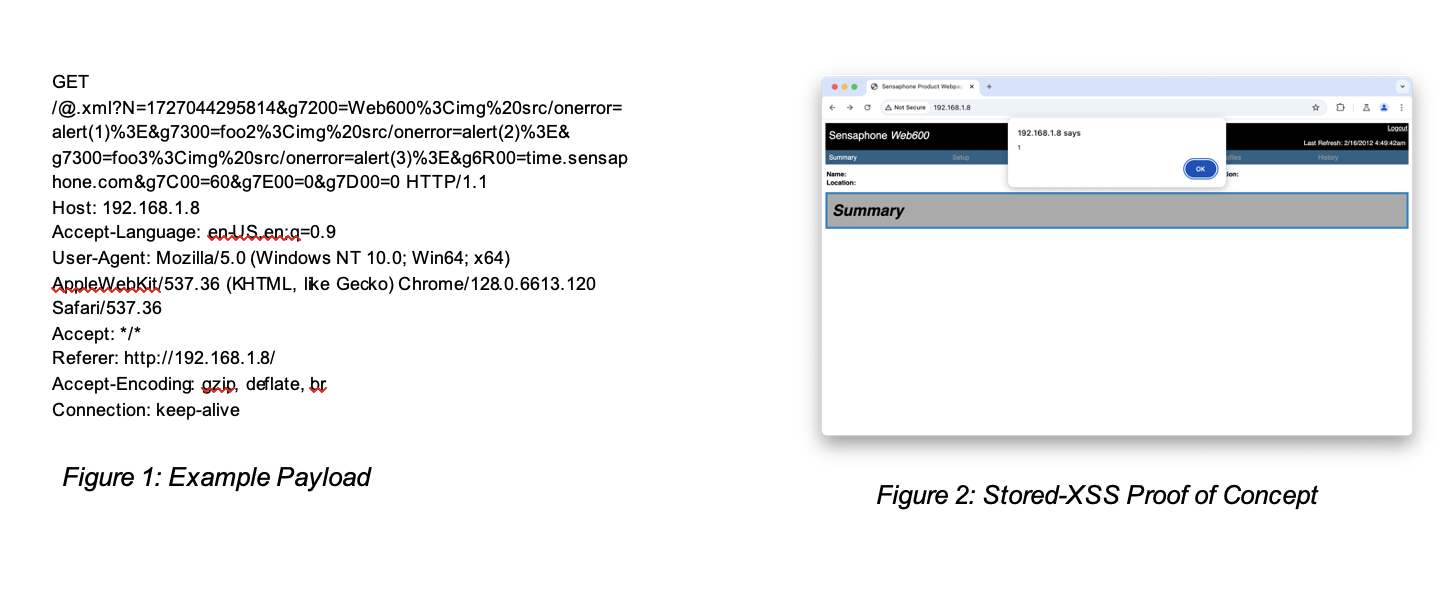 tcbutler320/cve-2024-55040-sensaphone-xss
Public disclose of several stored XSS vulnerabilities in the Sensaphone WEB600 (CVE-2024-55040)
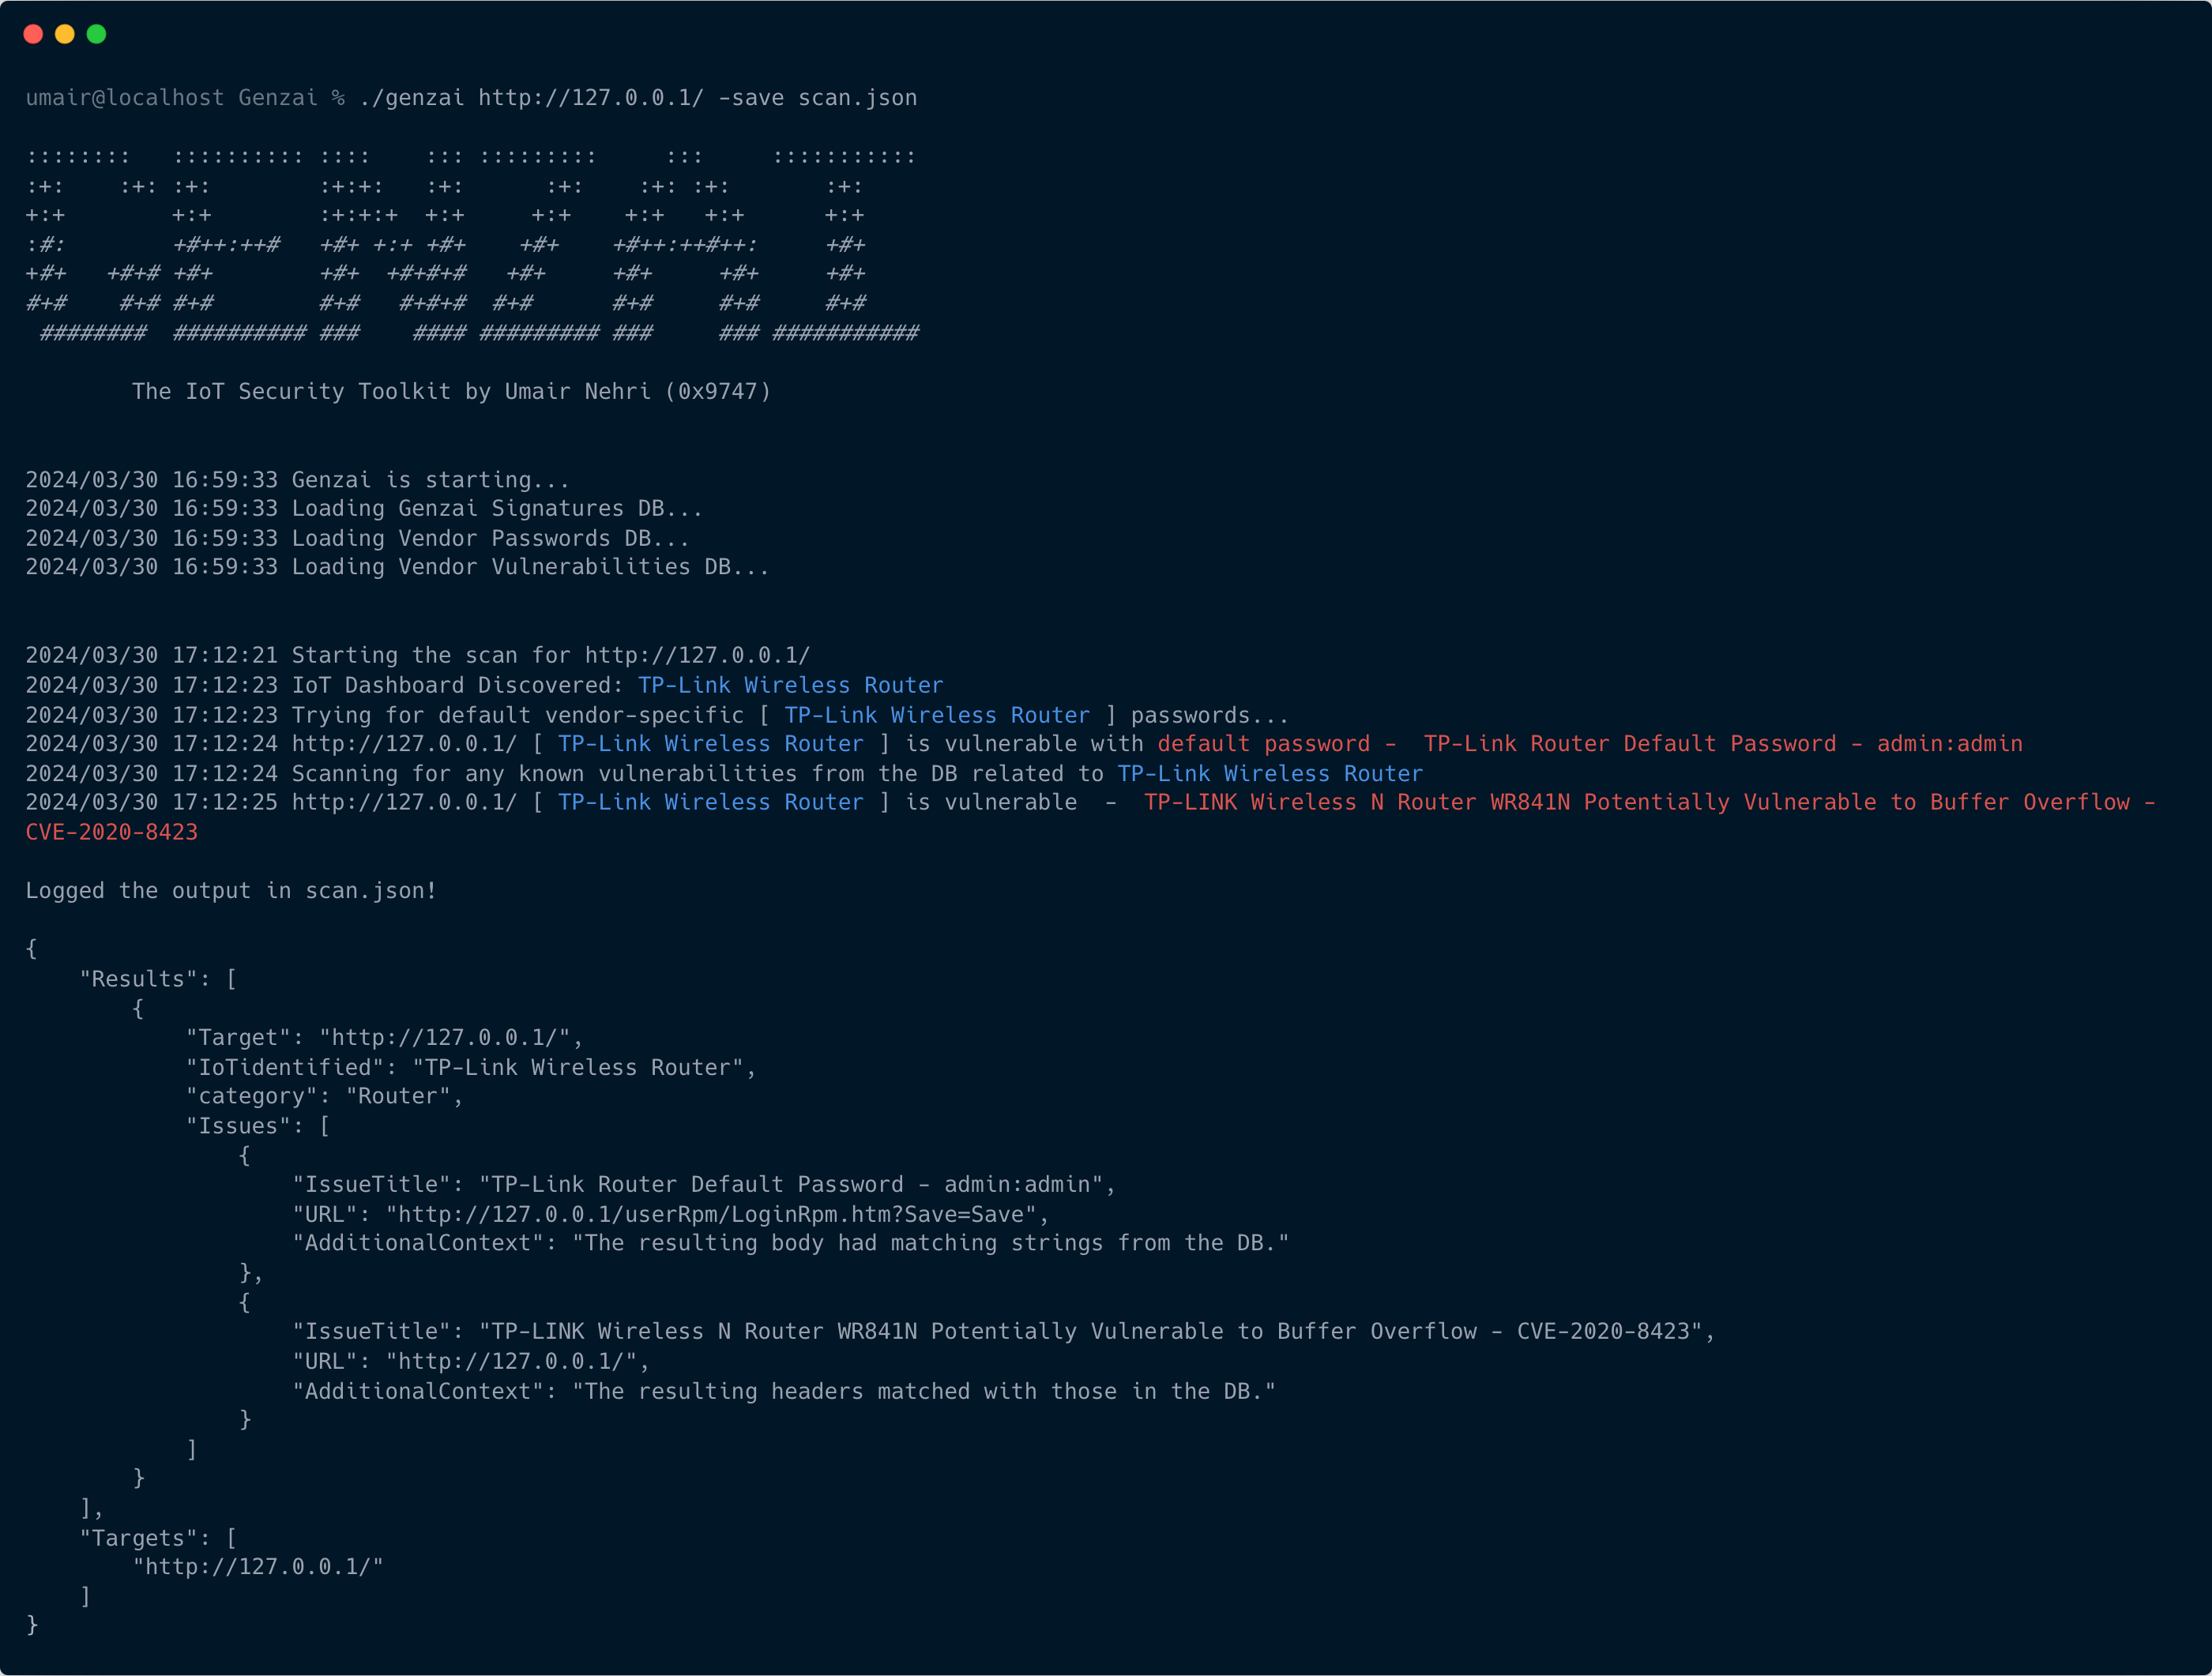 umair9747/genzai
The IoT security toolkit to help identify IoT related dashboards and scan them for default passwords and vulnerabilities.
 vulncheck-oss/cisco-ios-xe-implant-scanner
Go-based scanner that detects implanted Cisco IOS XE systems by sending crafted HTTP requests to identify compromised devices and vulnerable versions.