

waf-fu
 confused-binary/waf-fu
Terminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
cloud-securitydefensive-toolsincident-response+6
2
confused-binary/waf-fuTerminal UI for browsing and replaying AWS WAF v2 logs from CloudWatch, S3, and the sampling API, with YAML filtering, auth detection, and…
 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 infokom-ki/zimbra-cve-2026-73570-rules
Wazuh detection rules for CVE-2026-73570, an OS command injection in Zimbra Collaboration Suite, monitoring web access logs and zimbra.log for…
 paulvkitor/log4shellwithlog4j2_13_3
Springboot web application accepts a name get parameter and logs its value to log4j2. Vulnerable to CVE-2021-44228.
 0xbruno/wsusploit.net
C# proof-of-concept for CVE-2025-59287 targeting WSUS, demonstrating exploitation and providing defensive detection guidance for IIS logs and Windows…
 sam00/poc-cve-2026-42826-2026-42826-microsoft-azure-devops-information-disclosure-vulnerability
Exploits CVE-2026-42826 to enumerate and extract sensitive Azure DevOps data via unauthenticated REST API requests: pipeline YAML, variable groups,…
 zedocun/incident-analysis-response-check-point-security-gateway-cve-2024-24919-lfi-exploitation
Incident Response (IR) case study documenting the investigation of an exploitation attempt targeting CVE-2024-24919 (Arbitrary File Read) on a Check…
 nccgroup/pcap-burp
Pcap importer for Burp
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
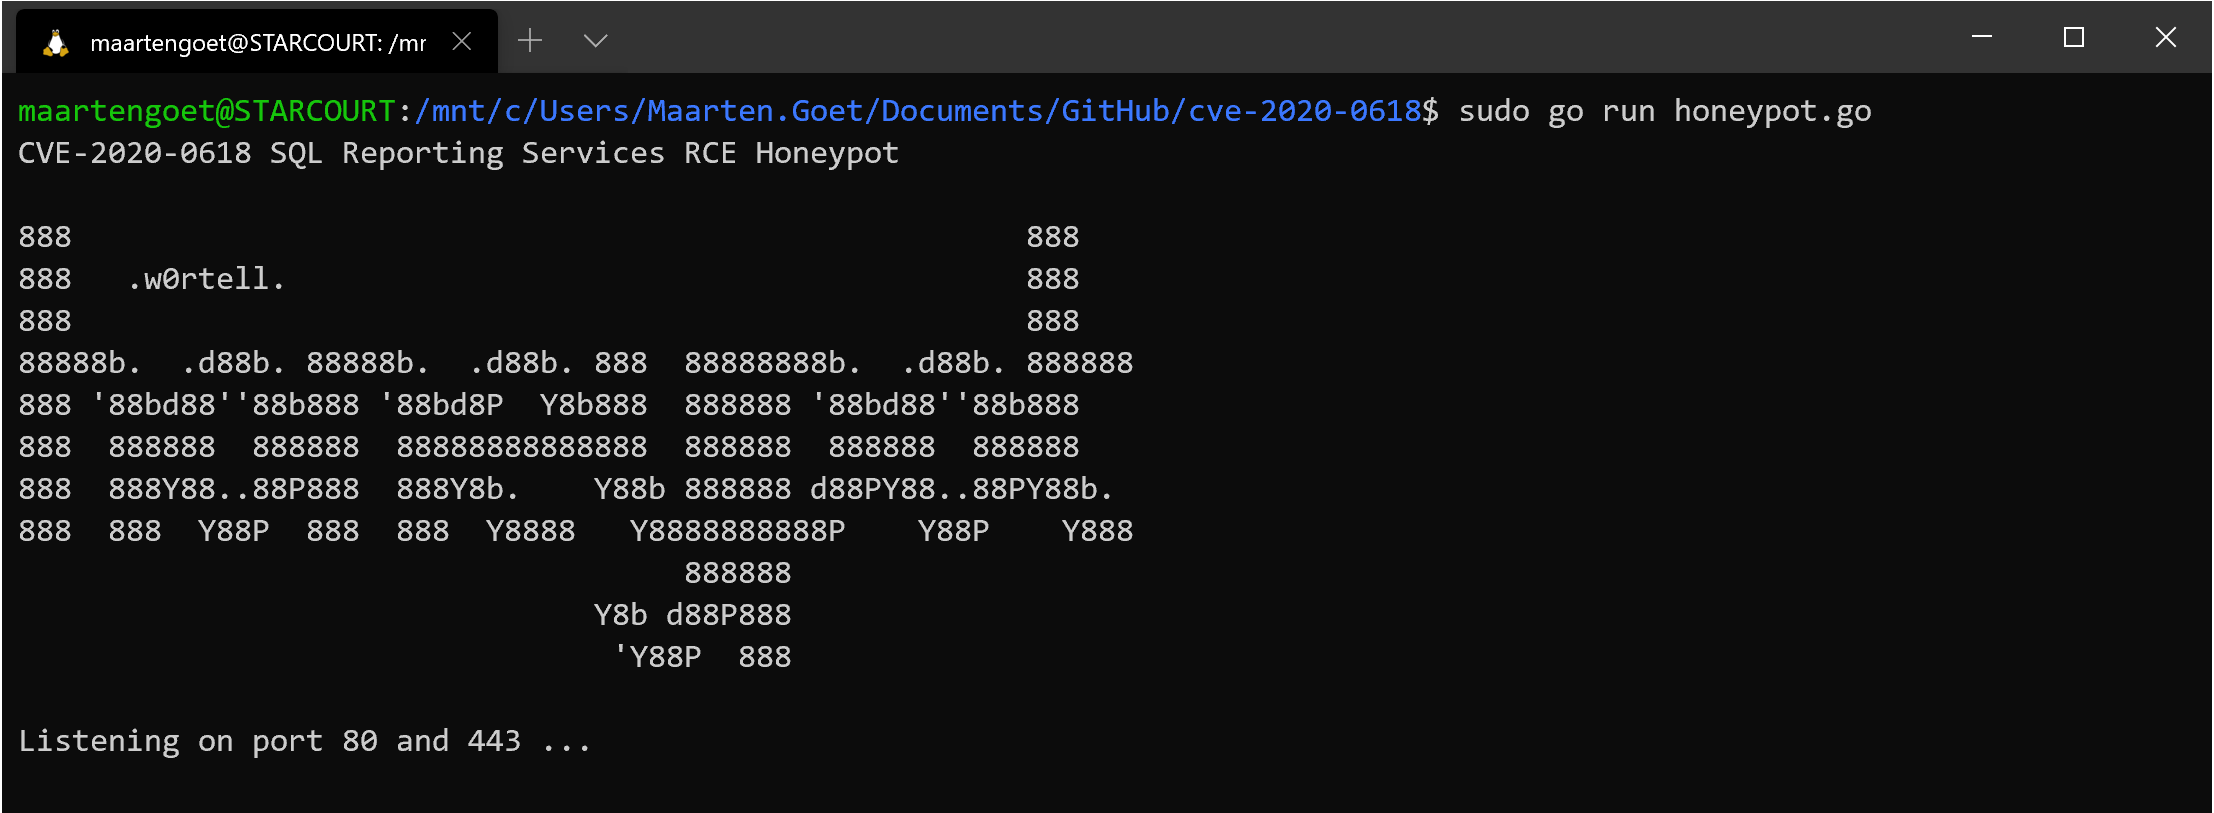 wortell/cve-2020-0618
CVE-2020-0618 Honeypot
 xw77cve/cve-2019-7642
Proof-of-concept exploit for CVE-2019-7642 demonstrating unauthenticated access to DNS query logs and login history on vulnerable D-Link routers via…
 eliushhimel/citrix-honeypot
Citrix ADC (NetScaler) Honeypot. Supports detection for CVE-2019-19781 and login attempts
 zach115th/toolshellfinder
Scans Windows IIS logs for signs of CVE-2025-53770 & CVE-2025-53771
 meganekos/secure-by-default-rce-demo
Secure-by-default demo lab showing how container hardening (distroless images, non-root, read-only filesystem, runtime-injected secrets) can…
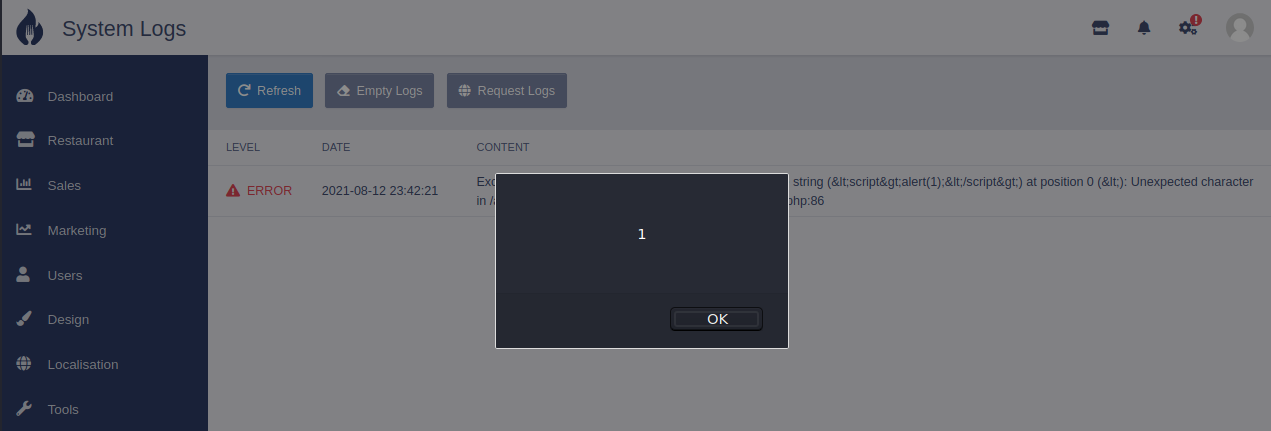 huskyhacks/cve-2021-38699-stored-xss
Stored XSS in TastyIgniter v3.0.7 Restaurtant CMS
 nles-crt/cve-2023-6895
Python script to scan websites for CVE-2023-6895 vulnerability. Sends crafted requests, checks responses, and logs exploitable URLs with progress bar…
 hestat/drupal-check
Tool to dive Apache logs for evidence of exploitation of CVE-2018-7600
 nagisayumaa/cve-2025-10377
CVE-2025-10377