
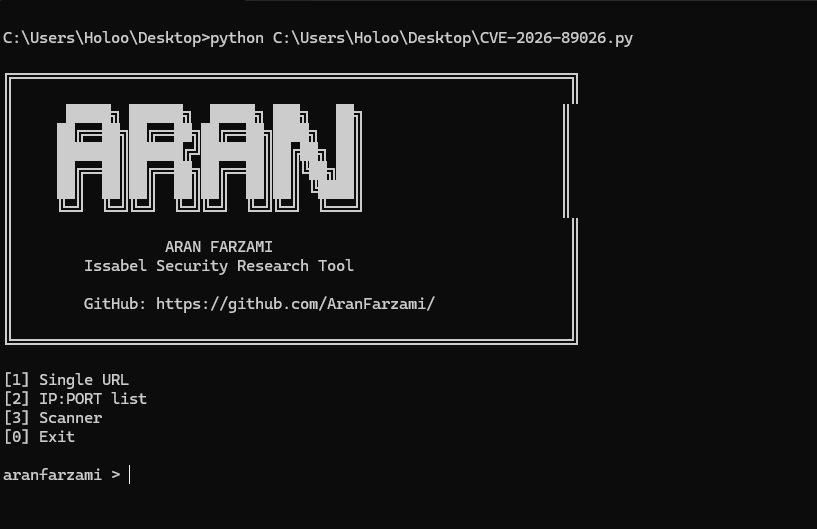
CVE-2026-89026
 aranfarzami/cve-2026-89026
PoC exploit and scanner for CVE-2026-89026, validating the Issabel PBXAPI authentication bypass via forged HS256 JWTs across single or listed targets.
authenticationexploitationpenetration-testing+5
1
aranfarzami/cve-2026-89026PoC exploit and scanner for CVE-2026-89026, validating the Issabel PBXAPI authentication bypass via forged HS256 JWTs across single or listed targets.
 gmh5225/fullscreenbrowserphishing
PoC of the phishing through setting browser in the fullscreen mode
 chandrimanath04-hue/cve-2024-31218-webhood-lab
Docker-based lab reproducing CVE-2024-31218, an unauthenticated PocketBase admin creation flaw in Webhood, with PoC, detection, and remediation…
 amulyakaushik/cve-2023-27163-lab
Docker-based lab reproducing CVE-2023-27163 SSRF in Request-Baskets, with exploitation verification, detection script, and network-isolation…
 s3v3n-jg/cve-2026-76460
Educational Flask lab simulating CVE-2026-76460 authentication bypass, with vulnerable, secure, and strict modes plus a PoC exploit script and…
 sebastianmautner/nuclei-cve-2025-24813
University Project of developing a template for safely testing for the CVE 2025-24813 on a server. It is intentionally made to not leave any lasting…
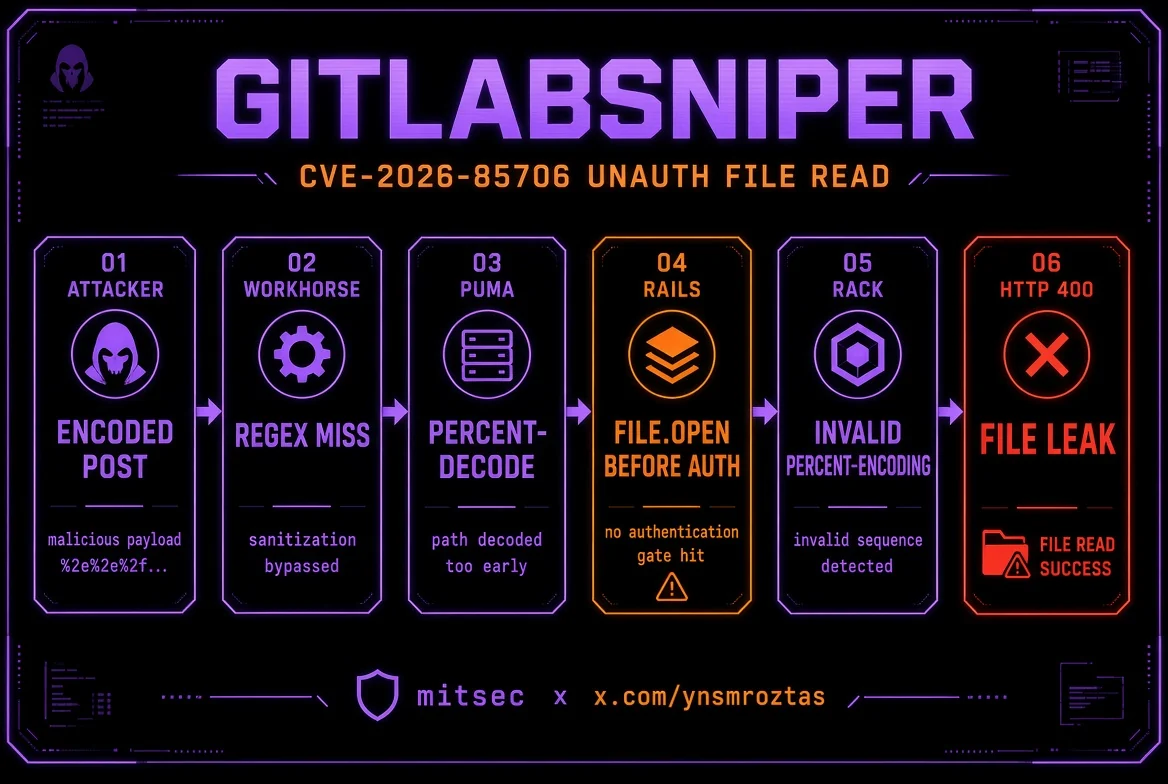 ynsmroztas/gitlabsniper
Single-file Python scanner and exploit for CVE-2026-85706, an unauthenticated arbitrary file read in self-managed GitLab CE/EE, with project…
 mattia-maria-scivoletto/internet-security-project
Academic report and LaTeX sources analyzing Maltego vulnerability CVE-2020-24656, an XXE injection enabling data exfiltration, written for an…
 moksh-nfsu/cve-2026-36392
Proof-of-concept for stored XSS in RISE CRM item title field (CVE-2026-36392), demonstrating session hijacking and account takeover with remediation…
 horkimhab/cve-2026-19516
Proof-of-concept for CVE-2026-19516, demonstrating session spoofing and SSRF in Grafana MCP. Intended for authorized security research and education…
 horkimhab/cve-2026-85046
Proof-of-concept for Chrome V8 zero-day CVE-2026-85046, providing educational exploit code and setup instructions for authorized security research in…
 horkimhab/cve-2026-psa-2026-00043-1
Proof-of-concept exploit for an unauthenticated root authentication bypass in Proxmox VE 7.0-8.0.3, intended for authorized security testing and…
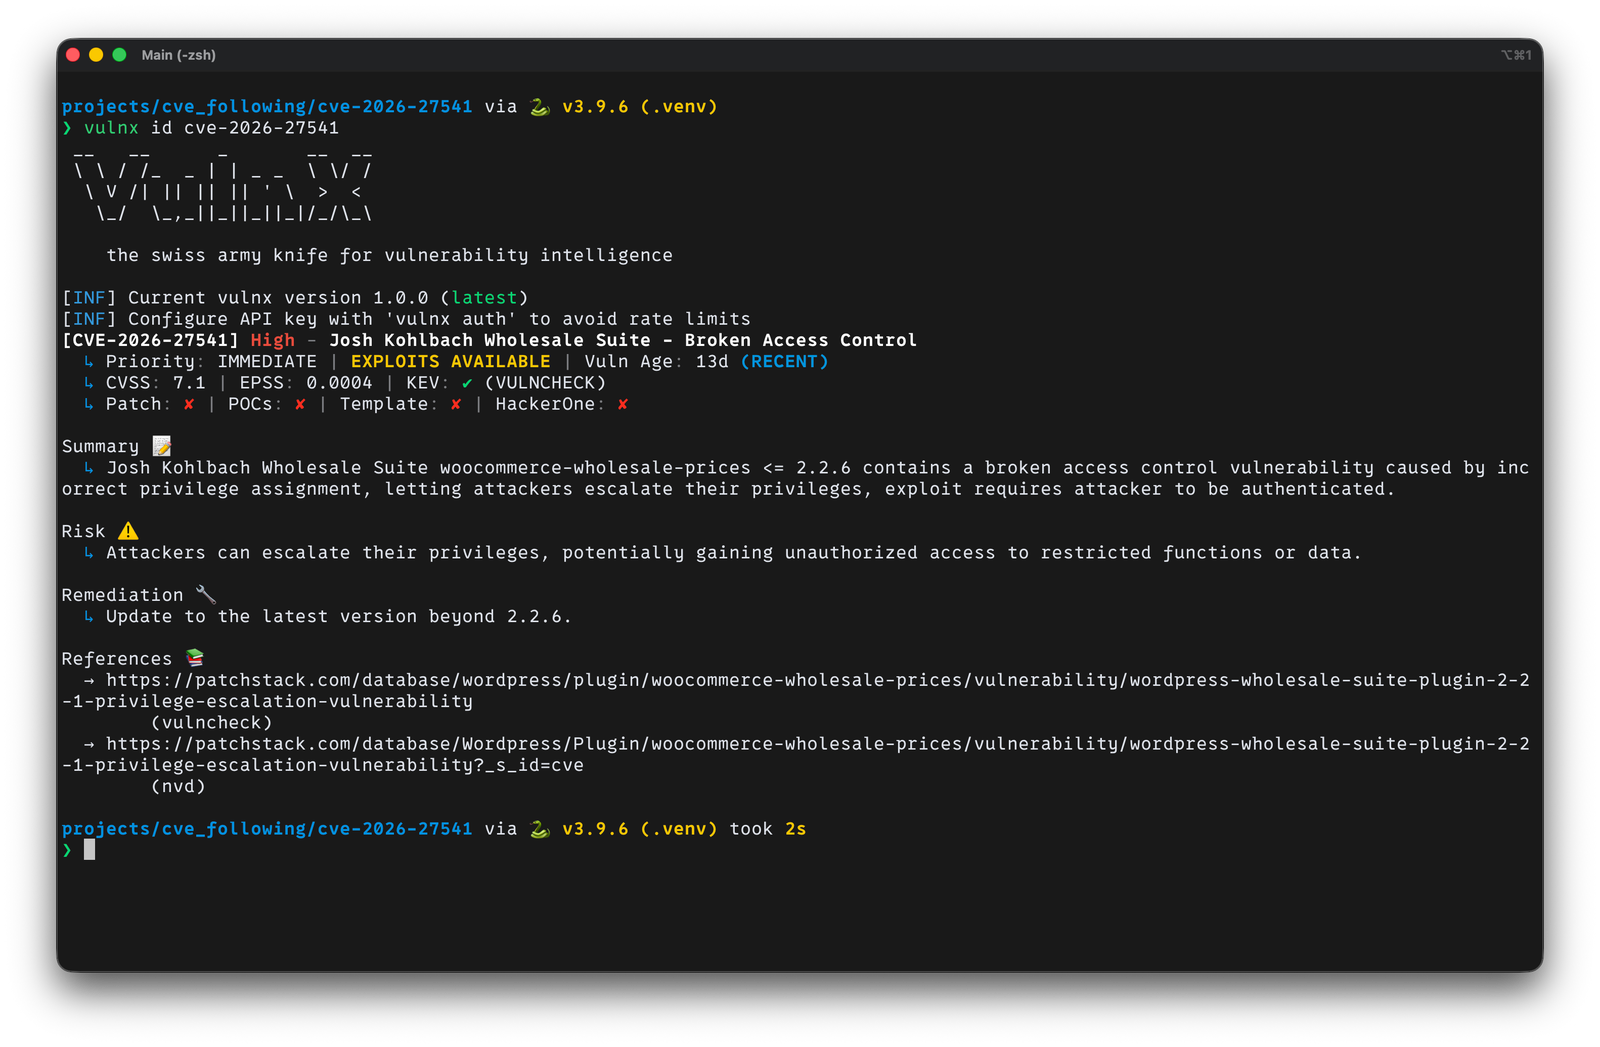 rootdirective-sec/cve-2026-27541-analysis-lab
Docker lab for reproducing CVE-2026-27541, an authenticated privilege escalation in WooCommerce Wholesale Prices. Compares vulnerable and patched…
 eqstlab/cve-2026-19478
Proof-of-concept exploit for CVE-2026-19478, an unauthenticated GraphQL injection in GitLab CE/EE allowing arbitrary method invocation and project…
 owasp/browser-security-project
Community-driven project providing guidance and resources to improve browser security, including best practices and educational materials for…
 lindhunt/cve-2026-26211
Public disclosure and proof-of-concept for CVE-2026-26211, a stored XSS vulnerability in Ekushey Project Manager CRM v5.0, including technical…
 tansique-17/cve-2025-61456
Public disclosure and proof-of-concept for a reflected XSS vulnerability (CVE-2025-61456) in an e-commerce project, including technical details, CVSS…
 tansique-17/cve-2025-61455
Public disclosure and proof-of-concept for CVE-2025-61455, a critical SQL injection in E-commerce Project v1.0, including technical details, PoC, and…