
CVE-2026-23921
 qucklecrabik/cve-2026-23921
Proof-of-concept exploit for CVE-2026-23921, a time-based blind SQL injection in Zabbix API via the sortfield parameter, enabling data extraction…
database-securityexploitationpenetration-testing+3
qucklecrabik/cve-2026-23921Proof-of-concept exploit for CVE-2026-23921, a time-based blind SQL injection in Zabbix API via the sortfield parameter, enabling data extraction…
 repo4chu/cve-2026-78804_dolibarr_authenticated_sql_injection
The action responsible for setting the per-warehouse stock alert threshold (`seuil_stock_alerte`) accepts user-controlled input and later…
 mimiloveexe/cve-2023-6567-poc
Proof-of-concept exploit for a time-based blind SQL injection in the LearnPress WordPress plugin, allowing unauthenticated attackers to extract…
 static-flow/burpsuite-team-extension
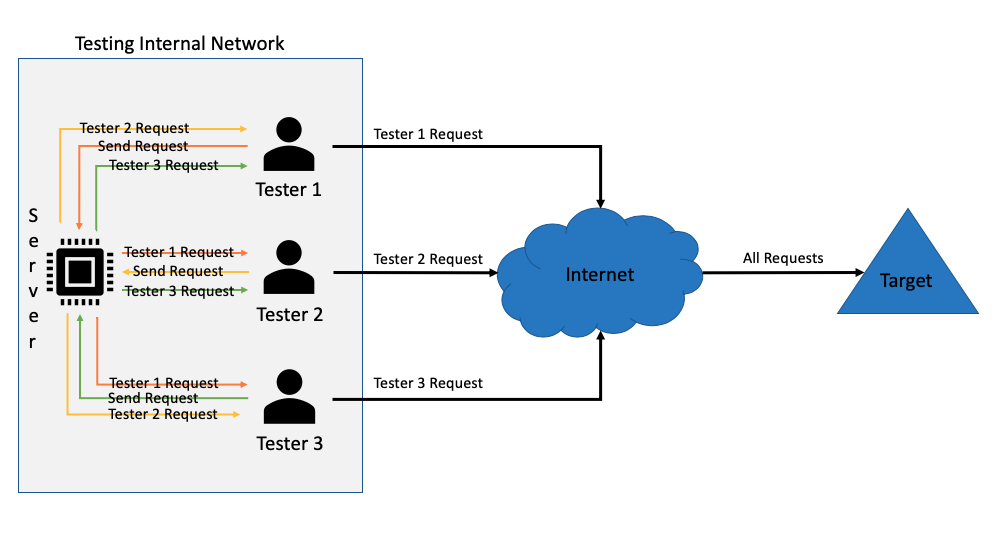
This Burpsuite plugin allows for multiple web app testers to share their proxy history with each other in real time. Requests that comes through your…
 hernanrodriguez1/sqli_sleeps
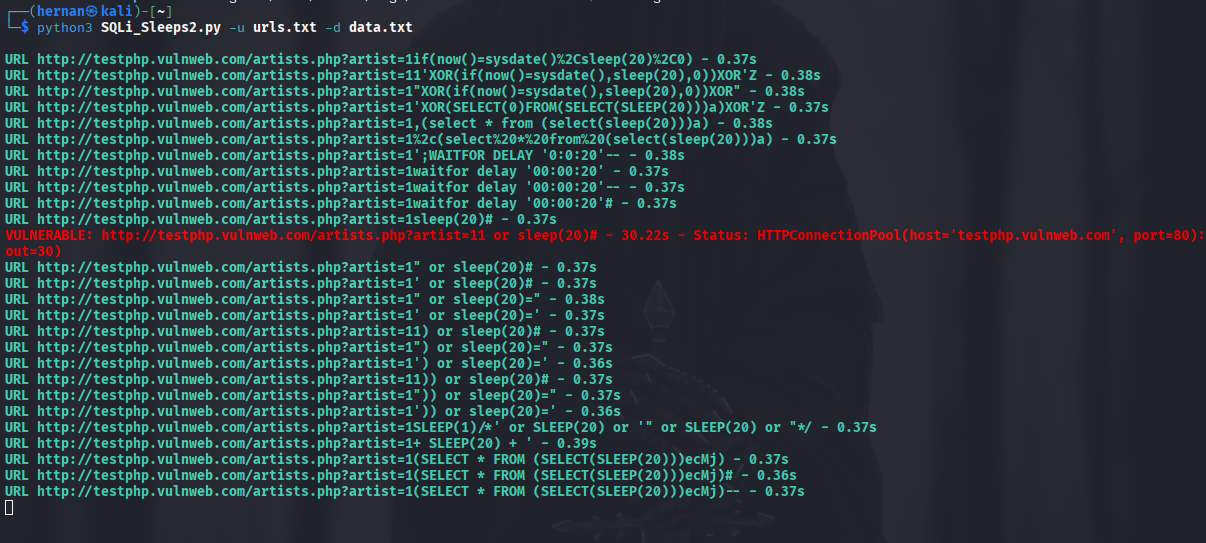
Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…
 nccgroup/requests-racer
Small Python library that makes it easy to exploit race conditions in web apps with Requests.
 kara-git/cve-2026-49048-joomcck-sqli
CVE-2026-49048 — JoomCCK 6.4.0 Unauthenticated SQL Injection (CVSS 9.8)
 padayali-jd/cve-2025-22964
Proof-of-concept exploit for CVE-2025-22964, a time-based blind SQL injection vulnerability in DDSN Interactive cm3 Acora CMS 10.1.1, enabling…
 ubaydev/cve-2024-8856
WordPress WP Time Capsule Plugin Arbitrary File Upload Vulnerability
 gquere/cve-2017-6913
Stored XSS proof-of-concept exploit for open-xchange OX App Suite webmail, demonstrating unescaped HTML time tag event attributes leading to…
 hyunchiya/cve-2025-14124
Unauthenticated SQL Injection (Time-Based Blind)
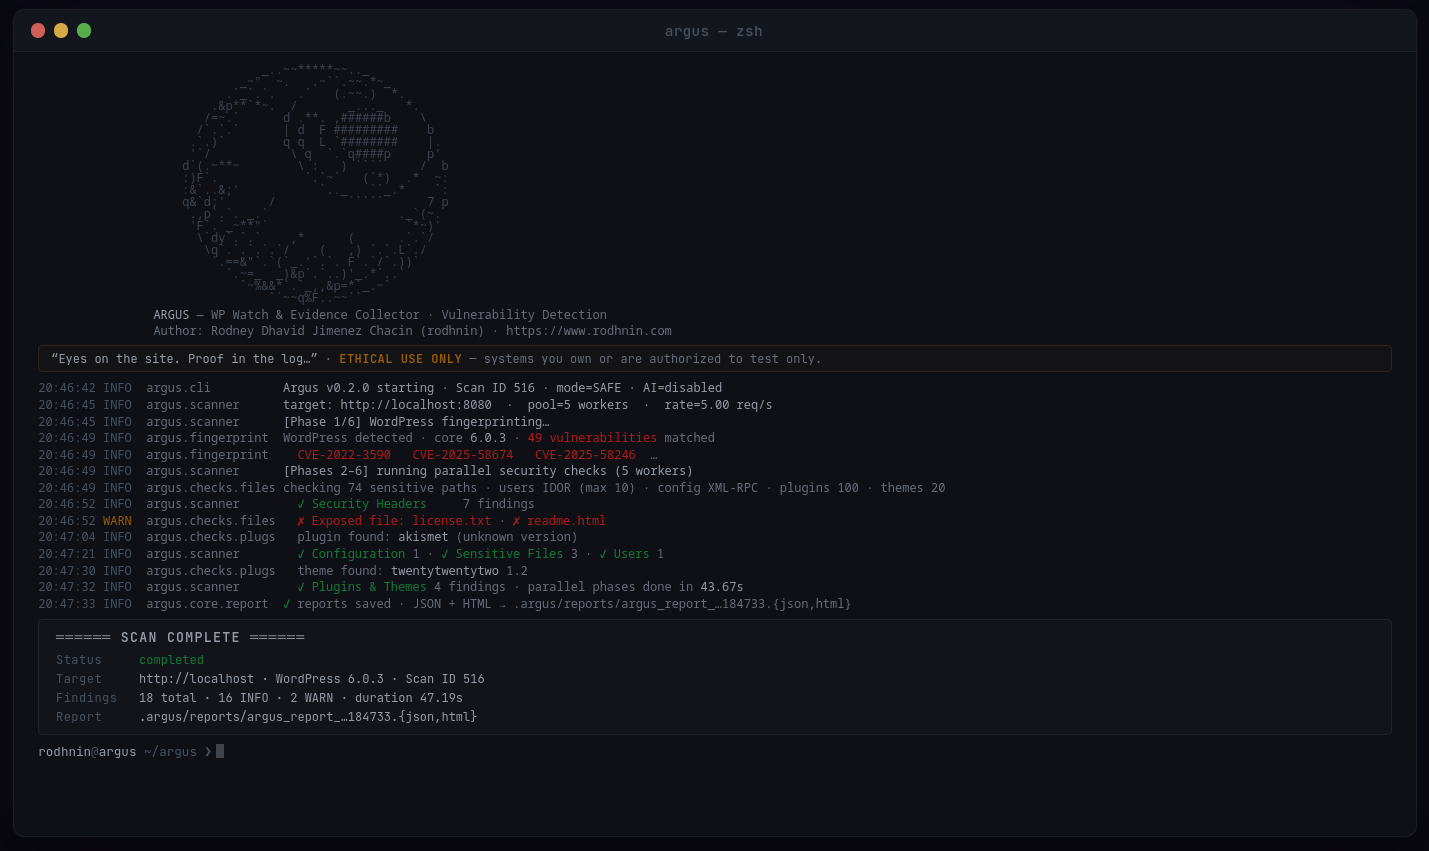 rodhnin/argus-wp-watcher
WordPress security scanner with AI-powered analysis, ethical compliance framework, and professional reporting.
 0xrar/cve-2021-41773
Exploit for Apache 2.4.49
 aether-0/cve-2025-55575
Time-based SQL injection detection template for SMM Panel targeting the service_detail parameter via crafted POST requests to /ajax_data, using…
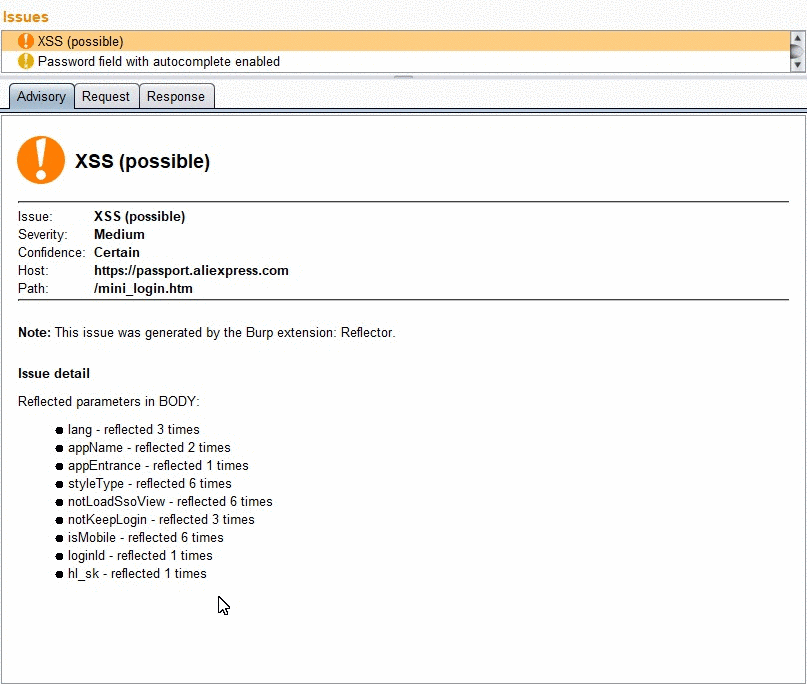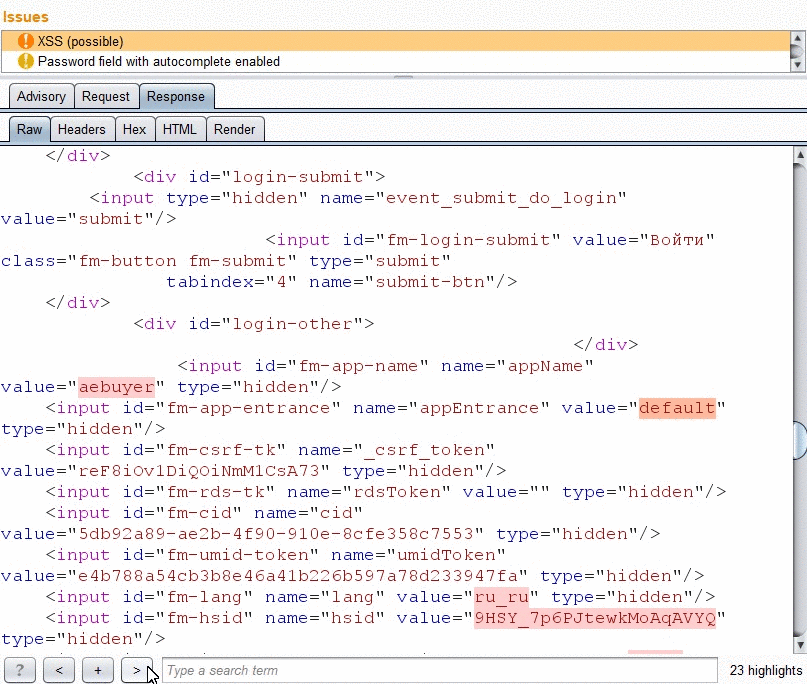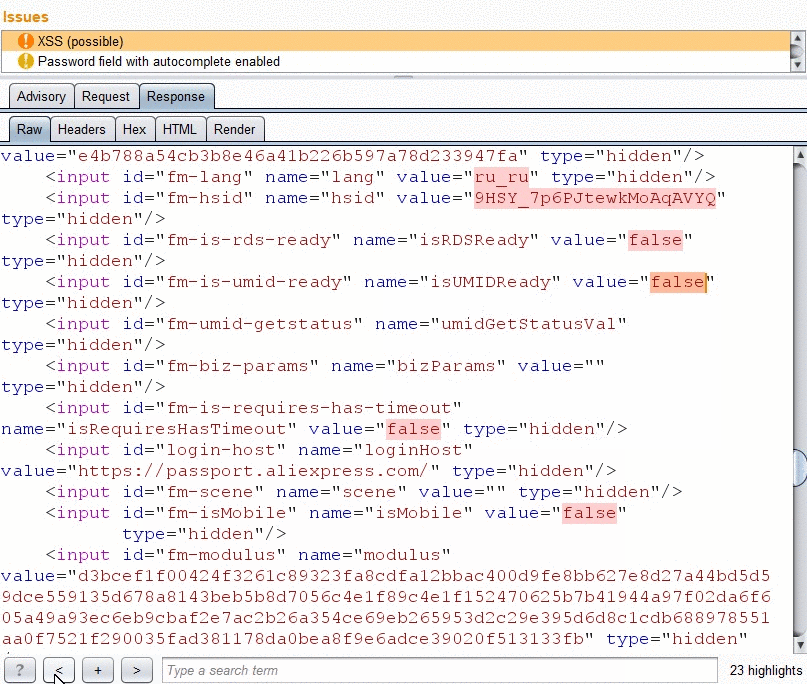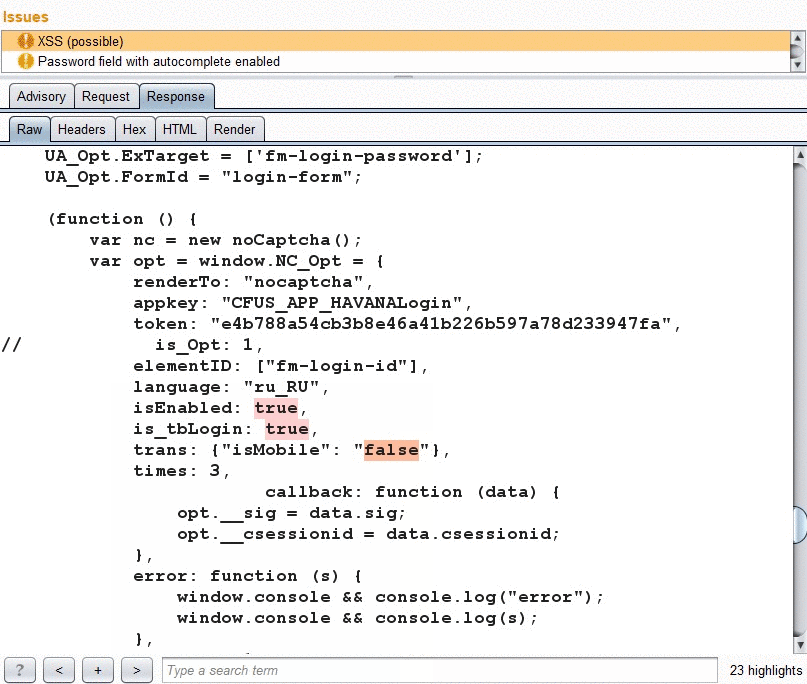 elkokc/reflector
Burp plugin able to find reflected XSS on page in real-time while browsing on site
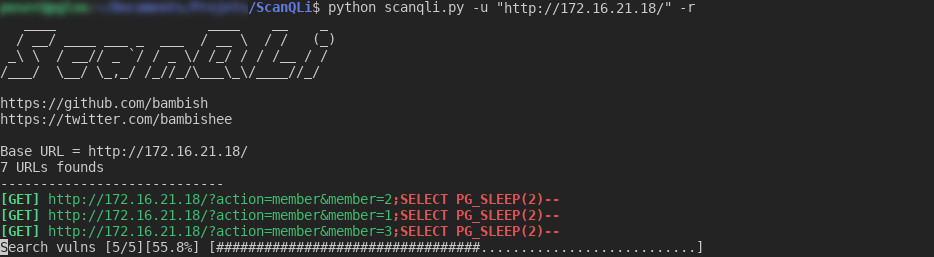 bambish/scanqli
SQLi scanner to detect SQL vulns
 mhaskar/blinder
A python library to automate time-based blind SQL injection
 jewel591/xssmap
Python-based XSS vulnerability scanner with support for POST/GET requests, parameter injection in cookies/referer/user-agent, and multiple encoding…