

security-harness
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
ai-securitycode-analysisdevsecops+9
22
dmdhrumilmistry/security-harnessMulti-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…
 unh00k3d/cve-2026-85706
Root-cause analysis, vulnerable Docker lab, and PoC scripts for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab via a Workhorse/Puma…
 rahulreddykarne/cve-2026-57836-confluent_kafka
Disabled TLS Certificate Verification for HashiCorp Vault KMS in confluent-kafka
 theqmaks/resolver
This extension integrates popular CAPTCHA solution services into BurpSuite to process different types of CAPTCHAs without manual intervention.
 valtersit/wordpress-cve-scanner
Scan your WordPress core, themes and plugins for known CVEs from the command line. Open source, auditable, privacy-first — powered by the ValtersIT…
 hassham1/cve-2026-94545-nextjs-og-poc
Isolated Docker lab and non-destructive Python scanner reproducing CVE-2026-94545, the Next.js next/og ImageResponse SVG injection, with vulnerable…
 polosss/by-poloss..-..cve-2026-19125
Verified proof-of-concept exploiting the EthPress <= 2.3.5 unauthenticated authentication bypass, granting a WordPress administrator session via a…
 1833ravikumar-max/cve-2021-41773-apache-path-traversal-lab
Docker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
 hassham1/cve-2026-87902
WordPress Core <= 7.1.1 unauthenticated LFI to RCE - validation lab, PoC, nuclei template (GHSA-7hp8-65ch-5whp)
 dinosn/cve-2026-87902-wordpress-lfi-lab
Reproduction lab + URL-list scanner + PoC for CVE-2026-87902 / GHSA-7hp8-65ch-5whp — WordPress get_page_template() unauthenticated LFI to conditional…
 i3it/cve-2026-18322
Root-cause analysis, passive version checker, and lab PoC for CVE-2026-18322, an unauthenticated privilege escalation in the Smart Popup by Supsystic…
 ressl/cve-2026-87902-poc
PoC for CVE-2026-87902 — unauthenticated path traversal in WordPress page-template resolution (local PHP inclusion, conditional RCE) with a pinned…
 mubix/ai-ctf
Local AI Capture-the-Flag platform with guided lessons on prompt injection, tool-call abuse, and OSINT against six simulated chatbot personas.
 learnerxuan/cve-2026-29057-poc
Docker-based lab reproducing CVE-2026-29057 Next.js request smuggling, comparing vulnerable 15.5.12 against patched 15.5.13 with a raw chunked HTTP…
 abraxas/cve-2026-79752
CVE-2026-79752 disclosure pack for CakePHP 5.2.13 SQL injection via FunctionsBuilder::cast, with a Python PoC script and Docker lab for authorized…
 abraxas/cve-2026-81648
Proof-of-concept exploit and lab for CVE-2026-81648, an unauthenticated arbitrary file deletion flaw in the WordPress CryptoPayment Gateway plugin.
 chandrimanath04-hue/cve-2024-31218-webhood-lab
Docker-based lab reproducing CVE-2024-31218, an unauthenticated PocketBase admin creation flaw in Webhood, with PoC, detection, and remediation…
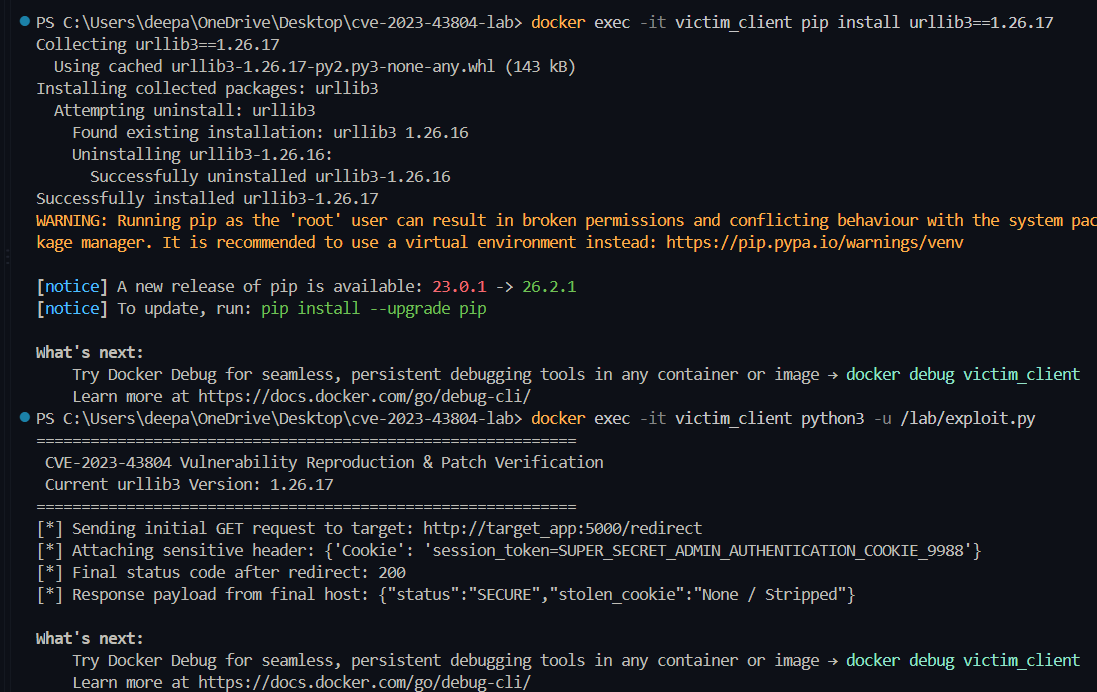 deepanshu-khurana/cve-2023-43804
Containerized three-tier lab reproducing CVE-2023-43804 urllib3 cookie leak via cross-origin redirects, with exploit script and patch verification.