
proxy2
 inaz2/proxy2
HTTP/HTTPS proxy in a single python script
general-purpose-utilitiesweb-proxies-interceptionweb-security
inaz2/proxy2HTTP/HTTPS proxy in a single python script
 openresty/lua-resty-limit-traffic
Lua library for limiting and controlling traffic in OpenResty/ngx_lua
 elazarl/goproxy
A customizable HTTP/HTTPS proxy library for Go supporting regular forwarding, CONNECT tunneling, MITM TLS interception, and programmatic…
 rmottanet/unauthscout
UnauthScout is an OSINT (Open Source Intelligence) tool developed in Bash for passive exploration of assets on version control platforms (GitLab and…
 fantaghost/fgscanner
FGscanner is an advanced, opensource URL scanner.
 mindpatch/startpage-parser
parsing search results from startpage search engine (based on google.com results)
 shoucheng3/xwiki__xwiki-rendering_cve-2023-37908_14-10-3
Generic wiki/HTML rendering system that converts textual input between syntaxes (wiki, HTML, XHTML). This repository contains a patched version…
 spamscanner/url-regex-safe
Regular expression matching for URL's. Maintained, safe, and browser-friendly version of url-regex. Resolves CVE-2020-7661 for Node.js servers.
 shoucheng3/vert-x3__vertx-web_cve-2019-17640_3-9-3
Analysis and exploitation code for CVE-2019-17640, a vulnerability in Vert.x-Web. Provides a targeted test case for security researchers validating…
 usutani/study-turbolinks-link
Known security vulnerabilities detected. CVE-2022-21831 Critical severity CVE-2025-24293 Critical severity CVE-2020-8162 High severity CVE-2024-26144…
 shanika04/dashbuilder
CVE-2016-4999
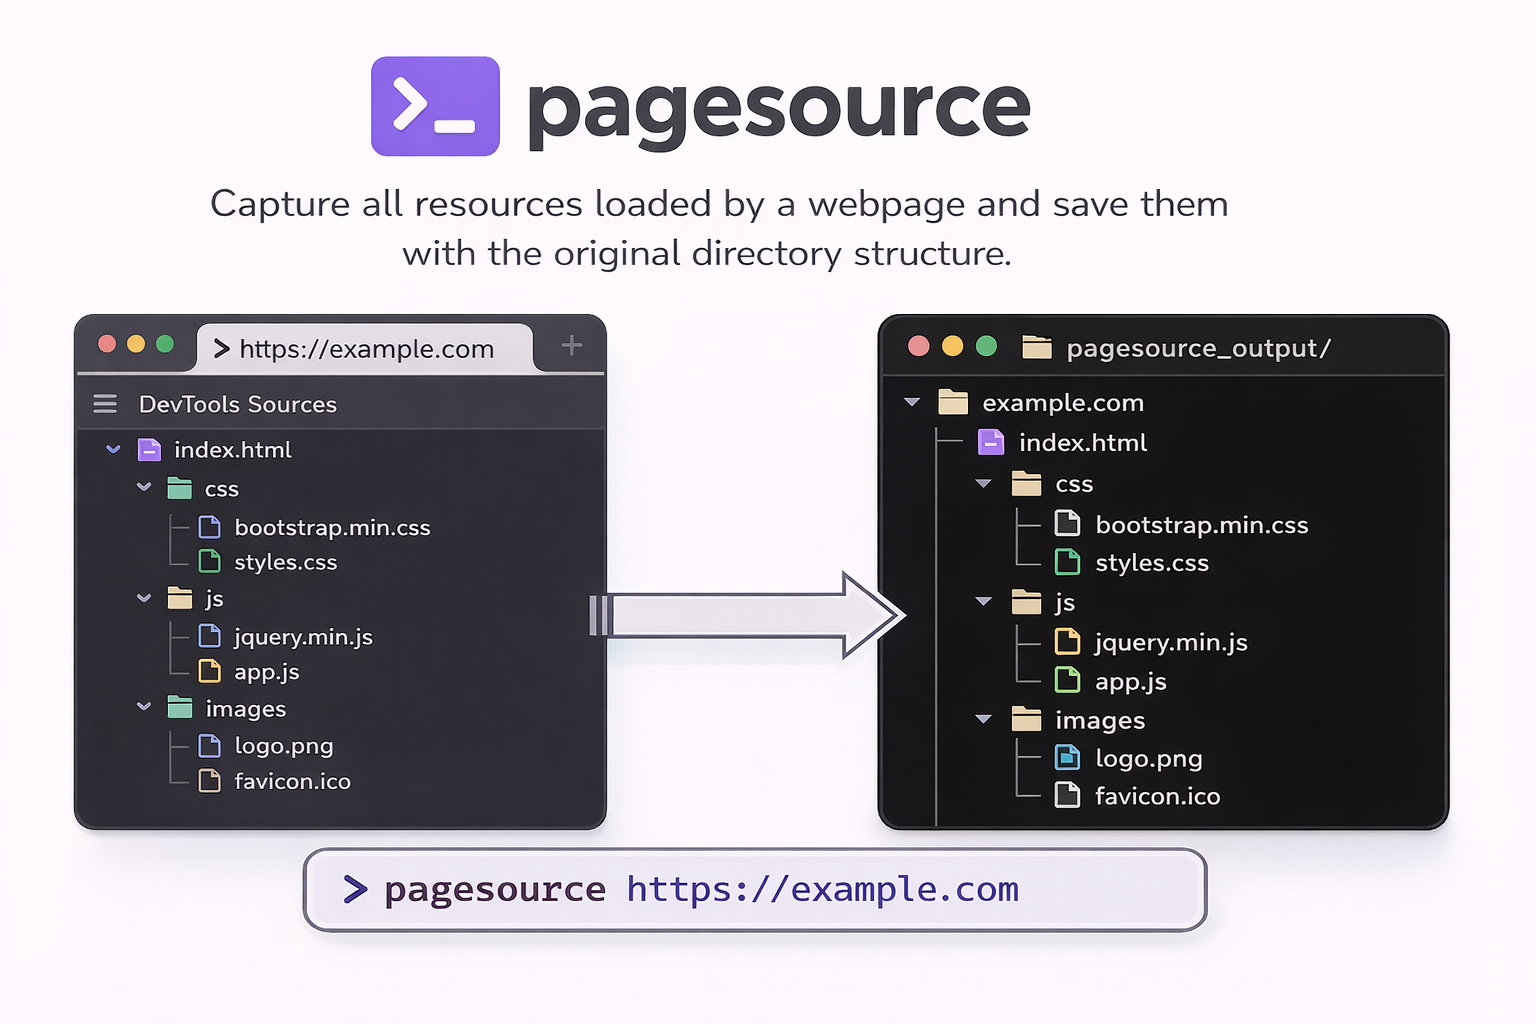 timf34/pagesource
CLI to download websites' actual JS/CSS/assets (not flattened HTML)
 bcdannyboy/cve-2023-38545
A proof of concept for testing CVE-2023-38545 against local curl
 imjdl/cve-2012-4431
Apache Tomcat source code repository for CVE-2012-4431, a Java servlet container vulnerability. Provides the vulnerable codebase for analysis and…
 trinadh465/jetty_9.4.31_cve-2023-26048
Repository dedicated to the analysis and exploitation of CVE-2023-26048 in Jetty 9.4.31, providing vulnerability research and proof-of-concept code…
 trinadh465/jetty_9.4.31_cve-2021-34428
Repository dedicated to CVE-2021-34428, a vulnerability in Jetty 9.4.31. Provides a patched or vulnerable version for analysis and testing of the…
 trinadh465/external_curl_aosp10_r33_cve-2021-22924
Command-line tool and library for transferring data using URL syntax, supporting various protocols including HTTP, FTP, and more.
 fastify/send
Node.js library for streaming files as HTTP responses with support for partial content, conditional requests, and configurable caching headers.…