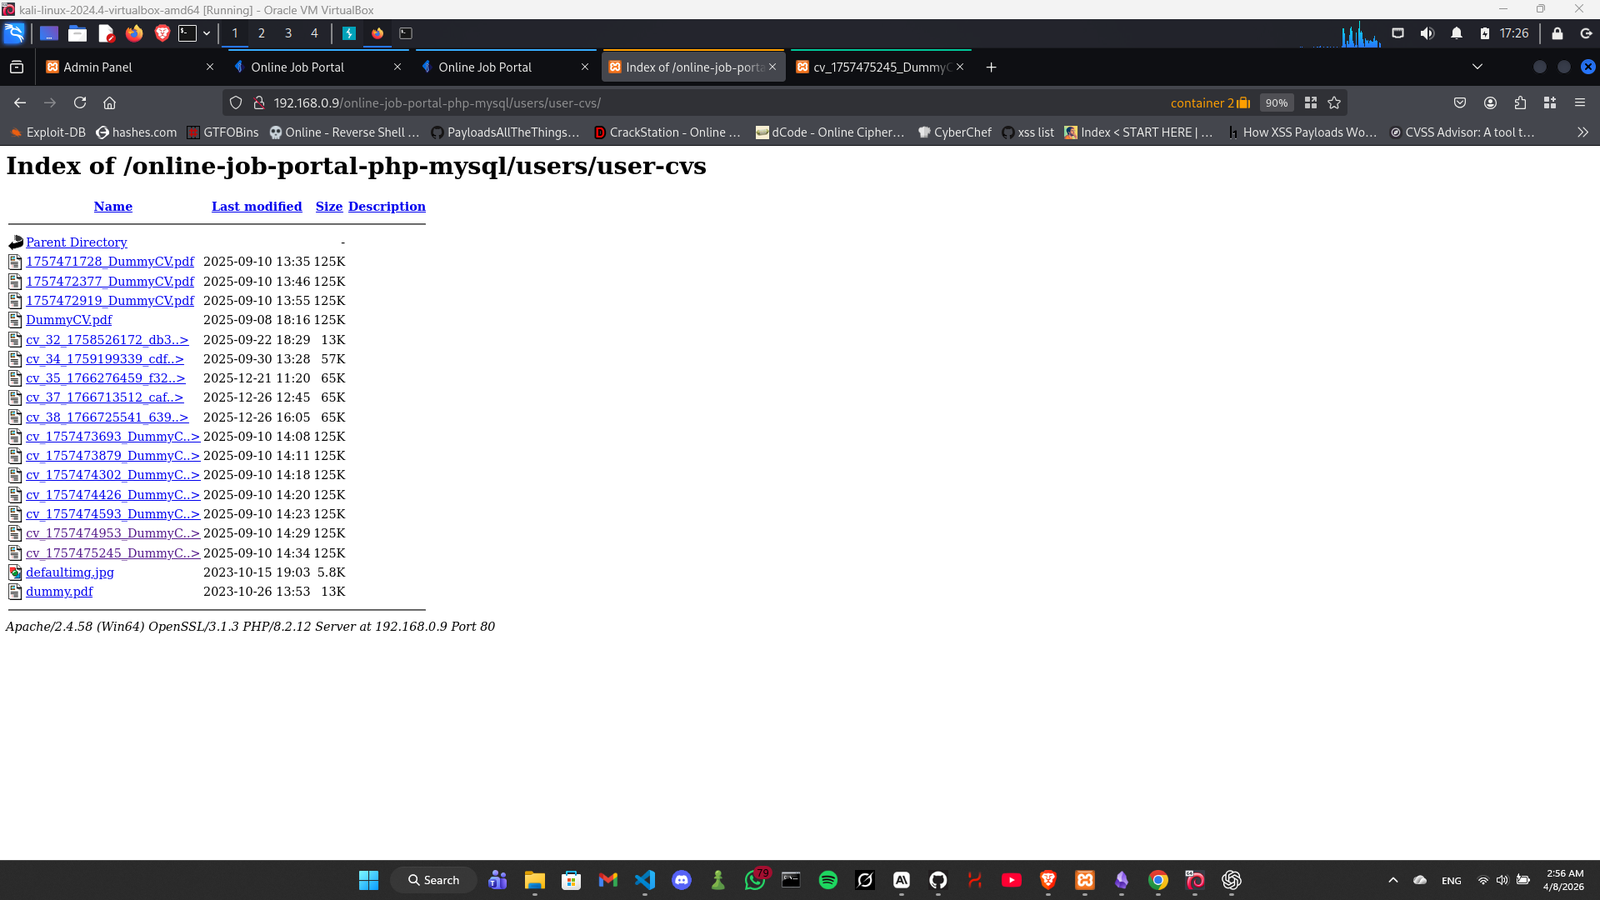
CVE-2026-7071-access-Control

Proof of concept demonstrating unauthenticated access to user resumes via directory listing in CodeAstro Online Job Portal, with reproduction steps…

Proof of concept demonstrating unauthenticated access to user resumes via directory listing in CodeAstro Online Job Portal, with reproduction steps…

Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…

WooCommerce Designer Pro <= 1.9.28 - Unauthenticated Arbitrary File Read

RestroPress – Online Food Ordering System 3.0.0 - 3.1.9.2 - Unauthenticated Information Exposure to Authentication Bypass via Forged JWT

SourceCodester Online Eyewear Shop Remote File Inclusion Vulnerability

CVE-2026-5513: Bookly <= 27.2 Stored XSS via Cookie (Unauthenticated)

Reproducible incident micro-postmortem for on-prem Microsoft SharePoint “ToolShell” (CVE-2025-53770): ATT&CK snapshot, “logs that matter” table,…

Red team Arsenal - An intelligent scanner to detect security vulnerabilities in company's layer 7 assets.

Wicked sick v2.0 script is intended to automate your reconnaissance process in an organized fashion.

Crawlector is a threat hunting framework designed for scanning websites for malicious objects.

Fast, accurate subdomain takeover scanner with zero false positives. Detects vulnerable subdomains, collects metadata (IP, CNAME, title, status…

PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…

crawls the website and finds broken social media links that can be hijacked