

php2shell-lab
 tani2shell/php2shell-lab
Black-box pentest lab for the PHP2Shell engine memory-corruption family (CVE-2026-109618 / CVE-2026-109619, CVSS 9.8/9.2). Dual-flag verified attack…
binary-exploitationcontainer-securityctf+7
4
tani2shell/php2shell-labBlack-box pentest lab for the PHP2Shell engine memory-corruption family (CVE-2026-109618 / CVE-2026-109619, CVSS 9.8/9.2). Dual-flag verified attack…
 brentmartinmiller/php2shell-check
Read-only triage script for WordPress sites after PHP2Shell (CVE-2026-109618, CVE-2026-109619). Checks for signs of compromise and writes a report…
 taniungou/php2shell-lab
Black-box pentest lab for the PHP2Shell engine memory-corruption family (CVE-2026-109618 / CVE-2026-109619, CVSS 9.8/9.2). Dual-flag verified attack…
 leonlai-tw/php-eol-cve-2026-109618-109619
Unofficial patches for PHP CVE-2026-109618 / CVE-2026-109619 (RCE, CVSS 9.2) on EOL platforms: PHP 7.3 on CentOS/RHEL 7 (Remi), PHP 5.4 on Amazon…
 oscerd/cve-2026-85313
Runnable Spring Boot proof-of-concept reproducing CVE-2026-85313, where Apache Camel camel-jetty enableCORS reflects any origin with credentials,…
 owasp/secure-headers-project
OWASP knowledge base and validator for HTTP security response headers, providing recommendations, statistics, and automated configuration checks.
 abraxas/pfsense-cp-maxprocperip
pfSense CE 2.9.0-DEVELOPMENT - High - Remote - Config injection - CP maxprocperip nginx
 abraxas/pfsense-limiter-aqm
pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - Config injection - limiter AQM newline
 abraxas/pfsense-ntp-gps-fudge
pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - Config injection - NTP GPS/PPS fudge
 abraxas/opnsense-wlan-wpa-line
OPNsense 26.7.6 - High - Remote - Config line injection - WLAN WPA identity
 m14r41/scan4secrets
Find credentials and secret with 170+ rules covering across source code, Web URL, and CI/CD, verifies them against vendor APIs, and generates SARIF,…
 abraxas/signal-server-dropwizard-admin
Signal-Server v20261007.0.0 - High - Remote - Privilege leftover - unauth Dropwizard admin :8081
 gmh5225/llm-guard-service
A service to provide protection against prompt injection, jailbreak attacks, and harmful content when interacting with AI services..
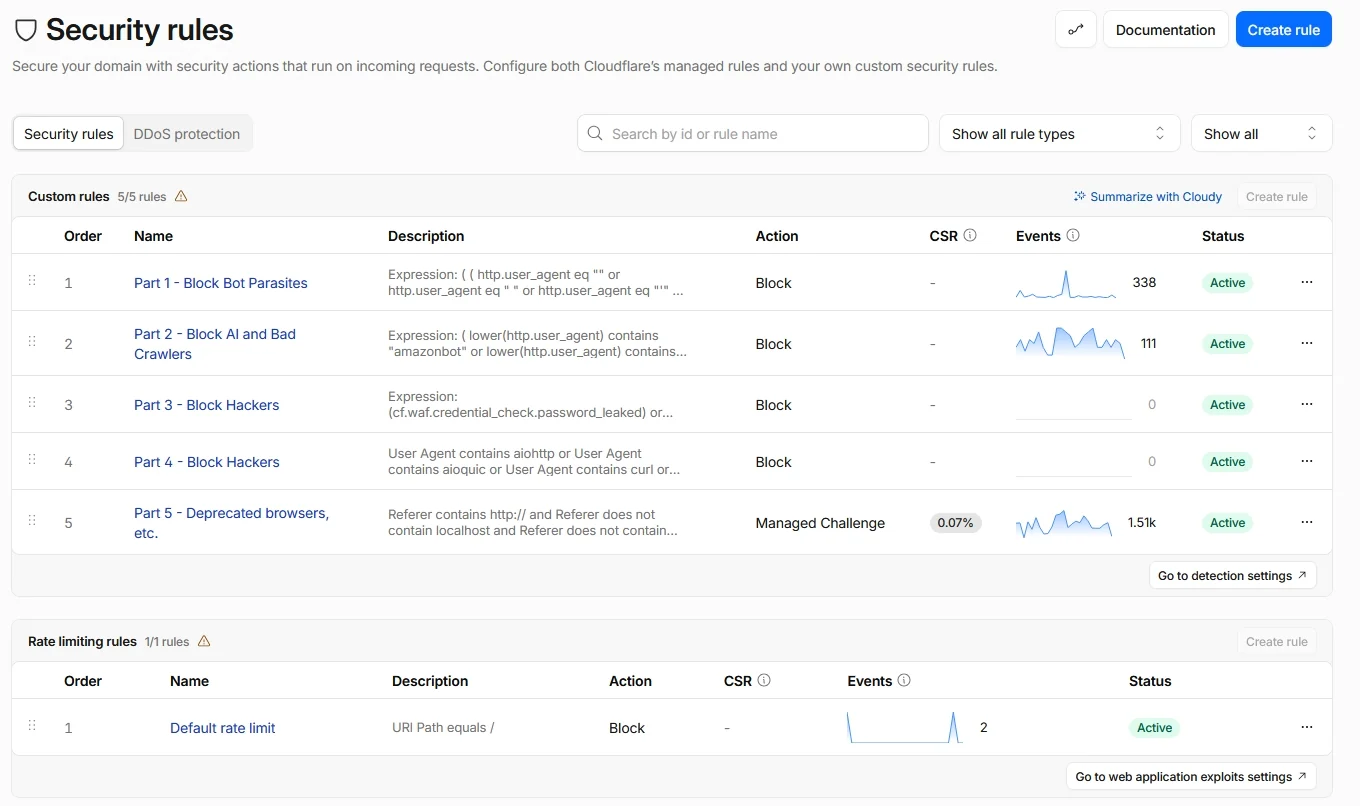 buybitart/cloudflare-security-art
Cloudflare Free Plan security rules (Zero Trust approach) for small websites
 rknf404/chromium-hardening-guide
Harden chromium (somewhat) for privacy and security (and performance)
 albinowax/activescanplusplus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…
 portswigger/active-scan-plus-plus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, code injection, and known CVEs like…
 si13nttt/cve-2025-32432
Python PoC exploiting CVE-2025-32432, an unauthenticated RCE in Craft CMS via Yii DI gadget injection, with assetId scanning, reverse shell, and…