
CVE-2026-100520-laranode-path-traversal
 wvllxe/cve-2026-100520-laranode-path-traversal
Path Traversal -> RCE in Laranode < 1.2.1 (CWE-22). PoC + advisory writeup.
exploitationpenetration-testingremote-access-tool+3
4
wvllxe/cve-2026-100520-laranode-path-traversalPath Traversal -> RCE in Laranode < 1.2.1 (CWE-22). PoC + advisory writeup.
 digitalsurgn/cve-2024-21546
Automated exploit toolkit and detection template for CVE-2024-21546, an unauthenticated RCE in UniSharp Laravel Filemanager, with WAF evasion and…
 e4zyy/project-cve-2025-54068
Fast Python scanner detects vulnerable Laravel Livewire v3 sites (CVE-2025-54068, CVSS 9.2). Separates risky sites into vuln.txt, safe sites into…
 fckoo/nanwinata-cve-2024-52301
Scans for CVE-2024-52301, an argument injection vulnerability in Laravel, using subfinder and httpx to identify affected web applications.
 rockmelodies/cve-2026-23524
Laravel Reverb 为 Laravel 应用提供实时 WebSocket 通信后端。在 1.6.3 及更早版本中,Reverb 将来自 Redis 通道的数据直接传递给 PHP 的 unserialize() 函数,且未对可实例化的类进行限制,导致用户面临远程代码执行风险。
 cappricio-securities/laravel-ignition-rxss
Laravel Ignition contains a cross-site scripting vulnerability when debug mode is enabled.
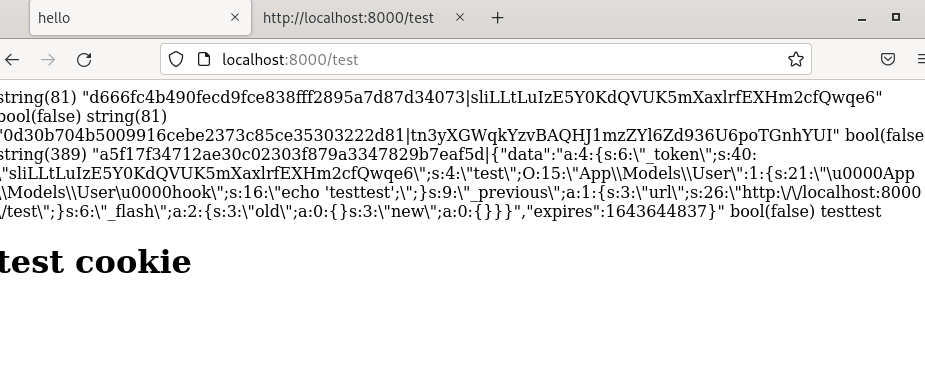 synacktiv/laravel_cookie_killer
Decrypt and re-encrypt Laravel session cookies to exploit insecure PHP deserialization for remote code execution.
 katsana/remote-control
Grant remote access to user account without sharing credentials
 luisdalmolin/recon-test-livewire
Test target: fresh Laravel 12 app with Livewire pinned to vulnerable 3.6.3 (CVE-2025-54068) for recon scanning
 madexploits/phpunit-exploit
PHPunit Checker CVE-2017-9841 By MrMad
 helgesverre/livewire-honeypot
High-interaction honeypot mimicking a vulnerable Laravel/Livewire app. Captures RCE exploits and webshells targeting CVE-2024-47823, CVE-2025-54068,…
 piperpwn/cve-2021-3129-piperpwn
Laravel Debug Mode and Payload
 cybercrewinc/cve-2025-64027
Reflected Cross-Site Scripting in Snipe-IT CSV Import Workflow
 banyaksepuh/mass-cve-2021-3129-scanner
Mass scanner for CVE-2021-3129 Laravel Debug RCE, automating detection across multiple hosts from a list.
 ajisai-babu/cve-2021-3129-exp
Laravel Debug mode RCE漏洞(CVE-2021-3129)poc / exp
 theethat-thamwasin/cve-2025-63307
An authenticated Stored Cross-site Scripting (XSS) vulnerability in laravel-file-manager v3.3.1 and below allows attackers with access to the file…
 sybelle03/cve-2021-43617
This is a reproduction of PHP Laravel 8.70.1 - Cross Site Scripting (XSS) to Cross Site Request Forgery (CSRF) vulnerability
 derrickschoen/laravel-framework
Fork of laravel/framework 10.50.2 with CVE-2026-48019 (CRLF injection in default email rule) backported into ValidatesAttributes::validateEmail.…