

joomla-bruteforce
 ajnik/joomla-bruteforce
Python script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.
authenticationpassword-attackspassword-cracking+4
138
ajnik/joomla-bruteforcePython script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 4nner/cve-2019-9053
Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
 pervinzahidli/cve-2026-77771
Advisory for CVE-2026-77771, a 2FA bypass in the miniOrange WordPress plugin via session-scoped OTP lockout, with impact analysis and remediation…
 zhairiazzeddine/exploit-cve-2023-6063-poc-vuln
Python PoC for CVE-2023-6063, an unauthenticated time-based blind SQL injection in WP Fastest Cache <=1.2.2, extracting WordPress password hashes and…
 mycode83/godirb
Fast and easy-to-use directory brute-forcer written in Go.
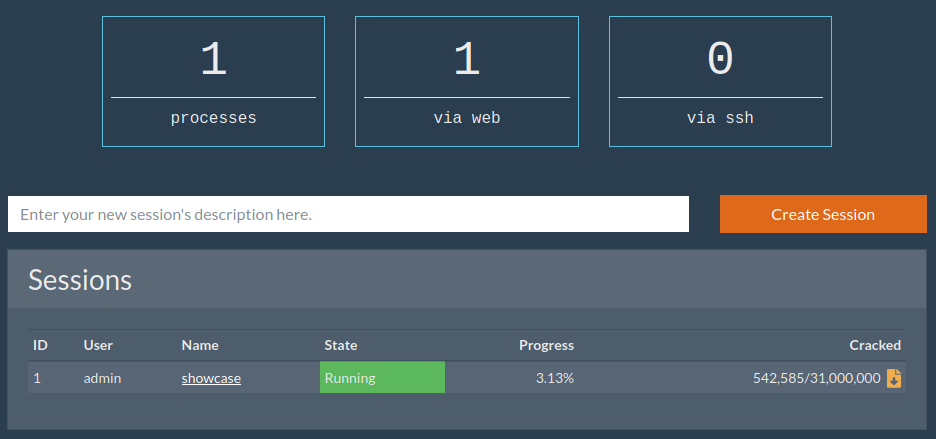 sadreck/crackerjack
Web-based GUI for Hashcat that simplifies password cracking with session management, mask generation, wordlist support, and multi-user access.
 dhammon/hoteldruid-cve-2021-42949
Exploit for CVE-2021-42949 in HotelDruid v3.0.3, demonstrating predictable session token generation and authentication bypass via brute force.

 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 george0papasotiriou/cve-2026-22016-ipfs-cid-spoofing-via-multihash-length-extension
Python proof-of-concept demonstrating IPFS CID spoofing via multihash length extension, highlighting content-addressing verification flaws that can…

 nu11secur1ty/insect
High-performance web path discovery and directory brute-forcing tool. Discovers hidden files, directories, and endpoints using customizable…
 dejanlevaja/wpbf
WPBF - a multithreaded WP brute forcer
 besioo/hackerone
Brute-force scraper for HackerOne disclosed reports via their public API, collecting report IDs, links, titles, and states for security research and…
 devanshbatham/favfreak
Making Favicon.ico based Recon Great again !
 z-bool/venom-jwt
针对JWT渗透开发的漏洞验证/密钥爆破工具,针对CVE-2015-9235/空白密钥/未验证签名攻击/CVE-2016-10555/CVE-2018-0114/CVE-2020-28042的结果生成用于FUZZ,也可使用字典/字符枚举(包括JJWT)的方式进行爆破(JWT Crack)
 noxurge/cve-2025-65900
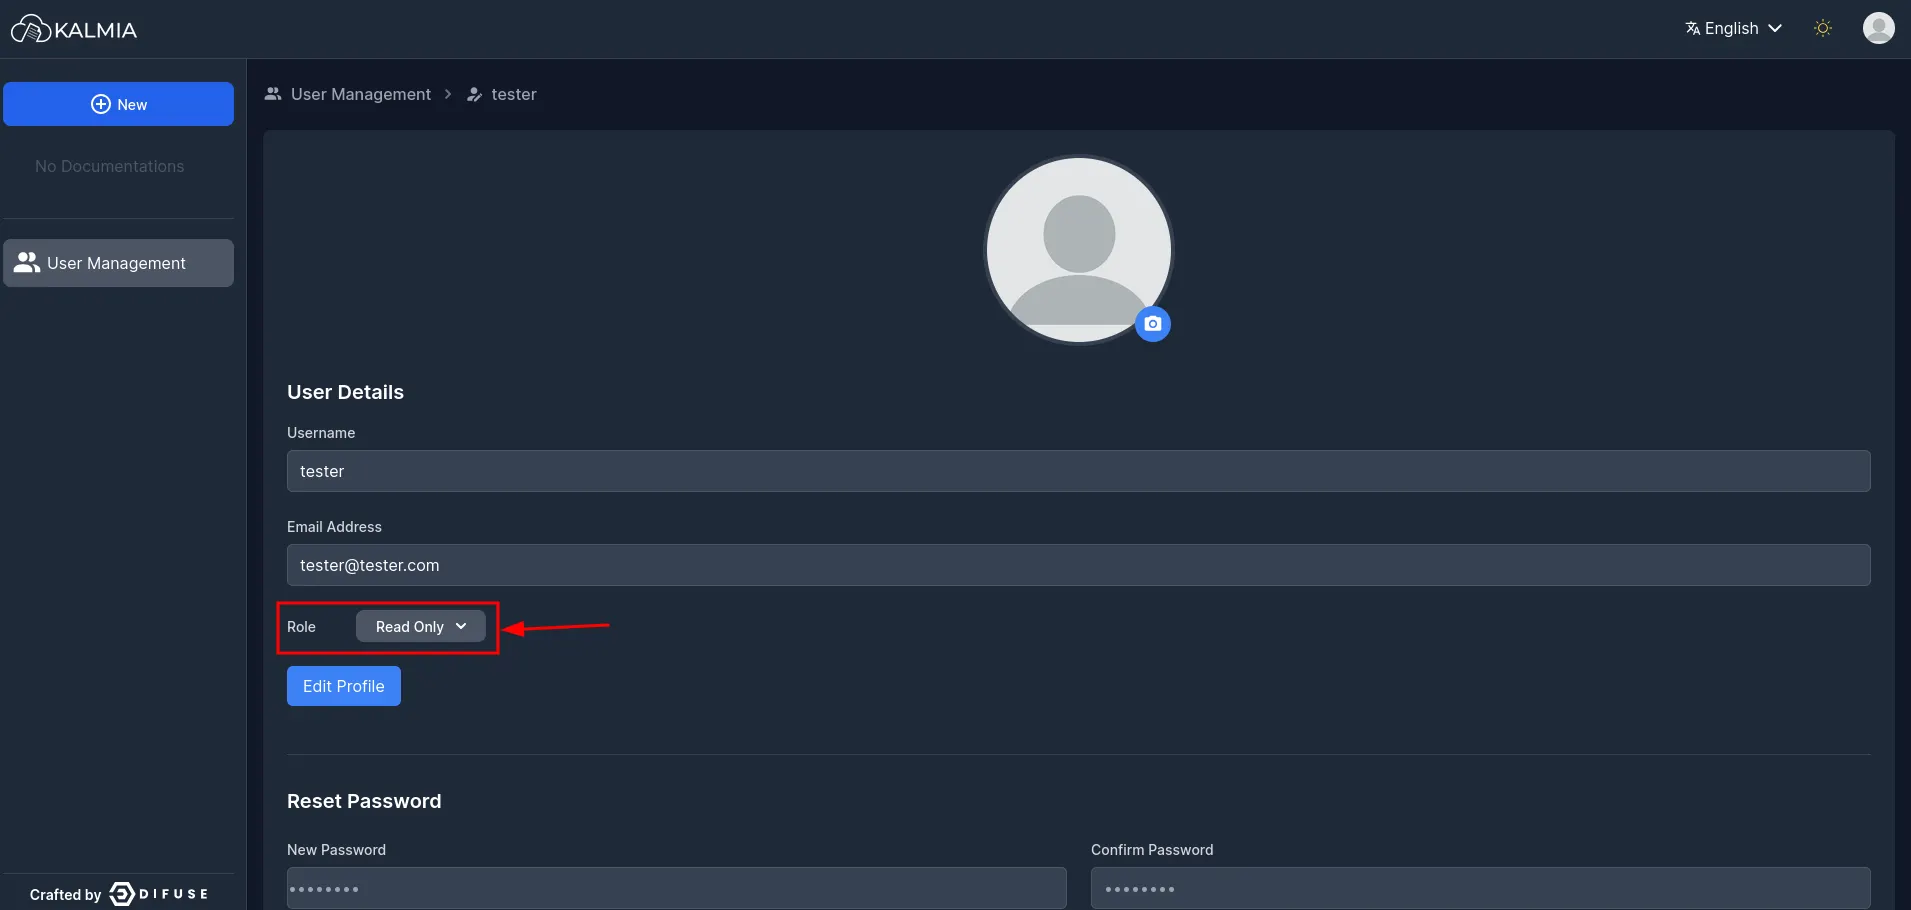
DifuseHQ Kalmia CMS version 0.2.0 contains an Incorrect Access Control vulnerability in the /kal-api/auth/users API endpoint. Due to insufficient…