CVE-2026-104051-pictshare-info-disclosure
 wvllxe/cve-2026-104051-pictshare-info-disclosure
Sensitive info disclosure via info API in PictShare < 3.7.1 (CWE-522). PoC + advisory writeup.
data-exfiltrationeducationexploitation+5
wvllxe/cve-2026-104051-pictshare-info-disclosureSensitive info disclosure via info API in PictShare < 3.7.1 (CWE-522). PoC + advisory writeup.
 hackinglz/ip-obfuscation
Generates obfuscated IP addresses and URLs using DWORD, octal, hex, IPv6-mapped, and fake-domain @ tricks for penetration testing, phishing…
 mmarting/unwaf
Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…
 saku0512/cve-2026-72815-poc
Local Go PoC demonstrating CVE-2026-72815, an X-Forwarded-For IP spoofing flaw in go-chi/chi middleware.RealIP that bypasses IP-based ACLs, with a…
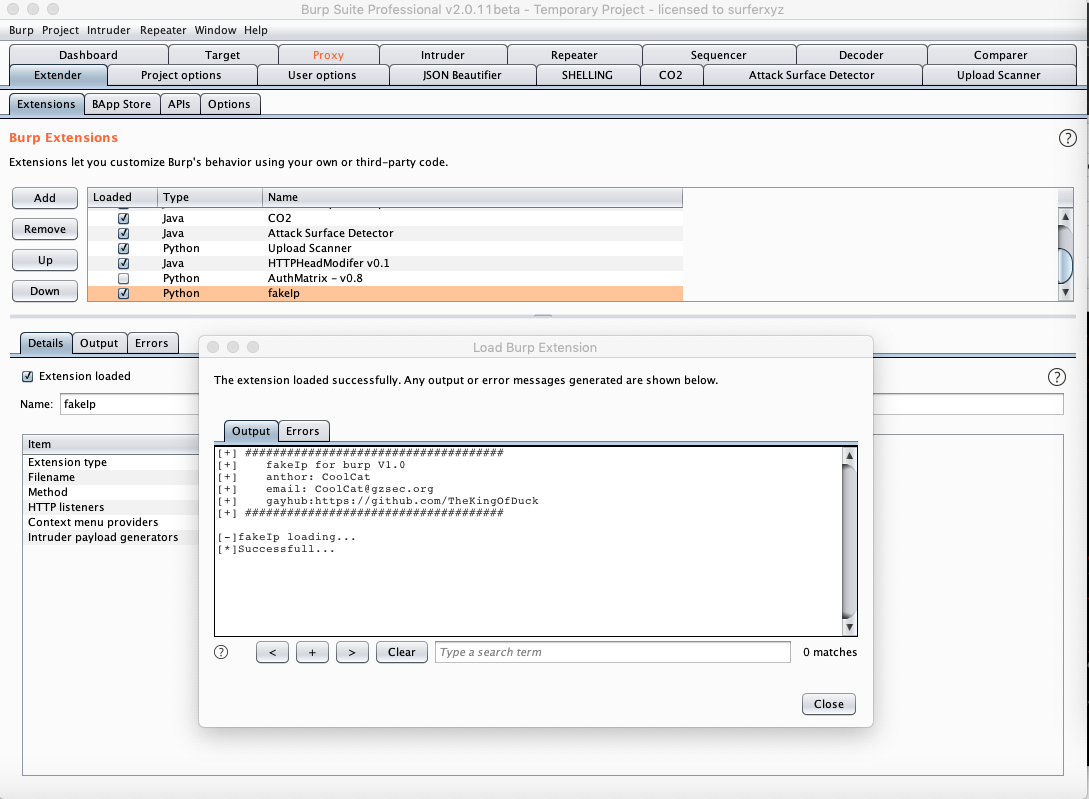 thekingofduck/burpfakeip
Burp Suite extension for spoofing IP addresses in HTTP requests, enabling testing of server-side IP restrictions and bypassing IP-based access…
 rodpwn/cve-2021-43798-mass_scanner
Mass scanner for Grafana CVE-2021-43798 unauthorized file read, supporting single targets, hostname lists, and IP ranges with PoC verification.
 redyank/cve-2026-33752
Demonstrates a redirect-based SSRF vulnerability in curl_cffi allowing internal network access, with PoC code and analysis of TLS impersonation…
 0x4meliorate/mimic
Frameless Browser‑in‑the‑Browser (BitB) - No iframes, no frame‑busting issues. A single‑script Shadow DOM / MutationObserver library for realistic…
 alkimcoskun/cve-2025-69848-security-advisories
Security advisory for CVE-2025-69848 – Reflected XSS in NetBox ProtectedError handling
 nullwhisper/cve-2026-14840
Proof-of-concept exploit for a WordPress plugin vote-limit bypass using spoofed X-Forwarded-For headers; ships a Docker lab to validate…
 bishopfox/ca-clone
Scripts to clone CA certificates for use in HTTPS client attacks.
 bishopfox/bigip-scanner
Determine the running software version of a remote F5 BIG-IP management interface.
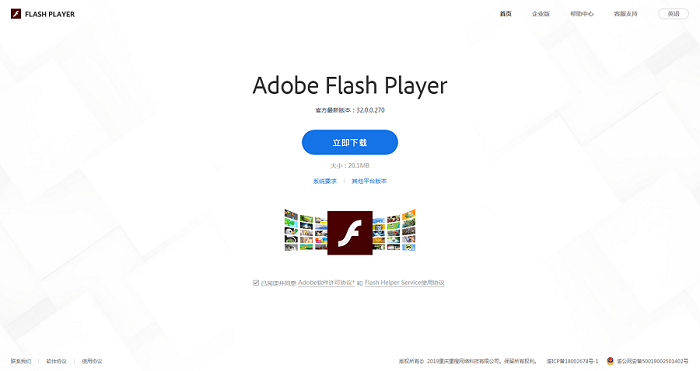 ianxtianxt/flash-player
flash钓鱼源码 中文+英文
 rxerium/ai-bot-ip-ranges
Official IP ranges for AI bot crawlers (OpenAI, Anthropic, Google, Microsoft, Perplexity). Weekly auto-updates.
 snailsploit/cve-2026-33693
CVE-2026-33693: SSRF via 0.0.0.0 Bypass in activitypub-federation-rust v4_is_invalid() (CVSS 6.5 Moderate)
 danmcinerney/device-pharmer
Opens 1K+ IPs or Shodan search results and attempts to login