
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
40 results
Kousei preview

Kousei

GitHubnu11secur1ty/kousei

Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
exploitationpassword-crackingpayload-generation+6
3
1 day ago
CVE-2019-9053 preview

CVE-2019-9053

GitHub4nner/cve-2019-9053

Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…

exploitationpassword-crackingpenetration-testing+3
113 years ago
Exploit-CVE-2023-6063-PoC-Vuln preview

Exploit-CVE-2023-6063-PoC-Vuln

GitHubzhairiazzeddine/exploit-cve-2023-6063-poc-vuln

Python PoC for CVE-2023-6063, an unauthenticated time-based blind SQL injection in WP Fastest Cache <=1.2.2, extracting WordPress password hashes and…
exploitationpassword-crackingpenetration-testing+4
22 days ago
CVE-2020-12712 preview

CVE-2020-12712

GitHub0xvedette/cve-2020-12712

Decrypts passwords stored in SOS JobScheduler (S)FTP profiles by exploiting the use of the profile name as the 3DES encryption key, enabling recovery…
cryptographyexploitationpassword-attacks+2
6 years ago
CVE-2021-24750 preview

CVE-2021-24750

GitHubfimtow/cve-2021-24750

Demonstration of the WP Visitor Statistics plugin exploit
exploitationpenetration-testingvulnerability-analysis+2
14 years ago
CVE-2025-63579 preview

CVE-2025-63579

GitHubbarisbaydur/cve-2025-63579

Unauthorized access to all user names and passwords entered in the Address Book feature found in Kyocera printers.
exploitationinformation-gatheringpenetration-testing+2
11 months ago
halo-cors-csrf-CVE-2026-67921 preview

halo-cors-csrf-CVE-2026-67921

GitHubunpredictable21/halo-cors-csrf-cve-2026-67921

Proof-of-concept demonstrating a combined CORS misconfiguration and CSRF protection bypass in Halo CMS, enabling cross-site request forgery attacks…
exploitationvulnerability-analysisweb-application-exploitation+1
1 month ago
Bug-Bounty-Wordlists preview

Bug-Bounty-Wordlists

GitHubya551n3/bug-bounty-wordlists

Curated collection of wordlists for bug bounty hunting, covering directories, subdomains, parameters, usernames, passwords, and web fuzzing payloads.

curated-resourcesfuzzinginformation-gathering+3
6349 months ago
JWT_Brute preview

JWT_Brute

GitHubjas502n/jwt_brute

JWT_Brute

authenticationpassword-crackingpenetration-testing+1
316 years ago
bleeding-heart preview

bleeding-heart

GitHubpierceoneill/bleeding-heart

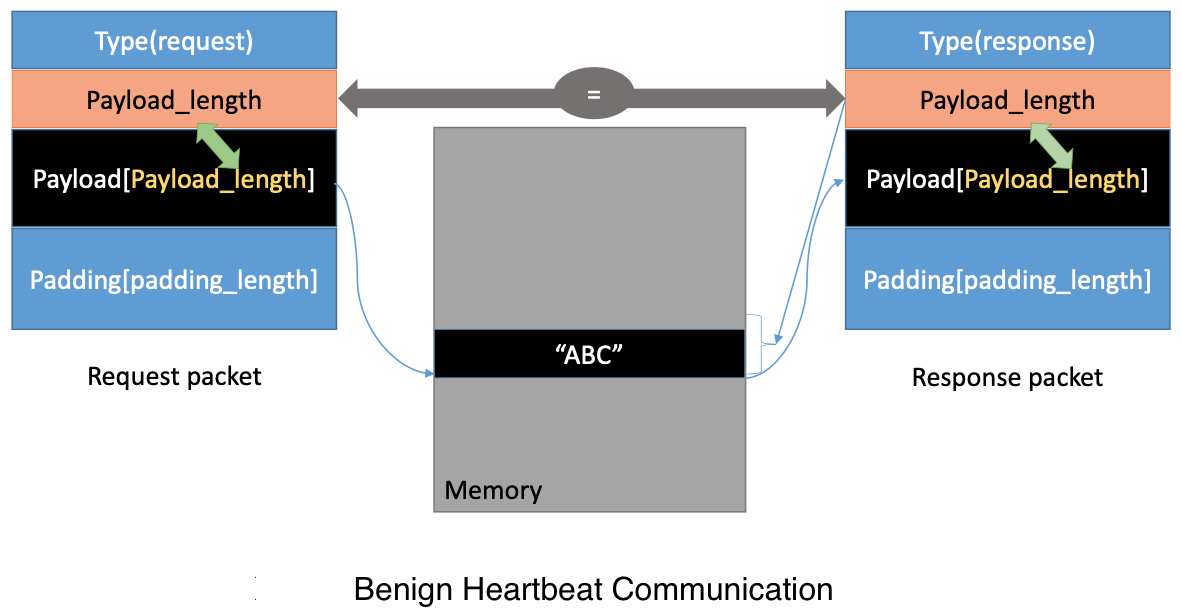
The Heartbleed bug `CVE-2014-0160` is a severe implementation flaw in the OpenSSL library, which enables attackers to steal data from the memory of…

cryptographyeducationexploitation+3
5 years ago
CVE-2018-14847 preview

CVE-2018-14847

GitHubtausifzaman/cve-2018-14847

This is a proof of concept of the critical WinBox vulnerability (CVE-2018-14847) which allows for arbitrary file read of plain text passwords. The…
exploitationinformation-gatheringnetwork-security+3
11 year ago
Venom-JWT preview

Venom-JWT

GitHubz-bool/venom-jwt

针对JWT渗透开发的漏洞验证/密钥爆破工具,针对CVE-2015-9235/空白密钥/未验证签名攻击/CVE-2016-10555/CVE-2018-0114/CVE-2020-28042的结果生成用于FUZZ,也可使用字典/字符枚举(包括JJWT)的方式进行爆破(JWT Crack)
exploitationfuzzingpassword-cracking+3
2871 year ago
CVE-2025-65900 preview

CVE-2025-65900

GitHubnoxurge/cve-2025-65900

DifuseHQ Kalmia CMS version 0.2.0 contains an Incorrect Access Control vulnerability in the /kal-api/auth/users API endpoint. Due to insufficient…

authenticationexploitationmisconfiguration+3
10 months ago
payloads preview

payloads

GitHubfoospidy/payloads

Git All the Payloads! A collection of web attack payloads.

ctfcurated-resourceseducation+6
4.0k5 years ago
wpscan preview

wpscan

GitHubwpscanteam/wpscan

WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
crawlerdynamic-code-analysisinformation-gathering+7
9.8k3 days ago
CVE-2021-3130 preview

CVE-2021-3130

GitHubjet-pentest/cve-2021-3130

Proof-of-concept for CVE-2021-3130: demonstrates credential exposure via HTML obfuscation bypass in Open-AudIT up to 4.0.2, revealing SSH, SNMP, and…
authenticationmisconfigurationpenetration-testing+2
5 years ago
CVE-2025-25749-Weak-Password-Policy-in-HotelDruid-3.0.7 preview

CVE-2025-25749-Weak-Password-Policy-in-HotelDruid-3.0.7

GitHubhuyvo2910/cve-2025-25749-weak-password-policy-in-hoteldruid-3.0.7

Proof-of-concept for CVE-2025-25749 demonstrating weak password policy in HotelDruid 3.0.7, with automated test scripts and mitigation…
authenticationeducationpassword-attacks+3
1 year ago
CVE-2018-16987 preview

CVE-2018-16987

GitHubgquere/cve-2018-16987

Technical disclosure of CVE-2018-16987: cleartext storage of external service passwords in Squash TM administration panel, with CVSS 4.1 scoring and…

configuration-auditinginformation-gatheringpassword-cracking+3
18 years ago
Previous123Next