

CVE-2026-77647
 nxploited/cve-2026-77647
SPIP before 4.4.20 allows unauthenticated remote attackers to execute arbitrary code
exploitationpayload-generationpenetration-testing+5
nxploited/cve-2026-77647SPIP before 4.4.20 allows unauthenticated remote attackers to execute arbitrary code
 baguette168/nmg
Generates parameterized .NET memory-shell payloads (VPP, MVC route, HttpListener) compatible with Godzilla, Behinder, and AntSword clients for red…
 fl0ydsec/cve-2026-15989
Mass scanner and exploit for CVE-2026-15989, the unauthenticated privilege escalation in Super Forms <= 6.3.316 that creates administrator accounts…
 winrarzipsexploit/cve-2026-87930
Joomla multi-CVE RCE suite with seven exploit modules for Balbooa Forms, Page Builder CK, SP Page Builder, JCE, iCagenda, Helix3, and SP LMS, plus…
 winrarzipsexploit/cve-2026-27540
Python exploit suite for CVE-2026-27540, an unauthenticated file upload RCE in the WooCommerce Wholesale Lead Capture plugin, with fingerprinting,…
 rootxn/cve-2026-12793
Python PoC for CVE-2026-12793 in JetFormBuilder <= 3.6.2: unauthenticated privilege escalation leading to plugin upload and remote code execution,…
 irsdl/ysonet
Deserialization payload generator for a variety of .NET formatters
 xshadow-here/cve-2026-0740
Automated mass exploiter for CVE-2026-0740, an unauthenticated arbitrary file upload in Ninja Forms File Uploads plugin, enabling remote code…
 open-flaw/cve-2026-25940
Proof-of-concept for CVE-2026-25940 demonstrating embedded JavaScript execution via crafted AcroForm radio button appearances in PDF viewers, with…
 mbanyamer/cve-2026-26335-calero-verasmart-rce
Automated exploit for CVE-2026-26335, a critical unauthenticated RCE in Calero VeraSMART via forged ASP.NET ViewState using static machine keys.…
 exploit-io/cve-2021-41349
Exploit tool for CVE-2021-41349 that generates an HTML form to deliver XSS payloads to Microsoft Exchange servers, enabling execution of arbitrary…
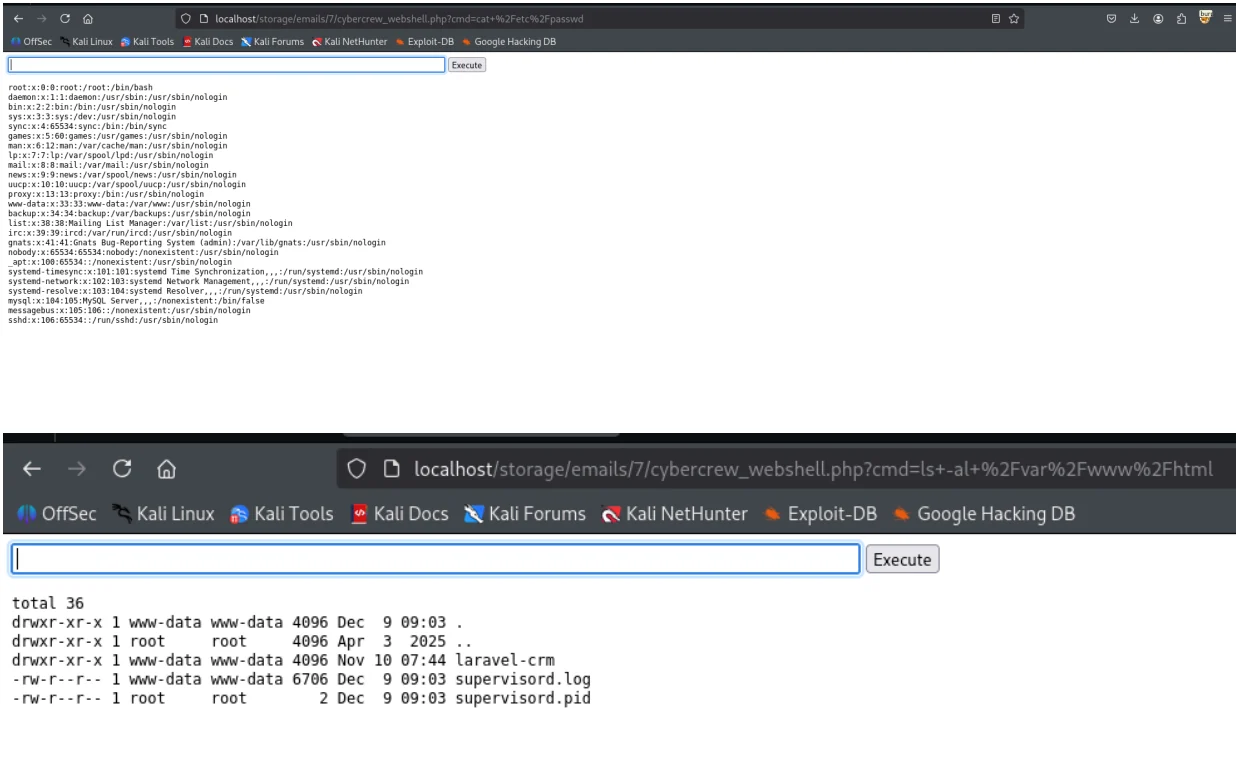 cybercrewinc/cve-2026-36340
Remote Code Execution (RCE) Vulnerability in Krayin CRM v2.1.5
 netvanguard-cmd/cve-2026-27597
Exploit for CVE-2026-27597, a critical RCE in Agentfront Enclave before 2.11.1, allowing sandbox escape and remote code execution.
 murrez/cve-2026-1306
Multi-target PoC runner for CVE-2026-1306 in WordPress midi-Synth plugin: fetches nonce, sends export AJAX request to upload files, and verifies…
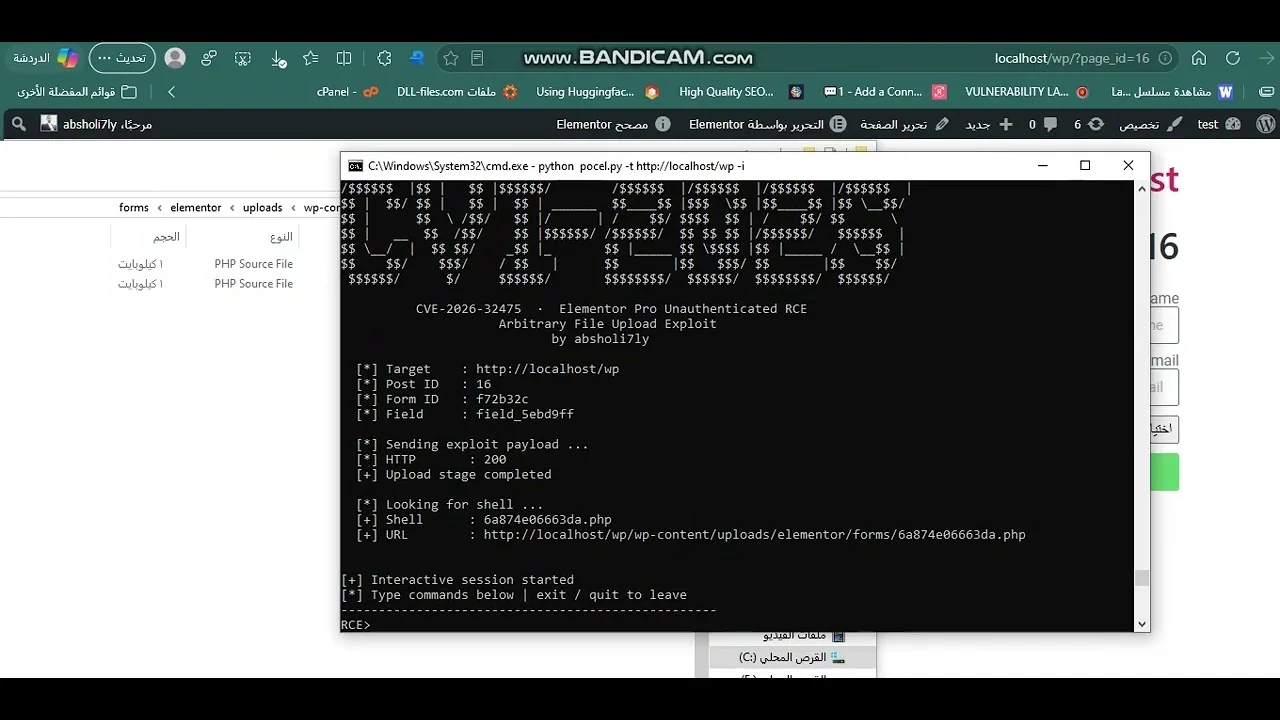 absholi7ly/elementor-pro-unauthenticated-arbitrary-file-upload-to-rce
CVE-2026-32475 The Elementor Pro Forms File Upload field handles validation and file processing in two separate loops with different handling of…
 typedefabcd1234ntd/cve-2026-19501-poc
Proof-of-concept for unauthenticated CSV formula injection in SureForms, showing crafted form submissions trigger spreadsheet formulas when exported…
 cypherhippie/cve-2026-34486---unauthenticated-rce-via-java-deserialization
EncryptInterceptor fail-open bypass in Apache Tomcat Tribes clustering leading to unauthenticated RCE via Java deserialization.
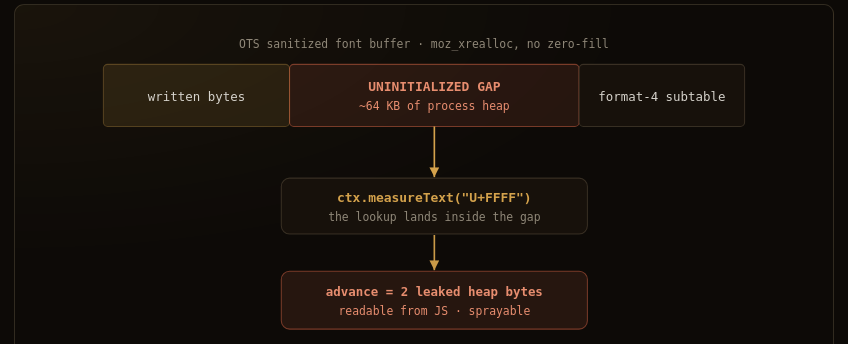 defineid/palimpsest
CVE-2026-74945, Uninitialized heap disclosure via a crafted web font (sec-high)